
Episode 41 of The Security Podcast of Silicon Valley aired on April 14, 2024, with Jon McLachlan hosting. The guest was Michael Moore, then chief privacy officer at Lacework (Podbean, Apple Podcasts, Spotify). The episode is called “Michael Moore, Chief Privacy Officer at Lacework, Securing Tomorrow: Navigating the Cyber Frontier.” It has no video version. Fortinet completed its purchase of Lacework on August 1, 2024 (Fortinet), and Michael came back to the show as Glean’s head of legal on episode 73.
The line that sums up the conversation came near the end. Jon had called security a growth opportunity, and Michael put security and privacy side by side.
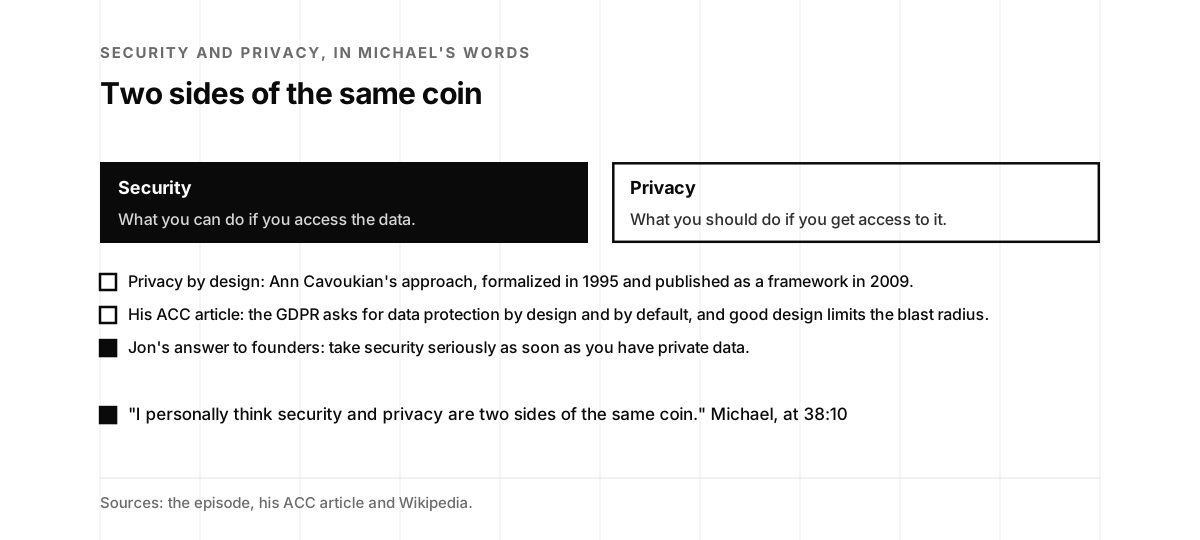
“Security is about what you can do if you access the data. Privacy is about what you should do if you get access to the data.”
Michael Moore, at 38:15
This page follows the conversation in order: a section for each part of it, eighteen figures, twelve clips from the tape, a LinkedIn post, the full transcript, and five tools: a quiz, a scorecard for whether you would catch an intruder early, a calculator for how long an intruder gets, a timeline, and a to-do list. Where the decodes of the tape disagree on a word, the transcript puts its best guess in brackets, and the page doesn’t quote or retell those words.
From inventor to patent agent
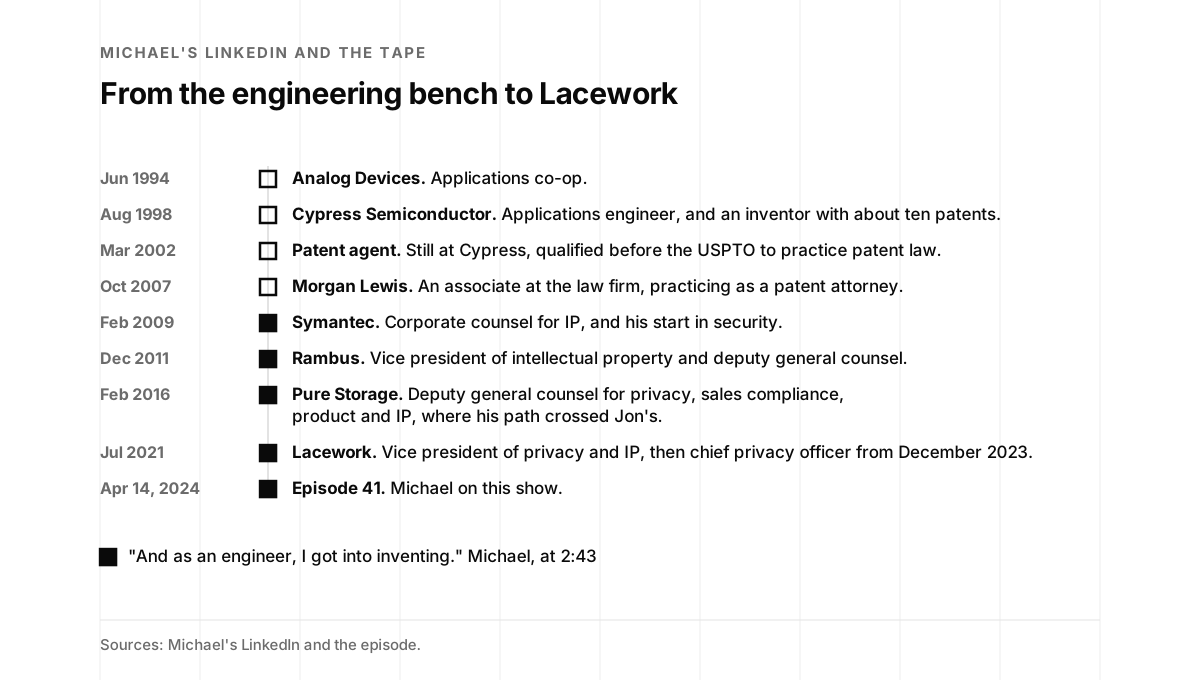
Jon opened with Michael’s résumé. He came up through Analog Devices, then Cypress Semiconductor as a patent agent and applications engineer.
“So you bring some of that engineering grit to the table.”
Jon McLachlan, at 0:32
After that came Morgan Lewis as an associate, Symantec as corporate counsel for IP, and Rambus as vice president of intellectual property and deputy general counsel. Then Pure Storage, where Jon and Michael’s paths crossed, and three years or so at Lacework. Jon asked how he got into law. Michael started with what Lacework does: protect customers against risks, threats, identity misuse and code supply chain attacks, with anomaly detection that stops known and unknown threats, zero days among them. A zero-day is a vulnerability unknown to the people who could fix it (Wikipedia). Then he went back to the start. His undergraduate degree was in electrical engineering, circuit design and the like. At Cypress he did product engineering, application engineering, and some code and system design.
“And as an engineer, I got into inventing.”
Michael Moore, at 2:43
“I was a successful inventor”
Michael Moore, at 2:46
He counts about ten patents from those years, and they got him interested in the legal side of technology. He became a patent agent, someone who is not quite an attorney:
“but is qualified before the USPTO to practice patent law.”
Michael Moore, at 3:02
In the United States, a patent practitioner is either a patent attorney or a patent agent, registered to represent clients before the United States Patent and Trademark Office. Either one may prepare, file and prosecute patent applications (Wikipedia). Business school and law school came next, and his work stayed tied to chip and software technology. The tech mattered to him, he said, and the people mattered more.
“what interested me was the creative, or the inventor aspect of people developing new cool stuff.”
Michael Moore, at 3:17
He told the same story to Sasha and Jon on episode 73.
The lifeblood of an innovation economy
He practiced first as a patent attorney at a law firm, then moved to Symantec, where he got into the security side of technology. His practice was intellectual property: patents, open source, trademarks, trade secrets.
“That’s really the lifeblood of an innovation economy.”
Michael Moore, at 4:00
But there are, he said:
“lots of people who want to steal that, and that’s where security comes in.”
Michael Moore, at 4:02
Then there are the people who want to misuse the personal data a company gathers.
“And that’s where the privacy aspect comes in.”
Michael Moore, at 4:10
He listed the threads that tie them together: data security, data privacy, trade secrets, copyright, patents, trademarks, and mask works for chips. In US law, a mask work is the two- or three-dimensional layout of an integrated circuit (Wikipedia). All of it comes down to one question, he said: you create something special, so how do you protect it?
Knocked off overseas
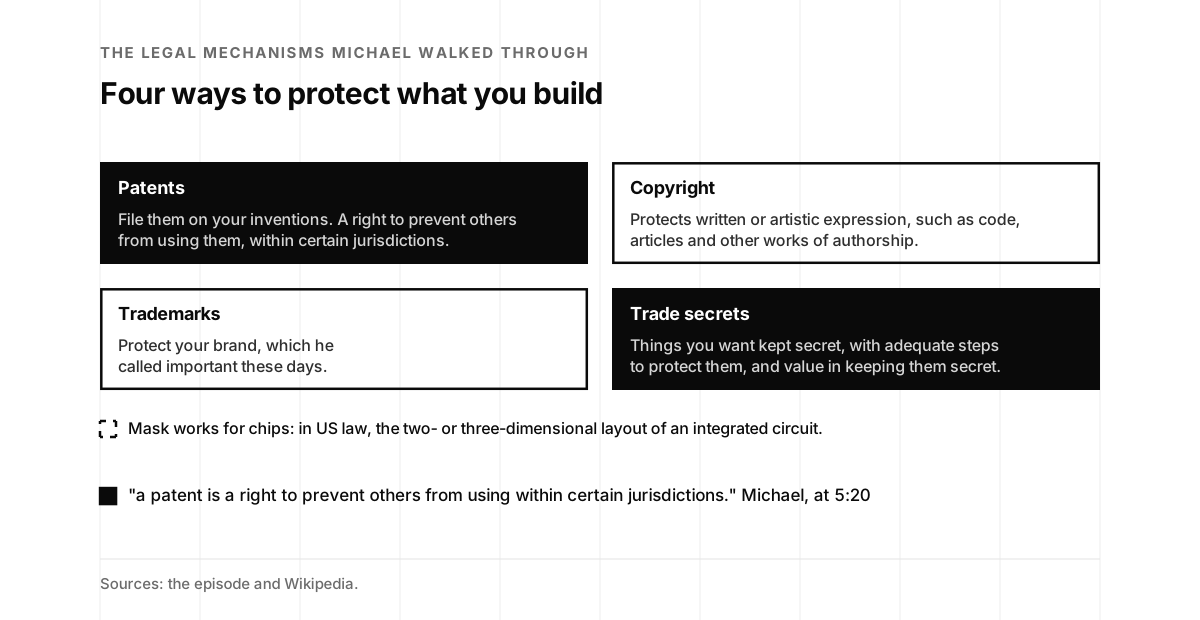
A company can spend many millions, or hundreds of millions, on research and development. The risk is someone cloning the result or knocking it off.
“putting counterfeits for cheap on Amazon or other marketplaces?”
Michael Moore, at 4:40
“And that’s a real problem.”
Michael Moore, at 4:44
It hits large companies and small inventors working in a garage alike, he said. Their products get knocked off overseas at cheap manufacturing shops and sold online for a fraction of the price.
“And that is actually a disincentive to innovation.”
Michael Moore, at 5:04
It’s a disincentive to progress and to investment too, he said. Clea Ostendorf of Code42 told the inside version of the same theft, people walking out the door with the roadmap, on episode 47.
Four ways to protect it
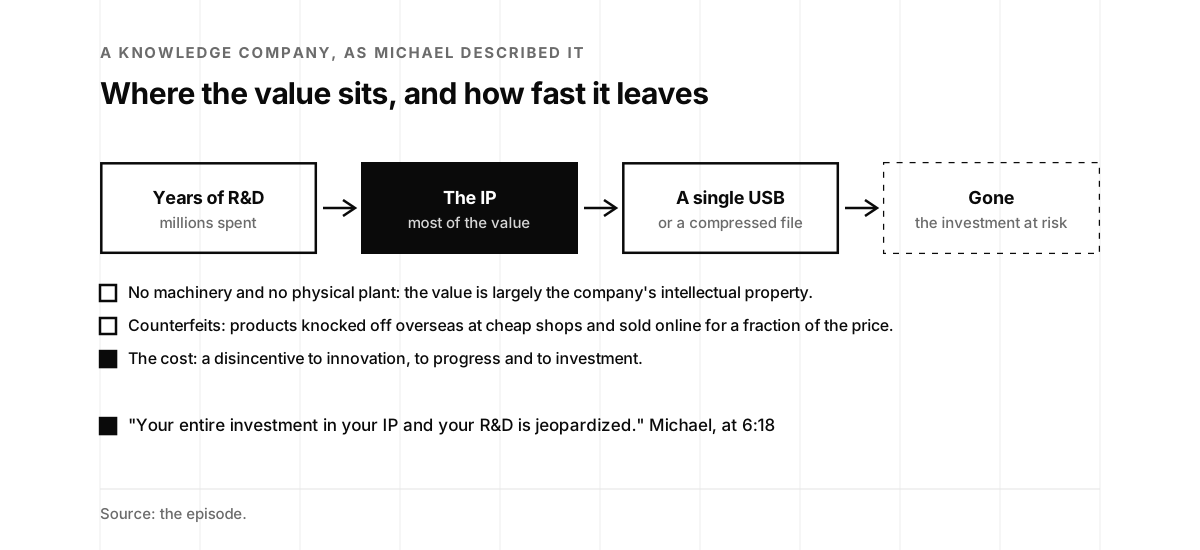
Then he walked through the legal mechanisms, one at a time. The first is to file patents on your inventions, and:
“a patent is a right to prevent others from using within certain jurisdictions.”
Michael Moore, at 5:20
Copyright protects written or artistic expression, such as code, articles and other works of authorship.
“You can use trademarks to protect your brand, which is very important these days.”
Michael Moore, at 5:35
Trade secrets protect things that are secret. To count, he said, you have to want them kept secret, take adequate steps to protect them, and draw value from keeping them secret. Wikipedia describes a trade secret as business information that has value because it isn’t generally known, and that the owner keeps secret for a competitive edge (Wikipedia). Most companies hold some mix of these.
“and these assets are worth an awful lot of money.”
Michael Moore, at 5:52
On episode 73, Michael described code, designs and brands as facets of the same problem.
On a single USB
A knowledge company has no machinery and no physical plant.
“then really your value is largely in the intellectual property of your company.”
Michael Moore, at 6:06
“And in many cases, that can be fit on a single USB or a small SD card, or just thrown over the internet in a compressed file, and it’s gone.”
Michael Moore, at 6:10
“Your entire investment in your IP and your R&D is jeopardized.”
Michael Moore, at 6:18
That is where technology, IP and law all come together, he said.
Sensitive and personal to them
The other piece, he said, is how much data the developed world processes. Much of it is personal: people’s lives, habits, preferences and finances.
“Things that are sensitive and personal to them.”
Michael Moore, at 6:50
“That data gets stolen, there is significant potential for misuse.”
Michael Moore, at 6:52
With financial data or social security numbers in it, he said:
“people’s lives can be ruined.”
Michael Moore, at 7:01
Credit gets destroyed, finances get wrecked, and some people struggle to hold a job. Companies suffer too.
“there are companies that get put out of business because they’re unable to compete once their data has been stolen”
Michael Moore, at 7:21
Good security and good privacy protect the company’s assets, employees and customers, he said, and the jobs that feed families and keep a roof over their heads. Jon picked up the human part. It’s easy to get lost in all this data and think of it as ones and zeros, he said, and:
“that stuff is connected to our lives.”
Jon McLachlan, at 8:19
The good fight
Michael took the thanks and turned it outward.
“we’re all fighting the good fight”
Michael Moore, at 9:20
He had just spoken at the Association of Corporate Counsel Cybersecurity Summit. The ACC, founded in 1983 as the American Corporate Counsel Association, serves attorneys who work in the legal departments of companies and other private-sector organizations (Wikipedia). The attendees included US law enforcement, the Department of Justice, the military and CISA. Many of their perspectives were about actors seeking to steal and misuse data.
“And I won’t name any countries.”
Michael Moore, at 10:20
Some of what those actors do is physical or kinetic, he said, some is in the cyber arena, and some is in the gray space in between.
In it for the information
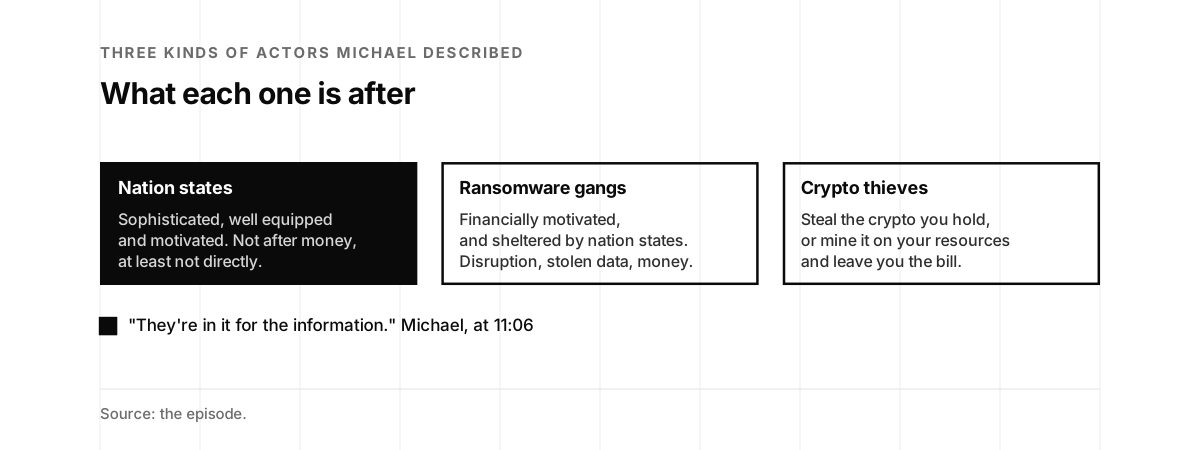
The first kind of actor he described is the nation state: sophisticated, well equipped and motivated.
“and they’re not after it for financial gain, at least not directly.”
Michael Moore, at 10:41
They try to break in and steal personal data, code, product designs and commercial data, anything of strategic value to their nation in a hostile scenario.
“They’re in it for the information.”
Michael Moore, at 11:06
Trevor Hilligoss, a former FBI agent, put the weight elsewhere on episode 86: on the motivated criminal with time, a little money and just enough skill.
Double extortion
The second kind is financially motivated, most often a ransomware gang. But, he said:
“the ransomware gangs don’t exist in a vacuum.”
Michael Moore, at 11:14
They operate under official or tacit protection from nation states less friendly to the West, he said, and they’re about disruption, stolen data and money. He had just written about them for the ACC with two colleagues from Lacework, its chief information security officer Lea Kissner and its field CISO Merritt Baer. Their article, “Don’t Let Your Company’s Reputation be Held for Ran$om,” ran on March 5, 2024 (ACC). Ransomware is malware that holds a victim’s data hostage until a ransom is paid, by encrypting it, by stealing it and threatening to publish it, or both (Wikipedia). The gangs move fast, he said.
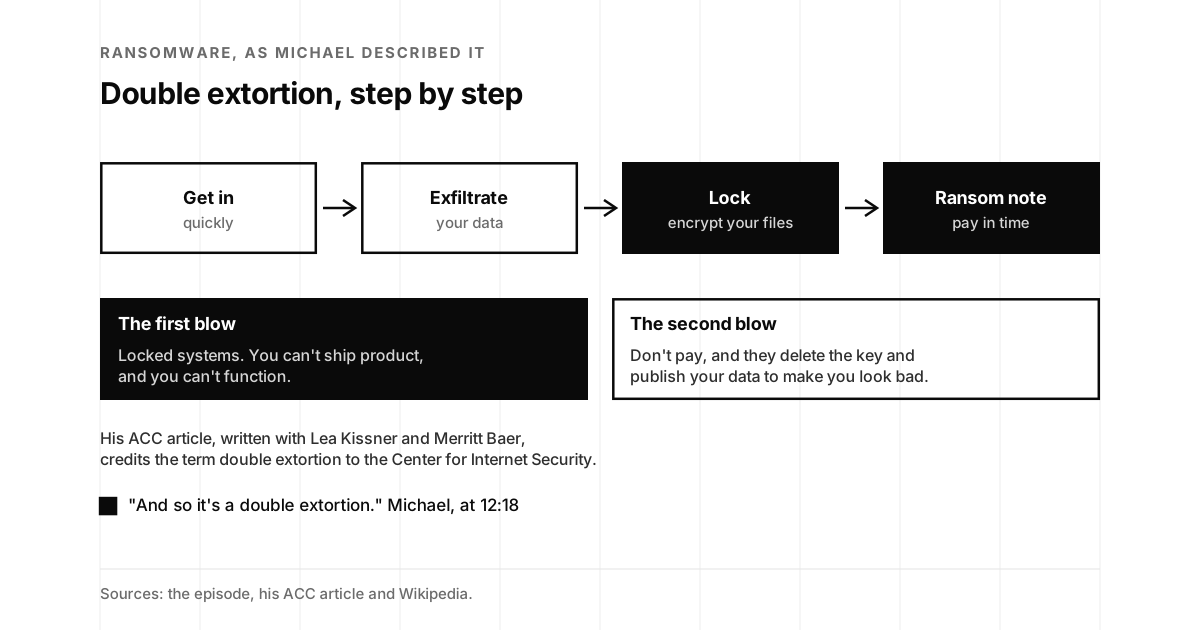
“They want to exfiltrate your data very quickly.”
Michael Moore, at 12:02
Then they encrypt or lock your files and put up a ransom note. Pay in time, or they delete the key and publish your data.
“And so it’s a double extortion.”
Michael Moore, at 12:18
The locked systems are the first blow, an immediate problem:
“because you can’t ship product, you can’t function.”
Michael Moore, at 12:26
His article credits the term double extortion to the Center for Internet Security, and adds the other half of the business model: ransomware sold as a service to affiliates who run the attacks. Damon Fleury of SpyCloud described the access that comes before a ransom event on episode 60.
Going after hospitals
The damage goes past money, he said. Some companies never recovered their data and shut down, and people lost paychecks.
“there are ransomware actors who are indiscriminate and who are going after hospitals.”
Michael Moore, at 12:56
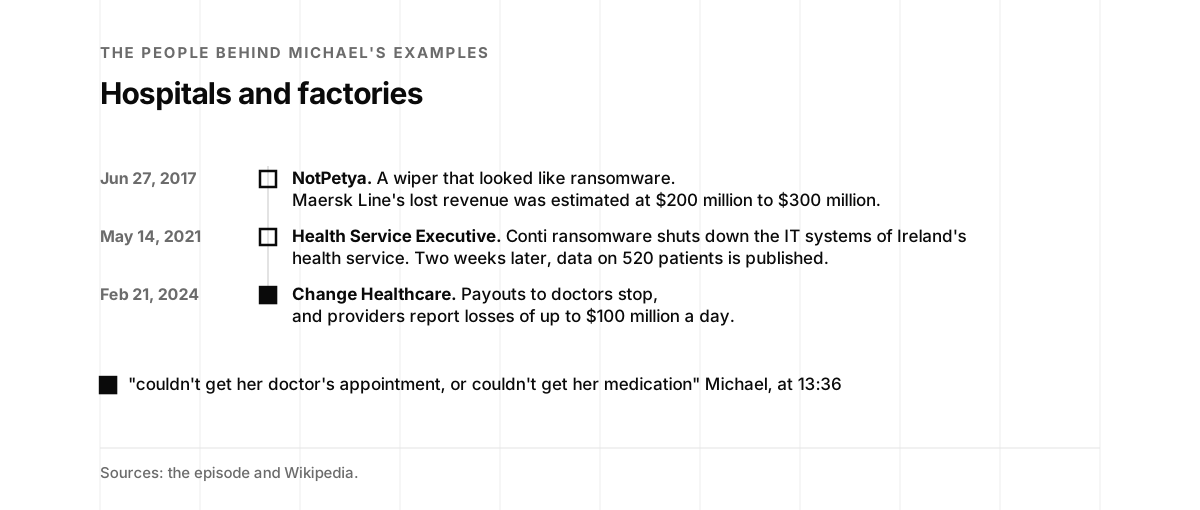
He mentioned UnitedHealthcare and a large pharmacy provider. On February 21, 2024, a cyberattack hit Change Healthcare, a payment and revenue cycle company that UnitedHealth Group’s Optum bought in 2022. It stopped payouts to doctors, and providers reported losses of up to $100 million a day. UnitedHealth Group said the attacker presented itself as ALPHV, also known as BlackCat (Wikipedia). Michael also pointed to a national health service that was seriously ransomed a couple of years before. People couldn’t get medical services or missed surgeries, and their health data was stolen. Ireland’s Health Service Executive was hit by Conti ransomware on May 14, 2021, which shut down its IT systems across the country. Two weeks later, it confirmed that data on 520 patients had been published online (Wikipedia). The victims, he said, have nothing to do with the tech or security space, and might not even own a computer. He pictured a grandmother who:
“couldn’t get her doctor’s appointment, or couldn’t get her medication”
Michael Moore, at 13:36
Jon put faces to it: someone’s daughter, someone’s mother.
On episode 60, Damon Fleury named healthcare and insurance as the most targeted industries in SpyCloud’s data, by a wide margin.
Real people, real lives
“This is not just some abstract technical thing.”
Michael Moore, at 13:46
It’s not a bunch of hackers banging on code, he said. In many cases, attacks have led to serious health problems and deaths, when people couldn’t get treatment or an ambulance couldn’t bring them into a hospital. Then he added a third kind of actor, after money by other means: stealing the crypto you hold.
“or to use resources to mine crypto and stiff you at the bill.”
Michael Moore, at 14:17
Some of that money funds crime, he said, or even weapons programs. He named the NotPetya attack, directed at Ukraine. It began on June 27, 2017, using a new variant of the Petya malware. Maersk Line was among the companies hit outside Ukraine, and its business interruption was estimated at $200 million to $300 million in lost revenue. NotPetya looked like ransomware, but with no way to decrypt, it worked as a wiper, and a White House assessment put the total damage above $10 billion (Wikipedia). Michael’s example was the factory floor.
“People can’t work in the factory because the parts don’t arrive”
Michael Moore, at 14:48
People get furloughed and miss a paycheck or two, he said. It’s up to everyone in the security industry to prevent and block these attacks, call out the attackers, and raise people’s awareness of how to protect their data and their privacy. Suha Can of Grammarly told the story of the leaked exploits behind WannaCry and NotPetya on episode 52.
A positive impact on someone’s life
Jon said no pressure for the security community listening. Michael called it a shared mission: to keep people’s lives, personal data and dignity safe. Some of the stolen data is personal and sensitive, things people expect to stay private about their lives or their health. It gets stolen, and:
“it’s dumped on the dark web for anyone to peruse.”
Michael Moore, at 15:46
“That’s not okay.”
Michael Moore, at 15:49
Jon added that this information is bought and sold. Then he shared the test he uses every once in a while. He asks himself:
“is what I’m doing having a positive impact on someone’s life?”
Jon McLachlan, at 15:56
It doesn’t matter whose life, he said: a fellow engineer, a business leader, an investor, a customer, a salesperson or the security community. If the answer is no, he steps back and asks why. Michael said most people in the field are out to do good, by securing the systems, networks and devices we all use.
“Any one of those victims could be our spouse, a grandparent, a parent, a child, relative.”
Michael Moore, at 16:46
It’s someone’s child, Jon said.
Every day is different
Jon asked what a typical day looks like for a chief privacy officer. That’s a great question, Michael said, because:
“every day is different.”
Michael Moore, at 17:05
“I wear many hats.”
Michael Moore, at 17:06
Privacy is one of them. He gets up early, and since he supports Europe, the first coffee goes with a check on what’s going on there.
“is that GDPR that you’re checking?”
Jon McLachlan, at 17:26
That’s one of the things, he said, along with general security questions, transactions, deals, and requests from customers and the sales team. On a given day he covers patents, trademarks, open source, security and sales questions, buy-side and sell-side transactions, privacy requests, speaking and writing, and compliance questions about employment or export. His base is intellectual property and privacy, where he grew up as an attorney.
“I’m generally much more of a generalist these days, covering whatever comes in.”
Michael Moore, at 18:22
“Ultimately, we’re there to take care of our customers.”
Michael Moore, at 18:30
More and more of his time went to customers and partners, educating, training and sharing what he learned, like what he had just heard at the ACC summit.
Good at threat detection
Jon asked what Lacework is famous for.
“One thing we’re traditionally known for is being really good at threat detection.”
Michael Moore, at 19:17
That’s where Lacework grew up, he said, and the technology is well protected and patented.
“But a lot of it is around very careful and thoughtful early detection of intruders in your system.”
Michael Moore, at 19:33
When Fortinet completed the acquisition that August, it called Lacework “a cloud security and cloud-native application protection platform (CNAPP) trailblazer” (Fortinet).
Four business days
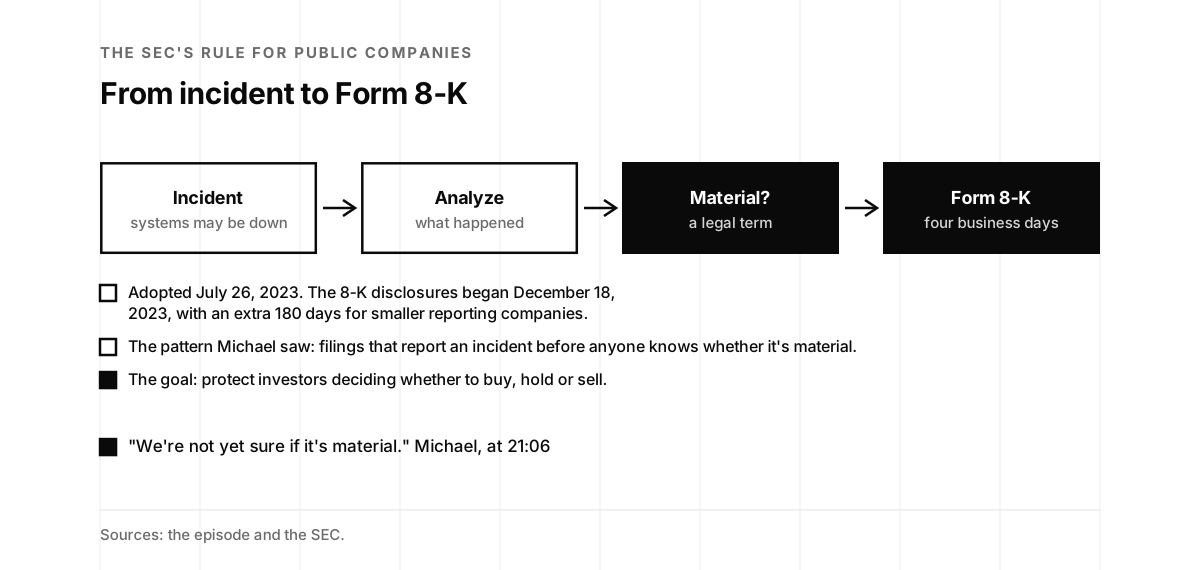
Early detection was becoming a necessity, he said, because of the SEC’s new cyber incident reporting rules. After an incident, a public company has to analyze it and decide whether it is material, a legal term the SEC defines:
“and then, within four business days, report to the SEC regarding what has happened.”
Michael Moore, at 20:09
The SEC adopted the rules on July 26, 2023. Form 8-K disclosure of a material cybersecurity incident is generally due four business days after the company determines the incident is material, and the 8-K requirement began on December 18, 2023, with an extra 180 days for smaller reporting companies (SEC). Michael described the moment that decision gets made, in the middle of a ransomware attack:
“your systems are down, your email is not working, your Slack’s not working”
Michael Moore, at 20:22
You can’t get into your records or see what’s going on in your company, he said, and you still have to make a hard call about materiality and file within a tight window. He had seen a pattern in the first months under the rule. Companies filed to say they had an incident:
“We’re not yet sure if it’s material.”
Michael Moore, at 21:06
That’s okay, he said, because at least they flag that something happened.
“But the intent of the rule, the SEC’s goal, is to protect investors.”
Michael Moore, at 21:11
Investors need enough to decide whether to buy, hold or sell. A filing that says there was an incident, with no word on materiality, doesn’t give them that.
“That just means something happened.”
Michael Moore, at 21:41
Change Healthcare was one of the first big tests. The day after the attack, on February 22, 2024, UnitedHealth Group filed a notice with the SEC (Wikipedia). Kayne McGladrey walked through what the SEC asked public companies to disclose on episode 56.
Detect them early
More detail sooner is good, he said. The best scenario is better still:
“when the bad actor gets into your systems, you detect them really early.”
Michael Moore, at 21:56
If you can’t detect them early, he said:
“at least limit what they can do”
Michael Moore, at 22:04
Do those two things well, and you’re less likely to reach the point of deciding materiality at all.
Breadcrumbs below the threshold
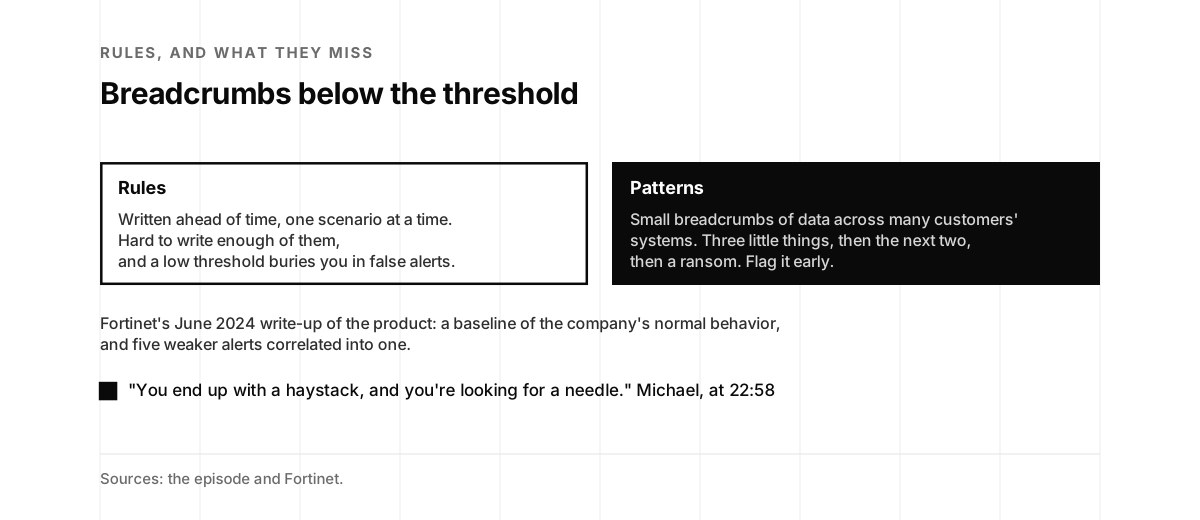
Lacework’s strength, he said, is catching intrusions early. He described a feature that takes lots of little breadcrumbs of data, each too small to cross the threshold of traditional rules-based security, and puts them together. Most traditional security uses rules, he said, and rules have helped in the past. The trouble is coverage:
“it’s generally very difficult to write enough rules to catch every scenario.”
Michael Moore, at 22:45
Set the trigger threshold low enough to catch more, and false alerts bury you.
“You end up with a haystack, and you’re looking for a needle.”
Michael Moore, at 22:58
Lacework watched many customer systems, he said, and learned the patterns that come before an attack. Three little things happen, and then:
“usually the next two things happen, and then you get ransomed.”
Michael Moore, at 23:17
Flag the pattern early, and the customer learns that someone has entered their systems. Two months after this episode, Fortinet’s blog told how the product, by then called Lacework FortiCNAPP, caught an accidental insider: it built a baseline of the company’s normal behavior and correlated five weaker alerts into one (Fortinet).
Low and slow
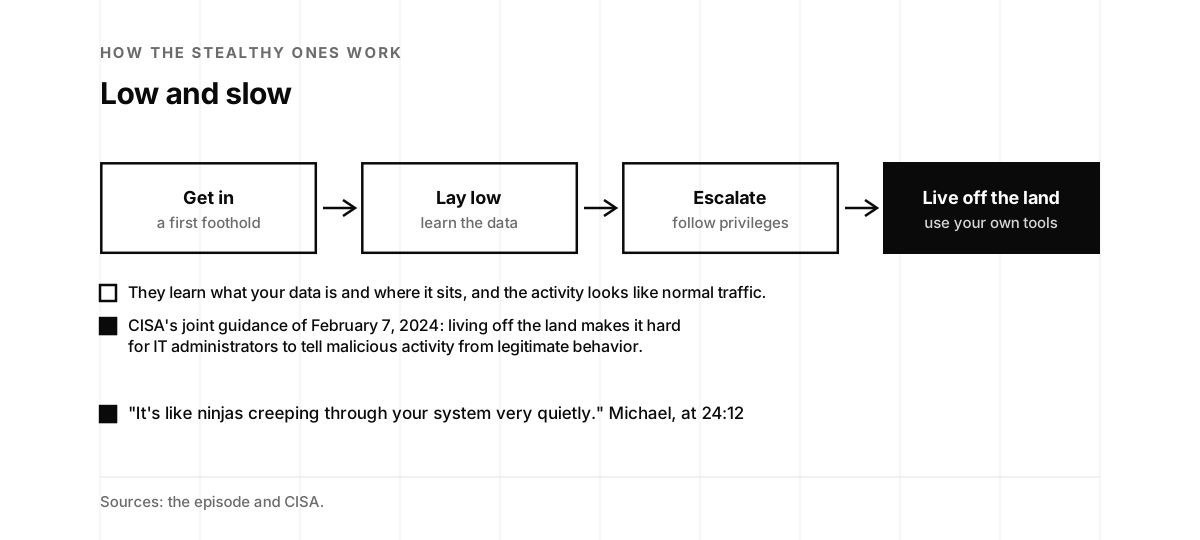
The nation-state actors and ransomware gangs are smart and stealthy, he said. They get in and:
“lay low and slow”
Michael Moore, at 23:39
They spy across the system slowly, learning and observing.
“They’ll learn what your data is, where it sits.”
Michael Moore, at 23:45
They follow privilege escalation.
“They’ll use a lot of your existing tooling.”
Michael Moore, at 23:51
He pointed to CISA’s new guidance on living off the land: using the tools already in your systems, so the activity looks like normal traffic. CISA published it on February 7, 2024, as joint guidance with the NSA, the FBI and seven other US and allied agencies. It says the technique keeps working “with little to no investment in tooling by malicious cyber actors” (CISA).
“It’s like ninjas creeping through your system very quietly.”
Michael Moore, at 24:12
Jon offered an image of his own: shoes doing the creeping.
“so it sounds like familiar traffic.”
Jon McLachlan, at 24:16
Michael liked it. That’s exactly what it is, he said: they use your shoes to creep through your system, and Lacework could pick that up early.
Out of band
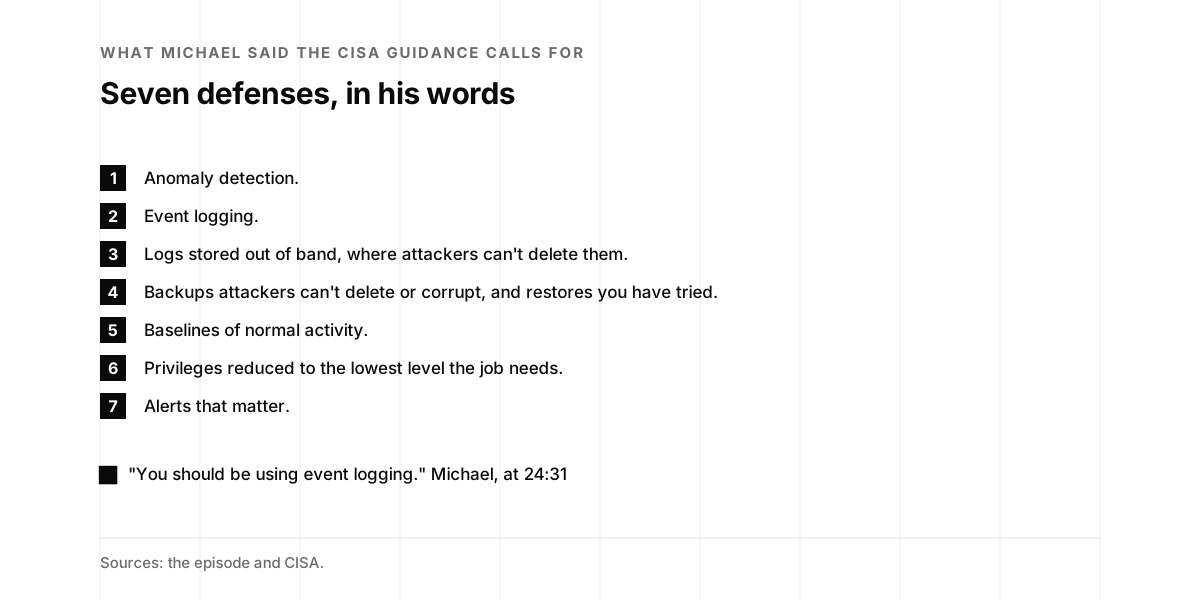
He listed what the CISA guidance calls for, starting with two things:
“you should be using anomaly detection.”
Michael Moore, at 24:29
“You should be using event logging.”
Michael Moore, at 24:31
Anomaly detection is finding the rare events that deviate from the rest of the data (Wikipedia). Detect the bad actor early, he said, and keep the evidence somewhere they can’t reach.
“You want to store your logs and make sure your logs are protected”
Michael Moore, at 24:48
That means a safe, out-of-band location, where attackers can’t delete them.
“In many cases, they’ll go in and they’ll delete your backups, so you can’t restore from backups.”
Michael Moore, at 24:54
“Or they’ll corrupt them, so the backups will exist”
Michael Moore, at 24:59
You only find out when you try to restore, he said.
“And they’ll delete event logs.”
Michael Moore, at 25:08
With the logs stored locally and deleted, it’s hard to figure out what happened. Lacework stored them separately and securely, he said, so attackers couldn’t wipe them. Our guide to immutable backups covers why ransomware goes after backups first, and the scorecard on Alan Braithwaite’s episode 50 page asks whether your logs would survive an incident.
Accounts nobody uses
CISA also recommends baselines of normal activity, he said, and least privilege:
“reduce your privileges to the lowest level necessary to the job.”
Michael Moore, at 25:25
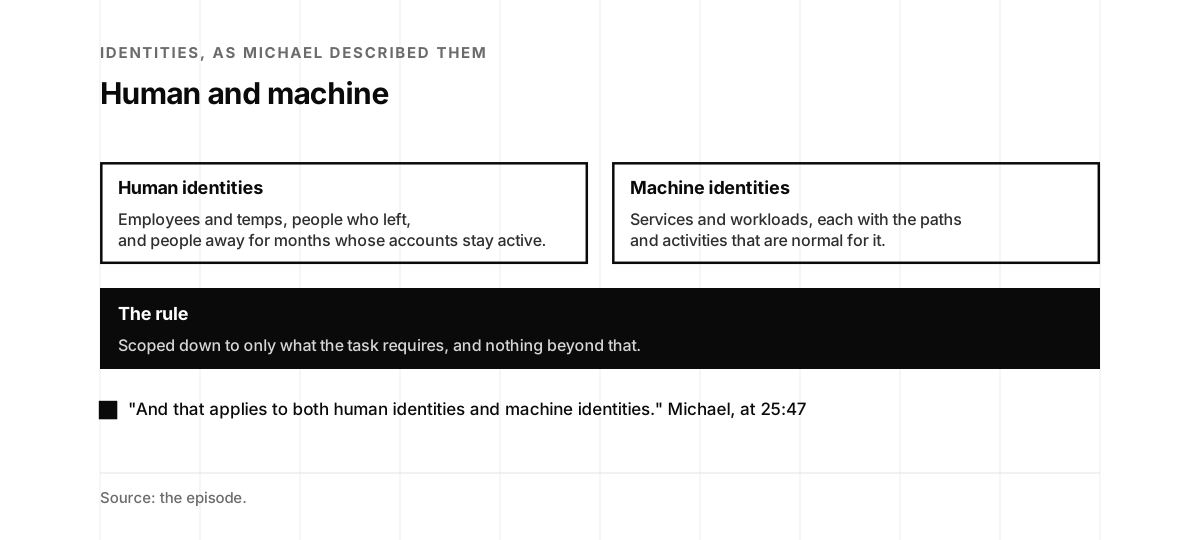
Lacework’s identity tooling looked at each identity, so a company grants only what a task needs and removes or scopes down the ones that are overly broad.
“And that applies to both human identities and machine identities.”
Michael Moore, at 25:47
Many companies keep accounts open for people who have left, he said:
“and there isn’t always good discipline around shutting those down when the person leaves.”
Michael Moore, at 25:56
Someone goes away for two or three months and comes back for two or three months:
“and the account stays active and unused during that time.”
Michael Moore, at 26:04
Keep every identity tightly controlled, he said, and:
“scoped down to only that which is required for the task, and nothing beyond that.”
Michael Moore, at 26:13
Alerts that matter
The last thing on his CISA list:
“you want to make sure you have alerts that actually matter.”
Michael Moore, at 26:19
People across the industry are buried under alerts, he said, and the needle sits in multiple haystacks of them.
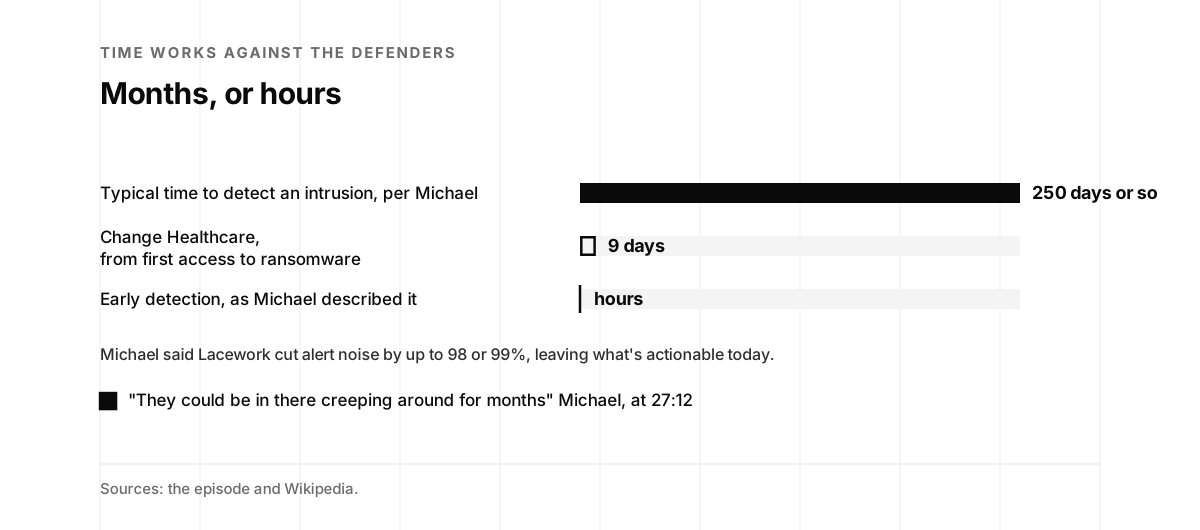
“one of the things we do is really tune down the alert noise, up to 98 or 99%”
Michael Moore, at 26:45
That leaves what’s actionable today, he said. And time works against the defenders.
“And typically, it’ll take 250 or so days to detect an intrusion in a system”
Michael Moore, at 27:02
Especially, he said, against a nation-state actor using the low-and-slow technique.
“They could be in there creeping around for months”
Michael Moore, at 27:12
Jon said they’re doing recon: looking at things and figuring out what’s worth taking. Michael agreed, and said you have to catch them early. Early detection can catch them within hours of getting in, he said, and block them or shut off the system. On episode 47, Clea Ostendorf asked whether anyone will act on an alert at all. The calculator below puts a number on the time an intruder gets.
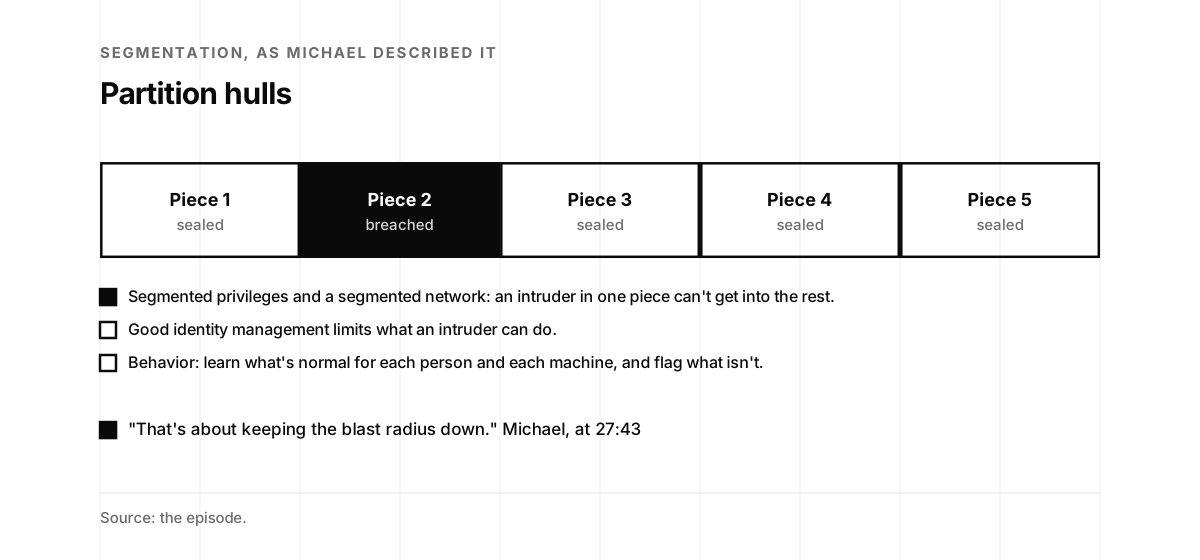
Partition hulls
Good identity management limits what an intruder can do, he said.
“That’s about keeping the blast radius down.”
Michael Moore, at 27:43
Segment the privileges and segment the network:
“such that even if they get into one piece, they can’t get into the rest.”
Michael Moore, at 27:51
He compared it to ships and submarines with multiple partition hulls:
“where if one gets breached, you can seal it off”
Michael Moore, at 27:59
“And you can get home.”
Jon McLachlan, at 28:03
Identity, segmentation and privilege management limit the damage and keep attackers from creeping through the whole infrastructure, he said. Andrew Rubin of Illumio built a company around the same question, what happens when the perimeter misses, on episode 88. Our blast radius playbook covers what a startup can do once someone is in.
Caveman code
Then you watch behavior, he said: what’s normal for each user, each entity and each machine. That matters when someone gets in:
“through a compromised user credential, which might be a valid credential”
Michael Moore, at 28:35
He used himself as the example.
“I’m an engineer. I can write code.”
Michael Moore, at 28:42
“I’d probably write caveman code if I wrote it today, because it’s been so long since I’ve done it.”
Michael Moore, at 28:44
In his role, he shouldn’t be poking around in the company’s code or making changes there. If he tried, it should get flagged, because he has no business doing that.
Machines have their own normal, he said: paths they talk on and activities they engage in. Machine learning watches both and flags what isn’t normal. The attackers this is for are determined, skilled and stealthy.
“This is not just some kid using social engineering”
Michael Moore, at 29:27
Where the rubber hits the road
“This is real security. This is where the rubber hits the road.”
Jon McLachlan, at 29:34
Jon had a story from Pure Storage, where the team used Lacework. During a production outage or emergency, he had to get into a box. Five seconds after he logged in over SSH, a teammate from the security team sitting next to him turned and asked whether he had just gone into that box. Jon asked if he was looking at his screen. He wasn’t. It was Lacework, flagging the access as unusual.
Michael said that’s the point.
“It’s hard to write rules for every possible scenario”
Michael Moore, at 30:19
Against skilled, determined attackers with unlimited resources and people, rules alone won’t cut it, he said. Learning what’s normal in the environment and flagging the rest is, in his view, the most effective way to find an intruder before the data leaves. Andrew Gontarczyk, then Pure Storage’s chief information security officer, was the guest on episode 2.
A healthy security posture
Jon said the new controls for publicly traded companies lined up with what a healthy security operation needs anyway. They overlap with a SOC 2, Type 1 or Type 2, and with ISO 27001, he said. Our guide to what SOC 2 is covers the first. Michael took it back to 2018, when GDPR came into force.
“there was a mad scramble by everybody getting ready for GDPR”
Michael Moore, at 31:24
Consultants everywhere offered GDPR services. What GDPR did, he said, was use the European Union’s market power:
“we’re going to use our market power to force change for good.”
Michael Moore, at 31:40
Some people alleged that the motive was to slow down US tech companies, he said. He thinks improving privacy in general is a good thing.
“it forced companies who wanted to do business with or in Europe to take privacy seriously.”
Michael Moore, at 31:57
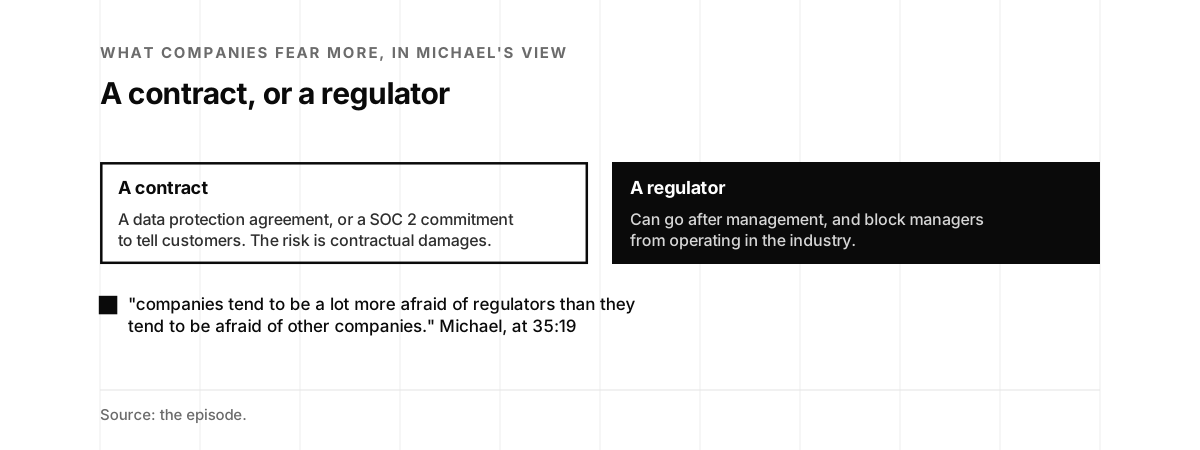
Before that, many companies hadn’t taken it seriously, because nothing forced them to. GDPR combined the threat of large fines and regulatory action with the embarrassment of a damaged reputation. The European Union adopted it on April 14, 2016, and it took effect on May 25, 2018. Fines can reach €20 million or 4% of a company’s worldwide annual turnover, whichever is greater (Wikipedia).
All of a sudden, he said, companies started taking privacy seriously. The environment is much healthier now, and companies follow the rules much better than they did five or six years earlier.
From nice-to-have to need-to-have
“the EU just did it again with all of those AI regulations.”
Jon McLachlan, at 32:42
“I will commend the EU for what they’re doing here.”
Michael Moore, at 32:46
“They’re also doing it for security.”
Michael Moore, at 32:48
He named two new laws. The first was NIS2, a European Union directive for protecting digital infrastructure, critical infrastructure in particular. It broadened the sectors the earlier NIS Directive covered and updated incident reporting and oversight. Member states had to put it into national law by October 17, 2024, and the old directive was repealed the next day (Wikipedia). Michael’s list of sectors ran from energy, transport, banking and water to cloud, telecom and data centers, then space, postal service, waste management, chemicals and food manufacturing. Companies that want to do business with or in Europe have to follow it, and its rules are prescriptive: security technology, risk analysis, vulnerability analysis, AI for detecting anomalies. Good security hygiene:
“has gone from being a nice-to-have or recommendation to a need-to-have, required to do business in Europe.”
Michael Moore, at 34:03
The second was DORA, the Digital Operational Resilience Act, for finance. It requires financial entities to strengthen their digital operational resilience, and it covers their ICT suppliers too (Wikipedia). It entered into application on January 17, 2025, for 20 types of financial entities and their ICT third-party service providers (EIOPA). Michael called its rules for banking, brokerages and insurance almost a superset, with a lot of interest from partners and customers.
“The US is following suit.”
Michael Moore, at 34:11
The SEC rule makes companies tell investors about material incidents, he said, and it also tells the SEC that these attacks are happening. The only way to target them is to understand the pattern.
“Where are the attacks happening? What sectors are they in?”
Michael Moore, at 34:34
More afraid of regulators
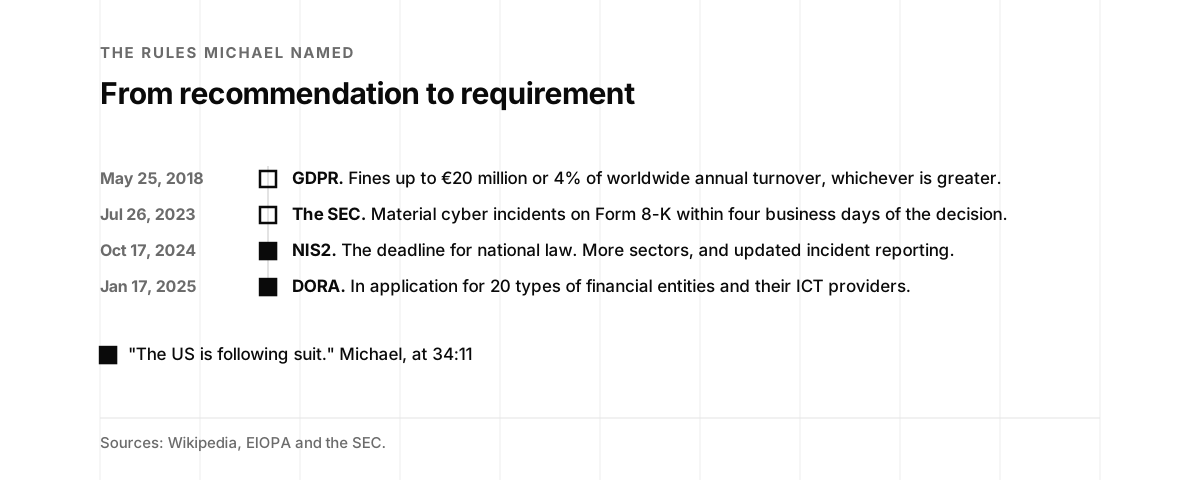
Jon said businesses selling to businesses already sign data protection agreements, especially in Europe, with clauses on how fast to disclose. A SOC 2 often comes with a commitment to tell customers about a security event. It’s crazy that it takes legislation, he said, to bring that to consumers. Michael agreed, and added a reason.
“companies tend to be a lot more afraid of regulators than they tend to be afraid of other companies.”
Michael Moore, at 35:19
“if you agree to something, you should always comply with what you agree to.”
Michael Moore, at 35:26
“It’s a contract, yeah.”
Jon McLachlan, at 35:31
A regulator can go after management, he said, and block managers from operating in the industry.
“that suddenly has much greater teeth than the prospect of contractual damages”
Michael Moore, at 35:45
He expected management to take security far more seriously than before.
“And security has often been considered, oh, it’s a cost, it’s expensive.”
Michael Moore, at 36:01
It’s a lot cheaper, he said, than paying a ransom, having your name dragged through the papers, and watching customers lose trust and take their business elsewhere. Our guide to the security exhibit your startup signed walks through what those contract clauses promise.
A growth opportunity
Jon said he often runs into the view that security is a cost center, especially from the business side of the house.
“I often find it’s much more productive to see security as a growth opportunity for the business.”
Jon McLachlan, at 37:32
Dot your i’s and cross your t’s, he said, and more markets open: you can sell into healthcare, defense and finance. Michael agreed, and added one more gain:
“you build up customer trust.”
Michael Moore, at 37:52
At Lacework, he said, privacy by design came up again and again. He worked closely with the engineering and tech teams to build products that protect privacy. Privacy by design is a systems engineering approach first developed by Ann Cavoukian, formalized in a 1995 report with the Information and Privacy Commissioner of Ontario and Dutch partners, and published as a framework in 2009 (Wikipedia). Michael’s article “Product Privacy Done Right,” written with Lea Kissner and Alan Mulvaney of Lacework, ran the day before the ransomware piece, on March 4, 2024. It points to the GDPR’s requirement of data protection by design and by default, and argues that good design limits the blast radius when attackers get past security (ACC). Abhi Sharma described Relyance AI’s founding pair, a privacy lawyer and an engineer, on episode 70.
Two sides of the same coin
Michael said Lacework took that philosophy seriously.
“I personally think security and privacy are two sides of the same coin.”
Michael Moore, at 38:10
“They absolutely are.”
Jon McLachlan, at 38:14
Then came the line at the top of this page: security is what you can do with access to the data, and privacy is what you should do with it. He closed by asking what the right thing to do is.
As soon as you have private data
Jon said founders often ask him when a growing startup should start grappling with security, and maybe pull in a security team. His answer:
“it’s as soon as you have private data.”
Jon McLachlan, at 38:39
“That’s when you need to take that seriously.”
Jon McLachlan, at 38:42
Michael drew the line between economic data, such as code, and data on people: employees, customers, prospects or users. They’re entrusting you with it, he said.
“You need to handle it properly.”
Michael Moore, at 38:58
If you don’t, he said, you violate their trust and put your company’s reputation at risk. Jon asked Kayne McGladrey the same question about hiring a security leader on episode 56, and our post on hiring a fractional CISO lists seven questions to ask before you sign one.
At scale, repeatedly
Jon asked what success looks like for Michael’s team and for Lacework. Keep customers secure, keep partners secure, and keep their customers’ data secure, Michael said, against nation-state attackers, ransomware gangs, crypto miners, digital vandals and anyone else trying to get in and disrupt their systems.
Do it at scale, do it repeatedly, and do it as widely as possible, he said, and in a way that protects people, because:
“it all goes back to people at the end”
Michael Moore, at 39:58
That means keeping trust, he said, and making sure data is protected and used appropriately, personal data and economic data alike: code, trade secrets and confidential data.
Get out from behind your keyboard
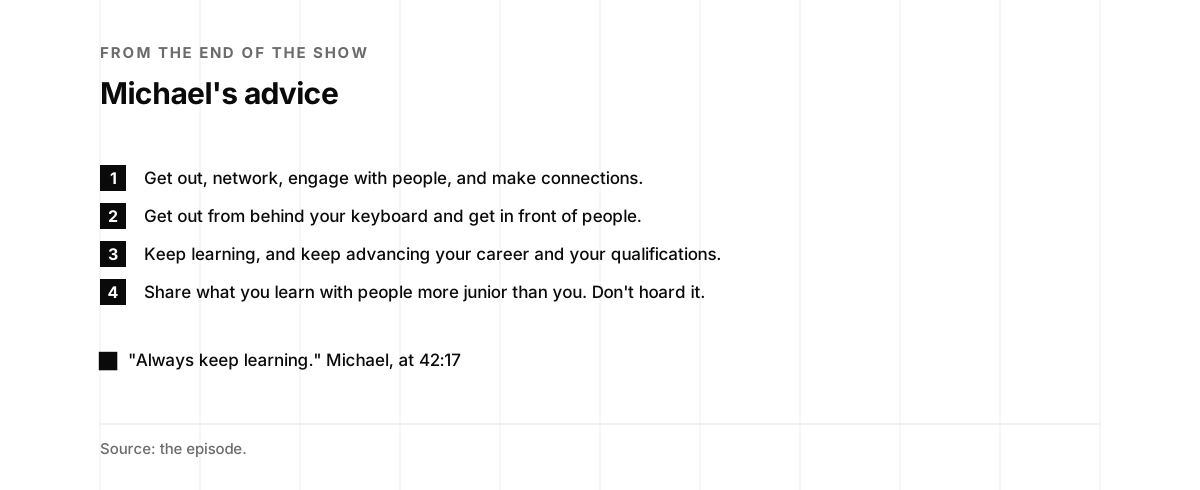
Jon asked what Michael would tell a younger version of himself. He had been an introvert, he said, and wasn’t active in networking, speaking or publishing. His advice for anyone at any stage of a career:
“get out, network, engage with people, make connections”
Michael Moore, at 40:51
Technology is great, he said, and the business is about people, who you know, and your ability to help and influence them.
“get out from behind your keyboard and get in front of people.”
Michael Moore, at 41:08
Jon agreed completely, and shared the trick he has used over the years:
“if you take that mentality that you do bring something interesting to the table, and that other people would love to meet you, then it becomes so much easier.”
Jon McLachlan, at 41:16
He had been one of those introverted engineers himself, he said. Michael said he enjoys educating people on the topic.
“I’d probably be a lecturer or teacher somewhere”
Michael Moore, at 41:50
Just without the grading, he said. He gave Sasha and Jon the same answer about being an introvert on episode 73.
Don’t hoard them
Jon asked for final words of wisdom.
He mentors younger attorneys and students interested in law, he said, and his advice to them starts with learning.
“Always keep learning.”
Michael Moore, at 42:17
He writes to share what he has learned, he said, and named the two articles: “Product Privacy Done Right” and the ransomware piece. More of his writing, on intellectual property, legal operations and more, is on his LinkedIn. When you build skills or knowledge, or just learn a useful tip, share it:
“Don’t hoard them.”
Michael Moore, at 42:56
Share them with people more junior, he said, who can learn from them.
Jon’s version: network, use LinkedIn, and connect with Michael. Michael said he enjoyed working with Jon in the past, and it was great to reconnect.
What happened after the tape
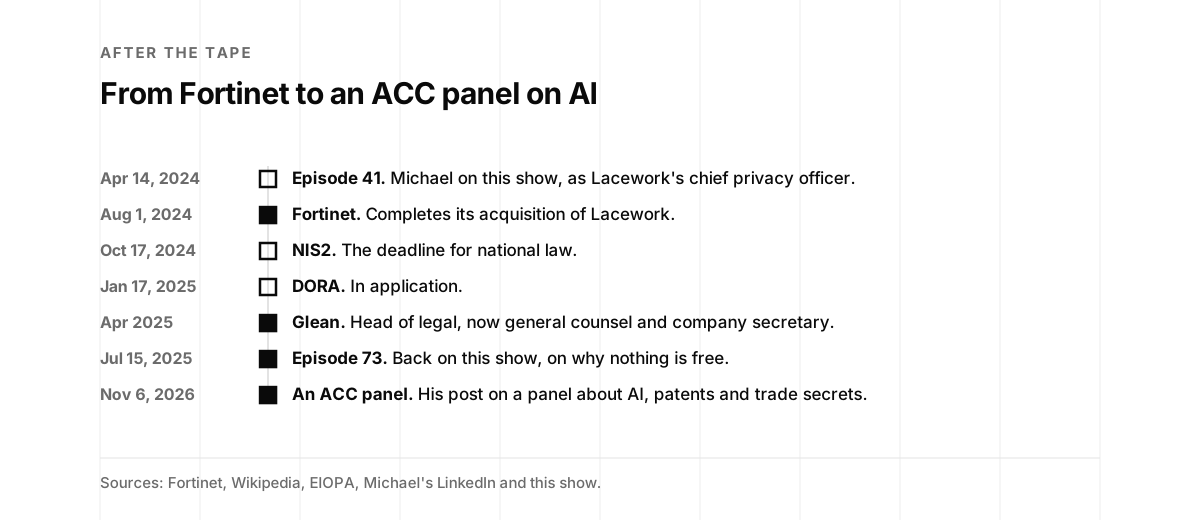
Fortinet bought Lacework. Fortinet completed the acquisition effective August 1, 2024, and said it would fold Lacework’s cloud-native platform into the Fortinet Security Fabric (Fortinet). Wikipedia lists the price as undisclosed (Wikipedia). Michael’s LinkedIn shows him leading the privacy program through the acquisition (LinkedIn).
Nine days inside Change Healthcare. UnitedHealth Group’s chief executive later testified that the attackers first got into Change Healthcare’s systems on February 12, 2024. They moved laterally for nine days and took about six terabytes of data before they deployed ransomware on February 21. In 2025, UnitedHealth Group estimated that the attack affected nearly 192.7 million people (Wikipedia). On the tape, Michael put the usual time to detect an intrusion at 250 days or so, and said early detection can catch an intruder within hours.
The EU deadlines arrived. Member states had to put NIS2 into national law by October 17, 2024 (Wikipedia), and DORA entered into application on January 17, 2025 (EIOPA).
Glean, and episode 73. Michael joined Glean as head of legal in April 2025, and his title there is now general counsel and company secretary (LinkedIn). On July 15, 2025, he came back to the show with Jon and Sasha Sinkevich to talk about what free AI tools cost.
His articles found a new home. Both ACC links from the show notes now go to ACC’s Corporate Counsel Now site, with his Glean title on the byline (ACC).
His post on AI and inventors. On November 6, 2026, Michael wrote about an Association of Corporate Counsel panel the day before, “The AI-Enhanced Inventor: How Artificial Intelligence Could Redefine Patentability and Trade Secret Protection.” His takeaways were to document the human contribution behind an invention, look again at the choice between a patent and a trade secret, and govern the AI tools engineers use. On the tape, he got into law through inventing.
Michael on an ACC panel about AI, inventorship and trade secrets.
Michael Moore · November 6, 2026
More on this show. Kayne McGladrey read the first SEC filings under the new rules on episode 56. Damon Fleury of SpyCloud talked about the access before a ransom event on episode 60, and Andrew Rubin of Illumio about stopping small problems from becoming catastrophes on episode 88. On the blog, Immutable Backups and Ransomware Recovery covers why attackers go after backups first, and Once They’re In covers shrinking the blast radius.
Did you catch it? A seven-question quiz
Seven questions from the episode. Each answer links the moment in the transcript.
Quiz · seven questions
Did you catch it?
Pick an answer to see whether you caught it.
-
What does Michael call intellectual property?
b. "That's really the lifeblood of an innovation economy." Transcript, 4:00.
-
Which actor did Michael say is in it for the information?
a. "They're in it for the information." Transcript, 11:06.
-
Besides locking your files, what does a ransomware gang threaten?
c. "And so it's a double extortion." Transcript, 12:18.
-
Once a public company decides an incident is material, how long does it have to report it to the SEC?
b. "and then, within four business days, report to the SEC regarding what has happened." Transcript, 20:09.
-
Where did Michael say your logs should live?
a. "sort of out-of-band location" Transcript, 24:51.
-
How long did Michael say it typically takes to detect an intrusion?
c. "And typically, it'll take 250 or so days to detect an intrusion in a system" Transcript, 27:02.
-
Security is about what you can do with access to the data. What is privacy about?
b. "Privacy is about what you should do if you get access to the data." Transcript, 38:19.
Would you catch them early?
Eight questions on whether you would see an intruder early, and keep them in one piece. Each tip quotes the tape or paraphrases it, and links its section.
Scorecard · eight questions
Would you catch them early?
Answer for your company as it runs today. If two answers fit, pick the lower one.
-
Do you know what normal looks like for your users and machines?
- No
- For some systems
- Yes, with baselines we keep current
CISA also recommends baselines of normal activity, Michael said. See Accounts nobody uses.
-
Where do your event logs live?
- On the systems they describe
- In one place an admin could still delete
- Out of band, where an intruder can't delete them
Michael's advice: keep logs where an intruder can't delete them. See Out of band.
-
When did you last restore from a backup?
- Never
- Over a year ago
- This quarter, and it worked
Michael's warning: you only find out a backup is corrupted when you try to restore it. See Out of band.
-
When someone leaves, how fast are their accounts shut down?
- Nobody checks
- Within a few weeks
- The day they leave, temps included
"and there isn't always good discipline around shutting those down when the person leaves." See Accounts nobody uses.
-
Are machine identities scoped as tightly as human ones?
- No
- Some of them
- Yes, each to its task
"And that applies to both human identities and machine identities." See Accounts nobody uses.
-
If an intruder gets into one system, how far can they go?
- Almost anywhere
- Some segments are walled off
- The breached piece is sealed off from the rest
"such that even if they get into one piece, they can't get into the rest." See Partition hulls.
-
Do your alerts get acted on?
- Most of them are noise
- Some get acted on
- We tune them to what's actionable
"you want to make sure you have alerts that actually matter." See Alerts that matter.
-
If you had an incident today, could you decide what it means and tell the people who need to know, on time?
- No plan
- A plan nobody has tested
- Yes: owners, deadlines and a practiced runbook
"and then, within four business days, report to the SEC regarding what has happened." See Four business days.
An intruder could sit for months before anyone noticed. Start with logs an intruder can't delete, and shut the accounts of people who left.
The pieces are there. Next, learn what normal looks like for people and machines, and tune alerts to what you'll act on.
You would likely see an intruder early and keep them in one piece. Keep testing restores, and keep the incident plan practiced.
How long does an intruder get?
Michael put the usual time to detect an intrusion at 250 days or so, and said early detection can catch an intruder within hours. This calculator compares the two.
Calculator
How long does an intruder get?
Two numbers: the days it would take you to notice an intruder today, and the hours it would take with early detection.
An intruder found on day 250 has had about 6,000 hours to learn your systems. Early detection at hour 6 gives them 1,000 times less time, and takes away 249.8 days of looking around.
The 250 days is Michael's figure from the tape for how long detection typically takes, longest against a nation-state actor using the low-and-slow technique. The 6 hours is a placeholder for his point that early detection can catch an intruder within hours: put in your own numbers. For scale, Change Healthcare's attackers moved through its systems for nine days before they deployed ransomware, as in What happened after the tape.
From inventor to chief privacy officer
Michael’s path, the rules and attacks he talked about, and the episodes on this site that pick up the thread. Filter by topic.
Timeline
From inventor to chief privacy officer
- Analog Devices
Michael starts as an applications co-op (LinkedIn).
- Cypress Semiconductor
Applications engineer, and an inventor with about ten patents (LinkedIn, on this page).
- Patent agent
Still at Cypress, now preparing and prosecuting its patents (LinkedIn).
- Morgan Lewis & Bockius
Michael joins the law firm as an associate (LinkedIn).
- Symantec
Corporate counsel for intellectual property, and his start in security (LinkedIn, on this page).
- Rambus
Patent counsel, then vice president of IP and deputy general counsel (LinkedIn).
- Pure Storage
Later deputy general counsel for privacy, sales compliance, product and IP, where his path crossed Jon's (LinkedIn).
- NotPetya
A wiper dressed as ransomware, with damages a White House assessment put above $10 billion (Wikipedia, on this page).
- GDPR
The European Union's privacy regulation takes effect (Wikipedia, on this page).
- Health Service Executive
Conti ransomware shuts down the IT systems of Ireland's health service (Wikipedia, on this page).
- Episode 2
Andrew Gontarczyk, then CISO of Pure Storage, on building a security team (episode page).
- Lacework
Vice president of privacy and IP, then chief privacy officer from December 2023 (LinkedIn).
- The SEC's rules
Material cyber incidents go on Form 8-K within four business days of the materiality decision (SEC).
- Form 8-K begins
The incident disclosures start for most public companies (SEC, on this page).
- Living off the land
CISA and partner agencies publish joint guidance on the technique (CISA, on this page).
- Change Healthcare
Ransomware stops payouts to doctors, nine days after the attackers got in (Wikipedia, on this page).
- Product Privacy Done Right
Michael, Lea Kissner and Alan Mulvaney on privacy by design (ACC).
- Held for ransom
Michael, Lea Kissner and Merritt Baer on ransomware, privacy and compliance (ACC, on this page).
- Episode 41
Michael on the show (Podbean, transcript).
- Fortinet
Fortinet completes its acquisition of Lacework (Fortinet, on this page).
- Episode 56
Kayne McGladrey on what the SEC asked for (episode page).
- NIS2
The deadline for member states to put the directive into national law (Wikipedia, on this page).
- Episode 60
Damon Fleury of SpyCloud on the access before a ransom event (episode page).
- DORA
The financial sector's resilience rules enter into application (EIOPA).
- Glean
Michael joins as head of legal (LinkedIn).
- Episode 73
Michael back on the show, on why nothing is free (episode page).
- Episode 88
Andrew Rubin of Illumio on what happens when the perimeter misses (episode page).
- AI and inventors
Michael on an ACC panel about AI, patents and trade secrets (LinkedIn, on this page).
What to do this week
Five things, in the order of the episode.
- Find out how long you’d take. Ask your team how long the last intruder or test went unnoticed, then put it in the calculator and take the scorecard.
- Move your logs out of reach. Store event logs and backups where an intruder can’t delete them, and test a restore, as in Out of band.
- Shut the accounts nobody uses. Start with people who left, then temps, then machine identities nobody can explain, as in Accounts nobody uses.
- Write down who decides. Name who calls an incident material, and who tells investors, regulators or customers by when, as in Four business days.
- Get help catching them early. Our 24/7 Monitoring & Response watches cloud, network and endpoints with people who respond. Our Counter Business Espionage & IP Protection keeps your roadmap and trade secrets yours. If you want to talk it through, book 15 minutes with us.