
Episode 56 of The Security Podcast of Silicon Valley aired on October 15, 2024, with Jon McLachlan hosting. The guest was Kayne McGladrey, then the field CISO at Hyperproof, a company whose software teams use to run their compliance and risk programs. Jon asked about his background, and the answer started a long way from security.
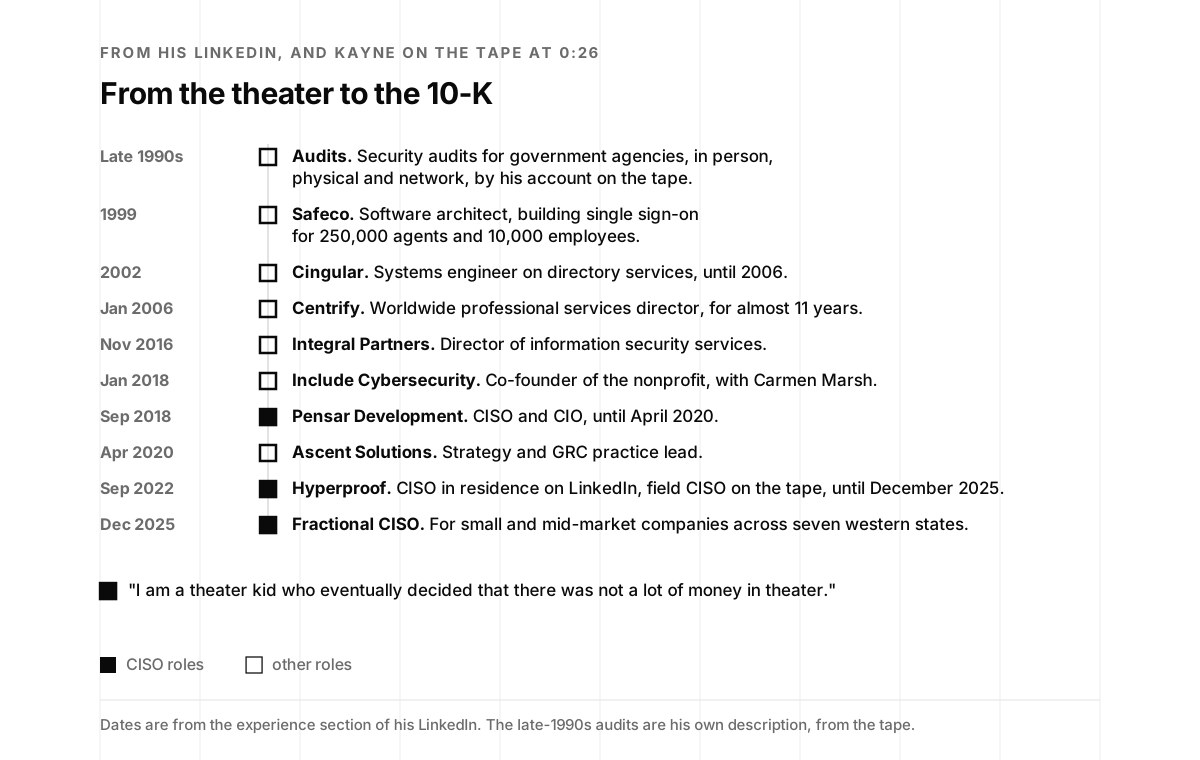
“I am a theater kid who eventually decided that there was not a lot of money in theater.”
Kayne McGladrey, at 0:27
He took what he learned on stage into security work, ran professional services, served as a CISO, and by the time of the recording had picked up one more skill he hadn’t planned on.
“And my special skill that I’ve most recently adopted, and it wasn’t on my bingo card for this year, is reading investor regulatory filings for the SEC in the 10-K.”
Kayne McGladrey, at 1:18
His LinkedIn fills in the years between (LinkedIn). He was a software architect at Safeco Insurance from 1999 to 2001, building single sign-on for 250,000 agents and 10,000 employees, then a systems engineer on Cingular Wireless’s directory services from 2002 to 2006. He spent almost 11 years at Centrify from January 2006, as worldwide professional services director, then ran information security services at Integral Partners from November 2016. From September 2018 to April 2020 he was CISO and CIO at Pensar Development, an industrial design and manufacturing firm with aerospace work, and from April 2020 he led strategy and the GRC practice at Ascent Solutions. He joined Hyperproof in September 2022. Along the way he co-founded Include Cybersecurity with Carmen Marsh, a nonprofit his profile describes as “dedicated to changing the face of cybersecurity professionals.” His headline lists him as a CISSP and a senior member of the IEEE. LinkedIn calls the Hyperproof role CISO in residence, and on the tape he called it field CISO.
The conversation was recorded in March 2024. That fits the tape: Jon mentions Hyperproof’s 2024 benchmark report, which came out on February 23, 2024, and Kayne promises a blog post that went up on March 25. It aired seven months later. Since then the SEC’s case against SolarWinds was dropped, the federal review board Kayne mentions lost its members, Hyperproof published the maturity model he was drafting, and he left Hyperproof at the end of 2025. He now works as a fractional CISO, and his book is out from CRC Press. The last section below covers that.
This page is the rest of it: a section for each part of the conversation with the sources beside it, thirteen figures, fourteen clips from the tape, a LinkedIn card, the full transcript, and four tools: a quiz, a scorecard for whether you could prove your controls run, a calculator for how long a failed control could go unnoticed, and a timeline from the Clue board game to his book.
A word on framing before the sections. Kayne said on the tape that he isn’t a lawyer, and nothing here is legal advice either. The SEC’s rules apply to public companies. The reason a startup should care, as he explained it, runs through its investors, its board members and its biggest customers.
From theater kid to the 10-K
Kayne’s own description of his path was that it doesn’t look like most people’s.
“And I took the improv skills that I’d earned and parlayed that into a cybersecurity career, which is a weird origin story, right?”
Kayne McGladrey, at 0:36
Improvisational theater, per Wikipedia, is the form in which “most or all of what is performed is unplanned or unscripted” (Wikipedia). His first security work sounds closer to that than to a textbook.
“I remember doing security audits, both in person as well as physical security as well as network security for government agencies in the late 90s and making a lot of it up as I go along, which was exciting.”
Kayne McGladrey, at 0:47
He credited a really good team back then, many good teams since and three mentors over his career. The newest skill was the one that set up the episode: reading the annual filings public companies make with the SEC. Form 10-K is “an annual report required by the U.S. Securities and Exchange Commission” (Wikipedia), and he said he could now read one “in about two seconds at a crack.”
Jon suggested it was a different type of singing and dancing, and Kayne agreed that the stage never left him.
“This is true. And I still am very comfortable on stage and with a live audience.”
Kayne McGladrey, at 1:40
His LinkedIn bears that out. For his Hyperproof years it lists “150+ media outlets, 75+ podcasts, and 30+ industry keynotes,” a bi-monthly compliance podcast called Drafting Compliance, and the annual IT benchmark surveys he led.
What the SEC asked for
Jon asked what the new 10-K disclosures are and why Kayne had been reading them. The answer began with how companies had treated the topic until then.
“So the reason I’ve been tracking that is most companies have had this concern over disclosing how or if or what they’re doing around cybersecurity.”
Kayne McGladrey, at 1:52
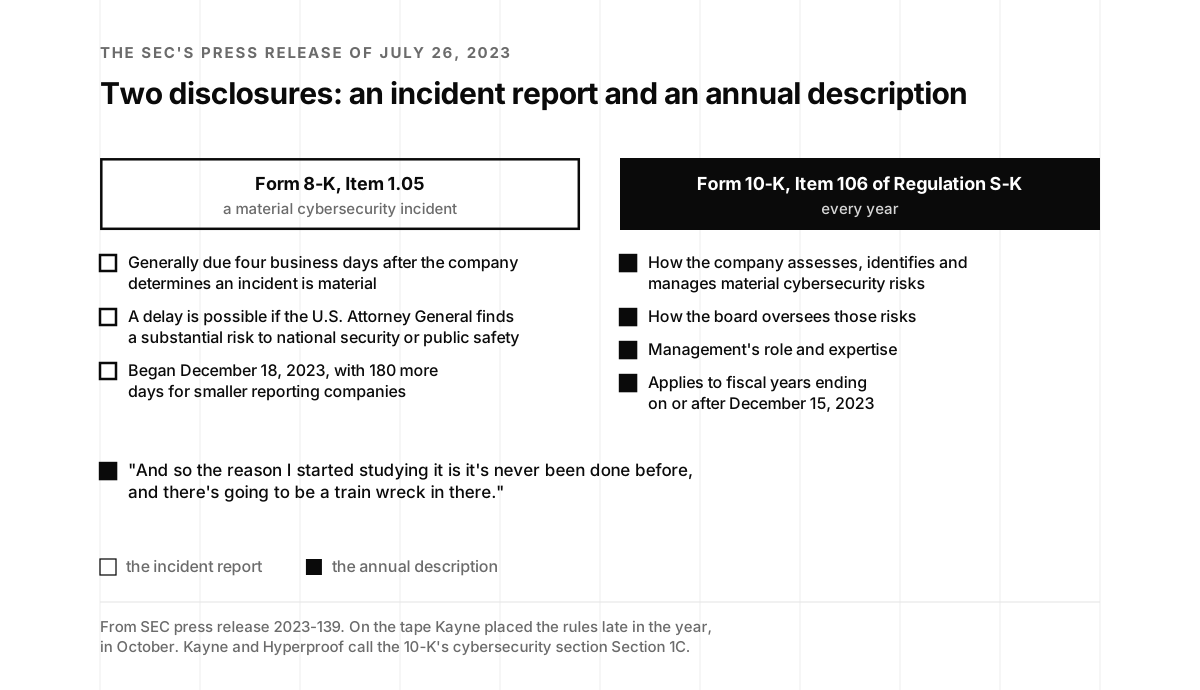
Then the change. As Kayne dated it, late last year, in October, the SEC told companies to explain how they manage cybersecurity risk and how the board and management are involved. The record puts the rules a little earlier. On July 26, 2023, the SEC adopted rules requiring registrants “to disclose material cybersecurity incidents they experience” and to describe, every year, their cybersecurity risk management, strategy and governance (SEC).
There are two parts. An incident report goes on Form 8-K under Item 1.05, generally due “four business days after a registrant determines that a cybersecurity incident is material,” with a delay possible if the U.S. Attorney General finds that disclosing right away poses a substantial risk to national security or public safety. The annual description is Item 106 of Regulation S-K, filed in the 10-K, and covers how the company assesses, identifies and manages material cybersecurity risks, how the board oversees them, and management’s role and expertise. The annual part applies to fiscal years ending on or after December 15, 2023, the incident reports began on December 18, 2023, and smaller reporting companies got 180 more days for those.
Kayne’s reason for reading every one of the new filings was that nobody had written one before.
“And so the reason I started studying it is it’s never been done before, and there’s going to be a train wreck in there.”
Kayne McGladrey, at 2:30
“And somebody’s going to do it really well, and somebody’s going to do it not so well.”
Kayne McGladrey, at 2:35
The worry wasn’t only his. He said the CISOs in the invite-only roundtable he runs, “for about 100 close friends,” were all anxious about the same thing: making a regulatory filing that says here’s how we manage our cybersecurity risks and here’s how the board gets involved, for the first time, in public.
A statement written by marketing
The second reason was a lawsuit. Kayne described the run-up this way, and it is his account of the events.
“Tim Brown of SolarWinds had done a really bang-up job of helping disclose to the CSRB, the Cybersecurity Review Board, about how they had been dealing with Russia being all up in their cybers.”
Kayne McGladrey, at 2:46
The board’s full name is the Cyber Safety Review Board. The Secretary of Homeland Security established it on February 3, 2022, “Modeled after the National Transportation Safety Board,” and its first report, on July 11, 2022, covered Log4Shell (Wikipedia). Then came the part that worried every CISO Kayne knew.
“And unfortunately, the SEC felt fit to file a civil lawsuit against Tim Brown, the CSO of SolarWinds, as well as SolarWinds, based on statements that were not regulatory in nature, like the security statement on their website, which, as best as everyone can tell, was like written by marketing.”
Kayne McGladrey, at 2:58
SolarWinds reported the breach of its Orion platform to the SEC on December 15, 2020. Per Wikipedia, the SEC sued the company in October 2023 for allegedly downplaying internal security risks before news of the attack, and “the case was dropped in November 2025” (Wikipedia). At the time of the recording the case was open, and Kayne’s reading of it was that the regulator had already chosen what it would enforce.
“So they already decided: hey, we’re going to go enforce based on their alleged non-operation of security controls and what was in a non-regulatory filing.”
Kayne McGladrey, at 3:18
The lesson outlived the case. A security page, a trust center or a questionnaire answer is a statement about your controls, whoever wrote it. If marketing drafts it, security should be able to prove every line.
Too little, too much
The new filings put the same pressure on a document that carries a signature.
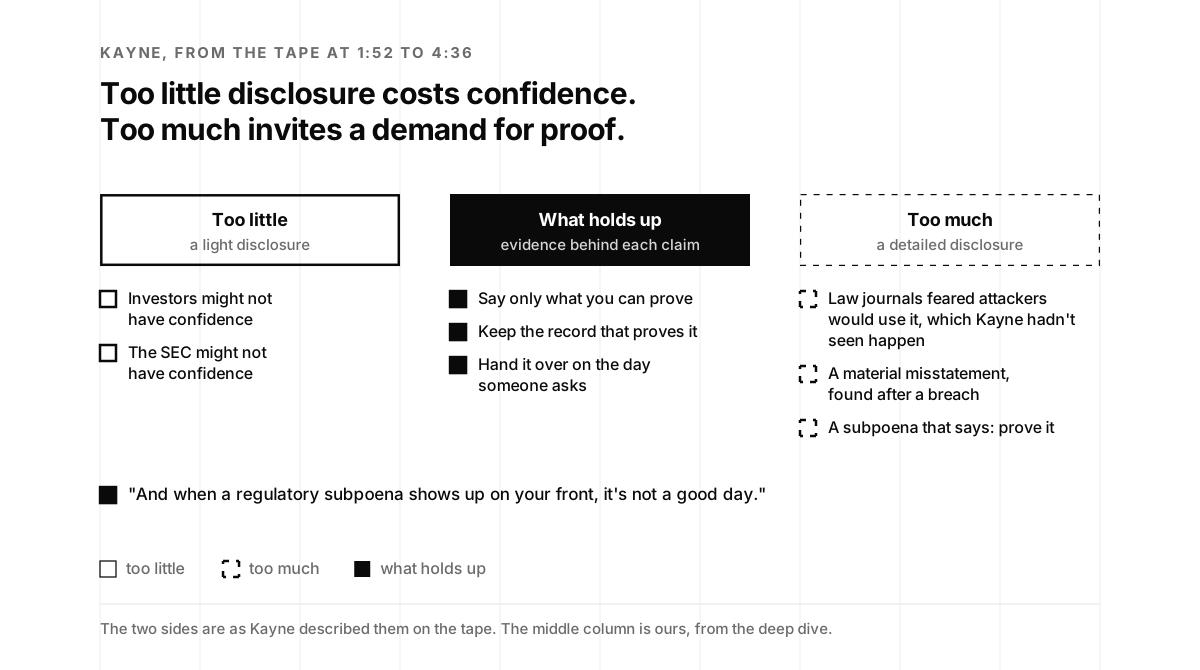
“That sets up a really interesting narrative: if you don’t disclose enough, investors might not have confidence, or the SEC might not have confidence.”
Kayne McGladrey, at 3:33
Disclose too much, and two fears follow. The first, which he said many law journals raised, is that attackers will read the filing to plan a better attack, which he hadn’t seen happen. The second is a material misstatement found after a breach, when the regulator asks for evidence.
“Like you said you were running, I don’t know, multi-factor authentication for all of your end users. Prove that to us.”
Kayne McGladrey, at 4:05
“And when a regulatory subpoena shows up on your front, it’s not a good day.”
Kayne McGladrey, at 4:12
That one sentence explains the rest of the episode. The disclosure itself is the easy part. The hard part is the record that backs it up, kept well enough to hand over on the day someone asks.
Vendors in the filing
Some companies went further than anyone asked, all the way to naming suppliers.
“I hope they got a sales discount from their vendor because I can think of a couple that like mention specifically who their vendors are, which is an interesting thing.”
Kayne McGladrey, at 4:27
Jon asked the obvious follow-up.
“What is not some sideways avenue of marketing or exposure to risk?”
Jon McLachlan, at 4:36
“I can think of one that specifically said we use Microsoft Azure for our entire tech stack, all up.”
Kayne McGladrey, at 4:41
Another filing named its providers for EDR, endpoint detection and response, and for IR, incident response. Kayne’s point was what that does over time: these filings would make 2024 and beyond a very interesting space for regulators and litigators, “because a filing that’s made right now exists in perpetuity and it’s a public record.” A list of tools in a public document is a map for whoever reads it, and it is still there after you switch vendors.
What it means for a startup
Jon brought it back to the listeners, many of them founders or early employees at security startups, selling into the companies making these filings.
“And if I’m one of these founders in a security startup and I’m part of one of these companies’ supply chains or I’m a vendor to one of these companies, what does that really translate to for me?”
Jon McLachlan, at 5:11
Kayne gave two answers. The first is where most startups are headed.
“The first is that most startups want to eventually either get acquired or exit via a PE or they want to go public.”
Kayne McGladrey, at 5:27
Either way, the institutional investor, the private equity buyer or the public market will want to see the company doing security in a reasonable fashion, which he noted is still not a legal standard, and looking like the other companies that do it. The second answer reaches startups that aren’t selling or listing at all: board members. A startup that shares a director with a public company gets that director’s expectations.
“They’re going to have these same level expectations because for them, this is their new normal.”
Kayne McGladrey, at 6:41
He expected those expectations to spread through the whole ecosystem of private startups and suppliers, as board members and investors come to see the disclosures as normal. A company that can’t make the same statements, or whose program is unusual for its industry and doesn’t know it, is “going to have a bad time,” he suspected. Our post on the security slide your board deck is missing is a practical place to start.
Eleven topics where four were required
The count that made Kayne’s analysis useful was how much companies chose to say.
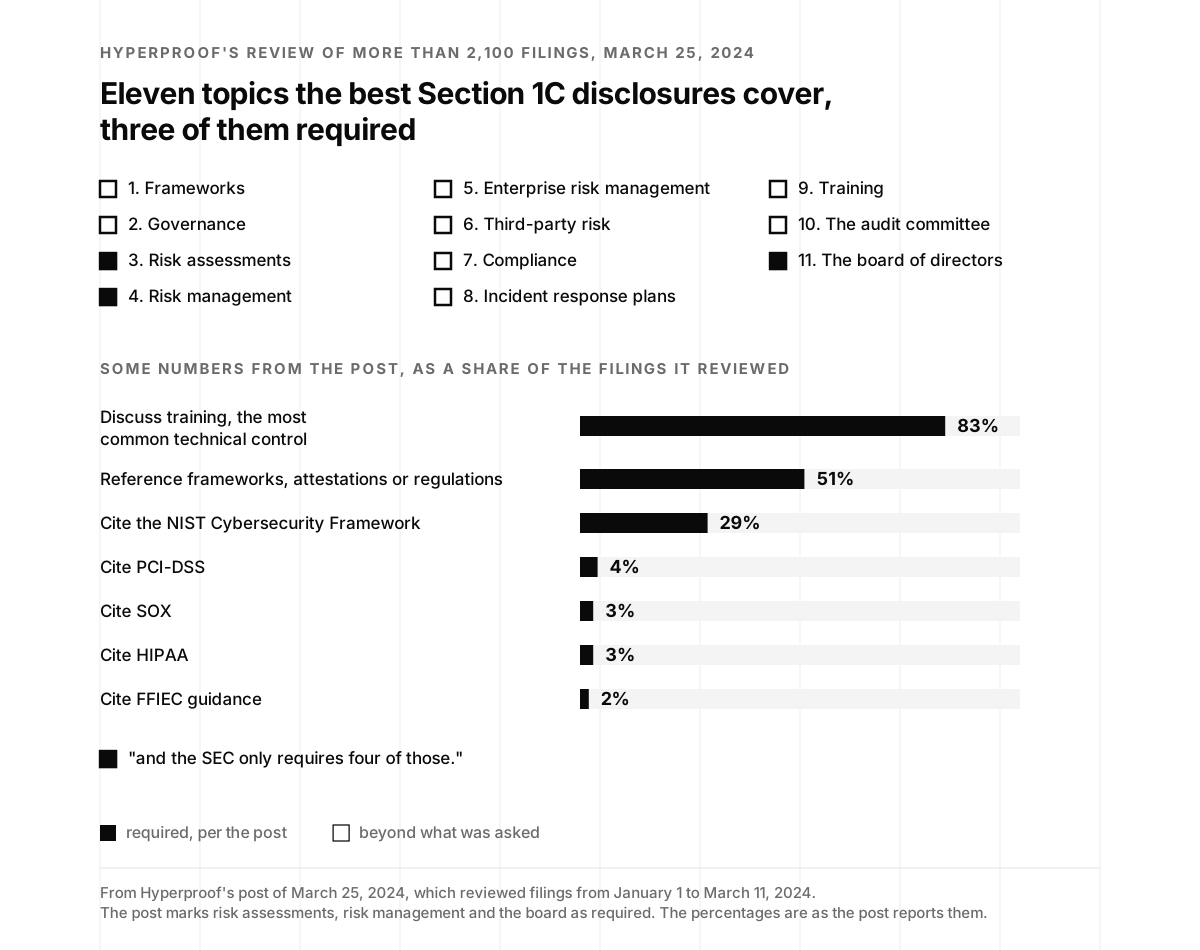
“And there are about 11 factors that I found that came across all the most robust 10-K Section 1C, and the SEC only requires four of those.”
Kayne McGladrey, at 6:01
Jon asked whether a SOC 2 Type 2 report would get a startup over the bar, and answered his own question.
“But SOC 2 is not going to be, it’s not going to cut it.”
Jon McLachlan, at 7:39
Kayne had the write-up ready.
“Yeah, so I’ve got a blog post up that will be up after this podcast is finished recording about those 11 factors.”
Kayne McGladrey, at 7:42
Hyperproof published it on March 25, 2024, as “Cybersecurity in Financial Disclosures: 11 Topics for 10-K Filings” (Hyperproof). The author reviewed Section 1C disclosures from the start of January, more than 2,100 filings between January 1 and March 11, 2024, and over 40% of them disclosed eleven distinct topics. The post’s summary is that “almost half of companies are sharing additional information on eleven different topics.” The four things the SEC asked for, in the post’s words, are identifying and managing risks, disclosing material breaches, board oversight and management’s role. (The page carries a newer byline after a January 2026 update, and its text is written in the first person.)
The eleven topics, in the post’s order, are frameworks, governance, risk assessments, risk management, enterprise risk management, third-party risk, compliance, incident response plans, training, the audit committee and the board of directors. The post marks risk assessments, risk management and the board as required and the other eight as beyond what was asked. A few numbers from it: 51% of filings reference frameworks, attestations or regulations, the NIST Cybersecurity Framework is cited in 29%, and training is “the most common technical control discussed” at 83%. The audit committee gets a nickname, the “kitchen sink committee,” for how much lands on it.
For a startup, the list doubles as a checklist. If a public company customer describes its program in those eleven terms, its security team will ask its vendors about the same eleven things.
Any framework, and who tells who
Kayne went through the topics that go furthest past the minimum, starting with the ones a startup might assume it already has covered.
“But these go beyond things like having a SOC 2 or an ISO.”
Kayne McGladrey, at 7:55
“So, for example, one of the top factors is use of literally any cybersecurity framework.”
Kayne McGladrey, at 8:02
He didn’t care which one. The NIST framework came up most, under several names, including once as the “NIST CFS.” The NIST Cybersecurity Framework dates to 2014 (Wikipedia), and companies cite it, he said, as a proxy for saying they know what they’re doing because they follow an industry standard. Governance was next, and he put the whole topic in one line.
“And that’s a broader topic of, when something happens, who knows when, who tells who?”
Kayne McGladrey, at 8:29
Some governance disclosures were tremendously detailed and some were light, and neither frameworks nor governance were required. What the SEC did require includes risk assessment and risk management, under the section of Regulation S-K he was reaching for on the tape, Item 106. Inside those, one subject stood out.
“Something nobody expected would be in there, but is very much in the cultural zeitgeist of cybersecurity right now, is third-party risk management.”
Kayne McGladrey, at 9:04
Some companies disclosed their vendor process in so much detail that Kayne said he wouldn’t want them as an account. One described an 11-step process that would send an auditor to audit a supplier in four hours, even one holding an ISO 27001 certification and a SOC 2 Type 2 report, as if four hours could beat both. ISO/IEC 27001 is the standard that sets the requirements for an information security management system (Wikipedia), and SOC 2 is one of the AICPA’s system and organization controls reports (Wikipedia).
“So there’s some disclosures in there that are just pure nightmare fuel”
Kayne McGladrey, at 9:44
If you sell to a company like that, the work is front-loaded: a current report, an answer library and someone who can take the call. Our sales support team answers security questionnaires and joins the buyer’s review as your security team.
A paper tiger
Whatever a company discloses, Kayne said, it needs the confidence that it is factually correct.
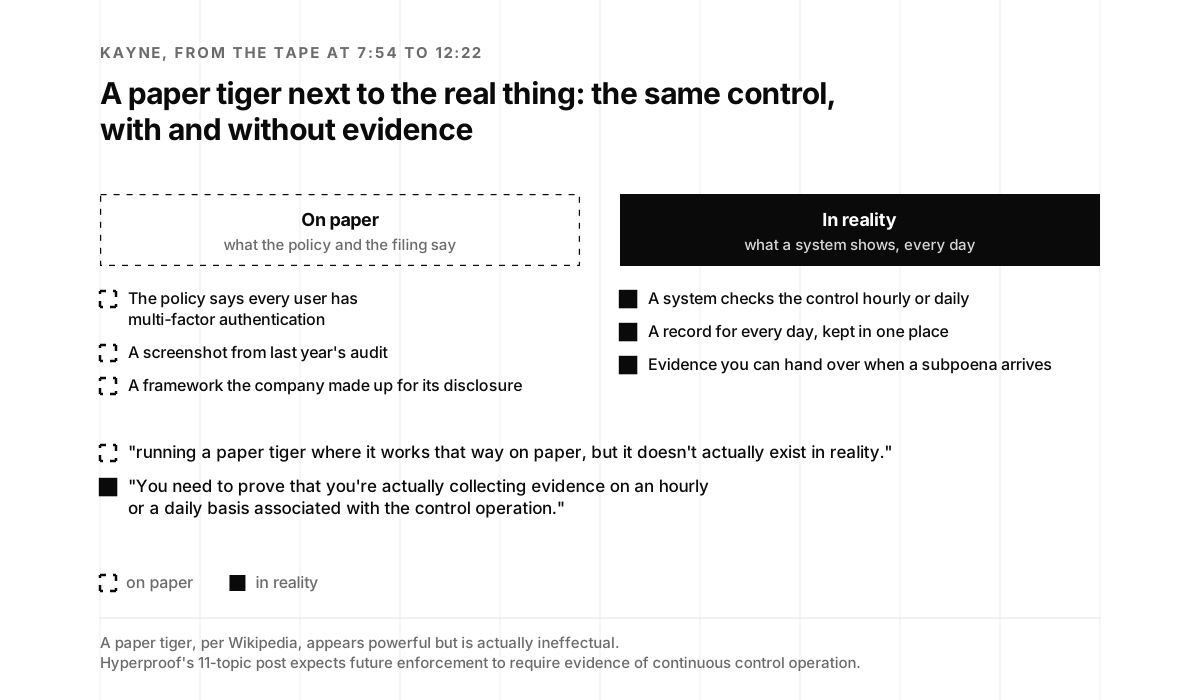
“Because the thing you don’t want to get caught out in is running a paper tiger where it works that way on paper, but it doesn’t actually exist in reality.”
Kayne McGladrey, at 9:58
A paper tiger, per Wikipedia, is something that “claims or appears to be powerful or threatening but is actually ineffectual” (Wikipedia). In a filing, it is a control that exists in a policy and nowhere else. In a security review, the common version is a setting that is enabled but not enforced, which our post on five questionnaire answers that quietly cost you the deal walks through. He expected that to go badly from a litigation and enforcement perspective, with a caveat he repeated more than once.
“Again, I’m not a lawyer. I’m not making legal advice.”
Kayne McGladrey, at 10:10
Continuously
Jon, who had noted that neither of them is a lawyer, asked whether a product like Hyperproof gives that confidence by checking the controls every day.
“you have the constant reinforcement that the controls are being audited daily?”
Jon McLachlan, at 10:22
“Continuously. Continuously. I think that makes a big difference.”
Kayne McGladrey, at 10:28
His example was a filing he wouldn’t name.
“They just full-on made up a fictional cybersecurity framework, and it’s in their public disclosure.”
Kayne McGladrey, at 10:38
The fix he described is a standard of evidence, not a better paragraph.
“You need to prove that you’re actually collecting evidence on an hourly or a daily basis associated with the control operation.”
Kayne McGladrey, at 10:52
That limits the regulatory and investigative risk after a material breach, and it also answers the question a CISO asks of every vendor. Maybe it’s EDR, maybe it’s a security operations center run as a service that watches the company’s SIEM, the security information and event management system that collects its logs.
“I want to know that the darn thing works so that I keep paying the bill”
Kayne McGladrey, at 11:23
He tied it to Hyperproof’s 2024 survey, which found that companies with a continuous assurance approach to their GRC platform, or to managing risk, had a substantially reduced risk of a data breach. Then he was careful about what that means.
“it is correlation, I should say, where we’re not saying this is absolutely a way to avoid the risk of a data breach, but it makes sense.”
Kayne McGladrey, at 12:03
The report is Hyperproof’s fifth annual IT risk and compliance benchmark, published on February 23, 2024 from a survey of more than 1,000 IT and GRC professionals (Hyperproof). Among its findings, 59% of respondents had a data breach in the previous 24 months, and “those still operating in silos are more likely to experience a breach.” His explanation for why the connection makes sense was about shared facts.
“If people are looking at the same thing, at the same set of facts, they’re going to make way better decisions”
Kayne McGladrey, at 12:09
The alternative he described was three or five different Excel spreadsheets and the work of figuring out, from them, how a risk is being managed. The 11-topic post makes the same point about enforcement: “future enforcement actions will likely require evidence of continuous control operation.”
There is no cybersecurity risk
Jon put the board’s side of it plainly. Directors allocate the company’s resources, including how much goes to security.
“how can you tell a paper tiger from the real deal?”
Jon McLachlan, at 12:39
Kayne said what works with boards isn’t what CISOs had been doing, and started with the most quotable line of the episode.
“I think a lot of us as CISOs have been guilty over the years of, first of all, saying that cybersecurity risk exists. It doesn’t. We have business risks. We manage business risks.”
Kayne McGladrey, at 12:52
“Cybersecurity is certainly a factor of business risk, but it is not itself a risk. Controversial opinion, I know.”
Kayne McGladrey, at 13:01
Two and a half years later the idea had become a book. His LinkedIn headline now lists him as the author of Cyber Risk is a Myth, from CRC Press, and on October 28, 2026 he posted about discussing it on Chris Clymer’s show.
I joined Chris Clymer on his show to talk about my book, and I came away convinced the term does more damage than anyone admits. Calling something "cyber risk" tells every executive without a technical background that it belongs to a specialist somewhere else in the building. The problem is that the specialist usually doesn't exist.
Kayne McGladrey · October 28, 2026
That post is the same argument from the tape, sharpened. If a risk is filed under cyber, it sounds like somebody else’s problem to every leader who isn’t technical. If it is filed under the business outcome it threatens, it has an owner.
A KPI and a key risk indicator
The second thing CISOs had been doing wrong, Kayne said, was the link to the business.
“But the other thing we’ve been doing is we’ve been failing to tie to business objectives.”
Kayne McGladrey, at 13:09
What matters most to a board is the company’s key performance indicators, so his method starts with the business leader’s KPI and attaches a risk measure to it.
“And then you need to tie a KRI, a key risk indicator, to that. That’s a way to get board engagement.”
Kayne McGladrey, at 13:34
A performance indicator measures how well an organization achieves its objectives (Wikipedia). A key risk indicator, per Wikipedia, is “an early signal of increasing risk exposures” (Wikipedia). His example was data exfiltration, an unauthorized transfer of data from a computer (Wikipedia). Counting uploads to Google Docs or Dropbox and USB disks plugged into computers is the security team’s view of it.
“You put that in front of a board, it’s a snooze fest.”
Kayne McGladrey, at 13:52
The same data means something when it is tied to a goal the board already tracks. HR wants happy employees and measures employee satisfaction. Security knows something about people who are about to leave.
“about six weeks before they decide, I’m done, I’m leaving, I’m going to go look for another company, they exfil all their data.”
Kayne McGladrey, at 14:10
A salesperson takes the book of business, an engineer takes the code in the repo, and both leave about six weeks later. Tied to HR’s KPI, the exfiltration count becomes a KRI.
“It’s a leading indicator for how that point is going to go.”
Kayne McGladrey, at 14:33
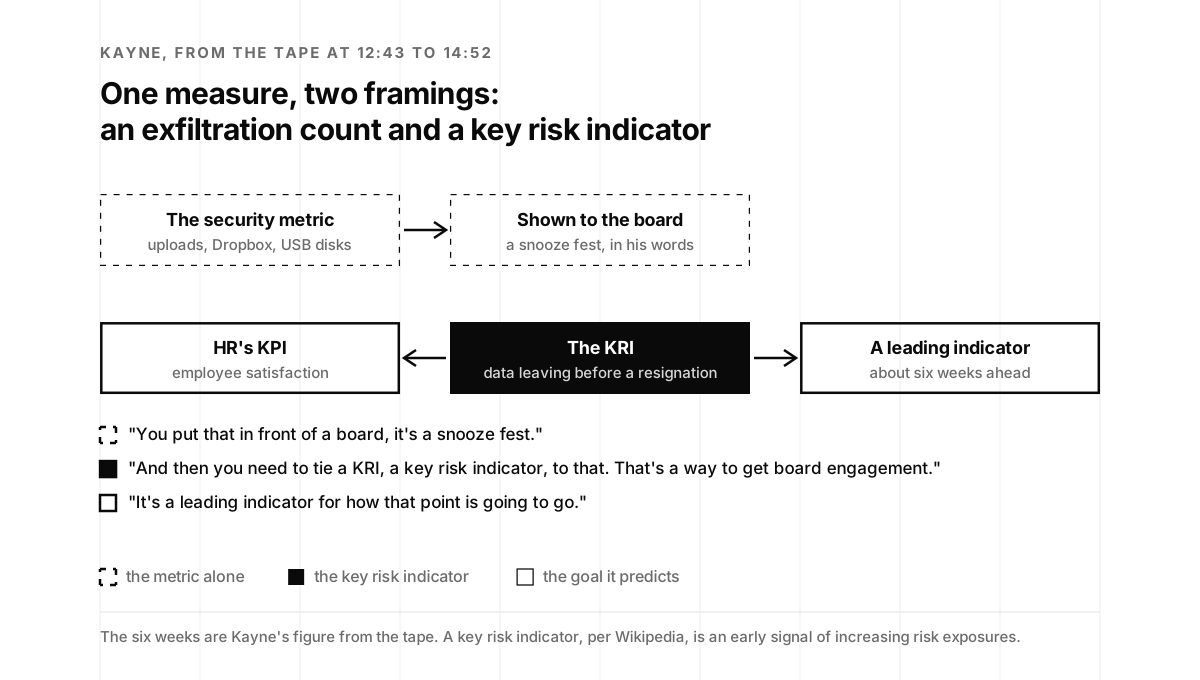
The general rule he drew is that leaders should look for these intersections, where the data security already has can inform how successful the business will be.
No perfectly secure system
Jon liked tying security back into the business, because a security team can spend any budget under the sun and still have business risks at the end of the day. He put the case against chasing perfection in his own words.
“I would argue that those don’t exist, that there’s always going to be risk and that we have to navigate that risk”
Jon McLachlan, at 15:24
The lens he suggested is the business’s own. Most businesses want to grow, and he named the report that often carries that growth: “I know that SOC 2 Type 2 often is like the go-to growth mechanism.” As companies get larger, he said, he was happy to hear that people are caring and that things are changing for the better.
Then you pay for the insurance
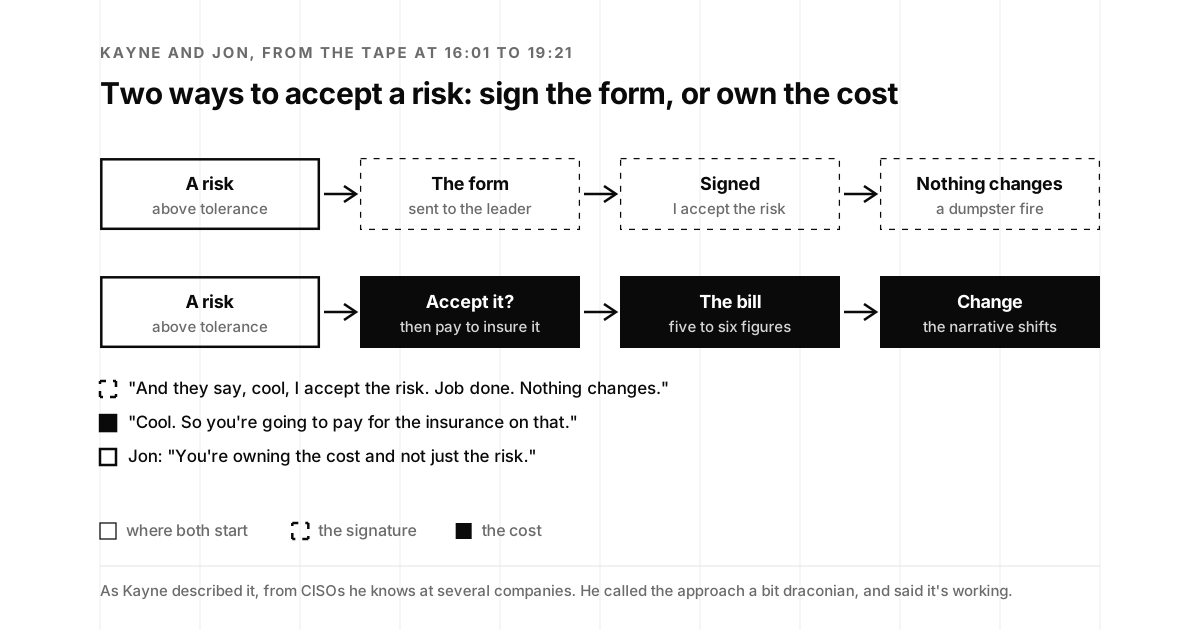
Kayne’s next story came from friends who are CISOs, and it starts with a familiar ritual. The team finds a risk above the company’s tolerance, sends the risk form to the business leader, and asks for a signature.
“And they say, cool, I accept the risk. Job done. Nothing changes.”
Kayne McGladrey, at 16:23
“And then we wonder why are we continuously living a dumpster fire.”
Kayne McGladrey, at 16:27
The CISOs he knew who had made a difference ran the same process with one change. When the business leader chose to accept the risk, the acceptance came with a bill.
“Cool. So you’re going to pay for the insurance on that.”
Kayne McGladrey, at 16:48
He said this was happening at several companies where he has friends, and the reaction is what changes behavior.
“wait, you’re telling me I’m going to take a five to six figure loss on my P&L for this quarter to buy incident response insurance and remediation insurance against a risk”
Kayne McGladrey, at 17:00
A report to the board on how long vulnerabilities stay open, and which department never closes them, doesn’t do that on its own.
“If they’re just printing money all day long, the board’s not going to care.”
Kayne McGladrey, at 17:27
A cost the leader owns does. It gives them a reason to get rid of a legacy system or patch their systems, because if their KPI is financial performance, the risk is now tied to it. Cyber insurance, per Wikipedia, protects businesses from risks relating to their information technology (Wikipedia), and Kayne admitted the approach can be a bit draconian. His verdict on it was short: “It’s working, right?” Jon’s summary was shorter.
“You’re owning the cost and not just the risk.”
Jon McLachlan, at 19:04
A fictional number
The same partnership, Kayne said, is needed when you size a risk.
“There’s this fiction that CISOs can magically use something like FAIR to figure out how much a risk will cost if it becomes an impact, right?”
Kayne McGladrey, at 19:24
FAIR, factor analysis of information risk, is “a taxonomy of the factors that contribute to risk,” and Wikipedia adds that “It is not a methodology for performing an enterprise risk assessment.” (Wikipedia). Kayne’s objection was to the inputs, not the math.
“I can ask the salesperson, the sales leader, I can ask the engineering leader, how much does this thing make on an hourly basis? But I don’t inherently know that myself.”
Kayne McGladrey, at 19:36
Without that collaboration, the number in front of the other leaders is fictional, and “where did this come from?” is a legitimate question. He went further: ethically, he said, CISOs and security leaders don’t have the ability to put forth a material number, especially now that the SEC’s rules turn on materiality, the auditing and accounting idea of how significant an amount, a transaction or a discrepancy is (Wikipedia).
“let’s partner with the business to figure out what is the potential impact there as opposed to just wet finger in the wind and making up a number.”
Kayne McGladrey, at 20:24
Favorite disclosures
Jon asked for his favorite Section 1C disclosure. Kayne pointed him to LinkedIn, where Jon said his posts are “hilarious and so much fun to follow.” The last one Jon remembered was a sad bear on a park bench, and Kayne said “that was about the DOJ whistleblower.” The approach, he explained, is a habit from his years on Twitter.
“LinkedIn is way too serious.”
Kayne McGladrey, at 21:20
“I read way too many law journals and I’m reading regulatory filings for fun.”
Kayne McGladrey, at 21:26
Then the favorites. A wine company he was pretty sure was among the worst he had read. And a whole category.
“There’s the whole category of SPAC, special purpose acquisition company, where they just don’t do cybersecurity at all.”
Kayne McGladrey, at 21:43
“They say they don’t have a cybersecurity program, don’t plan on having one.”
Kayne McGladrey, at 21:50
A SPAC is “also known as a blank check company” (Wikipedia), a listed shell company set up to buy a private company later. Kayne said he had to look up what that is. His other favorite was a filing that pointed at itself. It said the SEC required these disclosures in Section 1C, listed the regulatory requirements it had to meet, and then sent the reader in a circle.
“And then they said, for more details, see Section 1C.”
Kayne McGladrey, at 22:16
A few were combative in tone, written as if the SEC had forced the words out of them, and he hoped an SEC staff attorney who, he said, was reading his analysis would weigh in on how companies were reacting. The 11-topic post has a phrase for the type: “minimal or occasionally combative-toned disclosure.” The contrast he drew was with the companies that took the rule well.
“Because some are welcoming it. They’re being very transparent.”
Kayne McGladrey, at 22:48
Best and worst written
Jon asked whether the combative ones were technology companies. Mostly the opposite, Kayne said.
“Tech companies, actually, software and SaaS providers tend to be some of the best written.”
Kayne McGladrey, at 23:01
“I think the only ones that are more comprehensive are in the aerospace and defense space.”
Kayne McGladrey, at 23:07
He admitted a bias, having worked in aerospace and defense himself. What makes the tech filings strong, he said, is that CISOs are bringing basics in, including at companies that had somehow never had them.
“And the company they’re at goes, that’s a neat idea. We never thought of that before.”
Kayne McGladrey, at 23:29
The idea in question was a risk register. In the best filings he saw comprehensive disclosures around risk, governance and the board, including how security communicates with the board and, in some cases, outside consultants brought in to advise it. At the other end he put oil and natural gas exploration, an industry he used to try to do risk assessments for, where, as he remembered it, the companies could make money their way out of almost anything.
“I think, a quarter billion dollars was sort of their risk threshold.”
Kayne McGladrey, at 24:25
“It’s like anything above that line might be a business risk. We’ll get back to you.”
Kayne McGladrey, at 24:28
A risk register, written down
Jon heard the never-had-a-risk-register story with two reactions at once. One was disbelief.
“how did you get to be so successful and so large without just the basics?”
Jon McLachlan, at 24:58
The other was generosity. We’re always learning and growing, he said, and maybe a company just didn’t have the right person with the right expertise in the right place at the right time.
“I have this view of companies are just groups of people, right?”
Jon McLachlan, at 25:17
People come together to make a product or provide a service, they owe something to each other and to their customers, and with a diverse group the answer to what the right thing is will vary wildly. That is what standards are for. He ended on the oldest rule he knew.
“do not invent your own cryptography. Just don’t do it.”
Jon McLachlan, at 26:23
A risk register, per Wikipedia, is “a document used as a risk management tool and to fulfill regulatory compliance” (Wikipedia). It is the same idea applied to risk: a standard form, so nobody has to invent their own.
A maturity model for GRC
Kayne agreed, and said it led to the project he was working on.
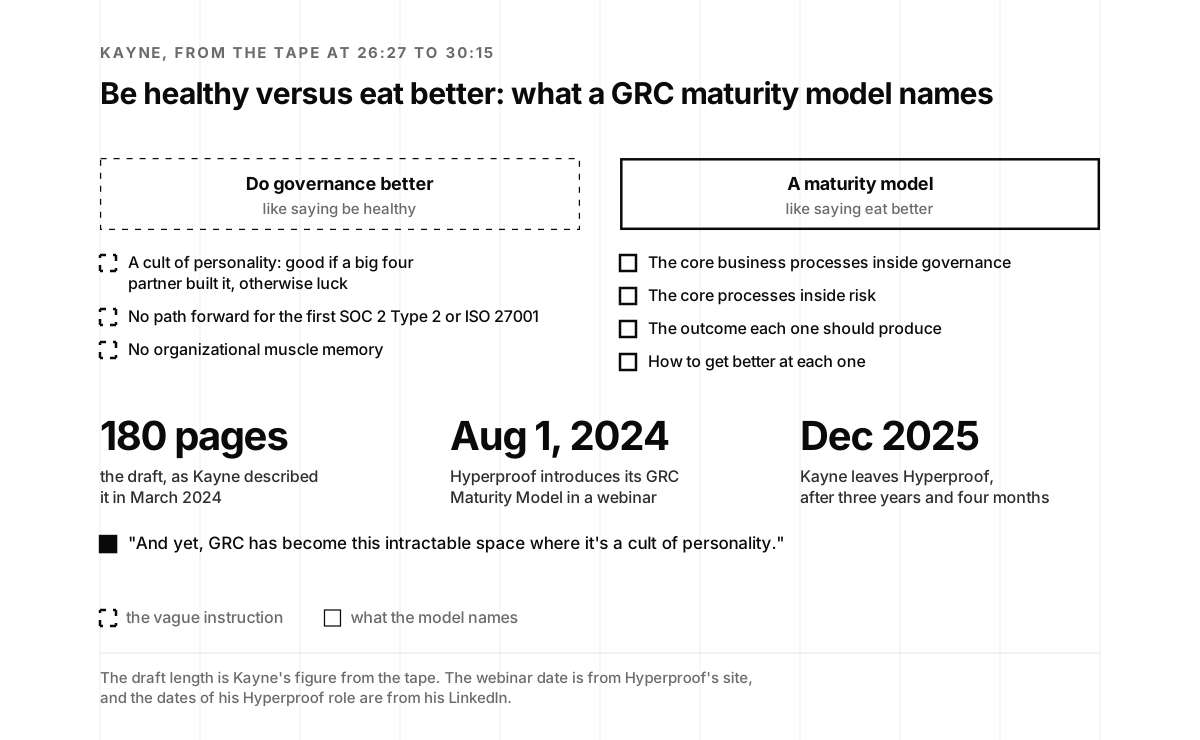
“It goes to an area that I’ve been working on for some time now, which is the concept of a maturity model for governance, risk, and compliance.”
Kayne McGladrey, at 26:28
Governance, risk and compliance, GRC for short, is a holistic approach to the three that took shape in the 2000s (Wikipedia). The problem he described is that the CISOs it reports to know what they’re doing but couldn’t tell you how to get better at it. Cybersecurity has many maturity models, of varying quality. GRC had nothing like them.
“And yet, GRC has become this intractable space where it’s a cult of personality.”
Kayne McGladrey, at 26:58
Someone who was a partner, or on track to be one, at a big four firm brings a well-rounded view of governance and compliance. Someone well-meaning without that background knows how to meet the standard in front of them, but hasn’t seen what good or bad looks like, and the company never builds the organizational muscle memory for its first SOC 2 Type 2 or ISO 27001. Telling a team to “do governance better” doesn’t help, he said, “because that’s like saying be healthy.” His model would name the core business processes inside governance and risk and the outcomes each one should produce.
“I hope to publish something later this year in this space”
Kayne McGladrey, at 28:24
The draft was about 180 pages, he said, and some of his roundtable friends had asked to read it. Hyperproof introduced its GRC Maturity Model in a webinar on August 1, 2024 (Hyperproof), and the model has its own page today (Hyperproof). His LinkedIn lists it among his work there.
Boundless civil liability
The reason the model mattered to him went beyond process. It was about the people doing the job.
“But where that comes to a concern for me is, as a person who has a lot of friends who are CISOs or senior levels of senior leaders in security, the amount of civil risk that we carry becomes a big disincentive to staying in the career.”
Kayne McGladrey, at 28:38
Without directors and officers insurance, indemnification or an umbrella policy, a security leader carries that risk personally. D&O insurance, per Wikipedia, is “liability insurance payable to the directors and officers of a company” (Wikipedia). And the leader depends on an organization that may not know how to get better at its job.
“and everything they write down that you sign in some cases is a reason you could go to court and lose everything.”
Kayne McGladrey, at 29:11
He had the Tim Brown case in mind, and he was blunt about where it left his peers.
“But in terms of civil liability, CISOs right now have boundless civil liability, and that concerns me deeply, right?”
Kayne McGladrey, at 29:23
He cited a study from the year before, which he didn’t name, that found 75% of CISOs were considering leaving their jobs for mental health reasons, and said he couldn’t imagine that had improved in 2024 with Section 1C now in force. His aim for the maturity work was to give people discipline and peace of mind, so that companies get more resilient and more effective, and so that senior leaders don’t panic and leave one day, as he put it, “because I could go to court just for showing up.”
Frustrated regulators
Jon thanked him for stepping up for the community.
“All the gratitude in the world for stepping up and providing some foundation for this.”
Jon McLachlan, at 30:21
Kayne said the 180-page draft was in a final editorial pass, and that he was hopeful. Then he looked back at how he got here.
“I had no idea what normalcy looked like.”
Kayne McGladrey, at 30:55
He said he might not have chosen the career had he known the social pressure, the economic pressure, the litigation and the personal liability, and he never expected to read regulatory filings and jurisprudence, “which is a $5 word,” for a living. He read the regulators’ side with some sympathy. They keep seeing personal data breached and money moving out of Western countries, he said, and they aren’t seeing progress.
“And so the regulators are becoming more prescriptive.”
Kayne McGladrey, at 31:52
“What can we each do within our community to try and make that a little bit better for everyone?”
Kayne McGladrey, at 32:01
Half can’t find their critical risks
Jon called that the mark of a real leader, then turned to the survey Kayne had presented, Hyperproof’s fifth annual IT benchmark.
“nearly half of the companies struggle with identifying critical risks so that they can prioritize the remediation.”
Jon McLachlan, at 32:28
The report’s number is 49% of respondents, who “struggle with identifying critical risks to prioritize remediations” (Hyperproof). Kayne’s explanation went back to the risk register.
“So I think that is a product of how companies have not had risk management discipline beforehand.”
Kayne McGladrey, at 32:39
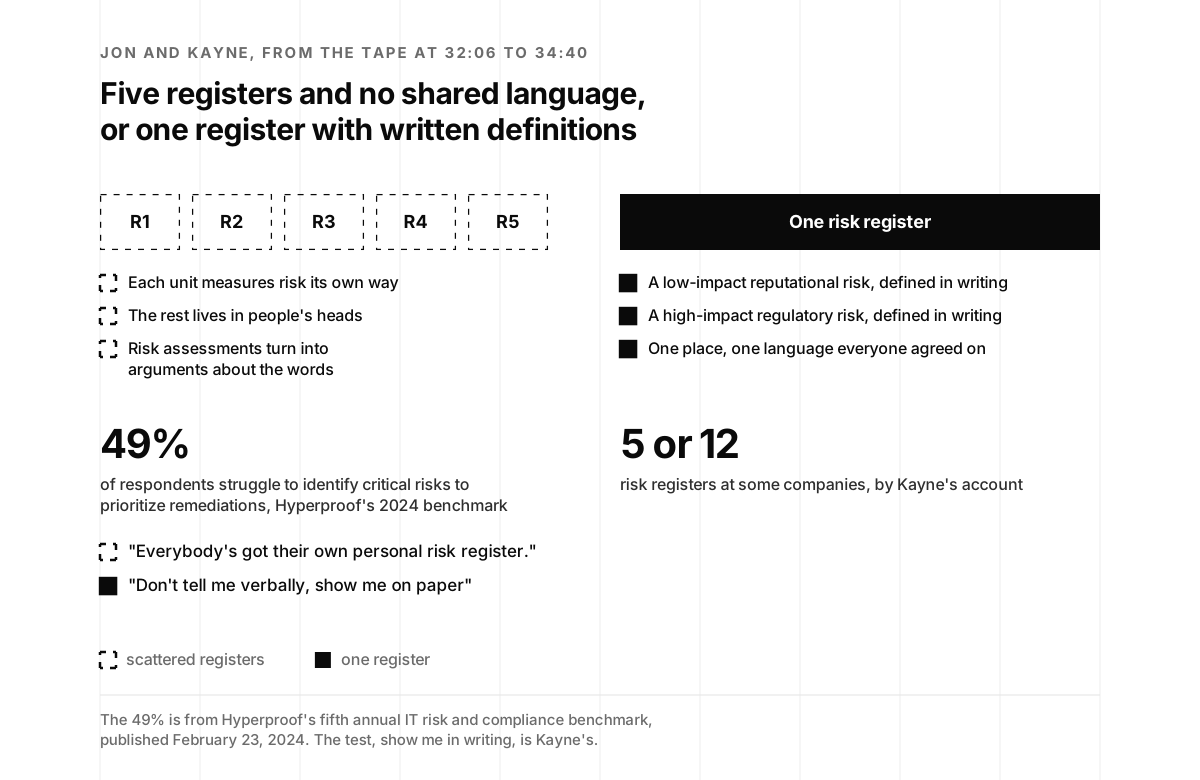
Some companies have no register. Others have five, or 12.
“Everybody’s got their own personal risk register.”
Kayne McGladrey, at 33:00
At a global defense company, separate registers with controls on who can see what are the nature of the business, he said, and elsewhere they aren’t. Scattered registers hurt strategy, insurance and careers. A CISO who isn’t told that the budget went to a global expansion ends up frustrated, and five business units with five ways of measuring risk can’t agree on what to fix first. His test from his advisory work was simple.
“one of the first things I’d ask folks was if they could show me in writing what a low-impact reputational risk was, or a high-impact regulatory risk.”
Kayne McGladrey, at 34:01
“Don’t tell me verbally, show me on paper,” he said. Without a common language, risk assessments turn into arguments over how big a risk is and whether it matters, and the same disagreement repeats across every register and every head it lives in.
Conway’s law and a prophet
Jon connected that to something he had watched as an engineer.
“What I’ve noticed coming up through the engineering ranks is that the software that engineers tend to write will reflect the communication channels within the company.”
Jon McLachlan, at 34:40
That is Conway’s law, named for Melvin Conway’s 1967 observation, which describes “the link between communication structure of organizations and the systems they design” (Wikipedia). Jon asked whether risk registers and risk language follow the same pattern, and sketched the extremes. At Apple, in his telling, there is a prophet and everyone listens. In a startup, everyone is running around doing whatever needs doing. In the middle, people build little empires that go to war with other parts of the company, and all of that politics shows up in the product, the code and the risk language.
Kayne had seen it from the outside, brought in to assess how companies got where they were.
“And often it comes to communications channel breakdowns or it comes down to expectations breakdowns.”
Kayne McGladrey, at 36:19
“If there’s an annual risk assessment process and only 20 percent of the company knows about it, how well of a treatment of your risks do you think you’re going to have?”
Kayne McGladrey, at 36:24
He granted that this sounds boring. The cure he described is committee meeting notes: a record that one named person agreed to mitigate a risk and another agreed to transfer one to insurance.
Professor Plum in the library
Then he explained why the notes matter, with a board game.
“The funny thing, though, is if you don’t write it down, often things come down to, do you remember the old Clue board game?”
Kayne McGladrey, at 36:57
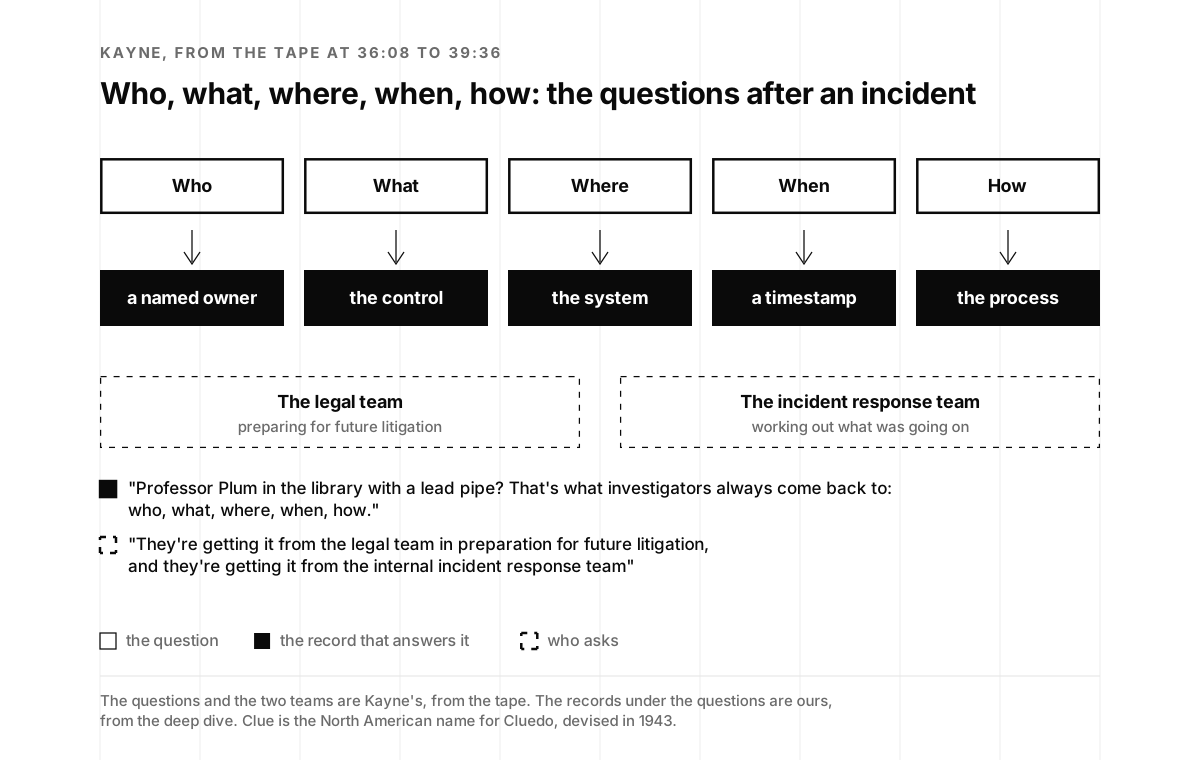
“Professor Plum in the library with a lead pipe? That’s what investigators always come back to: who, what, where, when, how.”
Kayne McGladrey, at 37:04
Clue is the North American name for Cluedo, which Wikipedia says Anthony E. Pratt devised in 1943 (Wikipedia). The game’s question is the investigator’s question, and after a breach it costs engineering time. A company without the habit of writing things down and keeping them in one place gets asked, after the fact, to show how each control was operating, and it gets asked twice.
“They’re getting it from the legal team in preparation for future litigation, and they’re getting it from the internal incident response team”
Kayne McGladrey, at 37:49
If nothing was written down and kept up, he said, the outcomes vary wildly.
FedRAMP writes everything down
The cleanest example of the discipline was the program Hyperproof was working toward at the time.
“That’s something that we’re also working on at Hyperproof is a FedRAMP. And you want to go through a documentation exercise, they will have you write everything down.”
Kayne McGladrey, at 38:11
FedRAMP is the U.S. government’s compliance program for cloud products, which provides “a standardized approach to security assessment, authorization, and continuous monitoring” (Wikipedia). Kayne compared it to an engineering change process. It is prescriptive about what has to be written down, how, how often it has to be maintained and how long the records are kept, and a startup that wants to sell to an agency finds the documentation hard to meet if it never built the habit for its commercial customers. ISO certifications are similar: “honestly, they love their documentation, right?” Hyperproof finished the job: on March 12, 2026 it announced that it “has launched a FedRAMP Moderate-authorized version of our platform” (Hyperproof).
He added a test of how far the culture reaches. When one part of a large company goes for FedRAMP, ISO or GxP, the good-practice rules of the life sciences, the assessment usually covers the whole company’s business processes, and that is when leaders learn how well their message has been getting out. If federal customers are on your roadmap, our FedRAMP readiness team starts with that documentation.
One org or many
Jon described the two ways he had seen security organized. In one, a CISO owns everything underneath: product security, infrastructure security, corporate security, governance and compliance, and maybe a red team as a feedback loop. In the other, the work is spread out, with product security inside engineering and corporate security under IT.
“And I’m not even sure where the red team ends up in an org like that.”
Jon McLachlan, at 40:20
He asked whether one structure serves a CISO, or the public interest, a little better. Kayne said both work.
“I think both of those are viable. What ultimately matters is ongoing sustainability and observability and transparency.”
Kayne McGladrey, at 40:50
What matters more, he said, is a way of proving it, and he was precise about the bar.
“If you were being investigated as part of a legal investigation, could you prove it?”
Kayne McGladrey, at 41:19
It is “a high standard that I advocate for,” he said. Saying you do something, having someone say it on the record and collecting log files or screenshots now and then don’t meet it. Continuous inspection of control operation does, centralized or not, and the org chart is irrelevant to the people asking.
“A lawyer does not care about how you structured your company.”
Kayne McGladrey, at 42:13
A guest badge on Thursday
Without continuous evidence, Kayne said, a smart investigator, whether from an insurer or a litigator, looks at the gaps. He made it concrete.
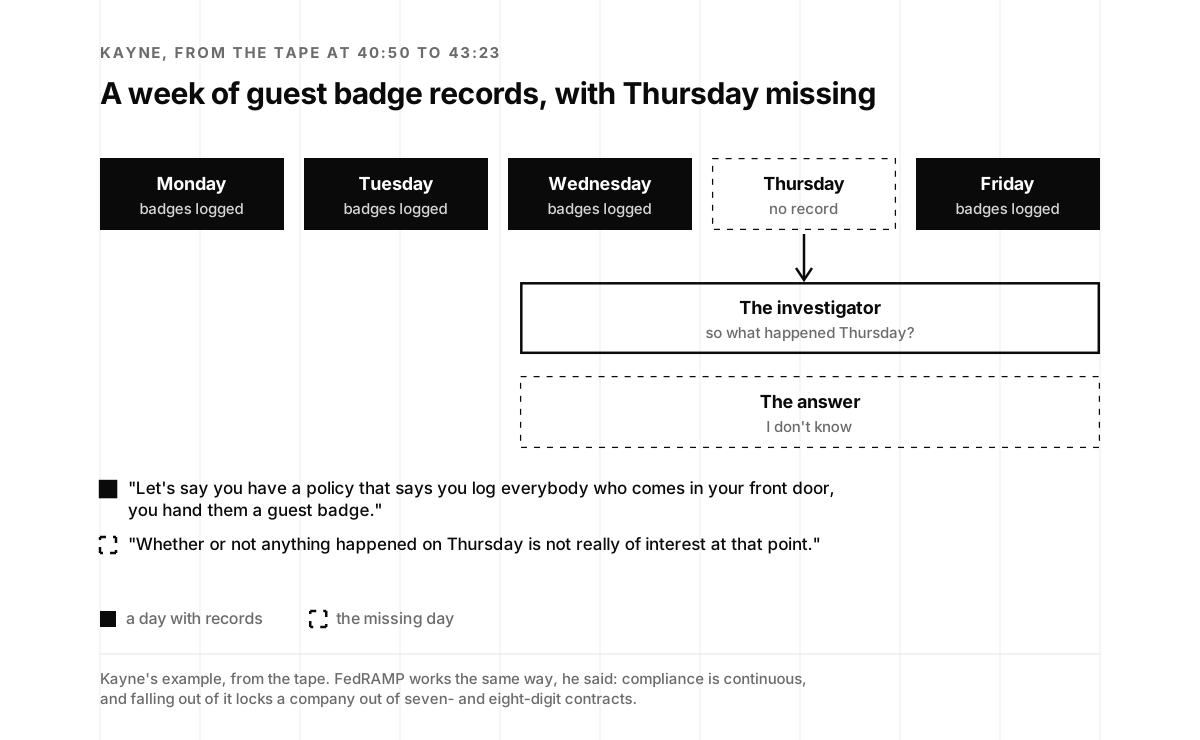
“Let’s say you have a policy that says you log everybody who comes in your front door, you hand them a guest badge.”
Kayne McGladrey, at 42:36
The badges come back at the end of each day, and the records are complete for every day except Thursday.
“they say, so what happened Thursday? And you go, I don’t know.”
Kayne McGladrey, at 42:52
“Whether or not anything happened on Thursday is not really of interest at that point.”
Kayne McGladrey, at 42:58
The missing day is the finding, because it is the absence of evidence for the argument that you were doing the thing. FedRAMP works the same way. It isn’t a once-a-year exercise, he said, but continuous compliance, and falling out of it locks a company out of seven- and eight-digit contracts. Jon’s reply was one word: “Painful.”
Weaponize it
Kayne turned the burden into an advantage.
“Right. You have to be able to prove you have a continuous assurance process.”
Kayne McGladrey, at 43:23
“And I think that as companies look at these opportunities, the advantage is you start thinking about cybersecurity, you can weaponize it.”
Kayne McGladrey, at 43:28
A SOC 2 Type 2 or another outside attestation lets a company show customers and its supply chain that it is more secure than the alternatives, and probably more trustworthy than its competitors. Jon called it a market distinguisher. Kayne agreed, and said the distinction wouldn’t last.
“I think at some point we’re going to hit table stakes where everybody’s got a SOC 2 Type 2, right?”
Kayne McGladrey, at 44:01
What is no longer a differentiator becomes a blocker to getting into a market. Jon had already seen it in AI startups raising $70 million seed rounds.
“They came out of stealth with a SOC 2 Type 2.”
Jon McLachlan, at 44:33
He saw it quickly becoming table stakes, especially for companies chasing larger contracts. Our SOC 2 Type 2 team works on that timeline, from readiness to a Type 2 report.
When to hire a CISO
Jon asked the question he hears most from founders, whatever they build.
“when is the right time to pull in a CISO, or a security leader?”
Jon McLachlan, at 44:57
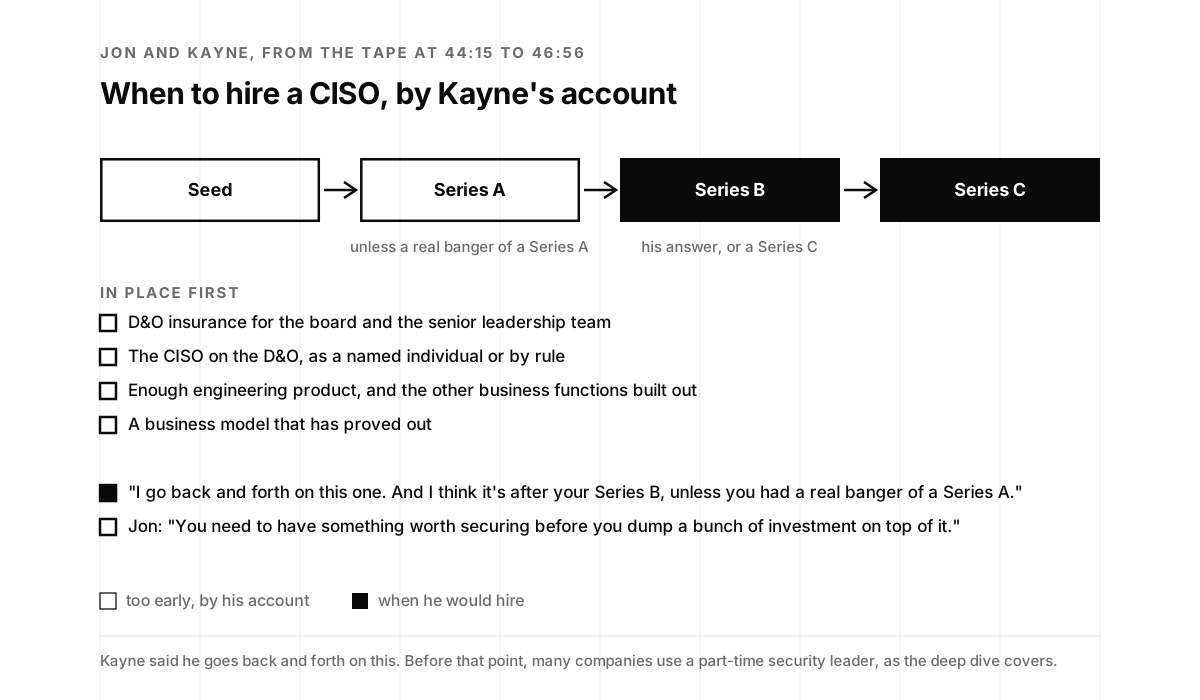
“I go back and forth on this one. And I think it’s after your Series B, unless you had a real banger of a Series A.”
Kayne McGladrey, at 45:01
Series B, maybe Series C, is when he would start thinking seriously about a security leader, because some things that have to be in place usually aren’t before then. One is D&O insurance for the board and the senior leadership team. Another is coverage for the CISO, “either as a named individual or by rule.”
“But if you’re not offering them a D&O spot in today’s climate, they have really no reason to join your company.”
Kayne McGladrey, at 45:43
Jon’s reply: “Huge liability.” Kayne added two more conditions. There has to be enough engineering product and enough of the other business functions built out, and he was careful to say that doesn’t make security an add-on. The point is centralizing the responsibility for communicating and overseeing security. Well-intentioned people can get a company to a Series B, with some hits and misses along the way.
“Companies with CISOs have hits and misses.”
Kayne McGladrey, at 46:25
“your business model has to prove out too before you bring in somebody to do security, right?”
Kayne McGladrey, at 46:38
Jon summed it up and Kayne agreed.
“You need to have something worth securing before you dump a bunch of investment on top of it.”
Jon McLachlan, at 46:43
Before that point, most companies need a part-time security leader more than a full-time one. Our guide to what a vCISO is, what it costs and when a startup needs one covers the trade-off, and our vCISO team comes with the security engineers to do the work.
Give back
Jon asked for final words of wisdom.
“I think you said it earlier on the show, Jon, and it’s really about giving back to the community.”
Kayne McGladrey, at 46:58
That means helping the field develop and diversify, and bringing different ways of thinking into what he called a challenging space over a challenging few decades. His question for senior leaders listening:
“how do I give back effectively and how do I incentivize people to get into this industry?”
Kayne McGladrey, at 47:21
“There’s a lot of different ways of thinking that we need that are not really well represented today.”
Kayne McGladrey, at 47:33
If you can influence a young person or someone changing careers, he said, take the chance, one-on-one or en masse. He has done it at scale before: Include Cybersecurity, the nonprofit he co-founded, set out to change who works in the field. And for anyone who wanted to find him, there was no ambiguity.
“There’s only the one of me. Thanks, mom and dad, for the unique name.”
Kayne McGladrey, at 47:58
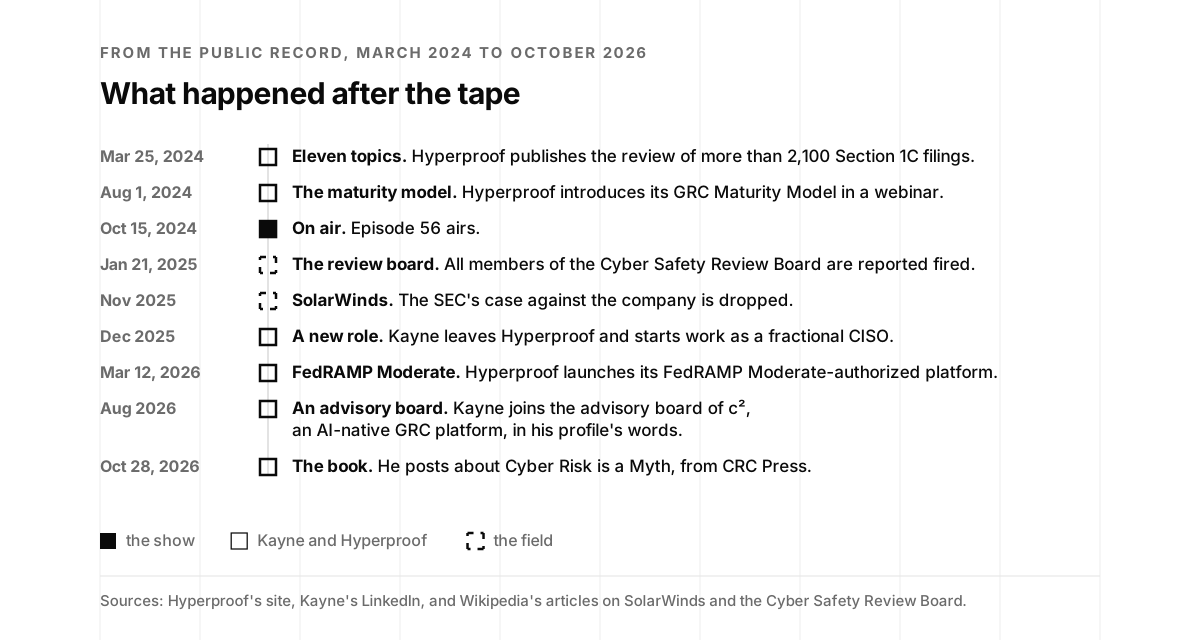
What happened after the tape
The post. On March 25, 2024, Hyperproof published the 11-topic analysis Kayne promised on the tape (Hyperproof). It covers more than 2,100 filings and names the SolarWinds case, which it gives as case 1:23-cv-09518 in the Southern District of New York.
The maturity model. On August 1, 2024, Hyperproof introduced its GRC Maturity Model in a webinar (Hyperproof), the model Kayne hoped to publish that year.
On air. The episode aired on October 15, 2024 (Podbean), and it is also on Spotify.
The review board. On January 21, 2025, it was reported that all members of the Cyber Safety Review Board had been fired (Wikipedia).
SolarWinds. In November 2025 the SEC’s case against SolarWinds was dropped (Wikipedia).
A new role. Kayne left Hyperproof in December 2025, after three years and four months, and has worked since as a fractional CISO for small and mid-market companies across seven western states, where, in his profile’s words, he helps them “translate risk into financial terms” (LinkedIn). Hyperproof’s author page now calls him “Former Field CISO at Hyperproof” (Hyperproof).
FedRAMP Moderate. On March 12, 2026, Hyperproof launched its FedRAMP Moderate-authorized platform (Hyperproof), the program Kayne said it was working on.
An advisory board. In August 2026 he joined the advisory board of c², which his profile describes as “an AI-native GRC platform.”
The book. His book, Cyber Risk is a Myth, is out from CRC Press, and on October 28, 2026 he posted about discussing it on Chris Clymer’s show (LinkedIn).
The part of the conversation that aged best is the plainest. Write the risk down, in one place, in a language everyone agreed on. Make the person who accepts a risk own what it costs. And collect evidence that each control runs, continuously, because the question after an incident is never whether you had a policy. It is what happened on Thursday.
Did you catch it? A six-question quiz
Six questions from the episode. Each answer links the moment in the transcript.
Quiz · six questions
Did you catch it?
Pick an answer for each. The explanation shows once you choose.
-
What did Kayne say about cybersecurity risk?
- It is the biggest risk a company has
- It doesn't exist on its own. There are business risks
- Only the CISO can own it
b. "saying that cybersecurity risk exists. It doesn't." Transcript, 12:56.
-
By Kayne's count, how many of the eleven topics in the best Section 1C disclosures did the SEC require?
- Four
- All eleven
- Two
a. "and the SEC only requires four of those." Transcript, 6:08.
-
What changed things when a business leader chose to accept a risk?
- A second signature on the form
- A report to the board
- Paying for the insurance on it
c. "Cool. So you're going to pay for the insurance on that." Transcript, 16:48.
-
Which board game did Kayne bring up?
- Monopoly
- Clue
- Risk
b. "do you remember the old Clue board game?" Transcript, 37:01.
-
In the guest badge example, what does the investigator ask?
- What happened Thursday
- Who designed the badges
- How many guests came that week
a. "they say, so what happened Thursday?" Transcript, 42:52.
-
When did Kayne think a startup should bring in a CISO?
- Before the first engineering hire
- Only after going public
- After the Series B, unless the Series A was a real banger
c. "And I think it's after your Series B, unless you had a real banger of a Series A." Transcript, 45:03.
Could you prove it?
Kayne’s bar was a legal one: if you were investigated, could you prove your controls ran? Eight questions on how close your program is.
Scorecard · eight questions
Could you prove it?
Answer for your program as it runs today. If two answers fit, pick the lower one.
-
If a customer, an insurer or a regulator asked you to prove one control ran last Thursday, what would you hand over?
- The policy that says we do it
- A screenshot from the last audit
- The record from that day, from a system that checks the control continuously
"You need to prove that you're actually collecting evidence on an hourly or a daily basis associated with the control operation." See Continuously.
-
When a business leader accepts a risk, what happens next?
- They sign a form and nothing changes
- They sign, and someone reviews it once a year
- They own the cost, insurance or a fix, in their own budget
"Cool. So you're going to pay for the insurance on that." See Then you pay for the insurance.
-
How many risk registers does your company keep?
- None. It lives in people's heads
- Several, by team or business unit
- One, with written definitions of impact everyone uses
"Everybody's got their own personal risk register." See Half can't find their critical risks.
-
What does the board see about security?
- Counts of alerts, patches and uploads
- A risk heat map
- Key risk indicators tied to the KPIs each leader is measured on
"And then you need to tie a KRI, a key risk indicator, to that." See A KPI and a key risk indicator.
-
Who checks the claims on your security page, trust center and questionnaire answers?
- Nobody. Marketing wrote them
- Security reviewed them once
- Each claim maps to a control with current evidence
"like the security statement on their website, which, as best as everyone can tell, was like written by marketing." See A statement written by marketing.
-
Where does the impact estimate for a risk come from?
- Security picks a number
- A model filled in with security's guesses
- The business leaders who know what the system makes
"let's partner with the business to figure out what is the potential impact there" See A fictional number.
-
Are decisions about risk written down?
- No
- Sometimes, in email
- Yes, in meeting notes kept in one place
"The funny thing, though, is if you don't write it down" See Professor Plum in the library.
-
Is your security leader, current or future, covered?
- We haven't thought about it
- We have D&O insurance, but it doesn't name them
- D&O covers them by name or by rule, and they're indemnified
"But if you're not offering them a D&O spot in today's climate, they have really no reason to join your company." See When to hire a CISO.
Your program reads well and would be hard to prove. Start with one register and one control you check every day, and make the next accepted risk come with its cost.
Some of it is backed by evidence and some of it is backed by memory. Find the controls you only check at audit time, tie one KRI to a leader's KPI, and write the next risk decision down.
Your evidence would hold up on a bad day. Keep it continuous, keep the register in one place, and make sure the person who signs for security is covered.
How long could a failed control go unnoticed?
Kayne gave no numbers for a typical company, so the defaults below are round examples. Count the controls your security page, questionnaires or filings describe, and sort them by how often anyone checks that they work.
Calculator
How long could a failed control go unnoticed?
Four counts: controls checked continuously, at least daily, controls checked about once a quarter, controls checked once a year at audit time, and controls nobody checks on any schedule.
Of the 40 controls you describe, 20% have continuous evidence. A control that failed today could go unnoticed for 210 days on average, and for 32 of them you couldn't show what happened last Thursday.
These defaults are examples, not figures from the episode. The average counts each control by the longest a failure could last before the next check: a day for continuous checks, 91 days for quarterly ones and a year for annual or unscheduled ones. Kayne's standard in Continuously was evidence collected "on an hourly or a daily basis," and A guest badge on Thursday shows what a single missing day looks like to an investigator.
From the Clue board game to Cyber Risk is a Myth
Everything on this page sits on one timeline, from the board game Kayne brought up to his book. Filter it by thread.
Timeline · 1943 to 2026
From the Clue board game to Cyber Risk is a Myth
Filter by thread. Dates are from the public record except where marked as part of this show.
- Cluedo
Anthony E. Pratt devises the game known as Clue in North America (Wikipedia, on this show).
- Conway's law
Melvin Conway's observation links an organization's communication to the systems it designs (Wikipedia, on this show).
- Safeco
Kayne becomes a software architect at Safeco Insurance, building single sign-on for 250,000 agents (LinkedIn, on this show).
- Centrify
He starts almost 11 years as worldwide professional services director (LinkedIn, on this show).
- The NIST Cybersecurity Framework
NIST publishes the framework the filings cite under several names (Wikipedia, on this show).
- Include Cybersecurity
He co-founds the nonprofit with Carmen Marsh (LinkedIn, on this show).
- CISO and CIO
He becomes CISO and CIO at Pensar Development, until April 2020 (LinkedIn, on this show).
- SolarWinds reports the breach
SolarWinds reports the Orion breach to the SEC (Wikipedia, on this show).
- The Cyber Safety Review Board
The board is established, modeled after the National Transportation Safety Board (Wikipedia, on this show).
- Hyperproof
Kayne joins Hyperproof, until December 2025 (LinkedIn, on this show).
- The SEC's rules
The SEC adopts rules for incident reports on Form 8-K and annual disclosures in the 10-K (SEC, on this show).
- The SEC sues SolarWinds
The suit alleges the company downplayed internal security risks (Wikipedia, on this show).
- The first incident reports
Form 8-K incident reports begin, and the annual disclosures cover fiscal years ending on or after December 15 (SEC, on this show).
- The 2024 benchmark
Hyperproof publishes its fifth annual IT risk and compliance benchmark (Hyperproof, on this show).
- The recording
Jon talks with Kayne while the first Section 1C filings are coming in (on this show).
- Eleven topics
Hyperproof publishes the review of more than 2,100 filings (Hyperproof, on this show).
- The GRC Maturity Model
Hyperproof introduces the model in a webinar (Hyperproof, on this show).
- Episode 56 airs
The episode goes out on Podbean and Spotify (Podbean, on this show).
- The review board's members
All members of the Cyber Safety Review Board are reported fired (Wikipedia, on this show).
- The SolarWinds case ends
The SEC's case against SolarWinds is dropped (Wikipedia, on this show).
- Fractional CISO
Kayne leaves Hyperproof and starts work as a fractional CISO (LinkedIn, on this show).
- FedRAMP Moderate
Hyperproof launches its FedRAMP Moderate-authorized platform (Hyperproof, on this show).
- An advisory board
He joins the advisory board of c² (LinkedIn, on this show).
- Cyber Risk is a Myth
He posts about his book on Chris Clymer's show (LinkedIn, on this show).
What to do this week
Five things, in the order Kayne’s argument suggests.
- Keep one register. Put every known risk in one risk register, and write down what low and high impact mean for each kind of risk, reputational, regulatory and financial, so the next assessment argues about the risk and not the words.
- Tie a KRI to each leader’s KPI. For each business leader, pick one number they’re measured on and one security signal that predicts it, the way data leaving the company predicts resignations for HR.
- Make accepted risks cost something. When a leader accepts a risk, put the cost of insuring it or fixing it in their budget, and record the decision in the meeting notes.
- Find your Thursdays. Take the controls your security page and questionnaire answers describe, and check whether you could show evidence for each one on any given day. The calculator above shows how big the gap is, and the scorecard covers the rest.
- Plan the security leader’s seat. Before you hire a CISO, make sure your D&O insurance covers them, by name or by rule, and that they’re indemnified. Until then, our vCISO team can lead the program, our SOC 2 Type 2 team can get the report your customers ask for, and you can book 15 minutes with us.