Podcast Episode 47

Episode 047 45 min

Clea Ostendorf, CISO of Code42, Securing the Unseen: on the Frontlines of Data Protection

with Clea Ostendorf · Code42

0:00 / 45:00

Also on Spotify, Apple Podcasts, YouTube, Podbean, Player FM

Episode 47 of The Security Podcast of Silicon Valley, published June 17, 2024. Host Jon McLachlan talks with Clea Ostendorf, then a field CISO at Code42, about wanting to be a diplomat and an actress, recruiting as matchmaking, stumbling into security through meetup and OWASP groups, what a field CISO does, insider risk and data loss prevention, the behaviors that put data at risk, a 30-second training video against the hammer, seeing source code uploaded to ChatGPT, trust centers and sharing between CISOs, putting the phone down, changing a status quo, the noise-to-value ratio and alerts nobody acts on, legal and HR as stakeholders, a roadmap walking out the door, mitigating a risk or signing it away, business drivers, Code42's move from backup to security, the company hat, the diversity hire and the personality hire, hiring for drive, critical infrastructure, personal data privacy, a universal basic income for your data, and seeing both sides.

Episode notes

Welcome to a new episode of the Security Podcast in Silicon Valley, a YSecurity production, where we delve into the ever-evolving landscape of cybersecurity, with Clea Ostendorf, Field CISO at Code42, as our distinguished guest. Clea's journey from an aspiring diplomat to a front-runner in cybersecurity offers profound insights into her unique approach that is reshaping the realm of data protection. Join us as our host Jon McLachlan, a seasoned expert in the field, engages Clea in a deep dive into how she merges traditional security methods with the pressing challenges of today’s digital world. Discover how Clea advocates for a collaborative security community and navigates the complex balance of work-life harmony in a demanding field. Tune in to uncover Clea’s strategies for fostering a culture of security that supports growth and innovation while protecting against insider threats. This episode is a must-listen for anyone interested in the intersections of technology, security, and corporate culture.

Hosted by Jon McLachlan — co-founder of YSecurity.

The deep dive

Does that matter?

Clea Ostendorf, then a field CISO at Code42, with Jon on wanting to be a diplomat and an actress, recruiting as matchmaking, stumbling into security, what a field CISO does, insider risk and the behaviors that put data at risk, a 30-second video against the hammer, source code in a chatbot, a duck on a pond, why sharing makes security stronger, putting the phone down, changing a status quo, the noise-to-value ratio, who your stakeholders are, a roadmap out the door, who owns the risk, from backup to security, the company hat, hiring for skills or for personality, critical infrastructure, taking control of your own data, being the product, and seeing both sides.

Episode 47 of The Security Podcast of Silicon Valley aired on June 17, 2024, with Jon McLachlan hosting. The guest was Clea Ostendorf, then a field CISO at Code42 (Podbean, Apple Podcasts, Spotify). The episode is called “Clea Ostendorf, CISO of Code42, Securing the Unseen: on the Frontlines of Data Protection.” It has no video version. Her LinkedIn lists her as co-founder and CEO of Wolfpack Security since June 2024 (LinkedIn), and Mimecast acquired Code42 in July 2024 (Wikipedia).

The question under the whole conversation came up eighteen minutes in. Clea was describing what happens when Code42 runs a trial at a company that thinks its controls are good enough.

“Somebody just took your roadmap out the door. Does that matter?”

Clea Ostendorf, at 18:15

Listen · Clea Ostendorf on episode 47, from 17:54
About 25 seconds: Clea on pushback, and the trials that prove the old controls wrong. The clip stops on its own. Read the full transcript.

This page follows the conversation in order: a section for each part of it, eighteen figures, ten clips from the tape, a LinkedIn post, the full transcript, and five tools: a quiz, a scorecard for whether your data protection fits how people work, a calculator for your noise-to-value ratio, a timeline, and a to-do list. Where the decodes of the tape disagree on a word, the transcript puts its best guess in brackets, and the page doesn’t quote those words.

From diplomat to security

Jon had read her LinkedIn before the show. He saw the law side of the house in her background, and maybe some international relations, and asked for a summary. Clea started with what she wanted to be.

“I wanted to be a diplomat, and an actress”

Clea Ostendorf, at 0:55

She did a little law internship and lived abroad. Then she needed a job to pay the bills, and somebody gave her an opportunity in sales and recruiting. She thought it was the best job ever. She sat at a desk, called people, heard what they wanted in a job, and then found them a match.

“and then I would find them a match.”

Clea Ostendorf, at 1:21

The business became transactional, she said, and more about margins and dollars than doing right by the person. So she looked for something different, and stumbled into security. Hacking into somebody’s bank account felt like “sort of a superpower.” She went to meetup groups and OWASP groups, and sought them out when she traveled. There she learned that the hacker side is only one part of it.

“now I know it’s called red teaming.”

Clea Ostendorf, at 2:17

The groups talked more about defense, protection and the human element.

“And it just got me hooked.”

Clea Ostendorf, at 2:25

That was fifteen years before, she said, and Jon repeated the number back. Her LinkedIn fills in the steps: an internship in Brazilian relations at an international law firm in 2009, then assistant manager at Enterprise Rent-A-Car, then technical recruiter and account manager at Signature Consultants from 2012, an account executive at Beacon Hill Staffing Group from 2014, and senior business development manager at nVisium, an application security firm, from March 2016. She joined Code42 in July 2019 as a senior insider risk security advisor, and became a field CISO in July 2023 (LinkedIn). Polina Morozov, a security recruiter, described her own work as matchmaking on episode 46.
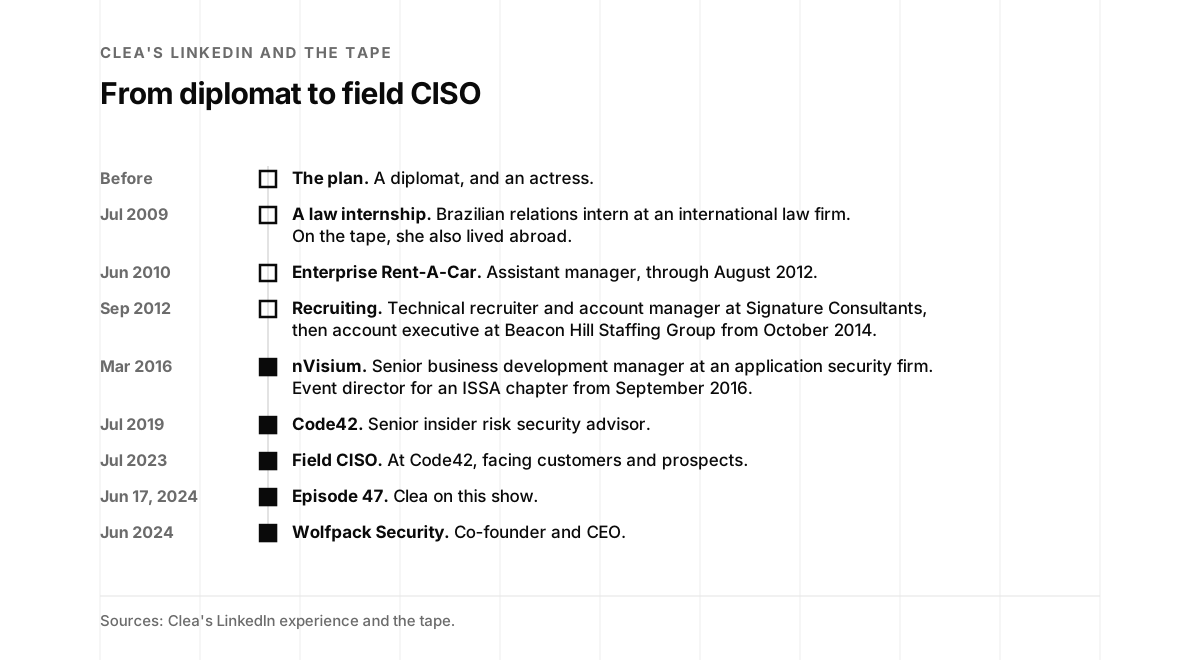
A timeline. Before: the plan, a diplomat and an actress. July 2009: a law internship, Brazilian relations intern at an international law firm, and on the tape she also lived abroad. June 2010: Enterprise Rent-A-Car, assistant manager, through August 2012. September 2012: recruiting, technical recruiter and account manager at Signature Consultants, then account executive at Beacon Hill Staffing Group from October 2014. March 2016, filled: nVisium, senior business development manager at an application security firm, and event director for an ISSA chapter from September 2016. July 2019, filled: Code42, senior insider risk security advisor. July 2023, filled: field CISO at Code42, facing customers and prospects. June 17, 2024, filled: episode 47, Clea on this show. June 2024, filled: Wolfpack Security, co-founder and CEO.
Clea's path, from the tape and her LinkedIn. Sources: the episode, LinkedIn and Wikipedia.

People I want on my side

Once she had the hook, Jon said, there was no turning back. Clea agreed. She called security people the smartest she had ever been with, the most clever and creative.

“and frankly, people I want on my side.”

Clea Ostendorf, at 2:40

When she started working for a security consulting company, she knew the people around her had probably seen everything. Her line for them was that they were still talking to her, so they were cool.

All of us field CISOs

Jon asked what a field CISO does at Code42. Clea said nobody has settled that yet.

“We are all figuring that out”

Clea Ostendorf, at 2:58

A group of field CISOs had gotten together and asked each other how they’re measured, what they do, and how they’re out in the market. Her answer was that the role comes in different flavors. A chief information security officer is the senior executive who sets the strategy and program that protect an organization’s information (Wikipedia). A field CISO does that work facing outward. Clea’s job was with customers and prospects: help them feel comfortable with the product, with how Code42 secures it, and with its point of view.

“challenge the status quo of what they’re doing around data protection.”

Clea Ostendorf, at 3:25

There’s the traditional way people want to approach data protection, she said, and there’s the reality of what it looks like today. Her job was to bridge that gap. She had a peer who did the inside work, supporting existing customer programs.

“It’s good to live on a bridge”

Jon McLachlan, at 3:42

She loved that group discussion: smart people who had done amazing things, still trying to figure it out together.

Two more field CISOs came on this show later. Jacob Berry, field CISO at Clumio, told how he stumbled into the same job on episode 58, and Kayne McGladrey, field CISO at Hyperproof, made the case for business risk on episode 56.
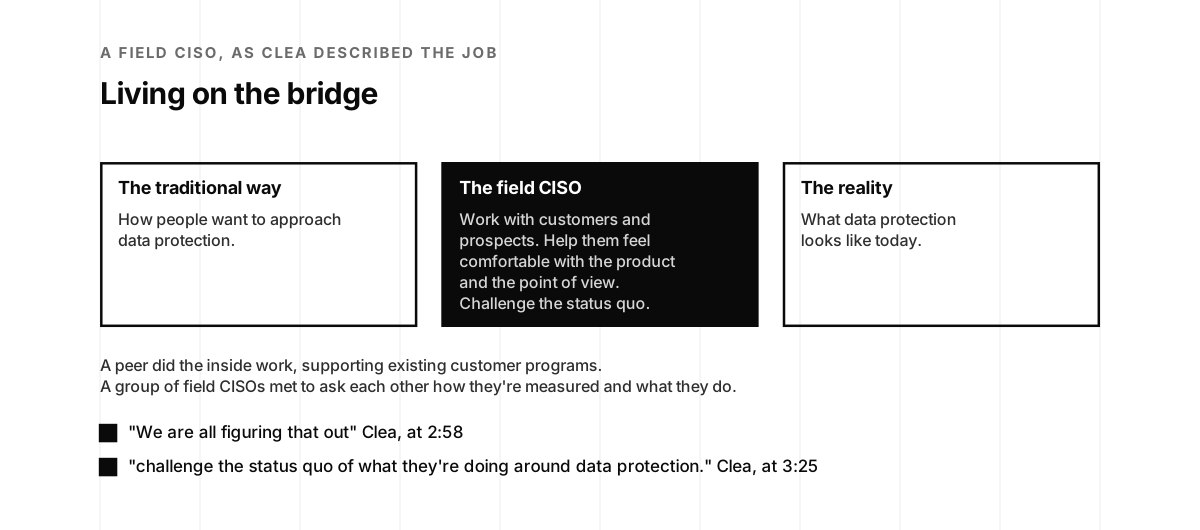
Three cards. The traditional way: how people want to approach data protection. The field CISO, filled: work with customers and prospects, help them feel comfortable with the product and the point of view, and challenge the status quo. The reality: what data protection looks like today. Below: a peer did the inside work, supporting existing customer programs. A group of field CISOs met to ask each other how they're measured and what they do. Then: "We are all figuring that out" Clea, at 2:58. And: "challenge the status quo of what they're doing around data protection." Clea, at 3:25
The field CISO's bridge, as Clea described it. Source: the episode.

Behaviors that put data at risk

Jon asked what Code42 does better than anyone else in the world.

“So Code42 is a data protection platform.”

Clea Ostendorf, at 4:24

It falls into insider risk or insider threat, she said, and data loss prevention. An insider threat comes from people within the organization, such as employees, former employees, contractors or business associates (Wikipedia). Data loss prevention software is a set of strategies and technologies that stop sensitive data from being sent or disclosed without authorization (Wikipedia). Code42 sees data move across endpoints, cloud and email, and gives risk indicators that show where to focus. It doesn’t start by classifying data, she said, because data no longer sits still.

“we’re thinking about what are the behaviors that would put data at risk.”

Clea Ostendorf, at 4:57

Her examples were a departing employee, new hires, an incident, a reorg or a layoff. Around those moments, Code42 watches where data moves and how people work with it, and the team decides whether to act. Wikipedia describes Incydr, the product, as a SaaS data protection tool for enterprises that guards intellectual property, source code and trade secrets, launched in September 2020 (Wikipedia).
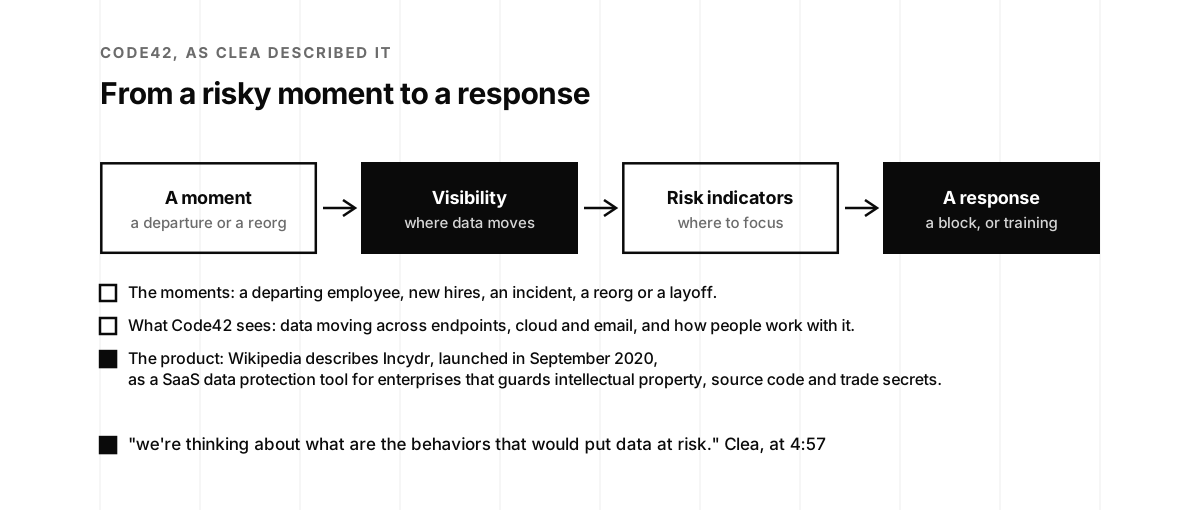
Four boxes joined by arrows. A moment, a departure or a reorg. Visibility, filled, where data moves. Risk indicators, where to focus. A response, filled, a block or training. Below, a list. The moments: a departing employee, new hires, an incident, a reorg or a layoff. What Code42 sees: data moving across endpoints, cloud and email, and how people work with it. The product, filled: Wikipedia describes Incydr, launched in September 2020, as a SaaS data protection tool for enterprises that guards intellectual property, source code and trade secrets. Then: "we're thinking about what are the behaviors that would put data at risk." Clea, at 4:57
From a moment that puts data at risk to a response, as Clea described Code42. Sources: the episode and Wikipedia.

Here’s the hammer

The responses run from the traditional block to something softer. Clea acted out the soft one.

“You’re syncing to iCloud. We don’t recommend that.”

Clea Ostendorf, at 5:29

“Here’s a 30-second video on how to reshape that behavior.”

Clea Ostendorf, at 5:31

She said they had seen effective changes in how people handle data that way. The other way sounds like this.

“Here’s the hammer. I’m telling you no.”

Clea Ostendorf, at 5:42

“It sounds like a long-term strategic investment in people.”

Jon McLachlan, at 5:45

Clea said you have to make that investment. You can tell people not to do something, she said, and it still won’t stick.

“unless they think there’s consequences or it affects them, it’s not really going to register.”

Clea Ostendorf, at 5:56

Listen · Clea Ostendorf on episode 47, from 5:18
About 25 seconds: Clea on the 30-second video and the hammer. The clip stops on its own. Read the full transcript.

Ganesh Krishnan of Anzenna made a similar case for contextual training on episode 34.
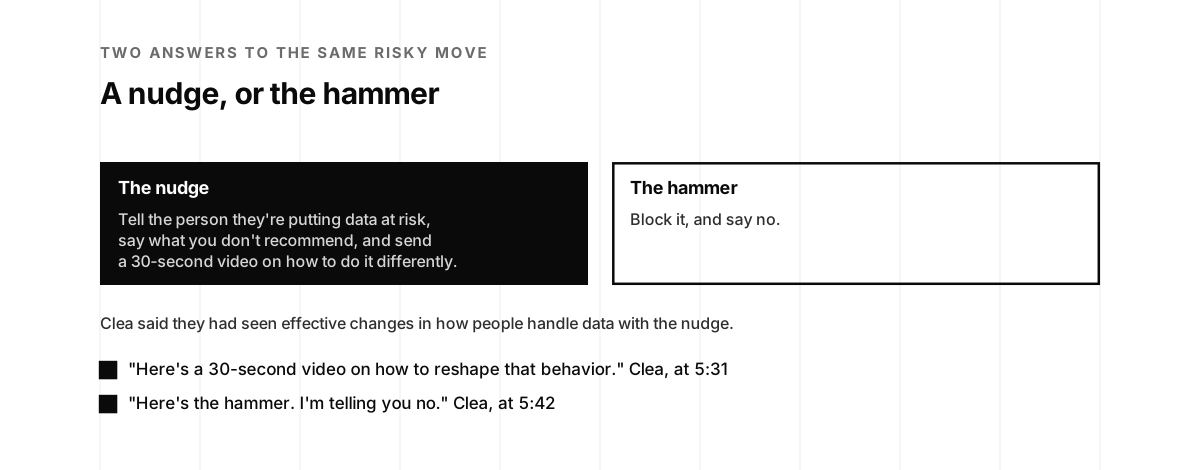
Two cards. The nudge, filled: tell the person they're putting data at risk, say what you don't recommend, and send a 30-second video on how to do it differently. The hammer: block it, and say no. Below: Clea said they had seen effective changes in how people handle data with the nudge. Then: "Here's a 30-second video on how to reshape that behavior." Clea, at 5:31. And: "Here's the hammer. I'm telling you no." Clea, at 5:42
Two ways to answer the same risky move. Source: the episode.

Source code in a chatbot

Jon tested it with a case. Could the software catch someone who had pasted company code into ChatGPT?

“you just uploaded half of the file from our private GitHub repo”

Jon McLachlan, at 6:04

Clea said yes.

“We can see large data uploads.”

Clea Ostendorf, at 6:18

“Source code is one of the strong use cases that we have”

Clea Ostendorf, at 6:22

Source code has value in itself, she said, and in dollars. Code42 has a lot of visibility into how it moves, and ways to control that.

A duck on a pond

Jon asked about a typical day. It depends on whether she’s in the office, Clea said. Her company was hybrid, and she went in twice a week. She’s a morning person, and likes a little time to herself before the day starts. Then come customer and prospect meetings, content, and community events. Those always look flawless from outside, she said, as if nobody did any work and everyone just showed up. Anyone who has hosted one knows the image of a duck gliding across a lake and paddling hard underneath. That was her: “Smooth on the surface,” and paddling hard below. Jon said he’d never met an unhappy duck.

Sharing makes us stronger

Jon asked what people get wrong about working in security. Clea named two things. The first is that everyone is highly technical. The second is the old habit of keeping quiet.

“the more information we give you, the more vulnerable we become.”

Clea Ostendorf, at 8:16

She saw a big change in how companies share. Trust centers lay out how a company is secured, what it’s doing and what its process is. CISOs talk to each other about breaches they’re dealing with.

“And people are collaborating, which just makes us all stronger, right?”

Clea Ostendorf, at 8:46

Jon loves the sense of community in the security community. He couldn’t imagine being so closed off that you can’t learn and grow, and asked where the growth mindset is for a lone wolf.

Clea said it would be isolating.

“you would feel like you’re alone battling these threat actors”

Clea Ostendorf, at 9:12
Listen · Clea Ostendorf on episode 47, from 8:23
About 25 seconds: Clea on the move from secrecy to sharing. The clip stops on its own. Read the full transcript.
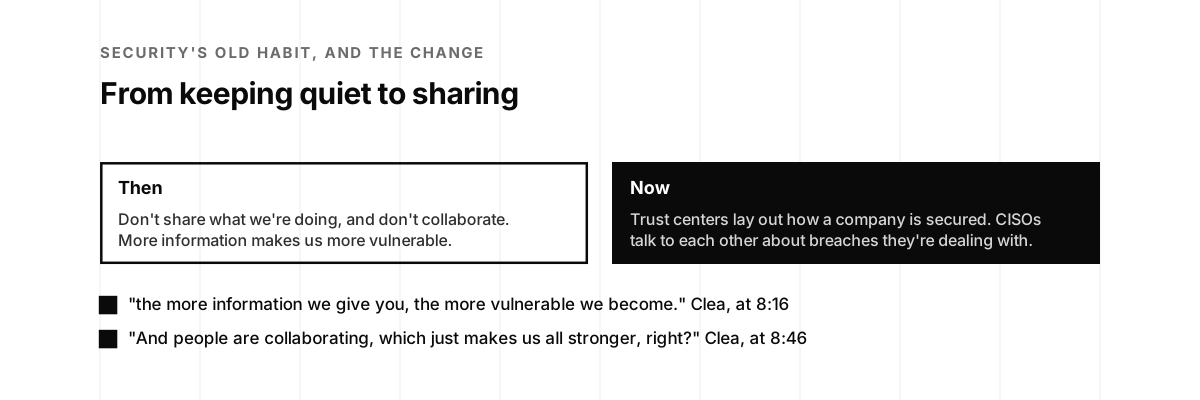
Two cards. Then: don't share what we're doing, and don't collaborate, because more information makes us more vulnerable. Now, filled: trust centers lay out how a company is secured, and CISOs talk to each other about breaches they're dealing with. Below: "the more information we give you, the more vulnerable we become." Clea, at 8:16. And: "And people are collaborating, which just makes us all stronger, right?" Clea, at 8:46
Keeping quiet, and the move to sharing. Source: the episode.

Put the phone down

Security can look like constant firefighting from the outside: high stress, high risk, high impact to the business. Jon asked how she finds a healthy balance with her personal time. Clea said the pull is real in this job, and in most jobs, when you care about the work.

“it’s really easy to get pulled in and want to do something 24/7”

Clea Ostendorf, at 10:25

“I think setting boundaries is important, but more so putting the damn phone down.”

Clea Ostendorf, at 10:36

She uses do not disturb mode, even for a few hours in the evening or the morning. Human nature, at least hers, is to solve a problem right away. Without a break, that catches up with you.

“you’re going to burn out.”

Clea Ostendorf, at 11:12

The cost is “You’re going to make mistakes.” Jon put it in racing terms.

“you can’t finish the race in red line.”

Jon McLachlan, at 11:29

Listen · Clea Ostendorf on episode 47, from 11:08
About 25 seconds: Clea on burning out, and Jon on the red line. The clip stops on its own. Read the full transcript.

To recharge, Clea moves. She had just started lifting weights, and yoga, walking or running all count. Her ask is small: one thing for herself in the day, thirty minutes or an hour.

“I’m not asking for hours.”

Clea Ostendorf, at 13:25

With that done, she said, she can give in every capacity.
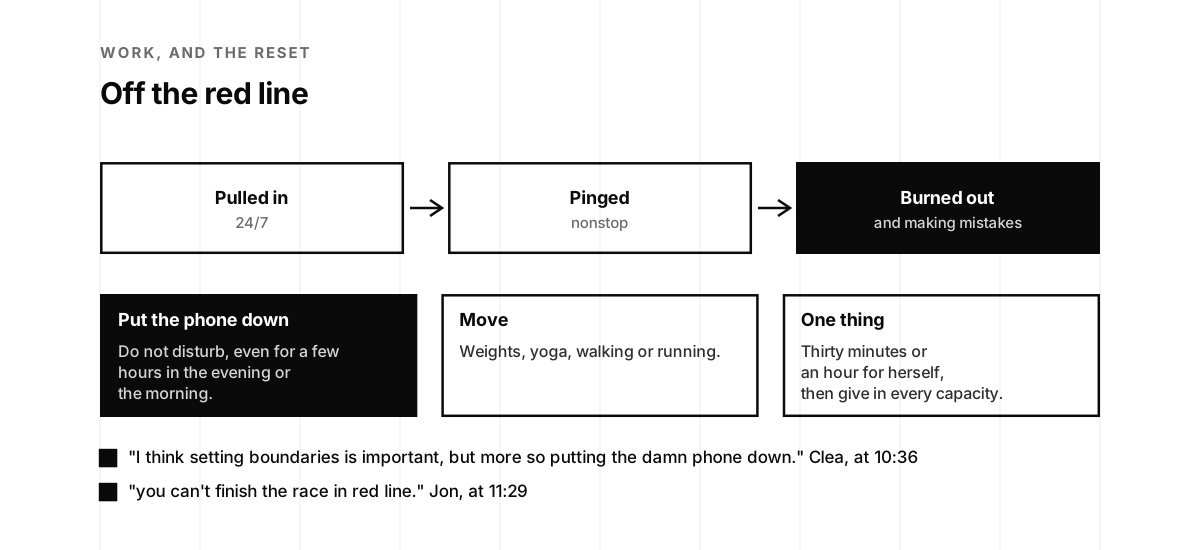
Three boxes joined by arrows. Pulled in, 24/7. Pinged, nonstop. Burned out, filled, and making mistakes. Below, three cards. Put the phone down, filled: do not disturb, even for a few hours in the evening or the morning. Move: weights, yoga, walking or running. One thing: thirty minutes or an hour for herself, then give in every capacity. Then: "I think setting boundaries is important, but more so putting the damn phone down." Clea, at 10:36. And: "you can't finish the race in red line." Jon, at 11:29
Work at red line, and the reset. Source: the episode.

Long-term plays

Jon asked where she gets her news when things are going down in security. Clea started with podcasts.

“podcasts are sort of long-term plays, right?”

Clea Ostendorf, at 14:26

You listen for an hour, she said, and you understand how someone thinks and how they would approach a problem. She loves the CISO Series, where David Spark has a show called Top Headlines, “a five-minute fast little snippet.” She also tracks major incidents and digs in when one affects Code42 or its customers. Jon is a huge fan of podcasts too, which surprised nobody.

Changing a status quo

Jon asked her to look ahead: what does success look like for her and her team? Clea had been with Code42 “about five years,” and said Code42 had spent that time changing how people think about data protection.

“anyone who is changing a status quo knows that it is not easy.”

Clea Ostendorf, at 15:27

“It takes longer than anyone expects.”

Clea Ostendorf, at 15:32

She thought the market had turned. People were saying they can’t just block and tackle their data anymore.

“That is not realistic in how people work together, right?”

Clea Ostendorf, at 15:48

Her example was the conversation itself. She and Jon were sharing a Google document back and forth.

“You’re not trusted in my network, but we’re still sharing data back and forth, right?”

Clea Ostendorf, at 16:01

Most of the market agreed that you need a different way, she said. The next step was harder.

“Now we need to actually show people how it’s possible”

Clea Ostendorf, at 16:15

Code42 was doing that with many big customers, and she called it a work in progress.
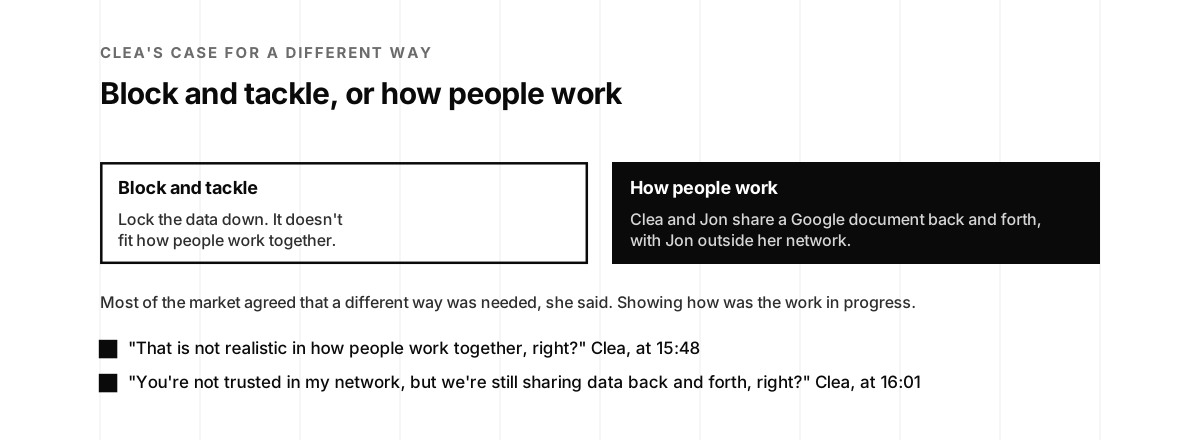
Two cards. Block and tackle: lock the data down, and it doesn't fit how people work together. How people work, filled: Clea and Jon share a Google document back and forth, with Jon outside her network. Below: most of the market agreed that a different way was needed, she said, and showing how was the work in progress. Then: "That is not realistic in how people work together, right?" Clea, at 15:48. And: "You're not trusted in my network, but we're still sharing data back and forth, right?" Clea, at 16:01
Block and tackle, and how people work together. Source: the episode.

The noise-to-value ratio

Every security tool is trying to figure out how to cut “the noise-to-value ratio,” she said.

“Oh, I’m going to die underneath all of these false positives.”

Jon McLachlan, at 16:36

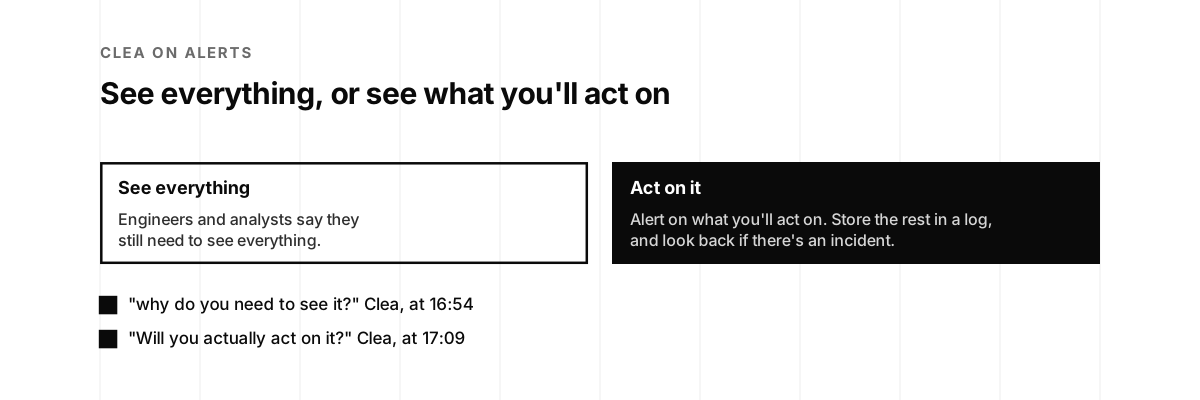
A false positive is a test result that says a condition is there when it isn’t (Wikipedia). Clea goes back and forth on this with the people who use the tools, the security engineers and analysts. They tell her they still need to see everything. If you won’t act on it and it adds no value, she asks:

“why do you need to see it?”

Clea Ostendorf, at 16:54

“Can’t you just store it in a log and look back”

Clea Ostendorf, at 16:55

Jon agreed: keep it as history. Clea named what Code42 was working on.

“The materiality of what you’re seeing.”

Clea Ostendorf, at 17:06

“Will you actually act on it?”

Clea Ostendorf, at 17:09

Listen · Clea Ostendorf on episode 47, from 16:40
About 30 seconds: Clea on alerts nobody acts on. The clip stops on its own. Read the full transcript.

The calculator puts a number on it.

Two cards. See everything: engineers and analysts say they still need to see everything. Act on it, filled: alert on what you'll act on, store the rest in a log, and look back if there's an incident. Below: "why do you need to see it?" Clea, at 16:54. And: "Will you actually act on it?" Clea, at 17:09
See everything, or see what you'll act on. Source: the episode.

Who are your stakeholders?

Jon asked what keeps companies from moving to this newer approach. Clea said the first question Code42 asks is about people outside security.

“who are your external stakeholders outside of security?”

Clea Ostendorf, at 17:25

That means legal, and it means HR. “Are you engaging with HR?” she asked. The business has to say which data matters.

“if you have indication from the business on what data matters”

Clea Ostendorf, at 17:37

You can’t focus on everything, she said. With the business in the loop, a security team can get ahead of events that put data at risk. If a reorg is coming, find out which team it affects and add monitoring there.
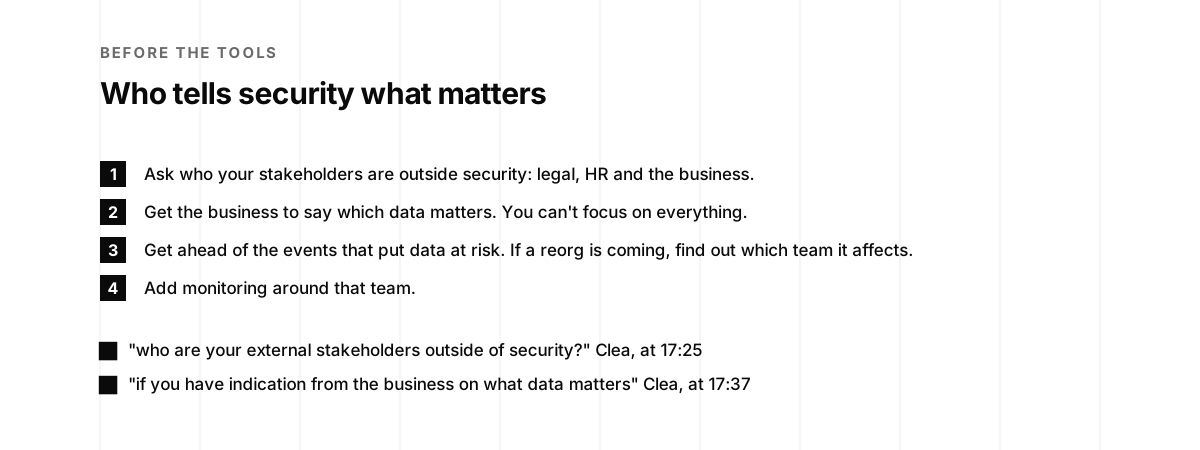
Four numbered steps. One: ask who your stakeholders are outside security, legal, HR and the business. Two: get the business to say which data matters, because you can't focus on everything. Three: get ahead of the events that put data at risk, and if a reorg is coming, find out which team it affects. Four: add monitoring around that team. Below: "who are your external stakeholders outside of security?" Clea, at 17:25. And: "if you have indication from the business on what data matters" Clea, at 17:37
The business tells security which data matters and when. Source: the episode.

Does that matter?

Then she named the obstacles.

“Initially, there’s pushback.”

Clea Ostendorf, at 17:55

“I just want to own this little castle, this little piece.”

Clea Ostendorf, at 17:56

The first obstacle is not wanting to involve other people. The second is that change is hard. People ask why they should rip and replace a tool when they think their controls are good enough.

“And every time we go into a POV, we prove it wrong.”

Clea Ostendorf, at 18:09

The trial turns up what the existing control missed, and then comes the question at the top of this page. Jon and Clea played out what comes next. It’s in the news. The people who left start a company with the data they took. Then you’re in a legal battle, she said.
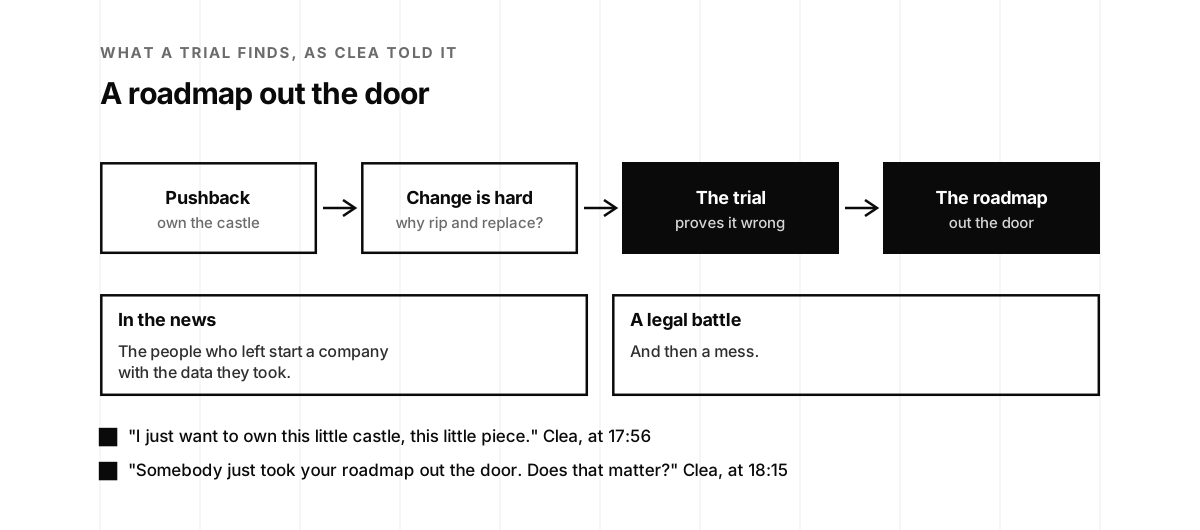
Four boxes joined by arrows. Pushback, own the castle. Change is hard, why rip and replace? The trial, filled, proves it wrong. The roadmap, filled, out the door. Below, two cards. In the news: the people who left start a company with the data they took. A legal battle: and then a mess. Then: "I just want to own this little castle, this little piece." Clea, at 17:56. And: "Somebody just took your roadmap out the door. Does that matter?" Clea, at 18:15
What a trial finds, and what comes after. Source: the episode.

Mitigate it or sign it away

Jon described the choices a business has. One is to “actively mitigate it,” with controls, mechanisms like DLP, and processes. If the business doesn’t want to mitigate the risk, it covers it another way. It can buy insurance, he said, or

“you get someone else to sign off on it, or another business owner to own it.”

Jon McLachlan, at 18:54

Kayne McGladrey told what happens after a business leader signs to accept a risk on episode 56. Clea had a live example, and kept the company’s name out of it. It was a large organization with lots of customers, sharing data back and forth.

“And they’ve had multiple insider incidents”

Clea Ostendorf, at 19:07

“where a managing consultant has taken project plans and customer information”

Clea Ostendorf, at 19:10

They paid big fines, she said, and “almost lost a customer.” They still hadn’t invested in Code42 or any product, she said. It didn’t have to be Code42. They didn’t want to upset the culture by seeming to watch the consultants too closely.

“but you’re going to take that business risk.”

Clea Ostendorf, at 19:38
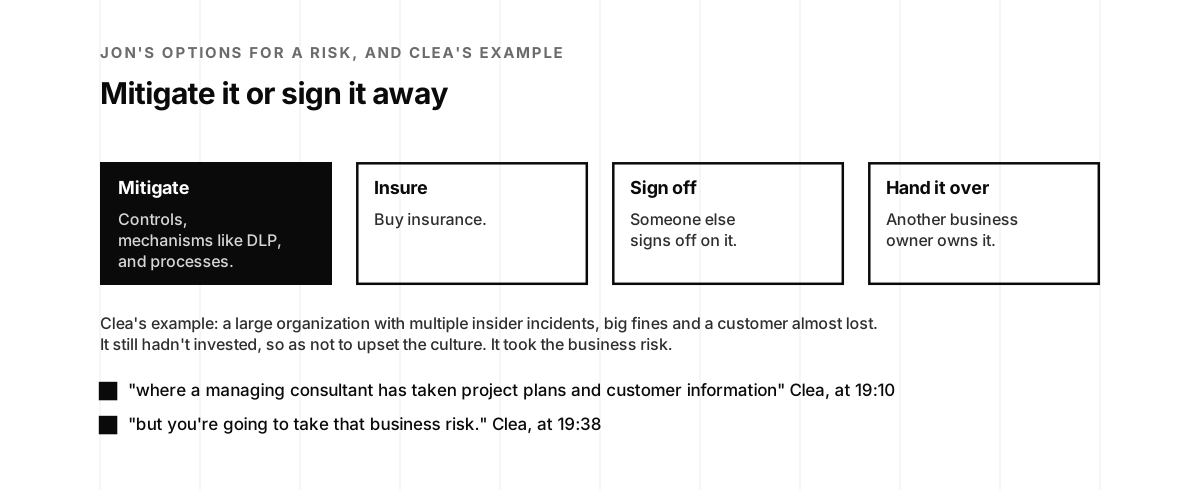
Four cards. Mitigate, filled: controls, mechanisms like DLP, and processes. Insure: buy insurance. Sign off: someone else signs off on it. Hand it over: another business owner owns it. Below: Clea's example, a large organization with multiple insider incidents, big fines and a customer almost lost. It still hadn't invested, so as not to upset the culture. It took the business risk. Then: "where a managing consultant has taken project plans and customer information" Clea, at 19:10. And: "but you're going to take that business risk." Clea, at 19:38
The ways to handle a risk Jon named, and the one Clea's example chose. Source: the episode.

No business driver, no initiative

Jon said there’s only so much security can do when a leader has decided to swallow a risk, knowing what it means and what it costs.

“There’s always going to be a cost associated with it.”

Jon McLachlan, at 19:53

Protecting your data is cheaper for the business, he said, and cheaper than what might happen if you don’t.

“without a business driver behind security initiatives, there is no security initiative.”

Jon McLachlan, at 20:10

A business leader has to see and feel the problem and the pain point, and decide to protect the data, the process or the IP. Clea said who carries it when they don’t.

“It’s the security team.”

Clea Ostendorf, at 20:40

The stress goes up when the business doesn’t back them. They know it’s a problem, and if something goes wrong, it’s their fault. It’s hard, she said, and Jon added that they don’t have the tools to solve it.
Listen · Jon McLachlan on episode 47, from 20:08
About 35 seconds: Jon on business drivers, and Clea on who carries the risk. The clip stops on its own. Read the full transcript.
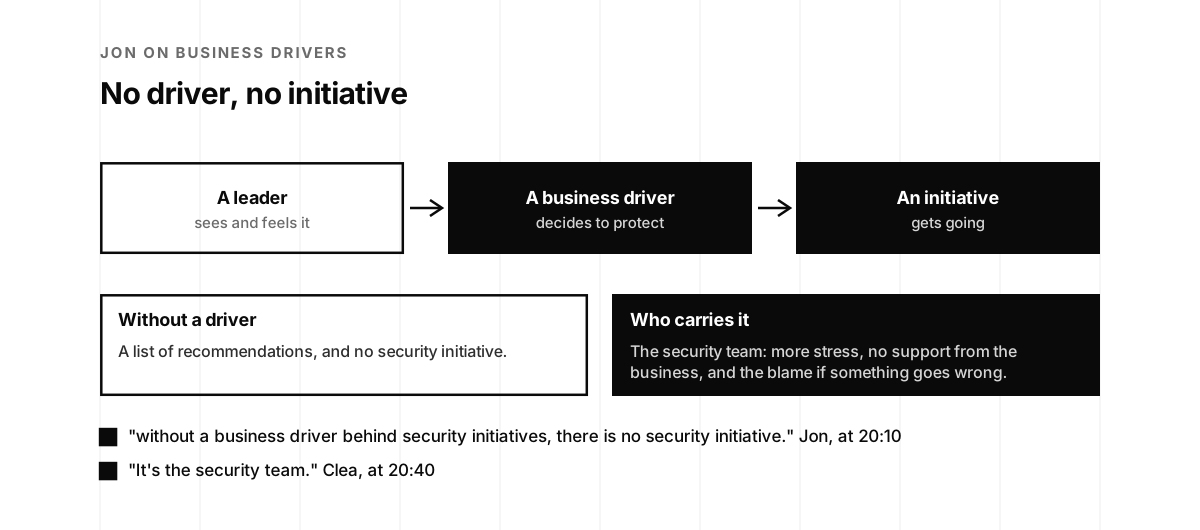
Three boxes joined by arrows. A leader, sees and feels it. A business driver, filled, decides to protect. An initiative, filled, gets going. Below, two cards. Without a driver: a list of recommendations, and no security initiative. Who carries it, filled: the security team, with more stress, no support from the business, and the blame if something goes wrong. Then: "without a business driver behind security initiatives, there is no security initiative." Jon, at 20:10. And: "It's the security team." Clea, at 20:40
Without a business driver, and who carries the risk. Source: the episode.

From backup to security

Jon asked about her most challenging day at Code42. Clea said it was the beginning.

“I would say when I started, it was the most challenging.”

Clea Ostendorf, at 21:03

The new job was only part of it.

“It was really shifting a mindset of an organization who has been very successful in what they were doing.”

Clea Ostendorf, at 21:09

“We came from backup,” she said, and the company was shifting into security. Code42 created CrashPlan in 2007. In August 2017 it announced it would shut down CrashPlan for Home to focus on enterprise and small business, and in September 2020 it launched Incydr (Wikipedia). The two products ask for different habits.

“backup is, you set and forget it, and you move on”

Clea Ostendorf, at 21:26

Security is different, she said.

“you constantly have to be tuning”

Clea Ostendorf, at 21:31

Security means looking into things, setting up alerts, removing things, and telling people what matters. She had to win over a smart engineering team and a smart sales team, who asked her what she knew about any of this. Then COVID hit, everyone went home, and that brought its own challenges. Jon said Code42 was lucky to have her. Clea pointed to the team.

“Good leadership is really important.”

Clea Ostendorf, at 22:23

“People who listen and will fight your battles.”

Clea Ostendorf, at 22:26
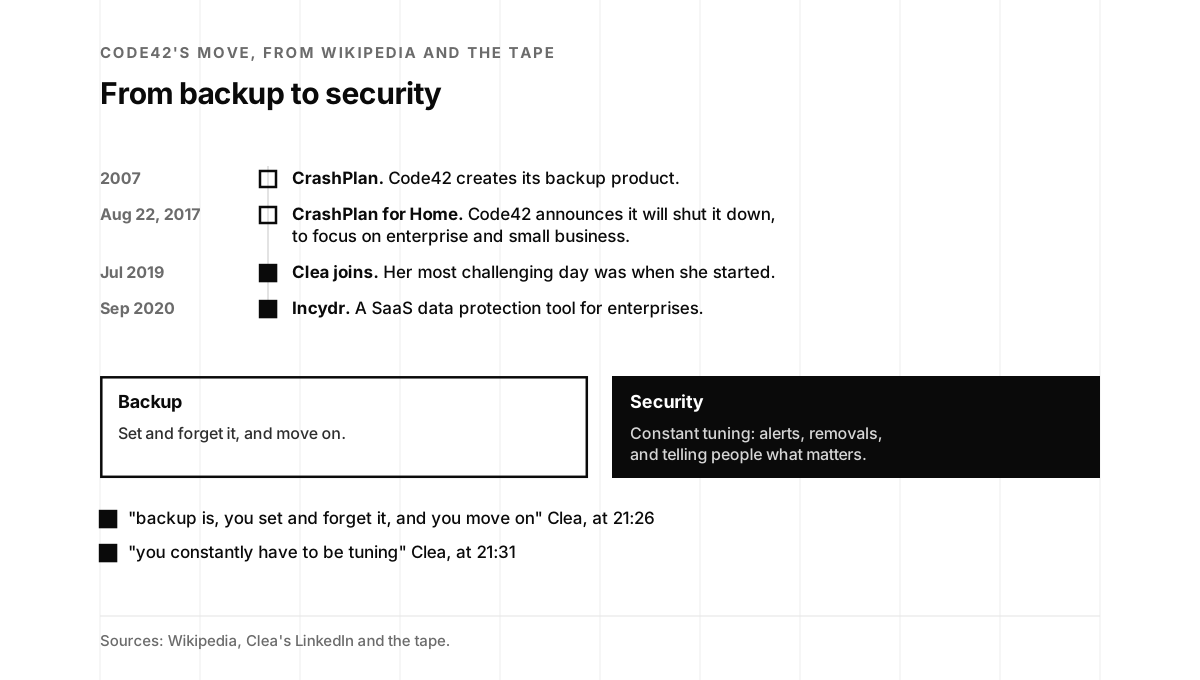
A timeline. 2007: CrashPlan, Code42 creates its backup product. August 22, 2017: CrashPlan for Home, Code42 announces it will shut it down, to focus on enterprise and small business. July 2019, filled: Clea joins, and her most challenging day was when she started. September 2020, filled: Incydr, a SaaS data protection tool for enterprises. Below, two cards. Backup: set and forget it, and move on. Security, filled: constant tuning, with alerts, removals, and telling people what matters. Then: "backup is, you set and forget it, and you move on" Clea, at 21:26. And: "you constantly have to be tuning" Clea, at 21:31
Set and forget, and constant tuning, with Code42's own move from backup to security. Sources: the episode and Wikipedia.

The company hat

Jon said it’s always interesting to find alignment inside a company. People get political, especially at larger companies, and process turns into bureaucracy. His fix is to go back to the basics, and remind everyone that they’re all in the same boat and on the same team. Everyone takes off their personal hats, or their little fiefdoms, and puts on the company hat. Then they think about what’s right for the company and the customer, together. “Oh, remove the ego,” Clea said, and Jon added that you check egos at the door. Jon used the same image of everyone in one boat with Ganesh Krishnan on episode 34.

The diversity hire

Jon said it must be harder in a field dominated by men. Clea said it’s another dynamic.

“I call myself the diversity hire sometimes.”

Clea Ostendorf, at 23:26

At one panel, she was told they were so happy to have a woman on it. She said she was glad she qualified that way. Jon said diversity is overlooked on teams.

“And it’s the differences that we all bring to the table”

Jon McLachlan, at 23:42

A team of copies is an echo chamber, he said, and misses critical gaps. Clea agreed, and added the part people skip.

“how are you going to make them feel like they are part of the team?”

Clea Ostendorf, at 24:40

She has worked in industries dominated by men her whole life, and some team outings don’t interest her.

“I want to go get a pedicure. I don’t want to go to a baseball game.”

Clea Ostendorf, at 24:59

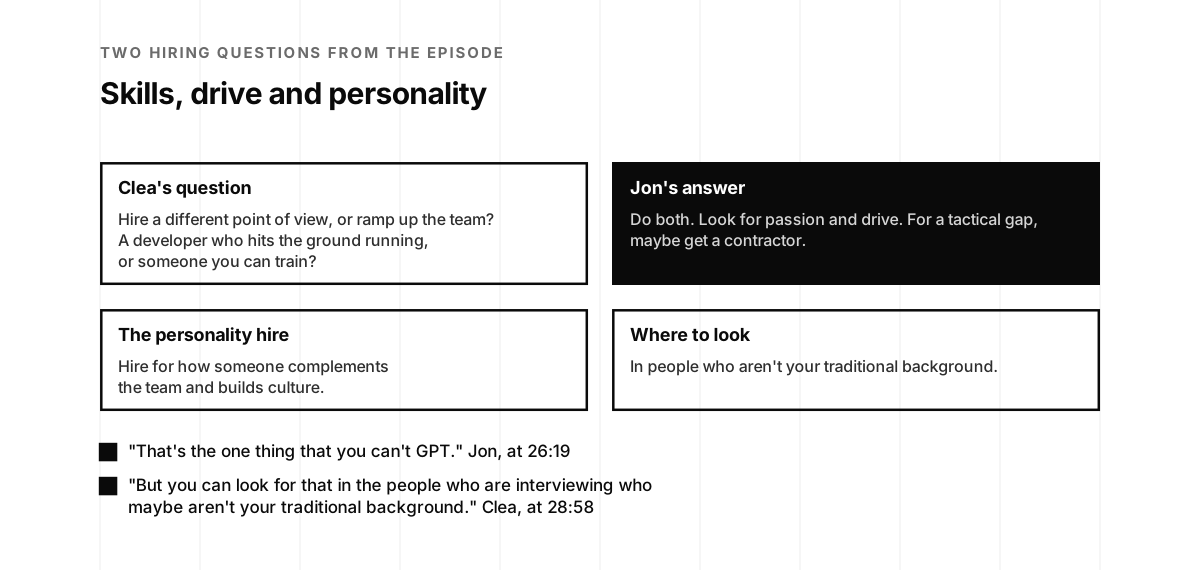
Jon offered to come along. Then Clea asked him a hard question: when do you hire someone with a different point of view, and when do you need to ramp up the team? She had put the same question to a recruiter. Do you need a developer who can hit the ground running, or someone you can train who might shape the direction?

You can’t GPT the drive

“You do both.”

Jon McLachlan, at 25:47

He called that a cop-out answer, then explained. He has interviewed many people. He used to look for specific things, and you still have to check that a person fits the skills. Being a little outside their comfort zone, learning and growing, is a good thing. Now he looks for passion and drive.

“That’s the one thing that you can’t GPT.”

Jon McLachlan, at 26:19

You can’t read it in Wiki or get a degree in it, he said, and with it “you can accomplish anything.” At some point he dropped the belief that the tech was what mattered most.

“actually, people matter at the end of the day.”

Jon McLachlan, at 27:54

Trust people to learn the technologies, he said. For a tactical gap, maybe don’t hire at all: “Maybe just get a contractor.”

Clea brought up a trend on TikTok, the personality hire.

“You hire more on the way that they’re going to complement the team”

Clea Ostendorf, at 28:39

That’s a hard thing for a hiring manager to say to a recruiter, she said: “go find me somebody charismatic and fun.”

“But you can look for that in the people who are interviewing who maybe aren’t your traditional background.”

Clea Ostendorf, at 28:58

“you can’t put that in the job description, right?”

Jon McLachlan, at 29:06

Those are soft skills, Jon said, and “good cultural fit” may be what recruiters mean by it. You still need skills to drive the business. Then he defined the business.

“A business is an entity that exists to make money.”

Jon McLachlan, at 29:33

A company is a group of people with a mission to solve a pain point and make people’s lives better. Usually those people are called customers.
Listen · Clea Ostendorf on episode 47, from 28:28
About 35 seconds: Clea on the personality hire. The clip stops on its own. Read the full transcript.
Four cards in two rows. Clea's question: hire a different point of view, or ramp up the team, a developer who hits the ground running, or someone you can train? Jon's answer, filled: do both, look for passion and drive, and for a tactical gap, maybe get a contractor. The personality hire: hire for how someone complements the team and builds culture. Where to look: in people who aren't your traditional background. Below: "That's the one thing that you can't GPT." Jon, at 26:19. And: "But you can look for that in the people who are interviewing who maybe aren't your traditional background." Clea, at 28:58
Two hiring questions from the conversation, and the answers. Source: the episode.

Critical infrastructure

Jon asked about the threats on her mind. Clea said she’d go broad first and then narrow it down, like a funnel.

“what I am scared about is our critical infrastructure.”

Clea Ostendorf, at 30:35

Critical infrastructure is what governments consider essential for a society and an economy to function (Wikipedia). She said she doesn’t know enough about securing it.

“I know there’s plenty of vulnerabilities.”

Clea Ostendorf, at 30:42

She told of a pen testing company that ran a bunch of pen tests on water treatment facilities. The question there was “where do you want us to begin,” she said.

“But I think we are really vulnerable.”

Clea Ostendorf, at 30:52

Look at how people got through COVID, she said. Crisis doesn’t bring out the best in many people. Her worry was what happens when “electricity, internet, water” are gone.

“what is society going to turn into, and how quickly are we going to devolve?”

Clea Ostendorf, at 31:15
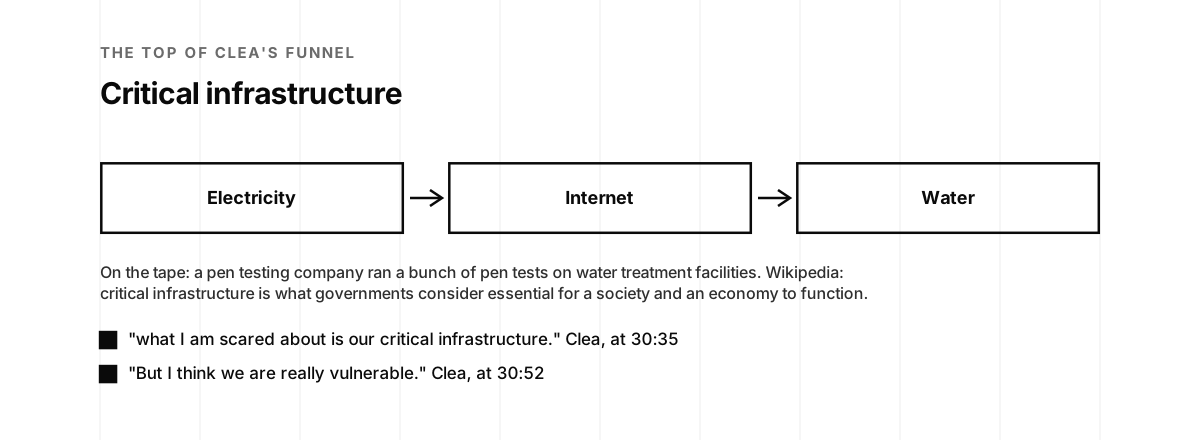
Three boxes joined by arrows: electricity, internet, water. Below: on the tape, a pen testing company ran a bunch of pen tests on water treatment facilities. Wikipedia: critical infrastructure is what governments consider essential for a society and an economy to function. Then: "what I am scared about is our critical infrastructure." Clea, at 30:35. And: "But I think we are really vulnerable." Clea, at 30:52
The top of Clea's funnel. Sources: the episode and Wikipedia.

Take control of your data

Then she moved to the narrow end of the funnel, the thing she thinks everyone is already dealing with.

“The more realistic thing that I think we’re all dealing with is our personal data privacy”

Clea Ostendorf, at 31:40

People have given out their information all over the internet. Now you can choose whether cookies track you, she said, and two years before that you couldn’t. A cookie is a small block of data a website’s server places on your device while you browse (Wikipedia).

“our data is still funneling and being collected and manipulated.”

Clea Ostendorf, at 31:58

“how do you start to take control over what information, personal information about you, is out there?”

Clea Ostendorf, at 32:05

She was starting to see products aimed at the general population, and she liked that. They give a little more sense of control.

“at least you can clean up the data spread that’s out there about your personal information.”

Clea Ostendorf, at 32:26

A data broker is a person or company that collects personal data about people, mostly from public records (Wikipedia). Leigh Honeywell of Tall Poppy talked about self-defense tools for people online on episode 5.

“I look forward to living in a future that has better privacy, now, for all of us.”

Jon McLachlan, at 32:33

Listen · Clea Ostendorf on episode 47, from 31:53
About 40 seconds: Clea on taking control of your personal data. The clip stops on its own. Read the full transcript.

Jon asked where cyber espionage is headed, and what it means for international relations.

“I assume everybody has access to everything already.”

Clea Ostendorf, at 32:51

All the nation states that want to see what we’re doing already can, she said. The interesting part is what comes next.

“What would be interesting is how it’s weaponized, right?”

Clea Ostendorf, at 32:58

The news is a business

Later, Jon said the news is a business.

“Yeah, the news is unfortunately a business.”

Jon McLachlan, at 34:28

“It’s designed to make money,” he said, with the same mechanisms social media uses to grab attention. His morning routine is an app called the Hourly News, which plays short headline clips from several news services in different countries, among them NPR, Fox News and CBC in Canada. The big events show up on all of them, told differently. Nobody is lying, he said, and you still hear the slant. You realize “it’s being curated.”

“You need to use your brain when you’re consuming information.”

Clea Ostendorf, at 36:07

Ask about their genesis

Jon asked for her favorite interview question.

“And I love to ask people their genesis.”

Clea Ostendorf, at 36:27

“Like, how did you get into what you’re doing today?”

Clea Ostendorf, at 36:31

You learn a lot about someone’s approach to life that way, she said. If they had a hard job and didn’t like it, what did they do to improve it?

“I am all about not staying static, right?”

Clea Ostendorf, at 36:42

She asks where they were then, how they got where they are, and what sacrifices they made or what paths they took. The answers show how someone is motivated, and how they’ll learn and fit into the team. Jon called it double-clicking on life experiences.

A huge book

Jon asked for a book or movie that changed how she sees the world.

“I am a voracious reader.”

Clea Ostendorf, at 37:31

Jon told listeners there are many books behind her. She reads and listens, so she couldn’t name just one. She likes stories everyone thinks they know, told from another side.

“I like to listen to books or read that tell a story that we all maybe know from a different perspective.”

Clea Ostendorf, at 37:45

She had just finished Covenant of Water, which she called about a foot big, an undertaking and well worth it. One part tells the story of World War II through what was happening in India.

“a perspective that you would never traditionally get from the Western history books that we see.”

Clea Ostendorf, at 38:12

The Covenant of Water is a 2023 novel by the physician and author Abraham Verghese. It follows three generations of a Malayali family in Kerala, in southwest India, from 1900 to 1977 (Wikipedia). Jon said different perspectives are exactly what he looks for in the news.

Invest in relationships

Jon asked what she would tell her younger self.

“When I was younger, I spread myself very thin.”

Clea Ostendorf, at 38:46

Maybe that helped, she said, because she had lots of experiences. Time is worth more to her now than when it seemed endless. Jon added the other half of being young: all the time in the world and no money.

“I didn’t focus on investing in relationships.”

Clea Ostendorf, at 39:17

She was happy floating around then, and a bit superficial. Now she values “one-on-one conversation” and getting to know how someone ticks. Jon said he was the same way, until it clicked for him.

“this tech stuff is great, but people are what matter.”

Jon McLachlan, at 39:58
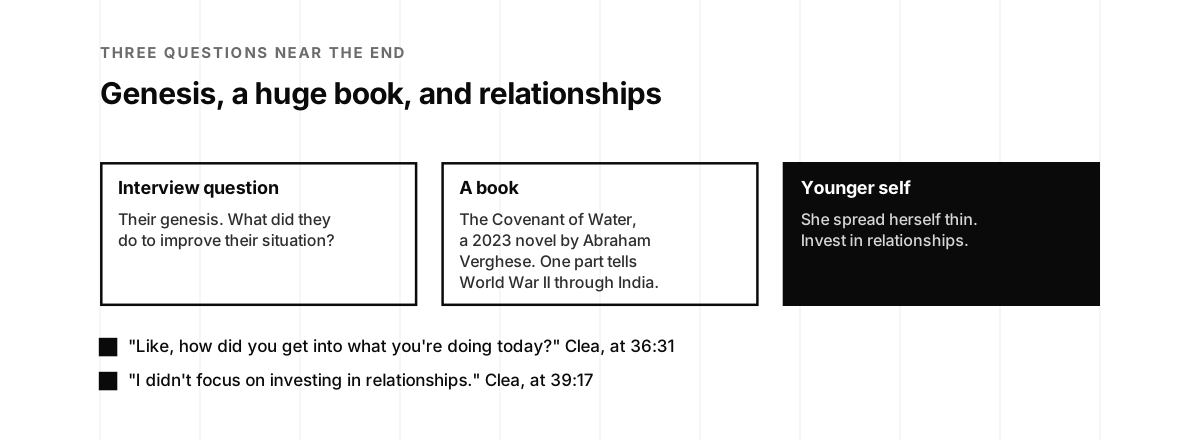
Three cards. Interview question: their genesis, and what did they do to improve their situation? A book: The Covenant of Water, a 2023 novel by Abraham Verghese, and one part tells World War II through India. Younger self, filled: she spread herself thin, and invest in relationships. Below: "Like, how did you get into what you're doing today?" Clea, at 36:31. And: "I didn't focus on investing in relationships." Clea, at 39:17
Three questions near the end of the show, and Clea's answers. Sources: the episode and Wikipedia.

A giant red button

Jon said many entrepreneurs listen to the show, and asked for one tool she wishes existed. Clea named it.

“Personal privacy.”

Clea Ostendorf, at 40:26

“because I just feel very exposed on the internet.”

Clea Ostendorf, at 40:29

Jon said everything people have uploaded over the past 15, 20 or 30 years is about to get a sweep from AI.

“And even if you didn’t tag yourself in a photo, people are going to know that was you.”

Jon McLachlan, at 40:49

Jon pictured a giant red button that wipes it all, and asked how much she would pay to wipe her history on the internet. Then he pictured another service, one that analyzes your exposure to risk on the internet, as in “Give me a number for how much I might lose.” Clea framed the question she’d want answered.

“How could my data be weaponized against me?”

Clea Ostendorf, at 41:38

She wants to take ownership of what’s been put out there. Trevor Hilligoss pointed listeners to a free personal exposure check on episode 86.

Listen · Jon McLachlan on episode 47, from 41:31
About 25 seconds: Jon on an exposure score, Clea on how data gets weaponized, and Jon's own try at the problem. The clip stops on its own. Read the full transcript.

You are the product

Jon had looked at this problem before. When he was building Peacemaker, which was all B2B, the team looked late at a B2C product for this exact problem. Adoption is hard, he said. Many people have accepted that they aren’t private, or think they aren’t important enough to matter. When you don’t pay for the product, he said, you are the product. Companies are positioning themselves to monetize our data, he said, and advertising works on us even when we don’t like to admit it. Michael Moore made a similar point about free AI tools on episode 73. Clea shared an idea she liked. Companies that use your browsing history, your clicks and whatever else they collect would let you opt in, and pay you for it.

“they’ll pay you a universal basic income, right?”

Clea Ostendorf, at 42:59

“Or you opt out of that, and they can’t touch anything you engage with.”

Clea Ostendorf, at 43:07

A universal basic income is a proposal where everyone in a population regularly gets a minimum income with no means test (Wikipedia). Most people would opt in and get paid, she said, and the companies would still make their money by advertising to the right people.
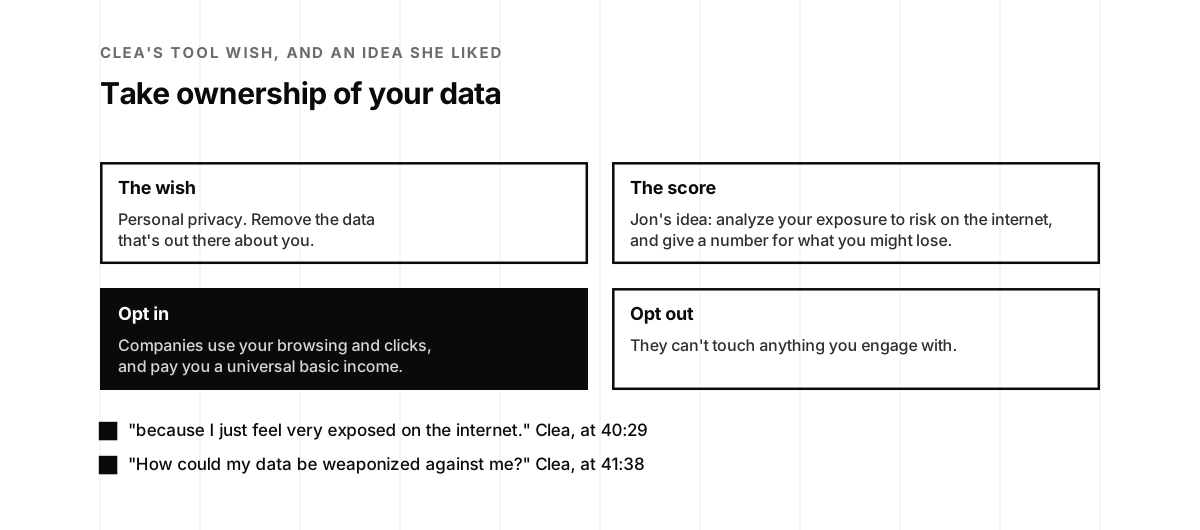
Four cards in two rows. The wish: personal privacy, and remove the data that's out there about you. The score: Jon's idea, analyze your exposure to risk on the internet, and give a number for what you might lose. Opt in, filled: companies use your browsing and clicks, and pay you a universal basic income. Opt out: they can't touch anything you engage with. Below: "because I just feel very exposed on the internet." Clea, at 40:29. And: "How could my data be weaponized against me?" Clea, at 41:38
Clea's tool wish, and the opt-in idea. Sources: the episode and Wikipedia.

Phase two

Clea turned the idea back on Jon.

“So, Jon, maybe you should invent that one.”

Clea Ostendorf, at 43:34

He’d squeeze it in if he had the spare time, he said, and turned it back on her.

“Maybe you’ve got the entrepreneurial spirit yourself.”

Jon McLachlan, at 43:41

“Perhaps,” she said, and called it phase two. Jon offered to team up as co-founders, and Clea told listeners they heard it here first. Her LinkedIn dates her start as co-founder and CEO of Wolfpack Security to June 2024, the month the episode aired (LinkedIn).

See both sides

Jon asked for her pearls of wisdom.

“always try and approach things from the other side.”

Clea Ostendorf, at 43:59

“See both sides.”

Clea Ostendorf, at 44:01

Jon said it’s enriching to step outside our comfort zone, and to remember the world is colored by the lenses we look through.

“We can try on different lenses.”

Jon McLachlan, at 44:16

Clea said there had been a lot of laughing, which is always a good way to start a day.

Listen · Clea Ostendorf on episode 47, from 43:56
About 20 seconds: Clea's parting advice, and Jon on lenses. The clip stops on its own. Read the full transcript.

What happened after the tape

Wolfpack Security. Clea’s LinkedIn lists her as co-founder and CEO of Wolfpack Security from June 2024. Her description there is about changing how the industry approaches penetration tests, by asking how vulnerabilities are introduced and what it takes to fix them (LinkedIn). The company describes itself as “Boutique offensive security, built for the enterprise,” with deep, manual testing, and lists itself as SOC 2 Type II compliant (LinkedIn). A penetration test is an authorized simulated cyberattack on a computer system, run to evaluate its security (Wikipedia).

Mimecast bought Code42. In July 2024, Mimecast acquired Code42. Mimecast is a British information security company founded in 2003, specialized in email security and risk management, and owned by Permira (Wikipedia).

Her post on the 105 problems. On September 22, 2026, Clea wrote that finding vulnerabilities is cheap. Her example was 569 vulnerabilities that came from 105 underlying problems. One kind of program optimizes for throughput: find it, ticket it, fix it, close it. The other asks why the house keeps catching fire. On the tape, she asked whether you will act on what you see.

Clea on the 105 problems behind 569 vulnerabilities.

Clea Ostendorf · September 22, 2026
Her post, with Wolfpack's article on why finding more vulnerabilities isn't the goal anymore. View on LinkedIn.

More from her feed. On October 5, 2026, she shared Wolfpack’s article “Manual Pentesting Isn’t Dead. Manual Everything Is.” Her summary was to automate the known risk and use human creativity to find the rest (LinkedIn). On October 28, 2026, she wrote: “Assumed breach exercises should be on every leadership roadmap.” (LinkedIn).

More on this show. Jacob Berry named insider threats as his biggest risk on episode 58. Trevor Hilligoss, a former FBI agent, talked about an insider at a bank on episode 86. On the blog, Stop Saying No makes the case for knowing your data over a blanket block, Shadow AI covers the AI tools your team already uses, and Pentest Once a Year? covers what enterprise buyers expect from a penetration test.
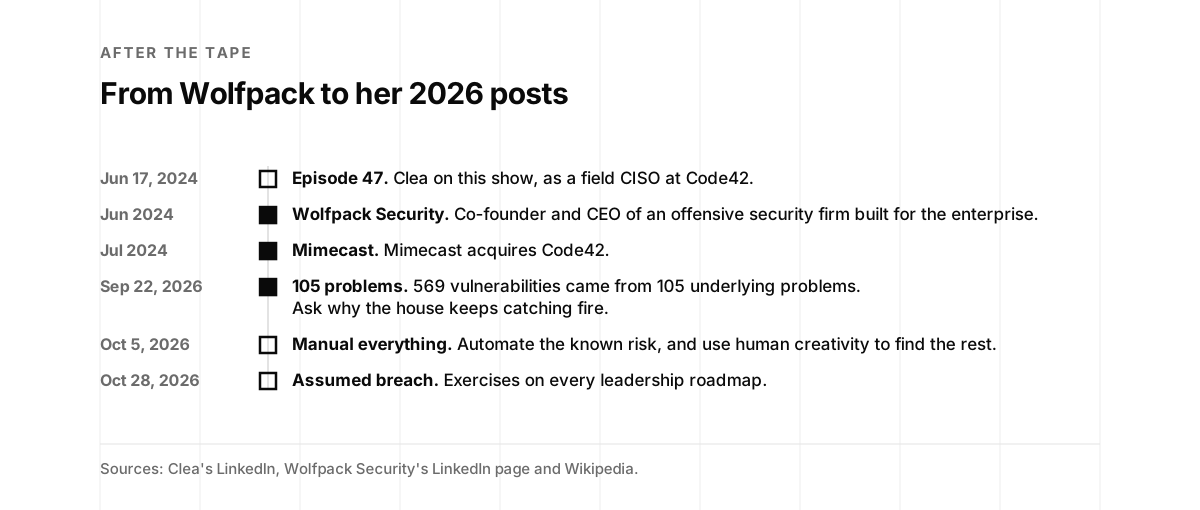
A timeline. June 17, 2024: episode 47, Clea on this show, as a field CISO at Code42. June 2024, filled: Wolfpack Security, co-founder and CEO of an offensive security firm built for the enterprise. July 2024, filled: Mimecast acquires Code42. September 22, 2026, filled: 105 problems, 569 vulnerabilities came from 105 underlying problems, so ask why the house keeps catching fire. October 5, 2026: manual everything, automate the known risk, and use human creativity to find the rest. October 28, 2026: assumed breach exercises on every leadership roadmap.
After the tape, from Wolfpack to her 2026 posts. Sources: LinkedIn and Wikipedia.

Did you catch it? A seven-question quiz

Seven questions from the episode. Each answer links the moment in the transcript.

Quiz · seven questions

Did you catch it?

Pick an answer to see whether you caught it.

  1. What did Clea want to be, once upon a time?

    a. "I wanted to be a diplomat, and an actress" Transcript, 0:55.

  2. What does Code42 look at, in place of classifying data?

    b. "we're thinking about what are the behaviors that would put data at risk." Transcript, 4:57.

  3. What's the softer response when someone puts data at risk?

    c. "Here's a 30-second video on how to reshape that behavior." Transcript, 5:31.

  4. What should you do with what nobody will act on, in Clea's view?

    a. "Can't you just store it in a log and look back" Transcript, 16:55.

  5. Which stakeholders outside security does Clea ask about first?

    b. "Are you engaging with HR?" Transcript, 17:31.

  6. In Clea's example, what did a managing consultant take?

    c. "where a managing consultant has taken project plans and customer information" Transcript, 19:10.

  7. What does Clea's favorite interview question ask about?

    b. "And I love to ask people their genesis." Transcript, 36:27.

Does your data protection fit how people work?

Eight questions on how your company protects data from the people who handle it. Each tip quotes the tape or paraphrases it, and links its section.

Scorecard · eight questions

Does your data protection fit how people work?

Answer for your company as it runs today. If two answers fit, pick the lower one.

  1. Has the business told security which data matters most?

    • No. Security guesses
    • For some teams
    • Yes, and it's written down

    "if you have indication from the business on what data matters" See Who are your stakeholders?.

  2. Do legal and HR take part in your insider risk program?

    • No
    • When something goes wrong
    • Yes, from the start

    "Are you engaging with HR?" See Who are your stakeholders?.

  3. Does monitoring change around departures, new hires, reorgs and layoffs?

    • No
    • For departures only
    • Yes, for each of them

    Clea's examples of moments that put data at risk. See Behaviors that put data at risk.

  4. When someone puts data at risk by mistake, what happens?

    • Nothing, or a block with no reason given
    • A block and a ticket
    • A short nudge that explains why

    "Here's a 30-second video on how to reshape that behavior." See Here's the hammer.

  5. Can you see source code or customer data going into AI tools?

    • No
    • In some tools
    • Yes, in all of them

    "We can see large data uploads." See Source code in a chatbot.

  6. Do your alerts get acted on?

    • Most are never looked at
    • Some get acted on
    • We alert on what we'll act on and log the rest

    "Will you actually act on it?" See The noise-to-value ratio.

  7. When the business declines a control, who owns the risk?

    • Security, by default
    • Nobody says
    • A named business owner signs for it

    "you get someone else to sign off on it, or another business owner to own it." See Mitigate it or sign it away.

  8. Do you share what you're seeing with peers at other companies?

    • Never
    • Sometimes
    • Yes, and we publish how we're secured

    "And people are collaborating, which just makes us all stronger, right?" See Sharing makes us stronger.

The little castle

Security works alone, and the business hasn't said what matters. Start with legal and HR, and ask which data you'd regret losing.

A work in progress

The basics are there. Next, watch the moments that put data at risk, and trade the hammer for a nudge where you can.

Bridge the gap

Your data protection fits how people work. Keep cutting the alerts nobody acts on, and keep the business owning its risks.

What’s your noise-to-value ratio?

Every security tool is trying to cut the noise-to-value ratio, Clea said. This calculator puts a number on yours.

Calculator

What's your noise-to-value ratio?

Three numbers: the alerts your team gets in a day, the percent of them worth acting on, and the minutes it takes to look at one.

23.8hours a day on alerts nobody acts on
25alerts a day worth acting on
19.0alerts of noise for each one of value

Of 500 alerts a day, 25 are worth acting on. The rest take 23.8 hours a day to look at, a noise-to-value ratio of 19.0 to 1.

Every default here is a placeholder: put in your own numbers. Clea's answer to the rest is to store it in a log and look back if there's an incident, as in The noise-to-value ratio.

From diplomat to Wolfpack

Clea’s path, Code42’s, and the episodes on this site that pick up the thread. Filter by topic.

Timeline

From diplomat to Wolfpack

  1. Code42

    Founded as an IT consulting company. The name honors Douglas Adams: in The Hitchhiker's Guide to the Galaxy, 42 is the answer to the ultimate question (Wikipedia).

  2. CrashPlan

    Code42 creates its backup product (Wikipedia, on this page).

  3. A law internship

    Brazilian relations intern at an international law firm (LinkedIn, on this page).

  4. Enterprise Rent-A-Car

    Assistant manager, through August 2012 (LinkedIn).

  5. Recruiting

    Technical recruiter and account manager at Signature Consultants, through September 2014 (LinkedIn).

  6. Beacon Hill

    Account executive at Beacon Hill Staffing Group, through March 2016 (LinkedIn).

  7. nVisium

    Senior business development manager at an application security firm, through July 2019 (LinkedIn).

  8. ISSA

    Event director for an ISSA chapter, through September 2019. ISSA is a not-for-profit association of information security professionals (Wikipedia, LinkedIn).

  9. CrashPlan for Home

    Code42 announces it will shut it down to focus on enterprise and small business (Wikipedia).

  10. Code42

    Clea joins as a senior insider risk security advisor (LinkedIn, on this page).

  11. Incydr

    Code42 launches its data protection product, and its leaders publish the book Inside Jobs (Wikipedia, on this page).

  12. Field CISO

    Clea becomes a field CISO at Code42 (LinkedIn, on this page).

  13. The Covenant of Water

    Abraham Verghese's novel, the book Clea had just finished (Wikipedia, on this page).

  14. Episode 34

    Ganesh Krishnan of Anzenna on why security awareness training is broken (episode page).

  15. Episode 46

    Polina Morozov on recruiting for security teams (episode page).

  16. Episode 47

    Clea on the show (Podbean, transcript).

  17. Wolfpack Security

    Clea becomes co-founder and CEO (LinkedIn, on this page).

  18. Mimecast

    Mimecast acquires Code42 (Wikipedia, on this page).

  19. Episode 56

    Kayne McGladrey, field CISO at Hyperproof, on business risk (episode page).

  20. Episode 58

    Jacob Berry, field CISO at Clumio, on insider threats (episode page).

  21. Episode 73

    Michael Moore on why free AI tools are paid for with data (episode page).

  22. Episode 86

    Trevor Hilligoss on the human behind the keyboard (episode page).

  23. 105 problems

    Clea on asking why 105 underlying problems produced 569 vulnerabilities (LinkedIn, on this page).

  24. Manual everything

    Clea shares Wolfpack's article on manual pen testing (LinkedIn).

  25. Assumed breach

    Clea puts assumed breach exercises on every leadership roadmap (LinkedIn).

What to do this week

Five things, in the order of the episode.

  1. Ask the business what data matters. Bring in legal and HR, as in Who are your stakeholders?. Then take the scorecard.
  2. Watch the moments that put data at risk. Departures, new hires, reorgs and layoffs, as in Behaviors that put data at risk.
  3. Try the nudge before the hammer. Pick one risky habit, such as syncing to a personal cloud, and answer it with a short explanation, as in Here’s the hammer.
  4. Count the alerts nobody acts on. Put a number on them with the calculator, and log the rest, as in The noise-to-value ratio.
  5. Close the door on your roadmap. Our Counter Business Espionage & IP Protection builds insider-risk programs, trade-secret controls and leak monitoring. Our Corporate Shadow-AI Detection & Mitigation finds the AI tools touching company data. If you want to talk it through, book 15 minutes with us.

Key takeaways

  1. Ask the business which data matters

    Clea's first question is who your stakeholders are outside security, such as legal and HR. Only the business can say which data matters, and you can't focus on everything.

  2. Watch the moments that put data at risk

    Code42 starts from moments like a departing employee, new hires, a reorg or a layoff, and watches where data moves and how people work with it.

  3. Try a nudge before the hammer

    A short video on how to reshape a behavior changed how people handle data. Unless people see consequences or feel affected, Clea said, a rule won't register.

  4. Alert on what you'll act on

    If nobody will act on an alert and it adds no value, store the data in a log for when there's an incident. Clea called this the materiality of what you're seeing.

  5. Someone has to own the risk

    Jon's options are to mitigate a risk with controls like DLP, buy insurance, have someone sign off, or hand it to another business owner. Without a business driver, he said, there is no security initiative.

  6. Backup and security need different habits

    Backup is set and forget. Security means constant tuning, alerts and telling people what matters. Clea's most challenging day at Code42 was the start of that shift.

  7. Make new people part of the team

    Hiring someone different is half of it, Clea said. The other half is making them feel included. Jon looks for passion and drive, which you can't get from a tool or a degree.

  8. Take control of your own data

    Clea wants products that help people remove the data spread about them, and an answer to how their data could be weaponized against them. Jon's version is a number for what you might lose.

  9. Ask about their genesis

    Clea's favorite interview question asks how someone got into what they're doing today, and what they did to improve a hard situation.

Chapters

Tap a chapter to play from there.

Pull quotes

“I wanted to be a diplomat, and an actress”

Clea Ostendorf ·

“and then I would find them a match.”

Clea Ostendorf ·

“And it just got me hooked.”

Clea Ostendorf ·

“We are all figuring that out”

Clea Ostendorf ·

“challenge the status quo of what they're doing around data protection.”

Clea Ostendorf ·

“So Code42 is a data protection platform.”

Clea Ostendorf ·

“we're thinking about what are the behaviors that would put data at risk.”

Clea Ostendorf ·

“Here's a 30-second video on how to reshape that behavior.”

Clea Ostendorf ·

“Here's the hammer. I'm telling you no.”

Clea Ostendorf ·

“unless they think there's consequences or it affects them, it's not really going to register.”

Clea Ostendorf ·

“We can see large data uploads.”

Clea Ostendorf ·

“the more information we give you, the more vulnerable we become.”

Clea Ostendorf ·

“I think setting boundaries is important, but more so putting the damn phone down.”

Clea Ostendorf ·

“you can't finish the race in red line.”

Jon McLachlan ·

“anyone who is changing a status quo knows that it is not easy.”

Clea Ostendorf ·

“You're not trusted in my network, but we're still sharing data back and forth, right?”

Clea Ostendorf ·

“Will you actually act on it?”

Clea Ostendorf ·

“who are your external stakeholders outside of security?”

Clea Ostendorf ·

“Somebody just took your roadmap out the door. Does that matter?”

Clea Ostendorf ·

“without a business driver behind security initiatives, there is no security initiative.”

Jon McLachlan ·

“backup is, you set and forget it, and you move on”

Clea Ostendorf ·

“That's the one thing that you can't GPT.”

Jon McLachlan ·

“But you can look for that in the people who are interviewing who maybe aren't your traditional background.”

Clea Ostendorf ·

“what I am scared about is our critical infrastructure.”

Clea Ostendorf ·

“How could my data be weaponized against me?”

Clea Ostendorf ·

“always try and approach things from the other side.”

Clea Ostendorf ·

About the guest

Clea Ostendorf, Field CISO, Code42

Clea Ostendorf is a security leader. Her LinkedIn lists an internship in Brazilian relations at an international law firm in 2009, recruiting and account roles at Signature Consultants and Beacon Hill Staffing Group, and business development at the application security firm nVisium from March 2016. She joined Code42 in July 2019 as a senior insider risk security advisor and became a field CISO in July 2023. She joined Jon McLachlan on episode 47, published June 17, 2024. Her LinkedIn lists her as co-founder and CEO of Wolfpack Security since June 2024, and Mimecast acquired Code42 in July 2024.

About the host

Jon McLachlan is co-founder of YSecurity, the on-demand cybersecurity team for startups, and of Cyberbase.ai. The Security Podcast of Silicon Valley is hosted by Jon McLachlan and Sasha Sinkevich. Jon McLachlan on LinkedIn ↗

Context and sources

  • Episode 47 on Podbean, June 17, 2024, with show notes on Clea's path from aspiring diplomat to field CISO, a collaborative security community, work-life harmony and insider threats. Source ↗
  • Clea Ostendorf's LinkedIn experience: co-founder and CEO of Wolfpack Security from June 2024, Code42 from July 2019 as a senior insider risk security advisor and field CISO from July 2023, nVisium from March 2016, Beacon Hill Staffing Group from October 2014, Signature Consultants from September 2012, and an ISSA chapter's event director from September 2016. Source ↗
  • Clea Ostendorf on LinkedIn, September 22, 2026: 569 vulnerabilities from 105 underlying problems, and asking why the house keeps catching fire. Source ↗
  • Clea Ostendorf on LinkedIn, October 5, 2026: sharing Wolfpack's article Manual Pentesting Isn't Dead. Manual Everything Is. Source ↗
  • Clea Ostendorf on LinkedIn, October 28, 2026: assumed breach exercises belong on every leadership roadmap. Source ↗
  • Wolfpack Security on LinkedIn: boutique offensive security built for the enterprise, with deep, manual testing. Source ↗
  • Wikipedia, Code42: an American cybersecurity software company in insider risk management, maker of CrashPlan from 2007 and Incydr from September 2020, acquired by Mimecast in 2024. Source ↗
  • Wikipedia, Mimecast: a British information security company founded in 2003, which acquired Code42 in July 2024. Source ↗
  • Wikipedia, Insider threat: a threat to an organization from people within it, such as employees, former employees, contractors or business associates. Source ↗
  • Wikipedia, Data loss prevention software: strategies and technologies that prevent the unauthorized transmission or disclosure of sensitive data. Source ↗
  • Wikipedia, Chief information security officer: the senior executive responsible for the program that protects an organization's information. Source ↗
  • Wikipedia, False positives and false negatives: a false positive wrongly indicates that a condition is present. Source ↗
  • Wikipedia, Critical infrastructure: infrastructure considered essential by governments for the functioning of a society and economy. Source ↗
  • Wikipedia, HTTP cookie: a small block of data a web server places on the user's device while they browse. Source ↗
  • Wikipedia, Data broker: a person or company that collects personal data about people. Source ↗
  • Wikipedia, Universal basic income: a proposal in which everyone in a population regularly receives a minimum income without a means test. Source ↗
  • Wikipedia, The Covenant of Water: a 2023 novel by Abraham Verghese about three generations of a family in Kerala. Source ↗
  • Wikipedia, Penetration test: an authorized simulated cyberattack on a computer system. Source ↗
  • Wikipedia, Information Systems Security Association: a not-for-profit organization of information security professionals, founded in 1984. Source ↗

Transcript

Automatic transcription. Jon McLachlan hosts this episode with Clea Ostendorf, field CISO of Code42. There is no diarization on the tape, so speaker labels were assigned from the content and checked against reference recordings of each voice from this episode and by pitch, and a few short lines may sit with the wrong speaker. Names and terms were normalized where the recognizer misheard them (Jon McLachlan, Clea Ostendorf, Code42, CISO, DLP, ChatGPT, GitHub, iWatch, LiveJournal, YSecurity). Words in [brackets] are best guesses where the audio is unclear. Answers are transcribed as spoken, with most repeated words and false starts kept. Short backchannels such as "yeah" and "right" are left out where they overlap the other speaker.

Read the full transcript 8,289 words

Jon McLachlan

Hello, everyone, and welcome to another episode of the Security Podcast in Silicon Valley. I'm here today with a very special guest, Clea Ostendorf. Welcome to the show.

Clea Ostendorf

Thank you.

Jon McLachlan

So good to have you. Where are you calling in from?

Clea Ostendorf

Calling in from Minneapolis, Minnesota.

Jon McLachlan

Oh, I hear the accent.

Clea Ostendorf

Oh, yeah. We'll break it out for the call.

Jon McLachlan

You are the field CISO for Code42.

Clea Ostendorf

I am a field CISO for Code42. A CISO. Yes. I am more externally facing, and then I have a fantastic peer who does more internal customer work, supporting existing programs.

Jon McLachlan

Amazing. And you bring a lot of great experience to the table. I'm looking at your LinkedIn. It looks like you actually came up through the law side of the house, and maybe some international relations in your background. Would you like to share with our audience just a snippet summary of yourself?

Clea Ostendorf

Sure. Once upon a time, I wanted to be a diplomat, and an actress, and then somehow I found myself in security. So my path into security started, yes, doing a little law internship, lived abroad, and then I needed a job to pay the bills. And so somebody gave me an opportunity in sales and recruiting. And I thought it was the best job ever, because I just sat at a desk, and I called people, and I spoke to people, and I heard about what they wanted in a job, and then I would find them a match. But that business became very transactional and less focused on doing what's right for the person and more about margins and dollars, which I found hard to grapple with. And so I started looking for things that were interesting to me and a little different. And I stumbled into security. And I said, "What is security? Oh, it's hackers. Oh, it's... yeah, what is this?" Yes. Cool... cool stuff. And it really felt like the ability to hack into somebody's bank account and just have that power was, like, sort of a superpower. So I started going to all these meetup groups and OWASP groups locally in Minnesota. And then when I would travel, I would seek them out as well. And I realized that that hacker aspect is only one part of it. We don't really talk that much about the... now I know it's called red teaming. We don't talk that much about that side of it. We talk more about the defense and protection and the human element. And it just got me hooked. And 15 years ago... here I am.

Jon McLachlan

Oh, 15 years ago. So once... once you got that hook, there's no turning back.

Clea Ostendorf

I loved it. Yeah. I just... I mean, I thought it was the smartest people I've ever been with, the most clever, creative, and frankly, people I want on my side. I was fully aware that when I started working for a security consulting company, like, you probably have seen everything, and you know what, you're still talking to me. So we're cool. We'll move on.

Jon McLachlan

Nice. And so now at Code42, as a field CISO, what do you do as a field CISO?

Clea Ostendorf

We are all figuring that out, all of us field CISOs. In fact, there is a group that got together, and, frankly, we asked, like, how are you being measured? What are you doing? How are you out in the market? So I think there's different flavors of a field CISO role. My role with Code42 is to work with customers or prospective customers to help them feel comfortable with the product and the way we are securing it and our perspective, and frankly, challenge the status quo of what they're doing around data protection. Because we have a traditional way that we want to approach things, and then we have the reality of what data protection looks like today, and have to bridge that gap. And I think that's where I live today.

Jon McLachlan

Amazing. It's good to live on a bridge, get to see two different worlds. Is that the security group that [Kayne] facilitates?

Clea Ostendorf

Yes, exactly. [Kayne]. So [Kayne] introduced, and that's who was helping. And I loved that discussion, because all of us were like, what do you... so how are you doing this? What are you doing? And to have an audience of very smart people, and a group of all these people who have done amazing things in their careers, and still trying to figure it out together, I love that community aspect.

Jon McLachlan

So at Code42, for our listeners who may be a little bit less familiar, could you help us understand what Code42 does better than anyone else in the world?

Clea Ostendorf

Sure. So Code42 is a data protection platform. We fall into the realm of insider risk or insider threat, as well as DLP, if you kind of want to classify us. And the way we approach things is we have visibility into all data movement across endpoints, cloud, email, et cetera. And then we provide risk indicators and highlight where you should focus your efforts. So rather than saying, hey, I'm classifying this data, and this data is not static like it used to be, we're thinking about what are the behaviors that would put data at risk. So that could be something like a departing employee or new hires, or maybe there's an incident or something happening within your organization, like a reorg or a layoff. I mean, those are realistic use cases, that then we can have visibility around where that data is moving, how people are interacting with it, and do we want to take some action? And then we have a series of responses, some of which are the traditional, you're going to block that behavior, and some of which are much more nuanced, like training. "Hey, you're putting data at risk. You're syncing to iCloud. We don't recommend that. Here's a 30-second video on how to reshape that behavior." And we've seen some really effective changes with reshaping the behavior of how users interact with data, versus, "Here's the hammer. I'm telling you no." It's just a different approach.

Jon McLachlan

It sounds like a long-term strategic investment in people.

Clea Ostendorf

Always. You have to. I mean, you can tell people not to do something, but unless they think there's consequences or it affects them, it's not really going to register.

Jon McLachlan

Do you... can that software detect, "Oh, no, you just uploaded half of the file from our private GitHub repo into ChatGPT-4, ChatGPT-4 Turbo, which just came out this week, and that's not aligned with our policies"?

Clea Ostendorf

Yes, yes. We can see large data uploads. Exactly. Source code is one of the strong use cases that we have, because we know source code is valuable intrinsically and then financially. And we have a lot of visibility and ways to kind of control that movement.

Jon McLachlan

So what's a typical day look like for you at [Code42]?

Clea Ostendorf

Depends if we're in the office or not that day. So we are hybrid workforce, and I go to the office twice a week, which does change how I function, right?

Jon McLachlan

Oh, I'm sure it does.

Clea Ostendorf

Yeah. Getting ready to go to the office is a process. It's not just rolling out of bed. But I like to wake up... I'm a morning person, so I like to wake up really early, have a little me time, that may be doing a little yoga or meditation, or just scrolling through my phone in silence. Then the day kicks off, and the day is either customer or prospect meetings, creating content. I love to do a lot of community events, and those seem to always come across like they're flawless, and no one put any work into it, and everyone just shows up. But if you've ever created an event or hosted an event, there is, like, the image of a duck gliding smoothly across the lake, but underneath, they're paddling like mad. So that's me. Smooth on the surface, and then paddling like mad.

Jon McLachlan

To super hard, committed, like, underneath the hood, and making all of the good stuff happen. Make sure that duck gets across that beautiful pond.

Clea Ostendorf

Yes, exactly. Early in the morning. Fed and happy, and it was worthwhile.

Jon McLachlan

Exactly. I've never met an unhappy duck. They do just float through life. They... don't they? That's awesome. What are some misconceptions about working in security that you think people have?

Clea Ostendorf

Oh, that's a good question. Misconceptions about working in security. That everyone is highly technical, or that everyone... like, traditional security, to me, has always been, we don't want to share what we're doing, and we don't want to collaborate, because the more information we give you, the more vulnerable we become. You can use that information against us. And I think there's been a pretty seismic shift in how both organization to organization, people are sharing information. You're seeing things like trust centers, right? Where you really lay out, this is how we're secure, this is what we're doing, this is our process, to even, like, groups who are saying, "Hey, we got... CISO to CISO, so we got breached, or we're dealing with this. What are you doing?" And people are collaborating, which just makes us all stronger, right?

Jon McLachlan

It does. It does. I love the collaboration. I love the sense of community in the security community. I couldn't imagine being so clammed up and secretive and hidden that you can't even share, like, what's going on, or learn and grow. Like, where's the growth mindset if you're just a lone wolf?

Clea Ostendorf

Right. And I think it would be really isolating too. I mean, you would feel like you're alone battling these threat actors, and you're doing it in a silo. I think that would be really hard.

Jon McLachlan

Yeah, I think that's spot on. So a lot of what happens in security could be perceived as, oh, no, put out the fire, and high stress, high risk, high vulnerability, high impact to the business. It sounds really stressful, especially maybe from the outside. How do you find a healthy balance between your work and your professional life and your personal time and motherhood?

Clea Ostendorf

Yes, I am the mother of two little boys who are super intense, as maybe all children are, just mine. I don't know. Nature versus nurture. I don't know.

Jon McLachlan

Yep. Maybe because they have... they're both brothers for each other. That energy just ricochets right off of...

Clea Ostendorf

I have a brother. I don't know. I mean, it is... they are, they are poco locos. That's what I call them.

Jon McLachlan

Poco loco.

Clea Ostendorf

That's... poco locos. Yep, poco locos. Every day, I'm like, how am I going to burn your energy? Are we jumping? Are we wrestling? Let it go. I think in this job, and I mean, most jobs, if you're passionate about something, it's really easy to get pulled in and want to do something 24/7, whether that is responding to internal requests or trying to just improve. I think setting boundaries is important, but more so putting the damn phone down. And I mean that. I have my iWatch, right? So of course, it's... I'm always getting pinged anyway, but it's really good to use that do not disturb mode, even for a few hours in the evening, or in the morning, or night, whatever. Just shut off as much as you can when you can, so that you're able to recharge. Because otherwise, it's both from a work perspective, you're getting pinged nonstop about issues or things, or people are asking for things, and you have to solve them. You're... human nature, at least for me, human nature, I want to solve it right away. And if you're not able to shut down at some point, you're going to burn out. You're going to just feel like that constant cortisol pumping through your body. And that's not in a state... the state you want to be in. You're going to make mistakes.

Jon McLachlan

Right. You can't run that engine at red line. Like, you can hit it, maybe touch it, and then back off very quickly, but you can't finish the race in red line.

Clea Ostendorf

No. And I think it's both personally, but also with relationships. If you're constantly... if your device and answering whatever machine is the most important thing, and people see that, your relationships, your children, whoever, that's going to affect you outside of just work and just your personal.

Jon McLachlan

Yeah, definitely. So how do you recharge?

Clea Ostendorf

I am a huge fan of movement in whatever form. I mean, I see a medicine ball behind you. So I, I, you... oh, yeah, yeah. Right. So, yep, I have to do something physical. And I just started lifting weights. That's been really fun, because it's incremental, maybe a little yoga, walking, running, I don't care. I just have to move my body to burn off that energy. And once I kind of realize how important that is to my mental health and physical health, I work it in wherever it is. So...

Jon McLachlan

Oh, that's amazing. I am exactly the same way.

Clea Ostendorf

So, what do you [do]?

Jon McLachlan

Exactly. So I'm a runner, a perpetually injured runner, and when I'm so injured that I can't run, I switch to biking. Also, [study]... yes, yes, you have a Peloton. I opted not for the Peloton, because I'm hooked on the Garmin ecosystem, and so I have one of those [unclear] that's connected to an actual pedal bike. And so I just jump on that, and Zwift, I think it's the app that I'm always using. So it's a great way to just sort of flush out all of that tensed-up energy and put it into something that's productive and healthy, and hit that reset button, maybe over a lunch, and just go on with it.

Clea Ostendorf

Yeah. For me, if I... whatever it is, whenever I can fit it in, it's just... you've done one thing for yourself in the day, and then you can... and then I'm able to give in every capacity. But if I just [put] one, like, selfish 30 minutes, an hour... I'm not asking for hours. I wish. I think I would probably get bored if it was more than an hour. But I'm just asking for a little time to reset myself and feel like, and now you can give and do what you do.

Jon McLachlan

Exactly. That's so healthy. Should be very proud of that. I think Minnesotans in general are just very healthy people as well. I don't know. Do you consider yourself Minnesotan, or transplant?

Clea Ostendorf

I don't think I'll ever consider myself Minnesotan. I am from the East Coast. I still have East Coast tendencies. Ask anyone you talk to. They're like, "Oh, no, Clea will tell you how it is." But I love Minnesota, and so I'm happy I'm here.

Jon McLachlan

Okay, excellent. It sounds like you fit very well.

Clea Ostendorf

I have tempered myself.

Jon McLachlan

Being from Minnesota myself, like, you sound... you basically have that Minnesota [twang].

Clea Ostendorf

Oh, thanks.

Jon McLachlan

So when things are going down and stuff ends up in the news, like, what's your favorite news source, or how do you get information? How do you get cued into all of that juicy... [the juicy] happenings in the security world?

Clea Ostendorf

I love podcasts, for two... I mean, podcasts are sort of long-term plays, right? You're listening for an hour, you're understanding somebody's thoughts and perspective on how they would approach things. So it's sort of like a learning experience. For straight news, [Dark Trace] is great. Love the CISO Series. David Spark does a podcast, and one of them is Top Headlines. That's a five-minute fast little snippet, and then you can absorb into it. And then I track everything on Google, any major incidents, and just kind of dig into that if it affects us or customers, and so on.

Jon McLachlan

Nice, nice. Also a huge fan of podcasts. No surprise there. So if you fast forward into the future, could you share with us what your vision looks like for success [at Code42], just for yourself and also your team?

Clea Ostendorf

Yeah, so we have been on a journey. I've been with Code42 about five years, and we've gone on a journey to kind of transform how people are thinking about data protection. So anyone who is changing a status quo knows that it is not easy. It takes longer than anyone expects. There's tons of things that come up and bumps you have to endure. But I think we have reached the point where people are saying, okay, no, I can't just block and tackle my data. That does not stick in our given world. That is not realistic in how people work together, right? Our motto, Code42, is [secure in the] collaboration culture. That is how we work today. I am... even us, we're sharing a Google document back and forth, right? You're not trusted in my network, but we're still sharing data back and forth, right? So you realistically secure that landscape. So we have now convinced most of the market that you need a different way. Now we need to actually show people how it's possible, which we are doing with several, many big customers, but it's a work in progress. I think we all are... every security tool out there is trying to figure out, how do you cut the noise-to-value ratio, right? That the amount of alerts that everyone is getting is just intangible.

Jon McLachlan

Oh, I'm going to die underneath all of these false positives. I mean...

Clea Ostendorf

And seriously, and I go back and forth with people, where people say... those who are using all the tools, we'll say the security engineers or analysts, are like, "No, but I still need to see everything." But if you're not going to act on it, and adds no value, why do you need to see it? Can't you just store it in a log and look back if there's an incident and you need to dig into it?

Jon McLachlan

Exactly. Exactly. Historical.

Clea Ostendorf

Yeah, that's what we're working on. The materiality of what you're seeing. Will you actually act on it?

Jon McLachlan

So what do you find is, like, the main objective for not moving forward into this more progressive space that you're trying... that you and your team are trying to help folks see and understand and connect with?

Clea Ostendorf

I mean, the first thing we're going to say is, who are your external stakeholders outside of security? So what does that mean? That means, have you talked to legal? Are you engaging with HR? Because the only way you're going to get better at and more proactive at protecting your data is if you have indication from the business on what data matters, right? You can't focus on everything, right? Getting proactive around events that would put data at risk. For example, is there going to be a reorg? So what team is going to be affected? Let's have more additional monitoring around there. Initially, there's pushback. "I just want to own this little castle, this little piece. I don't want to involve other people." So that's one back. And then, two, change is hard. "Why do I want to rip and replace something when I think I'm doing well enough with the controls that I have?" And every time we go into a POV, we prove it wrong. "Oh, you have [removable] media blocked? I'm sorry. Somebody just took your roadmap out the door. Does that matter?"

Jon McLachlan

Look, it's in the news.

Clea Ostendorf

Oh, look, it's in the news. "Oh, my gosh, look, they just started a company with that data that they took."

Jon McLachlan

Oh, no. Was that an issue? Oh, did that matter?

Clea Ostendorf

"Do you want to do something about that?" And now you're in a legal battle, and...

Jon McLachlan

Oh, what a mess. Yeah. I guess one of the ways to look at risk is to either, like, actively mitigate it, with controls and with mechanisms like DLP and other systems and processes to mitigate that. Or if the business does not want to mitigate the risk, you buy... you cover it some other way. You buy insurance, you get someone else to sign off on it, or another business owner to own it.

Clea Ostendorf

Yeah. I'm working with... how can I not make them guilty and clear who they are? Working with a large organization with lots of customers, where they share data back and forth. And they've had multiple insider incidents where a managing consultant has taken project plans and customer information, and they've had to pay pretty big fines, almost lost a customer, and they still have not invested in Code42 or any, really, product, and it doesn't have to just be us, because they don't want to upset the culture and seem like there's too much monitoring as to what the consultants are doing. So you're [losing] data, you're losing money, but you're going to take that business risk. And that's... there's only so much.

Jon McLachlan

Right. There's only so much you can do it if a founder or a CEO or leader of any kind has their heart set on swallowing risk, and they understand what that risk means and the costs associated with it. There's always going to be a cost associated with it. The idea is that not only is doing the right thing and protecting your data cheaper for your business, it's also cheaper compared to the things that might happen if you don't do those things, right? And I've noticed, without a business driver behind security initiatives, there is no security initiative. It's just, yeah, we want to do all these things, and we can recommend that folks focus on all of these things, but unless a business leader has seen and felt with... felt the problem and felt the pain point, and has decided to protect, in this case, data or processes or IP or whatever it is, it's really [going to be] quite challenging.

Clea Ostendorf

And who's [down] the line? It's the security team. I mean, it's an increased level of stress, where you're not getting support from the business. You know it's a problem. And if something goes wrong, it's your fault when you're not... It's hard. It's a hard problem.

Jon McLachlan

You don't have the tools to solve it. Yeah. Yeah. It could be a very challenging position to be in. And speaking of challenging and challenges, what's the most challenging day that you've had so far at Code42?

Clea Ostendorf

Most challenging day at Code42. I would say when I started, it was the most challenging. And that's not just because it was a new job. It was really shifting a mindset of an organization who has been very successful in what they were doing. We came from backup, [people] loved Code42 for backup, and trying to shift into security. And it's a very different mindset and a way to approach working with a product, right? Like, backup is, you set and forget it, and you move on, you don't want to touch it again. Whereas security, you constantly have to be tuning and looking into things and setting up alerts and removing things and communicating about what matters, because it's not straightforward. So that was challenging. It was winning over the hearts and minds of a very smart engineering team, a very smart sales team. A bunch of people are saying, like, "What do you know about this?" Right? It was an [overhaul]. What the hell am I doing? And then COVID hit, and we all went home, and that had its own challenges.

Jon McLachlan

Yeah, yeah. I could imagine. I could only imagine. It sounds like Code42 is really lucky to have you, and to help... have you help them navigate all of that complex space, and that shift from backups.

Clea Ostendorf

But we already did it. There are other people involved. So acknowledging that...

Jon McLachlan

I'm sure it was a team effort.

Clea Ostendorf

[unclear], but it was a journey with a really smart team.

Jon McLachlan

And good leadership. Wink, wink, nudge, nudge.

Clea Ostendorf

Good leadership is really important. People who listen and will fight your battles.

Jon McLachlan

Yeah, fight with you towards doing the right thing. It's always... it's always interesting, like, finding that internal alignment. A lot of people get very political inside different companies, especially, like, larger companies. There's a lot of bureaucracy sometimes about processes. I always find that a revisiting of the basics, reminding everyone that we're all on the same boat together, pointing out that we're actually all on the same team, is a really nice way to just [unclear] the [seas] and bring people back to the table. And we can take off our personal hats, or our little fiefdom or whatever that we've got building, and put on the company hat, and think about what's right for the company, what's right for the customer, together.

Clea Ostendorf

Yeah. Oh, remove the ego. I mean, I would echo that with your statement.

Jon McLachlan

Oh, yeah, definitely. Yeah, check egos at the door. Yeah, I imagine it's especially difficult in a male-dominated field, being a woman, too.

Clea Ostendorf

I mean, it certainly is another dynamic. I call myself the diversity hire sometimes.

Jon McLachlan

The diversity hire.

Clea Ostendorf

Mostly, I was at a panel, and they're like, "Oh, we're so happy that we have a female on this panel." And I'm like, I guess I'm glad I qualified that way.

Jon McLachlan

You know what? I think diversity matters so much and is so important. It's so overlooked sometimes on teams. And it's the differences that we all bring to the table that makes teams stronger than the sum of their individual [parts]. And that's why, like, diversity is so important, and it matters so much. And if you just get a giant echo chamber filled with copies of different organisms inside that same echo chamber, you're going to miss, like, really critical gaps. And the only way that you get that diversity on a team is you hire different types of people, or you don't. I know that when we hire folks, we look for very specific qualities and traits and experiences, but I also feel like complementing the skills of the team and complementing the experiences that those teams bring to the table is just as important.

Clea Ostendorf

Yeah, I mean, I agree 100%. I think there's two factors... I mean, many factors, but these two things stand out to me when we talk about this. First is, if you're bringing somebody who is so different into your team, how are you going to make them feel like they are part of the team? And I think that's something that's overlooked, right? Are you going to include them in the same way? Are they going to be comfortable? I've worked in male-dominated industries my whole life. There are things that guys like to do that I'm not interested in. And so how are you going to kind of compensate that difference to make this all...? I want to go get my... I want to go get a pedicure. I don't want to go to a baseball game.

Jon McLachlan

I'll go with you to go get a pedicure. Everyone loves a pedicure. There we go. [Mani-pedis] after work. Here we go.

Clea Ostendorf

Everyone loves a pedicure. There's that aspect. And then there's... we... and maybe I can toss this back to you. We talk about wanting to hire diversity. When do you hire diversity, or when do you hire somebody with a different point of view, versus when you really need to just ramp up the team, right? Because there's a constant benefit to both. Like, we can ramp... I've talked to our recruiters, and I asked her this question. She's like, [unclear] manager, do we need to just have a developer who can hit the ground running and scale our product, or do we... can we hire somebody we can train and help shape the direction in a different way? So what do you do?

Jon McLachlan

What do you do? You do both. Do both. I don't know. Maybe that's a cop-out answer. But I used to... I've interviewed so many people in my lifetime, and I used to be very specific in the things that I look for. And you have to be. You have to be making sure that they're going to be a good fit in terms of the skills that they bring to the table, and that they'll be able to be successful, and maybe not 100% in their comfort zone. If they're learning and growing, that's actually a good thing. I see that as a good thing. And the thing that I look for now in interviews is the passion, it's the drive. That's the one thing that you can't GPT. You can't read it in Wiki. You can't learn it. You can't go to school for that. You can't get a degree. If you have the drive and that fire, you can accomplish anything. And when you believe in people, and as a leader, I think, like, people can feel that, if you show them that you're going to be... that you'll take a risk with them, for them to take that next step for themselves, and you got their back, and you make them feel like they're part of the team 100%. And maybe that means going to get [manis and pedis] after work, or maybe that means doing a long run on the weekend together, or maybe that means... I don't even know what that means. It's different for different cultures, and it's different for different people, but it's different. And you have to listen to what matters to people in order to figure that stuff out. And that's why being a leader is both, like, super challenging, but also, like, very rewarding, I find, because it's about connecting with people and moving through uncomfortable spaces. Because I don't know anyone that you could just get to a point in your career and stop learning. Stuff in technology is constantly changing. You have to change with it. You have to learn. You have to grow. You have to move with it. Otherwise, it slowly becomes a little bit... a little bit, like, inch by inch, like, less relevant. So I don't know. I don't know about you, but that's kind of why I optimized for it. And at some point, I had an epiphany that I thought at the end of the day, like, the tech was what mattered 100%. And I really dropped that for... actually, people matter at the end of the day. And people that can see other people, or people that bring something that complements the team to the table, should definitely optimize for that. And trust people to be able to learn, like, the technologies. And if you have an emergency, a tactical need, I don't know, maybe don't hire someone. Maybe just get a contractor to fill that tactical gap. Maybe. I don't know. Like, just thinking out loud here. But every situation is different, and I could see cases being made for both sides. I don't know. What's your thoughts on all that?

Clea Ostendorf

I mean, I totally agree. There's something called... there's sort of, like, a TikTok trend going on right now called the personality hire, where you don't hire necessarily on the skill that somebody is bringing to the organization. You hire more on the way that they're going to complement the team and energize people and build culture and excitement around the company. And I think that's a hard thing to say as a hiring manager: "Hey, this is what I want to hire. Recruiter, go find me somebody charismatic and fun who's going to make everyone want to work harder." But you can look for that in the people who are interviewing who maybe aren't your traditional background.

Jon McLachlan

Yeah, for sure. I mean, you can't put that in the job description, right?

Clea Ostendorf

Yeah, it would be a hard [time].

Jon McLachlan

That's a soft skill. Those are all soft skills. Yeah. I mean, I guess when you... when a recruiter or someone will put, oh, good cultural fit, that's maybe what they're talking about. Yeah, yeah, maybe. But, you know, it's important to bring skills to the table as well, so you can contribute in a meaningful way towards, like, the mission of the company and help drive the business to be successful. And a business, really, what is a business? A business is an entity that exists to make money. It's so simple. It exists to make money. And you join it. A company is just an idea, right? It's just a group of people getting together to accomplish a mission, to solve a pain point, to make people's lives better. Usually those people are called customers. Hopefully, they're called customers. You have a good business, you have people that are paying you money, and you show up and you solve their problems, and everyone goes home happy, because everyone contributing to that mission feels better about being able to make people's lives better. And the people are actually paying you money to help make their life better. Like, you are making a real impact in the world. This makes me happy, because I want to live in a better world. So this is... all of these are good things. But in security, we deal with such hot-button topics. Can you... do you... would you like to discuss any current or potential future cybersecurity threats that are, like, top of mind with you?

Clea Ostendorf

Okay, we'll go really broad, and then we'll go in a funnel. Okay, what I am scared about is our critical infrastructure. And I don't know enough about securing it. I know there's plenty of vulnerabilities. I [worked] for a pen testing company who did a bunch of pen tests on water treatment facilities, and it's like, where do you want us to begin, right, to help you fix this? But I think we are really vulnerable. And I don't think... first of all, I don't think many Americans are able to manage hardship, right? Look at how we all endured during COVID, right? There... there was not... it's... it doesn't... crisis does not bring out the best in many people. And so when these things that we are so used to being around, we'll say electricity, internet, water, are gone, what is society going to turn into, and how quickly are we going to devolve? So that's my I'm-scared moment. Top of the funnel. That's top of the funnel. I bought a five-gallon freeze-dried thing from Amazon this weekend, just in case. Just in case. I mean, what is a five-gallon freeze-dried food going to do? I don't really know, but it helps me feel a little more prepared. The more realistic thing that I think we're all dealing with is our personal data privacy versus the security, right? Like, we have given out all of our information across the internet, because now we can choose if cookies are tracking us. Two years ago, we didn't choose, and our data is still funneling and being collected and manipulated. And so how do you reconcile that? And how do you start to take control over what information, personal information about you, is out there? And I'm starting to see more products targeted for the actual user, like general population, versus consumers, us consumers. Yes, I'm starting to see that. And I like that, because it, to me, gives a little more sense of control. It's not going to fix everything, but at least you can clean up the data spread that's out there about your personal information.

Jon McLachlan

Yeah, I will love that. I look forward to living in a future that has better privacy, now, for all of us.

Clea Ostendorf

Yeah.

Jon McLachlan

What do you think the role of cyber espionage is going to evolve into over the coming years? Oh, or its impact on international relations?

Clea Ostendorf

I don't know. We... I mean, I assume everybody has access to everything already. All of the nation states who want to see what we're doing. What would be interesting is how it's weaponized, right? There's a 23andMe attack, or data breach, and what they looked... what they went for was Asian Americans. They went... wanted all the data on Asian Americans and Ashkenazi Jews. So that was the demographic of the data that they took. They took everything, but they specifically called out that they were really targeting those two groups. And to me, why? How is that going to be weaponized? Are we going to... we can go down a spiral, right? Are you going to create, like, some super bug that only affects these groups who have this type of gene set, right? Or what are you going to do with that? So that, to me, is interesting. You know, we are going to get more complex on how this data is used outside of just general money laundering, and...

Jon McLachlan

That's nasty. Given the history... history, the human history that we all share and have in common. The history unlearned is a history repeated, for sure. And people think, oh, modern world is not so bad. I mean, I don't know. If you look around to see what Putin is doing with Ukraine, look to see what's happening in Belarus. Belarus is in Europe. I don't know if people understand that. There's a tyrant dictator over there who rigs elections very openly. Yeah, people [disappear] all the time.

Clea Ostendorf

And the amount of proxy wars that are going on. I mean, I have this debate with friends all the time. Are we... is the world a worse place, or are we just more aware of it? I think generally humans want to do good. And do we... and does the news only report on the bad? I mean, it's hard. I have to tune it out, because it doesn't...

Jon McLachlan

Yeah, the news is unfortunately a business. It's designed to make money. And it does that through the same mechanisms that TikTok and Twitter and anything else is trying to grab our attention... modern days. I could... [unclear] to have a little bit more credibility. And oftentimes it does, but oftentimes we have to remind ourselves that it is also a business. One of the best 99 cents I've ever spent in my life was a little app called the Hourly News. And all it does is, you open it up... this is my morning routine. You open it up, it'll play short news clippings of everything that has happened, like just the headlines in the news, the top, like, world headlines, and it'll go through NPR, Fox News, CBC in Canada, [Deutsche Welle] in Germany, Hong Kong News in Hong Kong. And you hear, like, from all of these different perspectives what's happening in the world. And you know what? Like, when a big event happens in the world, they all report on it. And I hear such different content. And it's not that anyone is lying. None of these news stations lie or deceive. It's just sometimes you don't hear all those... you don't hear everything that happens. And depending on what is reported, you can hear the slant, you can hear, like, the bias in all of these different styles, I would say, of how it's delivered. And then you realize, wow, it's being curated. And so it's just fascinating to hear the different perspectives through what's being reported, what's not being reported, as much as it is what is being reported, how it's being reported.

Clea Ostendorf

You need some analytical insight. You need to use your brain when you're consuming information.

Jon McLachlan

[unclear]

Clea Ostendorf

Logic.

Jon McLachlan

Let's do our own thinking every once in a while. It's healthy. So, hey, do you have a favorite interview question?

Clea Ostendorf

Like a job interview question? A job... job interview question?

Jon McLachlan

Or I guess it's open-ended, so you could...

Clea Ostendorf

I'm going to say job interview question. And I love to ask people their genesis. Like, how did you get into what you're doing today? Because I think you can learn a lot about somebody's just general approach to life. You had a really hard job. You didn't like it. So what did you do to improve your situation? I am all about not staying static, right? Always moving, literally and physically. I mean, literally...

Jon McLachlan

No, that's good. I like it.

Clea Ostendorf

Mental sense. But, you know, where were you then? And how did you get to where you were? And what sacrifices or what paths did you take? Because I think you can understand how somebody is motivated and what they're going to do to learn or improve their situation or fit into your general team if you're hiring.

Jon McLachlan

Yeah, definitely. No, that's awesome. I love that. It's just double-clicking on life experiences, getting to know the person, really. Would you say that there was a book or a movie that you watched or read that really changed the way that you see the world, that you would like to share with the audience?

Clea Ostendorf

I am a voracious reader.

Jon McLachlan

For everyone who hasn't seen, there are many books behind Clea.

Clea Ostendorf

I love to read. I either read or I listen to the books. So I can't say that I have one, but I like to listen to books or read that tell a story that we all maybe know from a different perspective. So I just finished Covenant of Water, which is about, I don't know, a foot big.

Jon McLachlan

Wow.

Clea Ostendorf

It's a huge book. It's a huge book. So it's an undertaking, but well worth it. And it tells, in one part of it, tells the story of World War II through what was happening in India. And that's just a perspective that you would never traditionally get from the Western history books that we see. And it just shapes another aspect of humanity that we don't traditionally get to experience.

Jon McLachlan

I love it. So you're looking for those different perspectives.

Clea Ostendorf

Yeah, absolutely.

Jon McLachlan

Amazing. It's exactly what I look for in the news.

Clea Ostendorf

[Chance] to see it from all different sides to make your own conclusion.

Jon McLachlan

If you had an opportunity to meet your younger self, would you... and would you have any advice for your younger self?

Clea Ostendorf

Yeah, lots of advice. When I was younger, I spread myself very thin. And I think maybe that benefited me, because I had lots of experiences. But I think as I have gotten older, and time is more valuable than it used to be, when it seemed like you had endless time and endless energy...

Jon McLachlan

And no money.

Clea Ostendorf

And no money, right?

Jon McLachlan

No money. You had all the time in the world and absolutely no money.

Clea Ostendorf

Didn't matter, right? 'Cause you'll figure it out. And you don't really need to eat three meals a day, and vegetables are optional, because, again, you're, like, functioning as your optimal self at 20. I didn't focus on investing in relationships. I was, like, happy floating around and sort of being superficial. And to me, I don't have time for that anymore. I really value one-on-one conversation and understanding how somebody ticks and getting to know them. And that's where I would say, younger self, think about that. And also, don't drink so much, 'cause it's not good for you.

Jon McLachlan

Yeah, it's hard on the body, alcohol. But it's amazing to build friendships and deep, meaningful connections with other human beings. Full disclosure, I was the same way. It was not something that I invested in my earlier years. And then at one point, it just clicked. And I was like, you know what? At the end of the day, like, this is all... this tech stuff is great, but people are what matter.

Clea Ostendorf

Definitely.

Jon McLachlan

Absolutely. So, we have a lot of entrepreneurs that listen to the show. And so this is a little bit of a leading question, but could you imagine one tool or service that it doesn't exist in the world today, and you just wish that someone would notice these pain points and solve it for you? Anything come to mind in that space?

Clea Ostendorf

Privacy. Figure out a way to do that. Personal privacy. It's... that's my hot button right now, because I just feel very exposed on the internet.

Jon McLachlan

What's amazing is what is about to happen, what is already happening. It's like all that stuff that we've been uploading to the internet for the past, like, 15, 20, 30 years, whatever, how long the internet has been around, is now going to receive, like, all of this swoop from AI.

Clea Ostendorf

Yeah.

Jon McLachlan

And even if you didn't tag yourself in a photo, people are going to know that was you.

Clea Ostendorf

Yeah. I'm, like, terrified, right?

Jon McLachlan

Yes.

Clea Ostendorf

I was an early adopter of Facebook, right? I put my life out there. LiveJournal, like, I had that. I don't... I mean, I want it all [back]... what I want. Someone invent that.

Jon McLachlan

Please wipe it all. There we go. A giant red button. How much would you pay to wipe your history on the internet?

Clea Ostendorf

I need to know what's first.

Jon McLachlan

You need... okay, all right, all right. So there's a little line items, like early Facebook photos, like [LiveJournals]...

Clea Ostendorf

[Blackmail me with.] And then I'll let you know how much [that gets] blackmailed for.

Jon McLachlan

There's an interesting service. Analyze my exposure to risk on the internet. Give me a number for how much I might lose [if] this gets into the wrong hands.

Clea Ostendorf

Yes. How could my data be weaponized against me? I want...

Jon McLachlan

That's an interesting question.

Clea Ostendorf

...to take ownership of what they've put out there.

Jon McLachlan

Yeah, when we were building Peacemaker, there was a... it was all B2B stuff. But at the very last minute, there was an attempt to think through what could be a B2C product and go after that problem in particular. And we got very excited about a lot of stuff. But you know what? It's hard to find that adoption for things like that. People... I feel like there's a lot of people that just have accepted that they are not private, or maybe that they believe, I don't know, they're not important enough to matter. Like, for those ending up disappeared or something like that, if you visit the wrong country, or you come from the wrong place, and you have the wrong... different set of ideas. But I think it's much more than that. I think that these companies are positioning themselves to monetize our data. And when you don't pay for a product, you are the product. You are the product. And you're being monetized. Our behaviors change, even though we don't like to admit that. Like advertising, we see it because it works, sort of thing.

Clea Ostendorf

Absolutely. One of the best ideas somebody had in regards to just the general data that's out there is that companies who use our general data, our browsing history or what we're clicking on or whatever they're collecting, you can opt in, that they'll collect that information and they'll pay you a universal basic income, right? That's how you set up. Hey, I am a product. I will click. I will do my thing. And you can use this data. Or you opt out of that, and they can't touch anything you engage with. And...

Jon McLachlan

Yeah, I love that.

Clea Ostendorf

Right? For most people, to be like, I don't care, I'm going to do it anyway. Send me a Google ad. It helps me. And then they can get paid for that, and then you can elevate the standard of living. And these companies can still make all their money, because they're advertising the right way, or to the right people.

Jon McLachlan

Yeah, there you go. And you share a profile of yourself with you and what matters, and the history of all your button clicking and all that stuff.

Clea Ostendorf

Yep. So, Jon, maybe you should invent that one.

Jon McLachlan

Oh, my goodness. If I have the spare time, like, I'll squeeze that in. I don't know. Maybe you've got the entrepreneurial spirit yourself.

Clea Ostendorf

Perhaps. Maybe that'll... that's phase two of my...

Jon McLachlan

We could team up and be co-founders, maybe.

Clea Ostendorf

You guys heard it here first.

Jon McLachlan

All right, there we go. Would you like to leave our listeners for any... with any pearls of wisdom?

Clea Ostendorf

Pearls of wisdom. Always... always try and approach things from the other side. See both sides.

Jon McLachlan

See both sides. I love it. Amazing. So enriching to step outside of our comfort zone and be a little... and just appreciate that the world is colored through these lenses that we're looking through it. We can try on different lenses. Whoa, surprise! Mind blown. Spectacular. This has been an amazing discussion. Thank you so much, Clea. It's been an awesome chat.

Clea Ostendorf

Yeah, likewise. Thank you for having me, and thank you for the opportunity. It was really fun. I think there's been a lot of laughing, which is always a good way to have your day start.

Jon McLachlan

That's... yeah, that's a good sign. And thank you to all our listeners for tuning in for another episode of The Security Podcast of Silicon Valley, a YSecurity production. I'm your host, Jon McLachlan. And stay tuned for more episodes in the future. Thank you, everyone. Thank you. Thank you.

FAQ

Questions this episode answers

Who is Clea Ostendorf?
Clea Ostendorf was a field CISO at Code42 when she joined Jon McLachlan on episode 47, published June 17, 2024. Her LinkedIn lists her at Code42 from July 2019, and as co-founder and CEO of Wolfpack Security since June 2024.
What does a field CISO do?
On the episode, Clea said field CISOs are still figuring that out. Her job was to work with customers and prospects, help them feel comfortable with the product and its point of view, and challenge the status quo in data protection. A peer did the internal customer work.
What does Code42 do?
Clea called Code42 a data protection platform in insider risk, insider threat and data loss prevention. It sees data move across endpoints, cloud and email, and flags behaviors that put data at risk. Wikipedia describes its Incydr product as a SaaS data protection tool for enterprises, launched in September 2020.
What is an insider threat?
An insider threat comes from people within an organization, such as employees, former employees, contractors or business associates, according to Wikipedia. Clea's examples of risky moments were a departing employee, new hires, a reorg or a layoff.
Can data protection tools see source code uploaded to ChatGPT?
Clea said Code42 can see large data uploads, and that source code is one of its strong use cases, because it has value in itself and in dollars.
What is the noise-to-value ratio in security?
Clea used it for how many alerts are worth acting on. Her advice: if nobody will act on an alert and it adds no value, store the data in a log and look back if there's an incident.
Why don't companies invest in insider risk tools?
Clea named pushback from teams that want to own their own piece, and that change is hard. Her example was a company with multiple insider incidents and big fines that still didn't invest, so as not to upset its culture.
What happened to Code42?
In July 2024, Mimecast acquired Code42, according to Wikipedia. Mimecast is a British information security company founded in 2003, specialized in email security and risk management.
What is Wolfpack Security?
Wolfpack Security describes itself on LinkedIn as boutique offensive security built for the enterprise, with deep, manual testing. Clea's LinkedIn lists her as its co-founder and CEO since June 2024.
What book did Clea Ostendorf recommend?
The Covenant of Water, a 2023 novel by Abraham Verghese. She said one part tells the story of World War II through what was happening in India.
Keep reading on the YSecurity blog
New episodes every other Tuesday

Got a story like this one?

We're always looking for practitioners who've been in the room when it mattered.