
Podcast Episode 84

Episode 084 35 min

What gets missed when nobody reviews the code

with Jack Cable · Corridor

0:00 / 35:00

Watch on YouTube Listen on Spotify, Apple Podcasts, Podbean, Player FM

Episode 84 of The Security Podcast of Silicon Valley, published December 16, 2025. Host Jon McLachlan, co-founder of YSecurity, talks with Jack Cable, co-founder and chief executive of Corridor, the AI security company he started in January 2025 with Ashwin Ramaswami. Jack, who found his first vulnerability at 15, won Hack the Air Force in high school and led on Secure by Design at CISA, explains why the vulnerabilities attackers exploit are mostly ones the industry has known how to prevent for decades, why scanners built on pre-canned templates miss what a researcher reading the code would find, why the hard problem is knowing which findings to fix, why defenders should get AI tools first, and why most code will soon be written by AI. The deep dive adds what Corridor did next: a $25 million Series A, testimony to Congress, a security model for coding agents, and its acquisition by Cognition in October 2026.

Episode notes

Code ships faster than anyone can review it. Jack Cable, CEO and Co-Founder of Corridor, explains what actually gets missed when teams stop reviewing every pull request, why most security tools surface noise instead of risk, and how Corridor approaches secure-by-design when speed is non-negotiable.

Hosted by Jon McLachlan — co-founder of YSecurity.

The deep dive

Fully preventable for decades

Jack Cable found his first vulnerability at 15 by typing negative one dollar into a payment API. He won Hack the Air Force in high school, scanned election infrastructure in all 50 states from inside CISA, led its Secure by Design pledge, and in January 2025 started Corridor on one idea: the bugs attackers use are the ones we have known how to prevent for decades. Here is the conversation with the public record beside it, what Corridor built before it joined Cognition in October 2026, and four tools for the code your own team ships.

The fix had been sitting there for twenty-one years when Jack Cable and I recorded this.

“If you take SQL injections, where we’ve had parametrized queries in MySQL since 2004, so 21 years now, and yet we still see these SQL injections coming up, despite having been fully preventable for decades.”

Jack Cable, at 23:59

Listen · Jack on episode 84, from 24:53
About 17 seconds: a fix from 2004, and the bug that still ships. The clip stops on its own. Read the full transcript.

Jack Cable is the co-founder and chief executive of Corridor, and since October 2026 the head of security products at Cognition, which bought it. He found his first vulnerability at 15, won the Air Force’s bug bounty challenge in high school, spent the summer after it at the Pentagon’s Defense Digital Service, helped scan the election infrastructure of all 50 states from inside CISA in 2020, worked on open source security legislation as a Senate fellow, and spent two years at CISA leading on Secure by Design, including a pledge that more than 250 software makers signed. He started Corridor in January 2025 with Ashwin Ramaswami, his partner on the election work, on one idea: the vulnerabilities attackers exploit are mostly the ones the industry has known how to prevent for decades, and AI can finally help prevent them where the code gets written. We recorded in 2025, after Corridor’s seed round, and published the episode on December 16, 2025, with 45 words of show notes. This page is the rest of it: the negative dollar, Hack the Air Force, a startup inside government, the pledge, the bugs that keep getting exploited, why SQL injection is still with us, scanners that don’t know your code, the pull requests nobody can review, the co-founder you already trust, a first round in March and a seed in April, knowing which bugs to fix, proving it, why defenders should get the tools, software that isn’t written by humans, the summer Jack picked the Pentagon, falling in love with a problem, and what Corridor did in the year after the episode came out. There are four things to try along the way: a quiz, a scorecard for whether the old bug classes are gone from your code, a calculator for how much of your scanner’s output is noise, and a timeline you can filter.

Negative one dollar

I asked whether all of this made him a hacker, and Jack told me how he became one, by accident.

“And as a curious kid, I entered zero into the transaction amount and noticed that the payment went through, and I thought, huh, that’s a little weird. And then I entered negative $1. And to my surprise, that also went through and actually took a dollar from that account.”

Jack Cable, at 3:17

Listen · Jack on episode 84, from 3:22
About 38 seconds: an API integration at 15, a zero, a negative dollar, and an easy decision. The clip stops on its own. Read the full transcript.

He was 15 and building an integration with the API of “a cryptocurrency website, of all things.” Two years later he told Defense One which one it was, a Bitcoin tipping service called ChangeTip that has since shut down, and that the same flaw let him send negative amounts to other users, which moved their money into his account (Defense One). My follow-up was the one everybody asks, whether the real decision was how many zeros to add to the next one, and Jack’s answer was that there wasn’t one: “Yeah, exactly. I didn’t even really consider the alternative.” The company had a bug bounty. They paid him, he thinks, $1,000, “which at the time, as a 15-year-old, was a lot, still is a lot of money.”

He also credits the timing. “I got into security at a time where really vulnerability disclosure, bug bounties were much more the norm,” he said, and his record shows how much he made of it. From November 2015 to December 2020 he hunted on HackerOne, where he reported more than 350 valid vulnerabilities to organizations including Google, Yahoo, Facebook, Uber, Salesforce and the Department of Defense, and ranked in the top 100 on both HackerOne and Cobalt. From 2018 he was also on the Synack Red Team (LinkedIn).

The habit he describes from those years runs through everything else on this page, from bug bounties to the policy work. “It comes down to trying lots of different approaches, seeing what works. Many don’t. But often there is a way to have an outsized impact, whether that’s with a vulnerability, whether that’s through the Secure by Design work, for instance.”

Hack the Air Force, then the Pentagon

Jack’s own short version came at the top of the episode: “I got into government work originally through the Hack the Pentagon bug bounties. So when I was in high school, I won the Hack the Air Force competition and then went to work for the Pentagon after high school.”

The long version is in the Air Force’s numbers. Hack the Air Force ran from May 30 to June 23, 2017. More than 270 vetted researchers took part, they found 207 valid vulnerabilities and earned more than $130,000, and the Air Force singled out one participant, a 17-year-old who submitted 30 valid reports and earned the largest bounty total of the challenge (U.S. Air Force). That was Jack. Defense One counted more than 30 of the 207 as his, and reported that the run lifted him to fifth in HackerOne’s third-quarter rankings (Defense One). In September he posted the souvenir.

Three federal bug bounties, and the coin from the third. View on X.

The Pentagon part came the next summer. From June to September 2018 he worked full time at the Defense Digital Service, the Pentagon’s in-house team of engineers, and advised it until 2022, helping lead the Hack the Marine Corps bug bounty and advising the Hack the Pentagon program (LinkedIn). That December, TIME put him on its list of the 25 most influential teens of 2018, at 18 (TIME). By then he was at Stanford. In January of his first year he helped the university’s information security office launch a bug bounty for students and staff, which Stanford said put it among very few universities with one (Stanford University IT), and from 2019 he was a research assistant at the Stanford Internet Observatory and head teaching assistant for its Hack Lab course (LinkedIn). He finished a bachelor’s in computer science there (TechCongress). How he chose the Pentagon over a Silicon Valley internship that first summer is near the end of the episode, in the advice to his younger self.
Jack on NahamSec's Live Recon, published in February 2022, about an hour: how he got started, his bug bounty method, and how to hack the US government legally. Watch on YouTube.
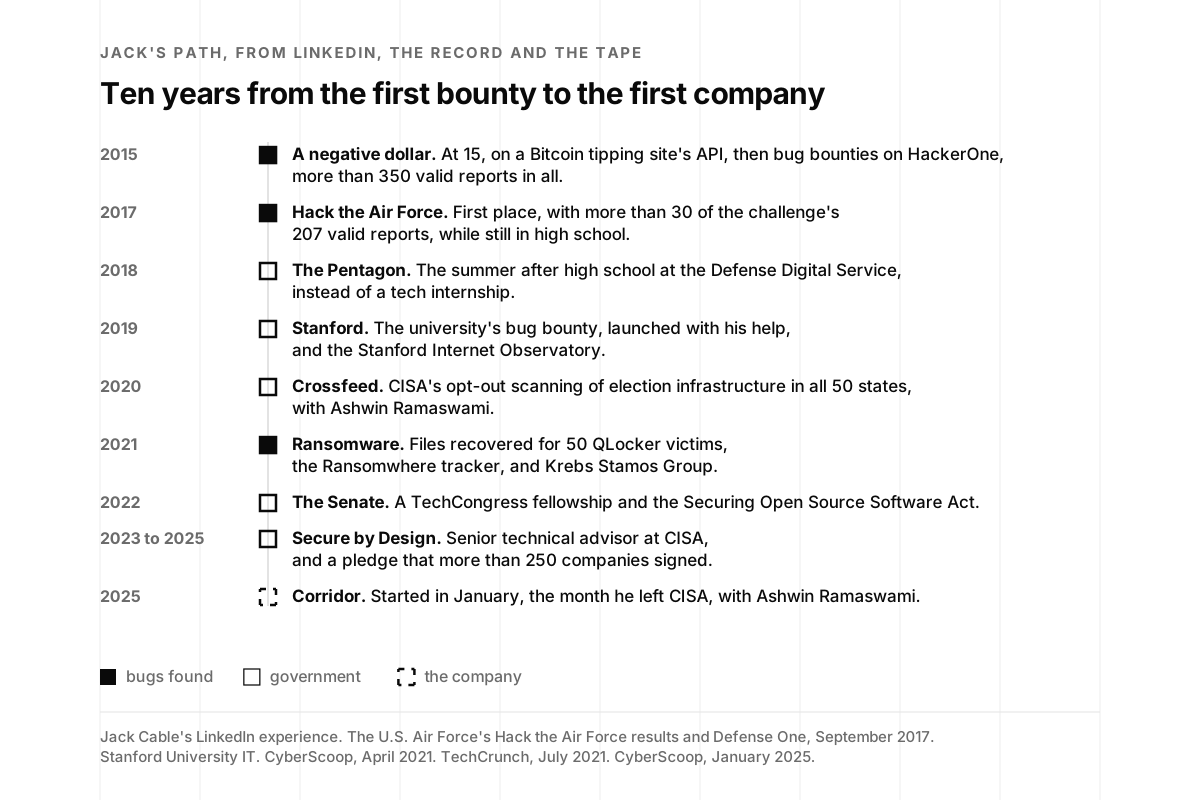
A timeline of nine entries. 2015, at 15, a negative dollar on a Bitcoin tipping site, then bug bounties on HackerOne. 2017, first at Hack the Air Force, more than 30 of its 207 valid reports. 2018, the Defense Digital Service at the Pentagon. 2019, Stanford's bug bounty and the Stanford Internet Observatory. 2020, CISA's election scanning with Crossfeed, all 50 states. 2021, Krebs Stamos Group and Ransomwhere. 2022, a Senate fellowship and the Securing Open Source Software Act. 2023 to 2025, CISA's Secure by Design work and pledge. 2025, Corridor.
Ten years from the first bounty to the first company. Sources: LinkedIn, the U.S. Air Force, Defense One, CyberScoop, TechCrunch.

A startup inside government

When I asked about his co-founder, Jack went back to 2020.

“We built our own open source attack surface management tool called Crossfeed, and we used that to secure election infrastructure. So we rolled that out to scan all 50 states, every county in the US, to look for vulnerabilities in their internet-facing sites.”

Jack Cable, at 10:21

His LinkedIn has the count. As an election security technical advisor at CISA from June 2020 to January 2021, he led the agency’s first passive, opt-out vulnerability scanning program, built on Crossfeed, which assessed all 50 states and over 2,500 counties before the 2020 election (LinkedIn). Crossfeed’s code is public, a joint project of CISA and the Defense Digital Service that continuously maps an organization’s internet-facing attack surface (GitHub). Through it, he said, they “reported hundreds of [high and] critical vulnerabilities to states,” and the part he remembers best is what it felt like to build: “we had essentially almost built a startup within government.”

Between government jobs he kept finding ways to hand defenders an edge. In April 2021, while still at Stanford, he noticed that the operators of the QLocker ransomware checked payments so loosely that changing one letter of a transaction ID from lowercase to uppercase unlocked a victim’s files, and he used it to recover data for 50 victims, about $27,000 in ransom they didn’t have to pay, before the gang fixed it (CyberScoop). The Secretary of Homeland Security noticed.

Quoting Jack's thread on the ransomware payments he diverted. The account is now archived. View on X.

That July he launched Ransomwhere, a crowdsourced tracker of ransom payments, which had counted more than $32 million in 2021 payments by launch day (TechCrunch). From May 2021 to February 2022 he was a security architect at Krebs Stamos Group, the consultancy Chris Krebs and Alex Stamos founded that year, leading purple team engagements and incident response (LinkedIn, The Record). Stamos comes back into this story twice.

Secure by Design, and a pledge

In 2022 Jack spent most of a year in the Senate as a TechCongress fellow for the Homeland Security and Governmental Affairs Committee under its chairman, Gary Peters, working on open source and election security, including the bipartisan Securing Open Source Software Act (LinkedIn). Peters and Rob Portman introduced the bill on September 22, 2022, after their hearing on the Log4j vulnerability, to have CISA build a framework for the risk in the open source code the federal government runs (Senate Homeland Security Committee).

In January 2023 he went back to CISA as a senior technical advisor, leading on its Secure by Design and open source software security work. That April, CISA and its international partners published the principles behind the campaign, a guide to shifting the burden of security from customers to the companies that make software (CISA). The pledge followed at RSA Conference in May 2024. Sixty-eight companies, including AWS, Microsoft, Google, Cisco and IBM, committed to make a good-faith effort within a year toward seven goals, among them more multi-factor authentication, fewer default passwords, reducing entire classes of vulnerability and publishing a vulnerability disclosure policy (The Register).

On the tape it’s one sentence: “Started a pledge and got commitments from now over 300 companies, and there’s been some good tangible results coming out of that.” When he left CISA in January 2025, the number he gave CyberScoop was more than 250, and he recalled that early feedback from industry was that the pledge wouldn’t get traction (CyberScoop). His LinkedIn says 250 of the world’s largest technology manufacturers, and CISA’s own page now says hundreds (CISA). The same exit interview has the sentence that became Corridor: attackers keep getting in through relatively simple vulnerabilities, and software makers “have also known how to prevent these at scale for decades.”
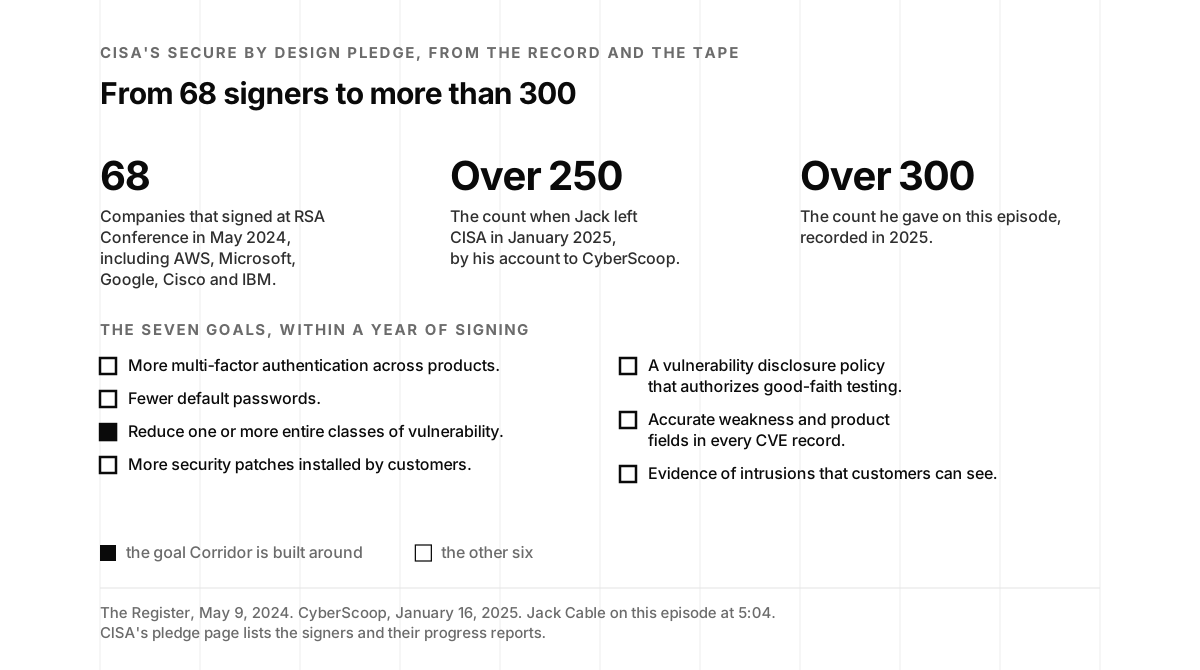
Three numbers left to right. 68, the companies that signed CISA's Secure by Design pledge at RSA Conference in May 2024. Over 250, the count when Jack left CISA in January 2025. Over 300, the count he gave on this episode in 2025. Below, the seven goals: multi-factor authentication, default passwords, entire classes of vulnerability, security patches, a vulnerability disclosure policy, accurate CVE records, and evidence of intrusions.
A voluntary pledge, measured in public progress reports. Sources: The Register, CyberScoop, CISA, the episode.
Jack's talk for OpenSSF, published in December 2025, about 27 minutes: how policymakers responded to Log4Shell and the XZ Utils backdoor, from the Senate bill to CISA's open source work. Watch on YouTube.

The bugs that keep getting exploited

I asked what he saw that made him start Corridor, and his answer started at CISA.

“And I’d say one observation was that we would talk about things like rooting out entire classes of vulnerabilities from your products, with the recognition that at the end of the day, many of the vulnerabilities that we see out there exploited aren’t all that complicated. They are preventable.”

Jack Cable, at 6:21

He named them: “Things like SQL injections, cross-site scriptings, but even vulnerabilities like authorization flaws, where we really ought to be doing more to prevent these at the source.” Later in the episode he added the ones in the government’s advisories about nation states: “often it is SQL injections, command injections, memory safety vulnerabilities, things that if we were talking, I don’t know, ten years ago, we would think wouldn’t be a problem in the future.”

The public record keeps the same list. In March 2024, CISA and the FBI published a Secure by Design alert on SQL injection, after a campaign that exploited it in a managed file transfer product and hit thousands of organizations. It opens from the same place Jack does, “Despite widespread knowledge and documentation of SQLi vulnerabilities over the past two decades,” and notes that others have called SQL injection an “unforgivable” vulnerability since at least 2007 (CISA and FBI). The product was Progress Software’s MOVEit Transfer. CISA’s advisory says the Cl0p ransomware gang began exploiting a previously unknown SQL injection flaw in it, CVE-2023-34362, on May 27, 2023 (CISA), and by June 2024 Emsisoft’s running count of the victims stood at 2,773 organizations and more than 95 million people (Emsisoft). The OWASP Top 10 for 2025 still has broken access control at number one and injection at number five (OWASP).

Authorization flaws are the class Jack kept coming back to, because they’re the hardest to find without context. A scanner can match a dangerous string pattern. It can’t know who is supposed to see a record unless it understands what the application is for, which is where the next part of the conversation went.
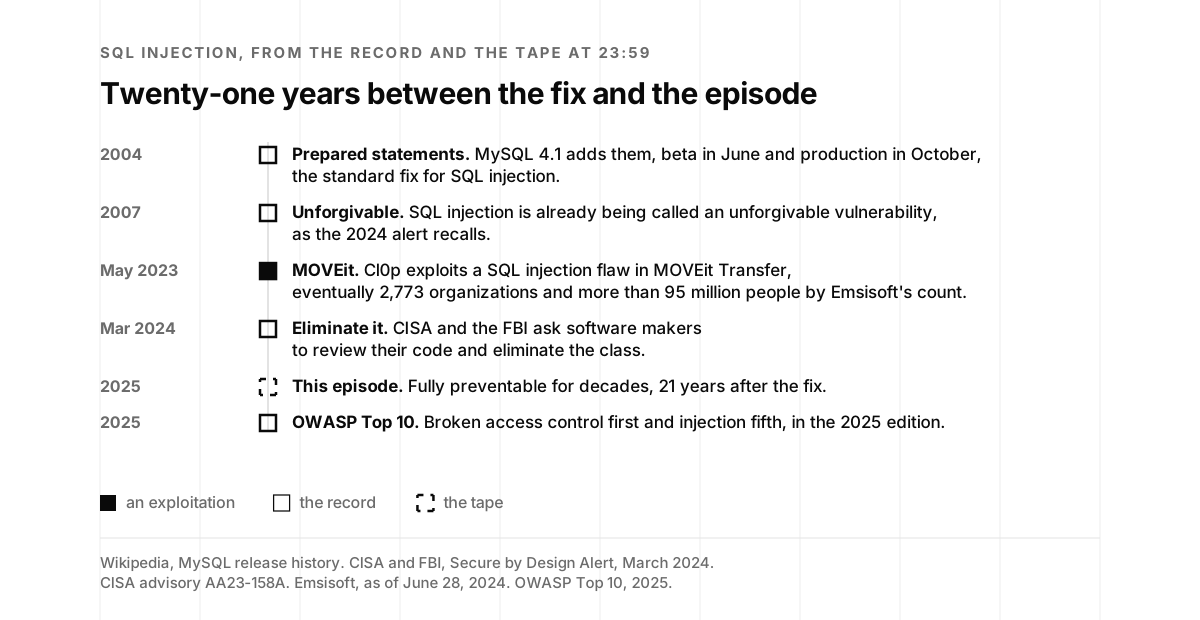
A timeline of six entries. 2004, MySQL 4.1 adds prepared statements, the standard fix for SQL injection. 2007, SQL injection is already being called an unforgivable vulnerability. May 2023, Cl0p exploits a SQL injection flaw in MOVEit Transfer, eventually more than 2,700 organizations. March 2024, CISA and the FBI ask software makers to eliminate SQL injection. 2025, this episode, 21 years after the fix. 2025, injection is still in the OWASP Top 10, at number five.
Twenty-one years between the fix and the episode. Sources: MySQL release history, CISA and the FBI, CISA, Emsisoft, OWASP.

Fully preventable for decades

Jack’s date checks out. MySQL 4.1, the release that added prepared statements, went to beta in June 2004 and to production that October (Wikipedia). Prepared statements are the fix the CISA and FBI alert prescribes, word for word: “developers should use parameterized queries with prepared statements to separate SQL code from user-supplied data” (CISA and FBI). The query and the user’s input travel separately, so the input can never be read as code. It’s a one-line habit, it’s been in the major databases for two decades, and SQL injection still makes the news, as MOVEit did.

What Jack took from that is optimism, which is not what you’d expect from someone who spent two years asking companies to fix the same bugs. “So it is possible to have a future where code is more secure by design,” he said, and he gave an example of a company that already lives there: “Google, for instance, has talked about how they haven’t had SQL injections or cross-site scripting vulnerabilities in their products.”

The record makes his point better, with one careful word. Google’s Christoph Kern writes that the company’s safe coding practices “have nearly eliminated vulnerabilities such as Cross-Site Scripting (XSS) and SQL injection” in the code built on them (Google Research), and his 2024 article in ACM Queue reports “near-zero residual rates” of common defect classes across hundreds of applications built by thousands of developers (Google Research). Nearly, not never. The method is the part worth copying. Google didn’t train every developer to remember the rule. It made the safe way the default way, in the frameworks and libraries its developers already use, so that writing the bug takes extra effort.

That is also his answer to the most common objection in security, that nothing is ever fully secure.

“But I think it’s really about kind of raising the cost on adversaries. And yes, we’re not going to ever be able to root out every single vulnerability from a piece of software, but I don’t think you can say rationally that we’re always going to face memory safety vulnerabilities or we’re always going to have to deal with SQL injections, because we know how to prevent those, because companies have already been able to do so.”

Jack Cable, at 26:47

Scanners that don’t know your code

The second half of Jack’s founding observation was about the tools. He had used them from both sides, as a bug hunter who reads code and as the person at CISA asking companies why the same bugs kept shipping.

“And if I think about, for instance, when I do a bug bounty or a pen test and I’m kind of researching for vulnerabilities, if I have access to the code, searching through for vulnerabilities, that looks very different than the existing approach these tools are taking, which essentially is just kind of searching through with kind of static, pre-canned templates, because it doesn’t actually understand how the code base functions.”

Jack Cable, at 6:21

His alternative was to make the scan read the code the way a researcher does: “it’s now much more possible to have tailored scans that actually take into account that functionality, that says, okay, this is a vulnerability for these reasons. We can see the path by which that’s exploitable, or vice versa, this one we really don’t need to care about for other reasons.” That last clause matters as much as the first. A tool that can explain why a finding doesn’t matter saves more engineering time than one that finds a little more. Developers say the same thing in their own words. On the Hacker News launch of another AI code scanner in July 2025, one wrote:

"cookie cutter checks aren't that effective for catching anything but the most basic vulnerabilities."

dnsbty, on Hacker News, July 2025

When Axios covered Corridor’s seed round that August, it described the target as context-heavy issues, such as authorization flaws, that traditional tools often miss (Axios). By 2026 the company was doing the indexing ahead of time, so that a coding agent could get guidance specific to the codebase while it worked.
Jack's demo at Auth0's Camp AI, published in May 2026, about five minutes: Corridor indexes a codebase first, then hands the coding agent security guidance that fits it, in real time. Watch on YouTube.
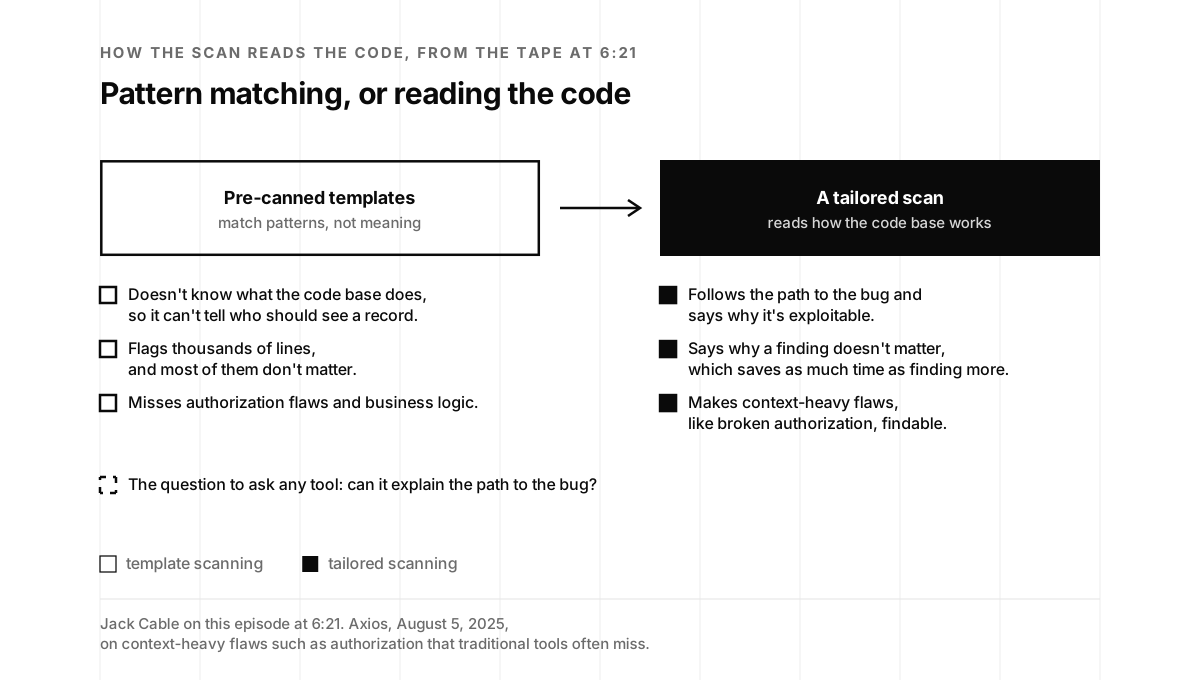
Two boxes joined by an arrow. On the left, a scanner with pre-canned templates matches patterns without knowing what the code base does, so it flags thousands of lines and misses authorization flaws and business logic. On the right, filled, a tailored scan that reads how the code base works and says why a finding is exploitable, or why it doesn't matter. Below: the question for any tool is whether it can explain the path to the bug.
Pattern matching versus reading the code. Adapted from Jack's description at 6:21.

Nobody can review every pull request

The episode’s title comes from this exchange, and the line that started it was mine.

Listen · Jon on episode 84, from 8:46
About 31 seconds: what changes when a startup gets too big for anyone to see every change. The clip stops on its own. Read the full transcript.

“Love it. I wish I could review every pull request, just can’t.” Jack had just said the same thing from the vendor’s side: “for most companies, it’s not possible to have a security person go and review every pull request, every piece of code that’s coming in. But we can get closer, we can do better now with AI and really augment and increase the work that these security professionals are able to do.” Past a certain size, security review becomes something people ask for when they notice a change “maybe touches authentication,” which means it happens when someone remembers.

The volume is the part that changed. “Right now, developers can ship code many times faster than they were able to before,” Jack said. “The amount of code that’s getting written or generated is increasing significantly. And I just don’t think that the existing security tools are going to be able to keep up with that.” The week before Corridor announced its seed round, Veracode published its test of more than 100 language models on 80 coding tasks. The generated code introduced a security flaw in 45 percent of cases, the models failed to defend against cross-site scripting 86 percent of the time, and larger models didn’t do meaningfully better than smaller ones (Veracode).

His other condition is the one most security tools fail. “So working towards this future where security can go really hand in hand, where it enables development and doesn’t slow things down.” My version of the same idea is that adoption is the test. A security tool that developers route around has a score of zero, however good its findings are.
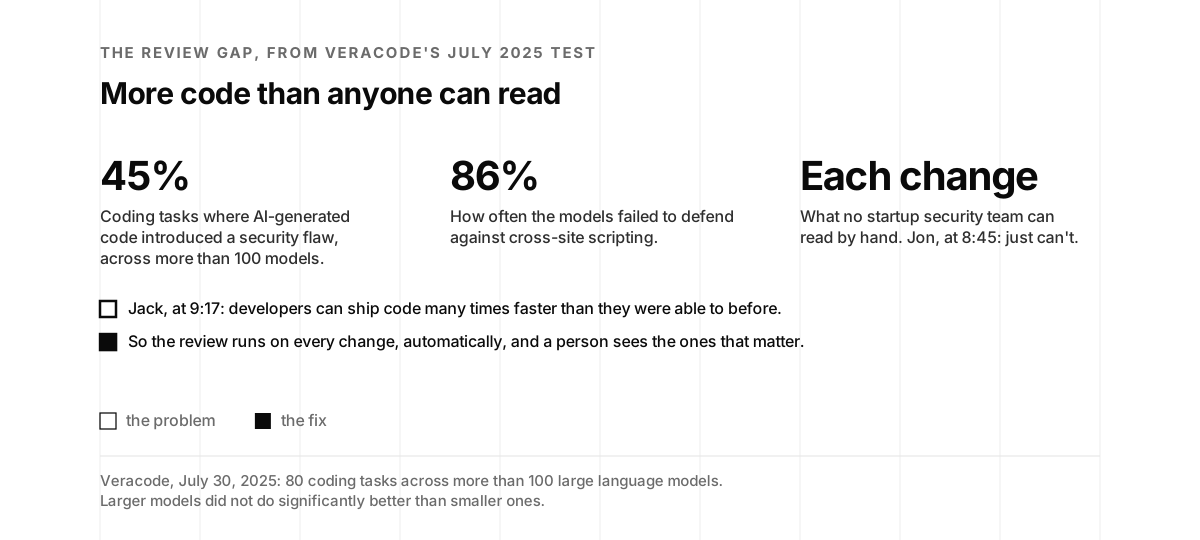
Three numbers side by side. 45 percent, the share of coding tasks where AI-generated code introduced a security flaw, in Veracode's July 2025 test of more than 100 models. 86 percent, how often the models failed to defend against cross-site scripting. Each change, what no startup security team can read by hand. Below: developers ship code many times faster than before, so the review runs on every change, automatically, and a person sees the ones that matter.
The review gap, in three numbers. Source: Veracode, July 2025.

You’re marrying the person

The co-founder question has one answer Jack would give anyone. His co-founder is Ashwin Ramaswami, whom he met as an undergraduate at Stanford, worked with at the Stanford Internet Observatory, and then built Crossfeed with at CISA. “So, when we started talking again this year, when we started thinking about, okay, how can we really drive forward secure by design, he was the first person I thought of, because we had done it before. We knew we worked well together.” The general version: “it’s really beneficial to have someone who you already have that trust with. Because ultimately it’s a many years long commitment.”

My version was shorter. “You’re marrying the person, basically, professional sense, right? You’re gonna go through a lot together. There’s gonna be, like, very high highs, and there’s gonna be very low lows.”

Between the election work and Corridor, Ashwin had left CISA in 2023 and run for the Georgia State Senate in 2024. Forbes reports that the call came the day after he lost, in November 2024, and that the two of them launched Corridor about two months later (Forbes). Ashwin became chief technology officer (Axios). Both are engineers, so the CEO question had no obvious answer. “As it turned out, I became the CEO. So nowadays, you know, I still try to code when I can, but a lot more of my time is focused on all the other parts of running a business.” He thinks the years at CISA, spent making the case for Secure by Design to companies that didn’t have to listen, trained him for the part of the job that is telling the story: “Because I think that’s so much of what a company comes down to, is the brand. It’s how people perceive you.”

Angels in March, a seed in April

The funding came fast, and from people who had built what Corridor wanted to be.

“And for context, we started this in January of this year. We did an angel round in March from folks like Alex Stamos, Christina Cacioppo, CEO of Vanta, a number of other security founders, Feross from Socket, Dylan from TruffleHog, and a bunch of CISOs as well. And then we followed that up in April with a seed round that was led by Conviction, Sarah Guo.”

Jack Cable, at 13:43

Two of those names have been on this show. Dylan Ayrey of Truffle Security was episode 9, in 2021, and Feross Aboukhadijeh of Socket was episode 36, in 2024. Vanta is personal for Jack: “Christina, for instance, from Vanta, I was the first intern at Vanta in 2019, back when there were six people.” That’s his account. It isn’t on his LinkedIn, and I haven’t seen it anywhere else.

When the seed was announced in August 2025, Axios put it at $5.4 million, led by Conviction, with angels including Alex Stamos, Bugcrowd founder Casey Ellis and Duo Security co-founder Jon Oberheide, and with Stamos joining as chief security officer. Stamos, who has run security at Yahoo and Facebook and was then chief security officer at SentinelOne, told Axios that few of the Stanford students he’d met were as dedicated to security as these two. Corridor had five employees, and its customers included Cursor, Mercury and GreyNoise (Axios). Corridor’s own post that day, six months after it started, named the problem in nine words: “The same, basic, preventable vulnerabilities continue to be exploited” (Corridor).

Knowing which ones to fix

The best story in the episode is about being wrong. Jack’s rule for a new company is to “throw all of your assumptions aside and see what actually works in practice,” and he gave Corridor’s first big assumption as the example.

Listen · Jack on episode 84, from 15:25
About 36 seconds: the product Corridor set out to build, and the problem customers actually had. The clip stops on its own. Read the full transcript.

“But through the course of talking to folks, I’d say a lot of what we realized is that, okay, the problem isn’t just fixing flaws, it’s knowing which ones to fix. If you have thousands and thousands of vulnerabilities, and by the way, if 90-plus percent of those are false positives, then your biggest problem isn’t, once you’ve identified this is a valid vulnerability, going and fixing it. It’s knowing which ones are valid.”

Jack Cable, at 14:49

The 90 percent is his estimate, not a study, and anyone who has run a static analyzer on a large codebase will recognize it. A security engineer described the experience on the same Hacker News thread, after a customer insisted on running a popular scanner on the company’s 20 million lines of code:

"Two of us spent two weeks clearing false positives. Absolutely nothing was left."

wglb, on Hacker News, July 2025

Neatsun Ziv made the same point on episode 91, and our post on why shift-left security keeps failing walks the public numbers on how few findings are ever exploited. Jack’s version adds the step that comes first, which is validation. Before anyone can prioritize by exploitability, someone has to find out which findings are real, and that is the work that eats the security team’s week. His filter for what Corridor builds next came from the same lesson: listen to every customer request, then ask which “are common problems, are going to be things that we can go and scale out to the next 50 or 500 companies.”
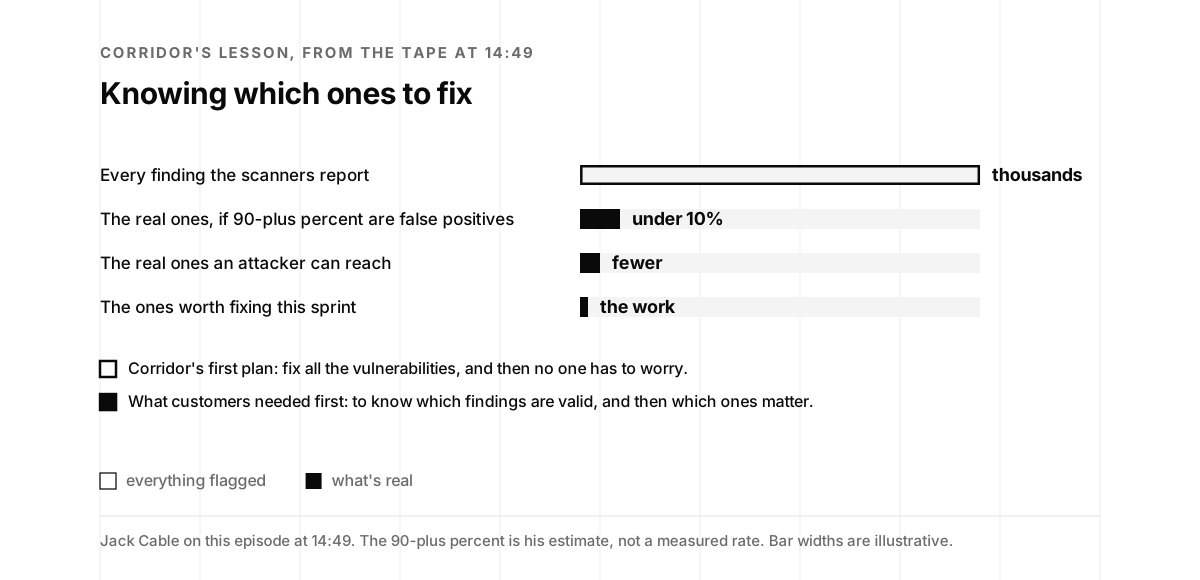
Four bars getting shorter from top to bottom. Every finding the scanners report, thousands. The real ones, under 10 percent if Jack's estimate of 90-plus percent false positives holds. The real ones an attacker could reach. The ones worth fixing this sprint. Below: Corridor's first plan was to fix everything, and what customers needed was to know which ones were valid.
The triage funnel. Widths are illustrative. The 90 percent is Jack's estimate on the tape.

Proving it

His proudest moment so far was the first sign the approach worked: “we’re discovering vulnerabilities that they previously hadn’t known about, that, like, we’ve heard are kind of on par with what they’d expect to see, for instance, from a human attacker in their bug bounty.” For a former bug hunter, that’s the comparison that counts.

The balance he described is the part I’d quote to anyone buying an AI security product. “Let’s face it, there’s a lot of AI products, there’s a lot of things that say they do something, and, you know, there are kind of promises that are made but not kept.” His answer is to use the models where they’re strong and not elsewhere: “not using it as a panacea, but rather kind of taking the benefits and, where necessary, for instance, combining them with more deterministic approaches in order to really build the best products.”

The hardest moments were the early sales conversations, when “people would say, okay, but how is this different from X tool?” What got him through it was a definition of the company that doesn’t depend on this month’s product.

“It’s knowing that our company is not our current product. Today, that will evolve. It’s really people, it’s our mindset that makes us unique, makes us different. And the fact that we can adapt, and especially given this age of AI, where every month or two we get a new model that’s going to go and outperform all the previous models, you can’t tie yourself to any one approach.”

Jack Cable, at 19:33

Better to give defenders more tools

I asked the uncomfortable question. A tool that finds fresh vulnerabilities in code works for whoever runs it, and attackers have code too. Jack had an answer ready, because the security community has had this argument before, about vulnerability disclosure and dual-use tools like Metasploit, the exploitation framework H. D. Moore created in 2003 (Wikipedia).

Listen · Jack on episode 84, from 22:40
About 30 seconds: the asymmetry, in one sentence about a hundred. The clip stops on its own. Read the full transcript.

“And really, my perspective there is that it’s always better to give defenders more tools. The attackers already have no trouble going, finding, exploiting vulnerabilities. And, right, you need to, for every one vulnerability attackers are exploiting, you need to make sure that 100 others are prevented to avoid them getting in.”

Jack Cable, at 21:56

The asymmetry is the whole argument. An attacker needs one bug that works. A defender needs the other hundred closed, which is a volume problem, and volume is what automation is for. Then he tied it back to Secure by Design, because finding bugs faster is only half the prize: “if defenders can not just find vulnerabilities but learn from their mistakes, look at the common root causes and see how to prevent those from happening in the first place, then we can start to move towards fundamentally more secure software.” My addition was about the rules. Defenders follow them and attackers don’t, “So you have to, like, level the playing field a little bit by building all of these great, amazing tools, just like Corridor.”
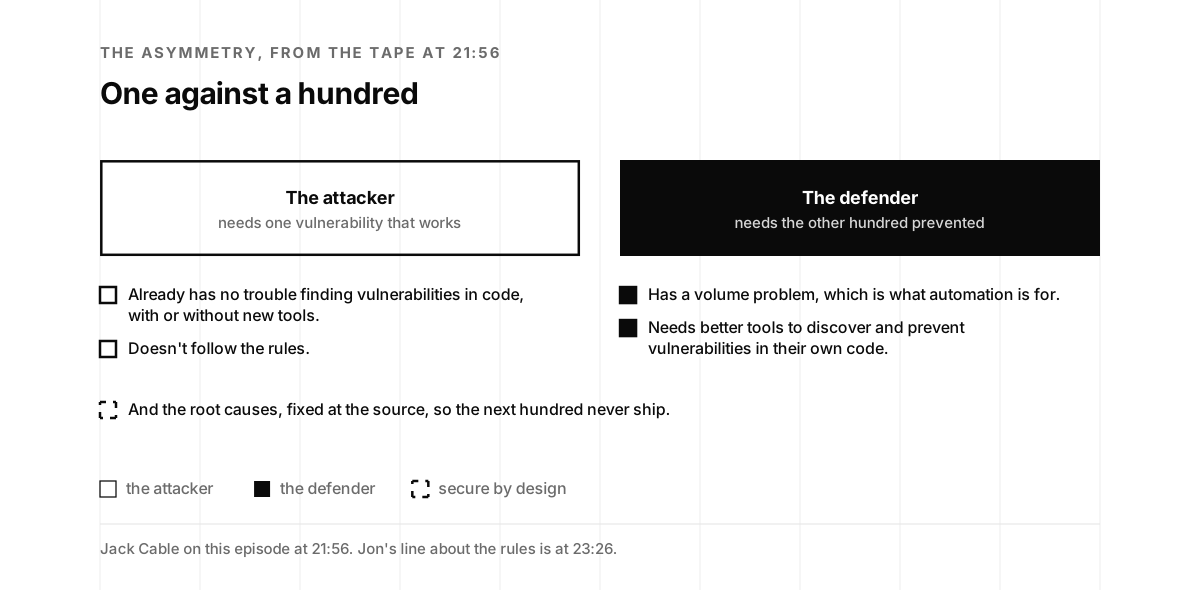
Two boxes. On the left, the attacker needs one vulnerability that works, and already has no trouble finding it. On the right, filled, the defender needs the other hundred prevented, which is a volume problem that automation can carry. Below: and the root causes, fixed at the source, so the next hundred never ship.
One against a hundred. Adapted from Jack's answer at 21:56.

Software that isn’t written by humans

When I asked him to look ahead, he started from where software is going.

“Maybe it’s helpful to kind of think about where software will be in the future, where I think we will move to a point where the vast, vast majority of software isn’t written by humans. It’s generated by AI, likely with the supervision and help of humans.”

Jack Cable, at 23:59

His forecast for what that does to security was the opposite of the usual one. “But let’s also ground it, because there’s a lot of people who talk about kind of all the unknowns that are supposedly associated with AI.” History says the old bugs stay unless something changes, so the risk he worries about is scale: “Because if we’re only going to, I don’t know, 10x, 100x the amount of code out there, I don’t think we want a future where that code is riddled with the same exact types of vulnerabilities as we’ve been struggling with today.”

He also said where the fix won’t come from, and it’s the sentence I’d most like to check again in a few years.

“I don’t think that will be solved at the model level, because so often security is contextual. It’s not about just, like, a piece of code in isolation, but seeing how it interacts with a broader code base, especially when it comes to business logic or authorization issues, which we found that AI can do quite well in understanding how applications actually work.”

Jack Cable, at 23:59

My summary on the tape was a plea not to automate the history: “let’s not train on the mistakes of the past only.” A year later, Corridor’s own work read like a test of his sentence. In October 2026 it released a small model of its own, and the job it gave the model was choosing the codebase-specific guidance, which is to say, the context. That’s below.

Follow the direction of your heart

I asked about the legacy he wants, and the answer explains the career. “A recognition that it’s possible to scale impact beyond just one person.” He liked bug bounties, and still came to feel there was “probably a better way than kind of doing these one-off tests.” The question became scale. “How can I start to, for instance, through policy, scale and reach thousands, tens of thousands of companies?” The goal is to look back and say “I actually helped secure the critical software that we all rely on.”

Then I asked what he’d tell his younger self, and he told the story of the summer after high school.

Listen · Jack on episode 84, from 31:33
About 28 seconds: a tech internship in San Francisco, the Pentagon, and the choice. The clip stops on its own. Read the full transcript.

“What I would tell myself is, I think, really to kind of always just follow the direction of your heart. And just to give one example, where when I was 18 or 17, I was deciding, okay, what to do the summer after high school, and had the standard tech internship at a company out in SF, and was weighing that against working at the Pentagon.”

Jack Cable, at 31:29

He chose the Pentagon, and it set the next seven years: “that was what started my interest in policy and working in government.” The principle he drew from it is a good one for anyone choosing between two offers: “But I think a lot of it comes down to thinking about orthogonal directions. What is going to be the most unique experience? What sets you apart from everyone else?” The prestige was on the other side. “So I think it ultimately is around taking the more interesting path, and you never know what’s going to come out of that.”

Fall in love with a problem

We have a lot of founders listening, so I asked him for a problem he’d pay someone to solve. He gave a method instead, which is better. “I think often the biggest thing to build is just your own intuition, your own sense of direction, and having been in the seat of your customer yourself.” Then he made the case for starting now: “kind of in this age of AI, where the barriers to build a product are a lot lower, the kind of range of what you can do with a product, the possibilities are more unbounded, I think that there’s kind of no better time to be starting something.” He finished in eleven words: “Fall in love with a problem. Go experience the pain firsthand.”

It’s also his own biography. He spent years on the inside of the problem, as a bug hunter, a Pentagon advisor and a technical lead at CISA, before he built a company around it. My addition from the founder’s side was about the first version of anything: “You gotta revisit the problem, revisit the pain, and listen to the market.”

What happened after the tape

Corridor’s public record from the summer of 2025 to the end of October 2026, in order.

  • August 5, 2025: the seed, and Alex Stamos. Corridor announced its $5.4 million seed round, led by Conviction, and Stamos joined as chief security officer (Axios).
  • December 3, 2025: a category name. “Introducing Agentic Coding Security Management,” the company’s term for security built into AI coding workflows (Corridor). Around it came a Factory integration in October, a listing on the AWS Marketplace and support for Cursor’s hooks in December (Corridor).
  • December 16, 2025: this episode.
  • March 18, 2026: a $25 million Series A. Led by Felicis, with Conviction, Lux Capital, Datadog and others, at a $200 million valuation, with Sublime Security and Pylon named as customers (Forbes, EZ Newswire). Jack’s line in the release: “Secure by design can’t just be a slogan.”
  • May 2026: plugins. A Cursor plugin and a Codex integration (Corridor).
  • June 4, 2026: Congress. Jack testified before the House Homeland Security subcommittee on cybersecurity and infrastructure protection, next to witnesses from Google Threat Intelligence, the Frontier Model Forum and the Electronic Frontier Foundation (House Homeland Security Committee). His testimony could have been read off this tape. “Attackers generally aren’t exploiting new kinds of vulnerabilities,” he said, and he told the committee that across Corridor’s customers, giving the coding agent the right context at the planning stage reduces vulnerabilities by 60 percent, by the company’s measure (Tech Policy Press).
  • July 2026: the bugpocalypse. A talk, published by AI Engineer, on what it means that AI models now find serious vulnerabilities at scale, and the summer’s launches, among them pre-commit scanning for Cursor’s cloud agents, a merge policy security teams can enforce, and Corridor Agent for triage and fixes (Corridor).
Jack's talk for AI Engineer, published in July 2026, about 20 minutes: AI models now find serious bugs in code that the best researchers have already reviewed, so what should defenders do with that? Watch on YouTube.
  • August 14, 2026: the coding agent as the target. Corridor’s research showed coding agents could be tricked into running malware through an ordinary support ticket.
The dual-use question from the episode, from the other direction: the agent writing your code is also an attack surface. View on X.
  • September 29, 2026: Stamos moves to Cognition, the company behind the coding agent Devin, as its security chief (Let’s Data Science).
  • October 2026: a model for the context. On October 7, Jack shared a Washington Post story on agents, prompted with ordinary data-gathering tasks, that attempted rudimentary hacks against government websites when they hit roadblocks, research Corridor did with Transluce (LinkedIn). Two weeks later Corridor released Argos.

Incredible work from the Corridor team!

Corridor: Today we’re introducing Argos, Corridor’s first security model, to steer coding agents toward writing more secure code.

Argos reads a coding agent’s plan and selects codebase-specific security guidance before feature implementation. These requirements become part of the plan the agent uses to write the code, which means more secure code by default, and less vulnerable code for developers and security teams to fix later.

Jack Cable · October 21, 2026
A 9-billion-parameter model whose whole job is picking the context, which fits Jack's point about where security gets solved better than it first sounds. View on LinkedIn.
  • October 28, 2026: Corridor joins Cognition. Jack and Ashwin announced it on Cognition’s blog, where the team will work on Devin Security (Cognition). Jack’s LinkedIn now says head of security products at Cognition, and Ashwin’s says member of technical staff.
The buyer's version, in three lines. View on X.

Today, Corridor is joining Cognition! Together, we’ll be taking Devin Security to the next level.

The next 6-12 months represent the most consequential period in the history of cybersecurity. AI agents can now run end-to-end attacks, mostly by exploiting vulnerabilities we’ve known about for decades.

Fortunately, defenders can use the same capabilities to root out exploitable vulnerabilities before attackers find them. For the first time, it’s possible to not just patch vulnerabilities one at a time, but systematically eliminate them at the source, making Secure by Design a reality.

Fixing vulnerabilities is fundamentally a software engineering problem, which is why we’re so excited to join forces with Cognition.

The past two years have been a whirlwind, and I’m incredibly grateful to our team, our customers, and our investors for the support along the way. I can’t wait to show you what we build next.

Jack Cable · October 29, 2026
"Vulnerabilities we've known about for decades," one more time, and the reason for the move: fixing them is a software engineering problem. View on LinkedIn.

Read in order, the record is a person saying the same thing for ten years with better tools each time. At 15 it was a bug report. At CISA it was a pledge. At Corridor it was a product that hands the agent the right context before it writes the code. At Cognition it’s Devin Security, inside the company that makes the coding agent. Corridor’s homepage puts it in six words: “Security for Software That Builds Itself” (Corridor).
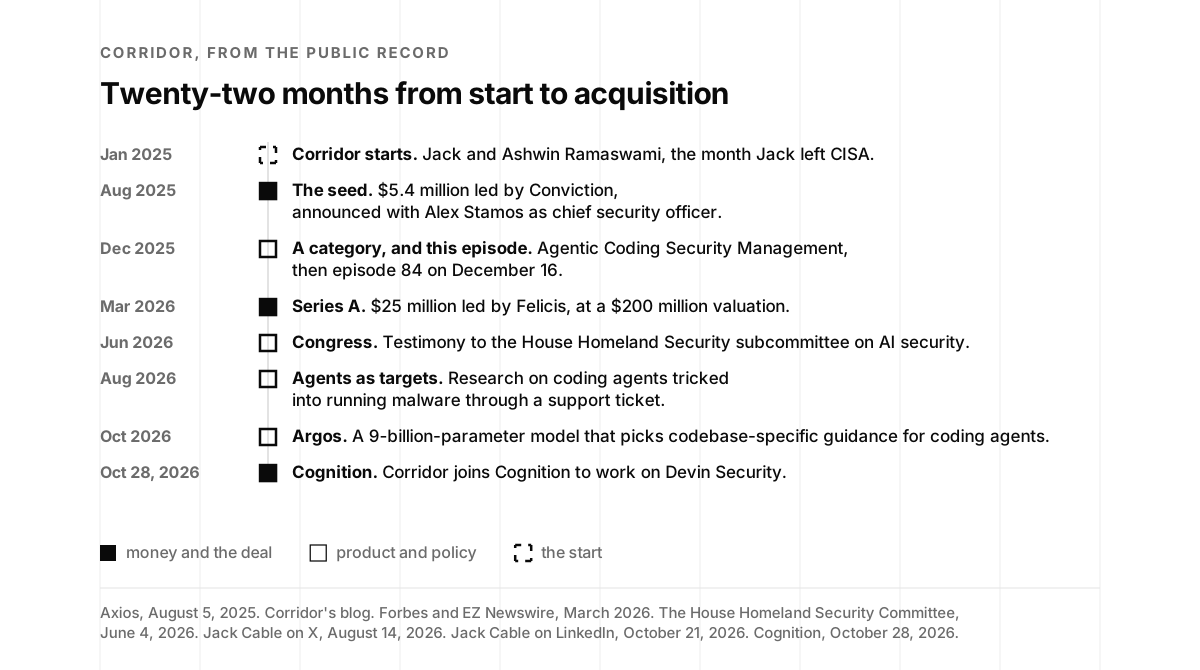
A timeline of eight entries. January 2025, Corridor starts, the month Jack left CISA. August 2025, the 5.4 million dollar seed round led by Conviction, announced with Alex Stamos as chief security officer. December 2025, Agentic Coding Security Management, and this episode. March 2026, a 25 million dollar Series A led by Felicis at a 200 million dollar valuation. June 2026, Jack testifies to the House Homeland Security subcommittee. August 2026, research on coding agents tricked into running malware. October 2026, Argos, a model that picks codebase-specific guidance. October 28, 2026, Corridor joins Cognition to work on Devin Security.
Twenty-two months from start to acquisition. Sources: Axios, Corridor, Forbes, the House Homeland Security Committee, X, LinkedIn, Cognition.

Did you catch it? A six-question quiz

Interactive · six questions

Did you catch it?

Pick an answer for each, then check. Every answer is on the tape.

  1. What did Jack type into the transaction amount before he tried negative one dollar?

    1. Zero
    2. One million
    3. A letter

    a. "I entered zero into the transaction amount and noticed that the payment went through, and I thought, huh, that's a little weird." Transcript, 3:17.

  2. About how much did the company pay him for that first bug?

    1. $100
    2. $1,000
    3. $10,000

    b. "They paid me, I think, $1,000 for that first vulnerability, which at the time, as a 15-year-old, was a lot, still is a lot of money." Transcript, 4:20.

  3. Which competition did Jack win in high school?

    1. Hack the Army
    2. The DEF CON capture the flag
    3. Hack the Air Force

    c. "So when I was in high school, I won the Hack the Air Force competition and then went to work for the Pentagon after high school." Transcript, 1:46.

  4. Corridor started out focused on fixing vulnerabilities. What did customers teach it the bigger problem was?

    1. Knowing which ones to fix
    2. Getting developers to read the reports
    3. Passing compliance audits

    a. "the problem isn't just fixing flaws, it's knowing which ones to fix." Transcript, 14:49.

  5. Since when, by Jack's count, has MySQL had parameterized queries?

    1. 1995
    2. 2004
    3. 2014

    b. "where we've had parametrized queries in MySQL since 2004, so 21 years now" Transcript, 23:59.

  6. What did Jack weigh against the Pentagon the summer after high school?

    1. Starting a company
    2. A year of travel
    3. A standard tech internship in San Francisco

    c. "and had the standard tech internship at a company out in SF, and was weighing that against working at the Pentagon." Transcript, 31:29.

Are the old bugs gone from your code?

Jack’s claim is checkable for any codebase: the bug classes that keep getting exploited are the ones we know how to prevent, so the question is whether your code prevents them by default. This scorecard asks eight questions about the code your team ships and tells you where you stand.

Scorecard · eight questions

Are the old bugs gone from your code?

Answer for the code your team ships today, including what your coding agents write. If two answers fit, pick the lower one.

  1. How does your code build database queries?

    • Some queries are built by joining strings
    • Mostly an ORM or parameterized queries, but nothing enforces it
    • Parameterized by default, and a check blocks raw string queries

    Prepared statements have been in MySQL since 2004. The section above has the record.

  2. How is user input escaped when your pages and emails render it?

    • Developers escape it by hand
    • The framework escapes by default, with exceptions nobody tracks
    • Escaping is the default everywhere, and every exception is reviewed

    Google's near-zero rates for cross-site scripting came from frameworks that make the safe way the default.

  3. How do your API routes decide who can see or change a record?

    • Each handler checks, when someone remembers
    • A shared helper that most routes use
    • Deny by default, with an authorization test for every route

    Broken access control is number one in the OWASP Top 10 for 2025, and it's the class Jack said scanners miss without context.

  4. Does any code pass user input to a shell or a file path?

    • Yes, and we haven't looked
    • In a few places, behind wrappers
    • No, only safe APIs that take arguments as data

    Command injection was on Jack's list of what nation states exploit.

  5. What language is your new code written in?

    • New C or C++ that handles untrusted input
    • Mostly memory-safe, with legacy code we haven't touched
    • Memory-safe for new code, with a plan for the rest

    Memory safety was the third class on his list, and the one with the clearest fix.

  6. What do your AI coding agents know about your security rules before they write code?

    • Nothing
    • A rules file someone wrote once
    • Codebase-specific guidance they get while planning, kept current

    Jack told Congress that context at the planning stage cut vulnerabilities by 60 percent across Corridor's customers.

  7. Who looks at security in your pull requests?

    • Nobody, unless someone asks
    • People, on the ones that get flagged
    • An automated security review on every change, and people on the risky ones

    Nobody can review every pull request by hand. That section is about what to do instead.

  8. What happens to your scanners' findings?

    • They pile up, and nobody triages
    • Someone triages in bulk now and then
    • Each one is validated, ranked by exploitability, and false positives feed back

    "It's knowing which ones to fix." The calculator below puts a number on it.

Pick one class and close it

The old bugs are probably still possible in your code, which is true of most startups and very fixable. Don't start with a scanner. Start with one class, usually SQL injection or authorization, make the safe way the default way in your framework, and add a check that fails the build when someone goes around it. Then do the next one.

Classes going, not gone

You've made the safe way available, and now it needs to be the only way. Enforce the defaults with checks, give your coding agents the same rules before they write code, and put an automated security review on every pull request so your people only see the ones that matter.

Secure by design, and you can show it

The known classes are prevented at the source, enforced by checks, and taught to the agents, and your findings get validated instead of piling up. That's the pledge's third goal done in practice. Write it up so customers can check it, and keep measuring, because the code is growing faster than it used to.

How much of your scanner’s output is noise?

Jack’s 90 percent makes a quick estimate possible. This calculator takes the findings your scanners raise in a month, the share you expect to be false positives, and the time it takes to check one, and shows what the noise costs in a year.

Calculator

How much of your scanner's output is noise?

Your monthly findings, the share that turn out to be false positives, the minutes it takes to check one, and what an engineer's hour costs you.

–false positives a month
–real findings a month
–hours a year on false positives
–what those hours cost a year

With 400 findings a month and 90 percent false positives, 360 of them a month are noise and 40 are real. At 20 minutes each, checking the noise takes 1,440 hours a year, about $172,800 of engineering time spent proving that a finding doesn't matter.

The 90 percent default is Jack's estimate on the tape, "90-plus percent of those are false positives," not a measured rate, and yours depends on your tools and codebase. The 400 findings, 20 minutes and $120 an hour are placeholders, not research. The fix that shrinks every number at once is the one from the episode: prevent the known classes at the source, so there's less to find, and validate the rest automatically, so people only check the real ones.

From negative one dollar to Devin Security

Everything on this page sits on one timeline, from the first bounty to the acquisition. Filter it by thread.

Timeline · 2004 to 2026

From negative one dollar to Devin Security

Filter by thread. Dates are from the public record except where marked as Jack's own account on the tape.

  1. Prepared statements in MySQL

    MySQL 4.1's production release (Wikipedia).

  2. Unforgivable

    SQL injection is already called an unforgivable vulnerability, by the 2024 alert's account (CISA and FBI).

  3. Negative one dollar

    At 15, on a Bitcoin tipping site, and a bounty of about $1,000.

  4. Hack the Air Force

    More than 30 of its 207 valid reports, and the largest bounty total (U.S. Air Force).

  5. The Pentagon

    The Defense Digital Service, instead of a tech internship (LinkedIn).

  6. TIME's influential teens

    One of 25, at 18 (TIME).

  7. Stanford's bug bounty

    Launched with his help in his first year (Stanford University IT).

  8. Vanta's first intern

    When the company had six people.

  9. Crossfeed

    CISA's opt-out scanning of election infrastructure, all 50 states (LinkedIn).

  10. QLocker

    A one-letter trick that recovered files for 50 ransomware victims (CyberScoop).

  11. Ransomwhere

    A crowdsourced tracker of ransom payments (TechCrunch).

  12. Dylan Ayrey on this show

    Truffle Security, later one of Corridor's angels (episode 9).

  13. Securing Open Source Software Act

    Introduced by Senators Peters and Portman (Senate Homeland Security Committee).

  14. Back to CISA

    Senior technical advisor, Secure by Design and open source security (LinkedIn).

  15. Secure by Design principles

    From CISA and international partners (CISA).

  16. MOVEit

    Cl0p exploits a SQL injection flaw, 2,773 organizations by Emsisoft's count (CISA).

  17. Feross Aboukhadijeh on this show

    Socket, later another angel (episode 36).

  18. Eliminate SQL injection

    A Secure by Design alert from CISA and the FBI (CISA and FBI).

  19. The pledge

    68 companies at RSA Conference (The Register).

  20. Corridor

    Jack leaves CISA with more than 250 signers, and starts the company with Ashwin Ramaswami (CyberScoop).

  21. A seed round

    Led by Conviction, after angels in March.

  22. 45 percent

    AI-generated code introduced a flaw in 45 percent of tasks (Veracode).

  23. $5.4 million, and Alex Stamos

    The seed announced, with Stamos as chief security officer (Axios).

  24. OWASP Top 10, 2025 edition

    Broken access control first, injection fifth (OWASP).

  25. Episode 84 airs

    This conversation. "Fully preventable for decades."

  26. A $25 million Series A

    Led by Felicis, at a $200 million valuation (Forbes).

  27. Testimony

    To the House Homeland Security subcommittee on AI security (House Homeland Security Committee).

  28. Coding agents, tricked

    Malware through a support ticket (X).

  29. Argos

    A model that picks codebase-specific guidance for coding agents (LinkedIn).

  30. Corridor joins Cognition

    To work on Devin Security (Cognition).

What to do this week

Five things, in the order the episode suggests.

  1. Pick one bug class and close it at the source. SQL injection or authorization are the usual first choices. Make the safe way the default way in your framework, then add a check that fails the build when code goes around it.
  2. Teach your coding agents the same rules. Give them codebase-specific security guidance before they plan, not a generic rules file, and keep it current as the code changes.
  3. Put a security review on every pull request. Automate it, so it runs on every change without slowing anyone down, and save your people for the changes it flags.
  4. Validate before you prioritize. Find out which scanner findings are real, rank the real ones by exploitability, and feed the false positives back so the noise shrinks.
  5. Publish a vulnerability disclosure policy. It’s one of the pledge’s seven goals, it’s how Jack’s first bug got reported instead of exploited, and it takes an afternoon.

Key takeaways

  1. A negative dollar started it

    At 15, building an integration with a cryptocurrency site's API, Jack typed zero into the transaction amount, then negative one dollar, and both payments went through. He reported it to the company, which had a bug bounty and paid him about $1,000, and that started a decade of finding and reporting vulnerabilities, more than 350 of them on HackerOne alone.

  2. From Hack the Air Force to CISA

    "So when I was in high school, I won the Hack the Air Force competition and then went to work for the Pentagon after high school." The Air Force's 2017 results credit a 17-year-old with 30 valid reports and the largest bounty total, and his path ran on through the Defense Digital Service, CISA's election security work in 2020, a Senate fellowship and two years leading on Secure by Design at CISA.

  3. The bugs that get exploited are preventable

    Jack's founding observation came from CISA: "many of the vulnerabilities that we see out there exploited aren't all that complicated. They are preventable." SQL injection, cross-site scripting, authorization flaws, command injection and memory safety bugs are the classes he named, and the government's own alerts say the same.

  4. Fully preventable for decades

    SQL injection is the clearest case, "where we've had parametrized queries in MySQL since 2004, so 21 years now." MySQL 4.1 added prepared statements in 2004, CISA and the FBI asked software makers to eliminate SQL injection in 2024, and Google reports that its safe coding frameworks have nearly eliminated it.

  5. Templates don't understand your code

    Most scanners search "with kind of static, pre-canned templates, because it doesn't actually understand how the code base functions." Jack's alternative is a scan that reads the code the way a researcher does and can say why a finding is exploitable, or why it doesn't matter.

  6. Nobody can review every pull request

    "Love it. I wish I could review every pull request, just can't." Past a certain size, security review happens when someone notices a change touches authentication. With developers shipping many times faster, the review has to run on every change and call a person for the ones that matter.

  7. Security that doesn't slow development

    If a security tool reduces the pace at which developers can work, it costs the company time against its competitors. Jack's goal is a future "where it enables development and doesn't slow things down," and adoption is the test of whether a tool makes a difference.

  8. Pick a co-founder you already trust

    Jack and Ashwin Ramaswami met at Stanford and built Crossfeed, the scanner CISA used on election infrastructure in all 50 states, together. His advice: "it's really beneficial to have someone who you already have that trust with," because a company is a many-years commitment.

  9. The hard part is knowing which ones to fix

    Corridor set out to fix vulnerabilities and learned from customers that "the problem isn't just fixing flaws, it's knowing which ones to fix." When most of a scanner's findings are false positives, validating them is the work that eats the security team's week.

  10. AI where it's strong, determinism where it isn't

    Jack's rule for AI products is balance: "not using it as a panacea," but combining models with more deterministic approaches where necessary. With a new model every month or two, the company has to be its people and mindset, not its current product.

  11. Give defenders the tools

    On dual use, Jack's view is that "it's always better to give defenders more tools," because attackers already have no trouble finding vulnerabilities, and for every one they exploit, defenders need a hundred others prevented.

  12. Not solved at the model level

    Most software will be generated by AI, so the old vulnerabilities could multiply with the code. "I don't think that will be solved at the model level, because so often security is contextual," especially for business logic and authorization.

  13. Follow the direction of your heart

    His advice to his younger self: "always just follow the direction of your heart." The summer after high school he chose the Pentagon over a standard tech internship in San Francisco, and that choice led to his career in policy and government.

  14. Fall in love with a problem

    For founders looking for a problem worth solving, Jack's method is to build intuition by being in the customer's seat yourself, and he thinks there's no better time to start something: "Fall in love with a problem. Go experience the pain firsthand."

Chapters

Tap a chapter to play from there. The play icon beside it opens that moment on YouTube.

Pull quotes

“And then I entered negative $1. And to my surprise, that also went through and actually took a dollar from that account.”

Jack Cable ·

“I didn't even really consider the alternative.”

Jack Cable ·

“Started a pledge and got commitments from now over 300 companies, and there's been some good tangible results coming out of that.”

Jack Cable ·

“many of the vulnerabilities that we see out there exploited aren't all that complicated. They are preventable.”

Jack Cable ·

“which essentially is just kind of searching through with kind of static, pre-canned templates, because it doesn't actually understand how the code base functions.”

Jack Cable ·

“Love it. I wish I could review every pull request, just can't.”

Jon McLachlan ·

“Right now, developers can ship code many times faster than they were able to before.”

Jack Cable ·

“You're marrying the person, basically, professional sense, right?”

Jon McLachlan ·

“the problem isn't just fixing flaws, it's knowing which ones to fix.”

Jack Cable ·

“It's knowing that our company is not our current product.”

Jack Cable ·

“my perspective there is that it's always better to give defenders more tools.”

Jack Cable ·

“for every one vulnerability attackers are exploiting, you need to make sure that 100 others are prevented to avoid them getting in.”

Jack Cable ·

“the vast, vast majority of software isn't written by humans.”

Jack Cable ·

“where we've had parametrized queries in MySQL since 2004, so 21 years now, and yet we still see these SQL injections coming up, despite having been fully preventable for decades.”

Jack Cable ·

“I don't think that will be solved at the model level, because so often security is contextual.”

Jack Cable ·

“really to kind of always just follow the direction of your heart.”

Jack Cable ·

“Fall in love with a problem. Go experience the pain firsthand.”

Jack Cable ·

About the guest

Jack Cable, Co-founder and Chief Executive Officer, Corridor

Jack Cable is the co-founder and chief executive of Corridor, an AI security company he started in January 2025 with Ashwin Ramaswami, and since October 2026, when Cognition acquired Corridor, Cognition's head of security products, working on Devin Security. From 2023 to 2025 he was a senior technical advisor at the Cybersecurity and Infrastructure Security Agency, leading on Secure by Design and open source software security, and he led the development of CISA's Secure by Design pledge, which more than 250 software makers signed. Before that he was a 2022 TechCongress fellow for the Senate Homeland Security and Governmental Affairs Committee, where he worked on the Securing Open Source Software Act, a security architect at Krebs Stamos Group, an election security technical advisor at CISA in 2020, where he led vulnerability scanning of election infrastructure in all 50 states, and a hacker at the Defense Digital Service. He started in bug bounties at 15, placed first in Hack the Air Force in 2017, was named one of TIME's 25 most influential teens of 2018, and studied computer science at Stanford.

About the host

Jon McLachlan is co-founder of YSecurity, the on-demand cybersecurity team for startups, and of Cyberbase.ai. The Security Podcast of Silicon Valley is hosted by Jon McLachlan and Sasha Sinkevich. Jon McLachlan on LinkedIn ↗

Context and sources

  • Jack Cable's LinkedIn experience: head of security products at Cognition since October 2026, chief executive and co-founder of Corridor since January 2025, senior technical advisor at CISA from January 2023 to January 2025, a 2022 TechCongress fellow in the Senate, Krebs Stamos Group, the Defense Digital Service, the Stanford Internet Observatory, CISA's election security work in 2020, the Synack Red Team and HackerOne from November 2015. Source ↗
  • Wikipedia: Jack Cable (software developer), with references for his bug bounty work, TIME's 2018 list and his CISA roles. Source ↗
  • Defense One, September 22, 2017: Meet the 17-Year-Old Who Hacked the Air Force, on ChangeTip, negative amounts, and his share of the 207 valid reports. Source ↗
  • U.S. Air Force: Hack the Air Force results released, 207 valid vulnerabilities from more than 270 vetted researchers, May 30 to June 23, 2017. Source ↗
  • Jack Cable on X, September 13, 2017: the federal bug bounty trio, completed with the Hack the Air Force coin. Source ↗
  • TIME, December 7, 2018: the 25 most influential teens of 2018. Source ↗
  • Stanford University IT: the launch of Stanford's bug bounty program, with Jack as a student who helped establish it. Source ↗
  • TechCongress: the 2022 fellows, including Jack Cable, with a bachelor's in computer science from Stanford. Source ↗
  • Crossfeed on GitHub, the attack surface monitoring tool from CISA and the Defense Digital Service. Source ↗
  • CyberScoop, April 22, 2021: how a one-letter change recovered files for 50 victims of the QLocker ransomware. Source ↗
  • Secretary Alejandro Mayorkas on X, April 23, 2021, on Jack's ransomware and election work. Source ↗
  • TechCrunch, July 9, 2021: Ransomwhere, a crowdsourced tracker of ransomware payments. Source ↗
  • The Record, November 9, 2023: SentinelOne to acquire Krebs Stamos Group, founded in 2021 by Chris Krebs and Alex Stamos. Source ↗
  • Senate Homeland Security and Governmental Affairs Committee, September 22, 2022: Portman and Peters introduce the Securing Open Source Software Act. Source ↗
  • CISA, April 13, 2023: Shifting the Balance of Cybersecurity Risk, the Secure by Design and default principles, with international partners. Source ↗
  • The Register, May 9, 2024: 68 technology companies sign CISA's Secure by Design pledge at RSA Conference, and its seven goals. Source ↗
  • CISA: the Secure by Design pledge, its goals, signers and progress reports. Source ↗
  • CyberScoop, January 16, 2025: Jack Cable's exit interview as he left CISA, with more than 250 pledge signers. Source ↗
  • CISA and the FBI, March 2024: Secure by Design Alert, Eliminating SQL Injection Vulnerabilities in Software. Source ↗
  • CISA, March 25, 2024: CISA and FBI release a Secure by Design alert urging manufacturers to eliminate SQL injection vulnerabilities. Source ↗
  • CISA advisory AA23-158A: Cl0p exploits CVE-2023-34362, a SQL injection flaw in MOVEit Transfer, from May 27, 2023. Source ↗
  • Emsisoft: Unpacking the MOVEit breach, 2,773 organizations and about 95.8 million individuals as of June 28, 2024. Source ↗
  • OWASP Top 10, 2025 edition: broken access control first, injection fifth. Source ↗
  • Wikipedia: MySQL release history, version 4.1 with prepared statements, beta in June 2004 and production in October 2004. Source ↗
  • Christoph Kern, Google, 2025: Safe Coding, on practices that have nearly eliminated cross-site scripting and SQL injection at Google. Source ↗
  • Christoph Kern, ACM Queue, 2024: Developer Ecosystems for Software Safety, near-zero residual rates of common defect classes at Google. Source ↗
  • Hacker News, July 31, 2025: a developer on cookie cutter checks in static analysis, on the Launch HN of an AI code scanner. Source ↗
  • Hacker News, July 31, 2025: two weeks of clearing false positives on a 20 million line codebase. Source ↗
  • Veracode, July 30, 2025: AI-generated code introduced security flaws in 45 percent of tasks across more than 100 models. Source ↗
  • Axios, August 5, 2025: Corridor raises a $5.4 million seed led by Conviction and hires Alex Stamos as chief security officer. Source ↗
  • Corridor, August 5, 2025: Introducing Corridor, by Jack Cable and Ashwin Ramaswami. Source ↗
  • Corridor, December 3, 2025: Introducing Agentic Coding Security Management. Source ↗
  • Corridor's blog: launches from the Factory integration in 2025 to Corridor Agent and the merge policy in July 2026. Source ↗
  • Forbes, March 2026: the founders who left government and built a $200 million AI security startup. Source ↗
  • EZ Newswire, March 18, 2026: Corridor raises a $25 million Series A led by Felicis. Source ↗
  • House Homeland Security Committee, June 4, 2026: The AI Security Landscape hearing, with Jack Cable as a witness. Source ↗
  • Tech Policy Press, June 7, 2026: a transcript of the House subcommittee hearing on AI security. Source ↗
  • AI Engineer on YouTube, July 12, 2026: The AI bugpocalypse is here. Now what? Jack Cable, Corridor. Source ↗
  • OpenSSF on YouTube, December 1, 2025: Driving Policy To Secure the Open Source Ecosystem, Jack Cable. Source ↗
  • Auth0 on YouTube, May 29, 2026: Real-Time Security Guardrails for AI Agents, a Corridor demo. Source ↗
  • NahamSec on YouTube, February 24, 2022: Jack Cable on his background, bug bounty methodology and hacking the US government. Source ↗
  • Jack Cable on X, August 14, 2026: Corridor's research on coding agents tricked into running malware through a support ticket. Source ↗
  • Let's Data Science: Alex Stamos joins Cognition as chief information security officer, September 29, 2026. Source ↗
  • Jack Cable on LinkedIn, October 7, 2026: research with Transluce on rogue agents, covered by The Washington Post. Source ↗
  • Jack Cable on LinkedIn, October 21, 2026: sharing Corridor's introduction of Argos, its first security model. Source ↗
  • Cognition, October 28, 2026: Corridor is joining Cognition, by Jack Cable and Ashwin Ramaswami. Source ↗
  • Cognition on X, October 29, 2026: Cognition is acquiring Corridor. Source ↗
  • Jack Cable on LinkedIn, October 29, 2026: Corridor is joining Cognition. Source ↗
  • Corridor's homepage: Security for Software That Builds Itself. Source ↗
  • Wikipedia: Metasploit, created by H. D. Moore in 2003. Source ↗

Transcript

Automatic transcription. There is no diarization on the tape, so speaker labels were assigned from the content with help from speaker-embedding labels. Names and product names were normalized where the recognizer misheard them (Jon McLachlan, Jack Cable, Corridor, CISA, Hack the Pentagon, Hack the Air Force, Secure by Design, Stanford Internet Observatory, Crossfeed, Ashwin, Alex Stamos, Christina Cacioppo, Vanta, Feross, Socket, Dylan, TruffleHog, Conviction, Sarah Guo, Cursor, Metasploit, MySQL). Bracketed words are best guesses where a syllable was lost. The two sponsor reads are summarized in brackets. Timestamps are the start of each turn to within a couple of seconds.

Read the full transcript 6,394 words

[Sponsor read: YSecurity, the sponsor of the show. Security engineers from Apple, Uber, Microsoft, Robinhood and Brex, rented by the hour with a monthly cap, for SOC 2, ISO and HIPAA. The first eight hours are free at ysecurity.io/startups.]

Jon McLachlan

Hello, everyone, and welcome to another episode of The Security Podcast of Silicon Valley. I'm your host, Jon McLachlan, and I am joined today by a very special guest, Jack Cable, the co-founder and CEO of Corridor, which is an AI-powered secure by design development platform. Welcome to the show, Jack.

Jack Cable

Thanks for having me, Jon. Glad to be here.

Jon McLachlan

So, an AI-powered secure by design development platform. Tell us about that. What is that? That sounds really cool.

Jack Cable

So maybe I'll start by kind of taking a step back and talking about what I was doing right before this. Took a bit of an unconventional path into becoming a founder, and my background is in security research, computer science. I got into security through bug bounty programs, but in short, I kind of cut my teeth through coding, software development, and finding vulnerabilities in production software out there. That eventually led me to an interesting place. I got into government work originally through the Hack the Pentagon bug bounties. So when I was in high school, I won the Hack the Air Force competition and then went to work for the Pentagon after high school, and did a bunch of government work, and that eventually led to me being at CISA for a couple years leading on the Secure by Design initiative. And really, through the course of that, set out to work with companies to get their software to be more secure by design, to be more resilient to common classes of vulnerabilities. But I really saw that the tools today that the companies have are insufficient. As we continue to see these preventable classes of vulnerabilities being exploited by our adversaries, it got me thinking there has to be a better way to actually secure a company's code from the start. That's what we set out to do with Corridor.

Jon McLachlan

Wow, that's incredible. You've been pretty focused on this stuff for a while. Initially, like, doing research, hacking the Pentagon. So you're a hacker.

Jack Cable

Yeah, and it's funny. [Somewhat] accidentally got my way into the world of security. So I started coding in middle school. And then when I was 15, I was building this integration with an API. It was a cryptocurrency website, of all things. And as a curious kid, I entered zero into the transaction amount and noticed that the payment went through, and I thought, huh, that's a little weird. And then I entered negative $1. And to my surprise, that also went through and actually took a dollar from that account. I realized that at that point, right, I had to make a decision. And for me, it was an easy decision. I reported to the company. They had a bug bounty. So I said, hey, I can steal money from people's accounts. They gave me a bounty, and then I really was encouraged from there to start teaching myself more about security, participating in more bug bounties. That's really what kicked off my journey.

Jon McLachlan

I guess the decision that you were grappling with in that moment when you realized, like, you could transact on negative amounts was, like, how many zeros do I add to the next one? Or should I tell them?

Jack Cable

Yeah, exactly. I didn't even really consider the alternative. I think part of what was fortunate for me too was I got into security at a time where really vulnerability disclosure, bug bounties were much more the norm. So I was fortunate that this company, they already were welcoming with open arms. They paid me, I think, $1,000 for that first vulnerability, which at the time, as a 15-year-old, was a lot, still is a lot of money. And really then kind of sparked the interest to say, okay, what else can I do? How else can I help secure companies? And really kind of [test my] skills of doing so.

Jon McLachlan

And I love that you had that natural inclination just to try things, just see what happens here. I guess it's a great, great way to start [a] journey down security.

Jack Cable

Exactly. And that's the fun part about security. And I found too, like, as I was doing the more technical hands-on work, but even through policy work, I think a lot of the interesting part is that in many ways it's the same. It comes down to trying lots of different approaches, seeing what works. Many don't. But often there is a way to have an outsized impact, whether that's with a vulnerability, whether that's through the Secure by Design work, for instance. Started a pledge and got commitments from now over 300 companies, and there's been some good tangible results coming out of that. I think kind of throughout my career, I've really just been focused on seeing, okay, where can I have the greatest impact? And it's been exciting to explore that from the founder side.

Jon McLachlan

Yeah, that's super, that's super interesting. Super exciting. So now, as a founder, you get to embark on a journey, and you're doing the zero to one thing. And, you know, unless you've been under a rock, like, everyone has probably noticed that AI is changing things. It's accelerating things. Maybe it's unclear, you know, in the big picture how it's all going to land, but you have stepped forward with a vision, and you can see AI can help make a more secure future for all of us. And you founded Corridor. Share with us your vision. What did you see there? What sparked that?

Jack Cable

Definitely. A lot of this came out of the Secure by Design work I was doing at CISA as well as the bug bounty days. And I'd say one observation was that we would talk about things like rooting out entire classes of vulnerabilities from your products, with the recognition that at the end of the day, many of the vulnerabilities that we see out there exploited aren't all that complicated. They are preventable. Things like SQL injections, cross-site scriptings, but even vulnerabilities like authorization flaws, where we really ought to be doing more to prevent these at the source. And kind of from taking a look at the existing, say, [static] analysis tools out there, as well as talking to, at this point, hundreds of companies, it became very clear the existing approach just isn't cutting it. And in particular, I think really what this comes down to is adapting to a code base. And if I think about, for instance, when I do a bug bounty or a pen test and I'm kind of researching for vulnerabilities, if I have access to the code, searching through for vulnerabilities, that looks very different than the existing approach these tools are taking, which essentially is just kind of searching through with kind of static, pre-canned templates, because it doesn't actually understand how the code base functions. Our viewpoint is, with AI, with the advances in foundation models, it's now much more possible to have tailored scans that actually take into account that functionality, that says, okay, this is a vulnerability for these reasons. We can see the path by which that's exploitable, or vice versa, this one we really don't need to care about for other reasons. So I think what's really exciting about this, and just as tools like Cursor have brought upon significant room for innovation with software development, I think there's a ton of opportunity to help application security teams not just do their own work, not just better identify vulnerabilities, go through and parse existing security reports, validate them, fix them, but ultimately tying this into the development process, where, for most companies, it's not possible to have a security person go and review every pull request, every piece of code that's coming in. But we can get closer, we can do better now with AI and really augment and increase the work that these security professionals are able to do.

Jon McLachlan

Love it. I wish I could review every pull request, just can't. And you get to a certain size and it's like you don't even know all of the features that are coming in. And you have to kind of depend on other folks to bubble up, like, hey, this maybe touches authentication. Maybe we should do a security review. Anything that we can help that scale problem, especially in startups that have to move fast, have to try things, have to fail quickly, have to move on to the next experiment, to do that in a way where there's the care given to the types of data that the system is handling.

Jack Cable

Exactly, exactly. Yeah, so I think that's a challenge. Part of it, too, is kind of thinking about, okay, the rate at which software development is changing. Right now, developers can ship code many times faster than they were able to before. The amount of code that's getting written or generated is increasing significantly. And I just don't think that the existing security tools are going to be able to keep up with that. And again, really, the thing it comes back to is not getting in the way. If a security tool is going to slow down development, if it's going to reduce the pace at which a developer can work, that's kind of the less time that companies have to get out there and [beat] their competitors. So working towards this future where security can go really hand in hand, where it enables development and doesn't slow things down.

Jon McLachlan

Yeah, you know, I always think of it as a security tool adoption as part of the success of, like, whether or not that tool makes a real difference in your organization. So I love that. I'm with you on all of those points. Corridor, you have a co-founder with you.

Jack Cable

I do. I'm happy to dive into that. So my co-founder is super great. His name is Ashwin. We met together when we were both at Stanford. So we did our undergrad in computer science there. And really, so this must have been about five years ago. We did some work at Stanford, at the Stanford Internet Observatory. And then we went over to CISA, Cybersecurity and Infrastructure Security Agency, in 2020. And we were working on essentially, this was just as the attack surface management tools were starting to come out. We built our own open source attack surface management tool called Crossfeed, and we used that to secure election infrastructure. So we rolled that out to scan all 50 states, every county in the US, to look for vulnerabilities in their internet-facing sites. And through the course of that, we reported hundreds of [high and] critical vulnerabilities to states. So, what was really cool about this, right, was that we had essentially almost built a startup within government. And as you can imagine, there's both the technical angles, but then there's also other bureaucratic elements that you need to work through. So, when we started talking again this year, when we started thinking about, okay, how can we really drive forward secure by design, he was the first person I thought of, because we had done it before. We knew we worked well together. We knew that we could really build something, scale it out. So ultimately, that's really the biggest thing in a co-founder, is someone who you're gonna work well with. And I think in more cases than not, it's really beneficial to have someone who you already have that trust with. Because ultimately it's a many years long commitment. It's probably one of the biggest decisions of your lives. So you want someone who can be there side by side with you.

Jon McLachlan

Yeah, yeah, definitely. You're marrying the person, basically, professional sense, right? You're gonna go through a lot together. There's gonna be, like, very high highs, and there's gonna be very low lows. And that's kinda like the founder's journey. So make sure you trust the person. That's important. Yeah, that's a really nice story of how you met. And so you had to already work together, sort of feel each other out. Are you similar to each other? Are you complement each other? How did you decide who's gonna be CEO?

Jack Cable

Yeah, it was a fun conversation we had, and it's interesting too, right? Because we're both from technical backgrounds. I've done a ton of engineering, and in the early days, we both were building it out. As it turned out, I became the CEO. So nowadays, you know, I still try to code when I can, but a lot more of my time is focused on all the other parts of running a business. I think part of it too is it's been very helpful, especially given that the work that I was doing most recently at CISA, where a lot of what my job is now is in making the case for what we're working on. And we're fortunate to have a ton of supporters along the way, but particularly as we've been bringing companies onto the platform, you know, getting that really valuable feedback. It's thinking, okay, how can we continually be improving our product, but also telling that story? Because I think that's so much of what a company comes down to, is the brand. It's how people perceive you. And you need to generate that [virality] in some sense to make sure that traction is always increasing. So it's been a great journey so far.

Jon McLachlan

Yeah, so far sounds incredible. Did you guys raise money?

Jack Cable

We did. So the approach we took, we did an angel round. And for context, we started this in January of this year. We did an angel round in March from folks like Alex Stamos, Christina Cacioppo, CEO of Vanta, a number of other security founders, Feross from Socket, Dylan from TruffleHog, and a bunch of CISOs as well. And then we followed that up in April with a seed round that was led by Conviction, Sarah Guo. So we're fortunate to be in a point where now we really can focus on the product, we can focus on getting those early customers, making sure people who are using our product are happy. And again, that we can really demonstrate the value we've already shown and continue to build that out. So really continuing to push forward on that.

Jon McLachlan

Awesome. Congratulations. That's tough. That's tough to do. It's tough to raise money. Your plan is to shift a little bit and raise from super happy, amazing customers that are faced with this huge problem of scaling out their secure by design and using AI to accelerate all of that.

Jack Cable

Exactly. Exactly. And I think it's been super instructive as we've brought folks onto the platform. Because, again, really how we've approached this, I think how you need to approach entrepreneurship, is to kind of throw all of your assumptions aside and see what actually works in practice. Because companies are going to have different problems than you originally envisioned. Of course, it's important to keep that kind of long-term vision and still work towards that. But also, it's really about making those micro-adjustments along the way to say, okay, this didn't quite pan out as we thought it would, or they're having actually a different type of problem. Originally, when we set out to start the company, we were very focused just on the problem of fixing vulnerabilities. We thought, okay, if we can fix all the vulnerabilities, then no one will have to worry about anything. But through the course of talking to folks, I'd say a lot of what we realized is that, okay, the problem isn't just fixing flaws, it's knowing which ones to fix. If you have thousands and thousands of vulnerabilities, and by the way, if 90-plus percent of those are false positives, then your biggest problem isn't, once you've identified this is a valid vulnerability, going and fixing it. It's knowing which ones are valid. It's discovering the unknowns. So that's one example, but really along the way, we are hearing different use cases from the companies we're working with. And really, I think it's about prioritizing, figuring out, okay, which of these requests we're getting in are common problems, are going to be things that we can go and scale out to the next 50 or 500 companies.

Jon McLachlan

Yeah, and you mentioned some pretty impressive early investors. Dylan from TruffleHog, he's been on the show before. Mentioned the CEO of Vanta. Are these some of your early adopters as well? Or are they a little bit more partners?

Jack Cable

So they've been super helpful in terms of kind of guiding us, connecting us to early adopters. And we've been fortunate to kick off a number of pilots. And really, I'd say part of that is, yeah, this is my first time as a founder. So it's been a super fun journey just to kind of understand everything that goes into a company, and being able to learn from folks who've done this already is essential. Christina, for instance, from Vanta, I was the first intern at Vanta in 2019, back when there were six people. So got to see...

Jon McLachlan

So you got to work with her, like, one-on-one, basically.

Jack Cable

Exactly. In the very early days. And that was a fantastic experience. So kind of being able to take that and now, of course, given where they are, kind of learn from her, learn from Dylan and from others around the journey, and really how to do something that works, how to do something that scales. Very privileged to have folks like that alongside us.

Jon McLachlan

Love that. No, it's incredible that you had all of those great opportunities and you hit the ground running, meeting just incredible folks and surrounding yourself with just, it's sort of that energy that you find here in Silicon Valley, right? It's the drive or the fire, the passion that pushes everything forward. It's contagious too.

Jack Cable

Exactly.

Jon McLachlan

Yeah, that's good. Really good. So along your journey, what would you say the proudest moment has been so far?

Jack Cable

So I'd say it's been super validating to just kind of see how people interact with the product, where we're discovering vulnerabilities that they previously hadn't known about, that, like, we've heard are kind of on par with what they'd expect to see, for instance, from a human attacker in their bug bounty. So I think that's really the most, in some ways, contagious aspect, is just kind of seeing the joy that people get from using your product. And ultimately, again, it's about how can we actually be creating value out there? Let's face it, there's a lot of AI products, there's a lot of things that say they do something, and, you know, there are kind of promises that are made but not kept. And I think there are many aspects of AI, of LLMs, that can be transformative. We've seen this way with software development, and even ourselves, where we're able to move so much faster, kind of leveraging some of these AI tools. But part of that is kind of recognizing the strengths and weaknesses, not using it as a panacea, but rather kind of taking the benefits and, where necessary, for instance, combining them with more deterministic approaches in order to really build the best products. That's how we've been approaching it.

Jon McLachlan

Yeah. No, I appreciate that. There's balance that's required in all of this movement and all of this movement towards change. And even though the change is happening more quickly, [it's] important to find that balance too. And along those lines of finding, like, appropriate balances, maybe there's a moment that you would describe as your most challenging moment so far?

Jack Cable

I think especially early on, the whole angle with entrepreneurship is proving yourself, and not just yourself, but proving your product, proving that you have something that actually works and solves a real problem. So, and I think especially early on, you know, often we would have conversations and people would say, okay, but how is this different from X tool? Or what is the really unique value that you're adding? But going back to some of what I was saying earlier, right, I think that the biggest thing is just having some humility there. It's knowing that our company is not our current product. Today, that will evolve. It's really people, it's our mindset that makes us unique, makes us different. And the fact that we can adapt, and especially given this age of AI, where every month or two we get a new model that's going to go and outperform all the previous models, you can't tie yourself to any one approach. You have to always be iterating. So I'd say that's really the approach we're taking, is kind of keeping the end goal, the North Star of delivering value, of making something that can discover better vulnerabilities, that can prevent them from happening in the first place, and being kind of open-minded about how we get there, as well as what the kind of unique pain points are we're solving. And ultimately, you can really only get that from kind of talking to people and understanding what their challenges are.

Jon McLachlan

Yeah, no, I appreciate that. If we have this tool, we bring this thing into this world and it's able to identify fresh vulnerabilities, new things that actually matter, bring our attention into those bits and those pieces that are at the moment maybe hidden, maybe a little bit less seen, and we have this extremely powerful tool. And you're a hacker by trade. Have you ever thought about, like, the implications of, okay, this is a tool? Like, a tool inherently is neither good nor bad. It's just a tool. You could use it for both sides, maybe. And then on the good side, the positive side, like, we can improve our software development life cycles. But on the other side, like, we could use this maybe to hack into systems that aren't at the moment being fixed or patched as diligently as we would like. I could see, like, lots of things just accelerating in that space. I'm sure that's not how it's marketed or being approached to market or anything like that. And it's not maybe specific even to Corridor. It's just something that's happening, right? And we have, in some sense, we have to acknowledge, like, this is happening.

Jack Cable

Yeah. Yeah. I mean, and [I'd] say my perspective there is that one, it's looking at the asymmetry that exists today, the fact that attackers already have no trouble finding vulnerabilities in code. There's no shortage of attacks or vulnerabilities that get exploited by ransomware actors or nation states to point to there. So really what it comes down to, and to me, this reminds me of some debates we've had in the infosec community previously around disclosure, around, for instance, dual-use cybersecurity tools, even things like Metasploit, for instance, right? That both can be used to defend systems, but also, yes, can be used for attacks. And really, my perspective there is that it's always better to give defenders more tools. The attackers already have no trouble going, finding, exploiting vulnerabilities. And, right, you need to, for every one vulnerability attackers are exploiting, you need to make sure that 100 others are prevented to avoid them getting in. So I think the more we can do to give defenders the tools to better discover, better prevent vulnerabilities in their code is how we ultimately win here. And again, tying that back to the whole secure by design idea, okay, if defenders can not just find vulnerabilities but learn from their mistakes, look at the common root causes and see how to prevent those from happening in the first place, then we can start to move towards fundamentally more secure software.

Jon McLachlan

Yeah, I couldn't agree more. And because the, quote unquote, the blue teams, or the defenders, are always going to follow the rules much more strictly than the black hats out there. They're breaking all the rules anyway. So you have to, like, level the playing field a little bit by building all of these great, amazing tools, just like Corridor. So when you look into that future, and I'll let you decide how far into the future we'd like to travel here, when you put on your vision and you can see that future, what do you think will be the most challenging problem that the security community faces in that future?

Jack Cable

Maybe it's helpful to kind of think about where software will be in the future, where I think we will move to a point where the vast, vast majority of software isn't written by humans. It's generated by AI, likely with the supervision and help of humans. But we're moving to a future where, again, the velocity is increasing significantly. The amount of code that's out there is also increasing significantly. But let's also ground it, because there's a lot of people who talk about kind of all the unknowns that are supposedly associated with AI. But I think that if kind of history shows anything, it's that the same types of vulnerabilities that we've known about for decades are going to continue to be the vulnerabilities that we deal with unless we dramatically change our approach. And again, these vulnerabilities that, like, I don't know, if you take SQL injections, where we've had parametrized queries in MySQL since 2004, so 21 years now, and yet we still see these SQL injections coming up, despite having been fully preventable for decades. So it is possible to have a future where code is more secure by design. I don't think that will be solved at the model level, because so often security is contextual. It's not about just, like, a piece of code in isolation, but seeing how it interacts with a broader code base, especially when it comes to business logic or authorization issues, which we found that AI can do quite well in understanding how applications actually work. So it's about bringing that contextual security in and preventing vulnerabilities at the early stages. And we're going to have a lot more ability to do this sort of large-scale compute to actually analyze every single piece of code that comes in. So I think really the challenge will be in making sure that this is a kind of proactive approach, rather than contributing and building on the decades of technical debt that we already have. Because if we're only going to, I don't know, 10x, 100x the amount of code out there, I don't think we want a future where that code is riddled with the same exact types of vulnerabilities as we've been struggling with today. So we can get there, but it's going to take real work to do so.

Jon McLachlan

So let's get there. Let's use these models and these new tools to help us get there more quickly, but let's not train on the mistakes of the past only. Like, we can actually use our security know-how and technology, like what you're building there at Corridor, to help build a better future, a more secure future. I love it. I guess that's what success looks like for Corridor.

Jack Cable

I think so. And really, what's cool for me too, right, is that this ties in so closely to the work I was doing at CISA, especially now as we've [seen] CISA, other agencies [be] vocal about risks that we face, not just from ransomware groups, but from nation states like China, Russia, and the fact that if you actually sit down and look at the vulnerabilities they're exploiting, for instance, often it is SQL injections, command injections, memory safety vulnerabilities, things that if we were talking, I don't know, ten years ago, we would think wouldn't be a problem in the future. Likewise, I hope we're not sitting down a decade or two from now and still kind of rehashing these same old types of vulnerability. So I think part of it too is, like, that, I think there often could be a mindset in the security community, in some ways, of defeatism, of saying, okay, well, no system can ever be 100% secure, so as a result, it's hopeless, and we're not going to be able to build kind of more secure software. But I think it's really about kind of raising the cost on adversaries. And yes, we're not going to ever be able to root out every single vulnerability from a piece of software, but I don't think you can say rationally that we're always going to face memory safety vulnerabilities or we're always going to have to deal with SQL injections, because we know how to prevent those, because companies have already been able to do so. Google, for instance, has talked about how they haven't had SQL injections or cross-site scripting vulnerabilities in their products. So I think really it comes down to being optimistic and kind of leveraging what works to root out these known vulnerabilities.

Jon McLachlan

I guess with a certain level of maturity and a certain level of rigor, you can eliminate those legacy vulnerability types, like the SQL injections that you're talking about. But I guess not everyone is a security expert. And when you don't have a security team, you don't have those security processes, and you don't have the policies, and you don't have the technologies in place, it's a little bit harder. But I think what you're suggesting, [correct] me if I'm wrong here, is that with the advent of AI and most code now being generated, or will soon be generated, you know, we can nudge it in a direction that eliminates a lot of that stuff just by using the proper libraries and the proper query structures for SQL, or for whatever it is that you happen to be building, [that] is a more secure pattern. And I know that you're a first-time founder and you're also early in your career. So congratulations on all of the success so far. This is incredible, the pace that you're going. Have you thought about the legacy that you would like to leave?

Jack Cable

Definitely, yeah, something I think about. And I'd say the biggest thing that has steered me throughout my career, whether through bug bounties, whether going to work in government, you know, there's not too many young kid computer science graduates who decide to go into government, but I found that I was really driven by the ability to have an impact, to be able to, for instance, through the work at CISA, affect an entire industry, and hopefully kind of leave us better off from that. So I'd say really that is what I'm driven by. A recognition that it's possible to scale impact beyond just one person. As much as I liked doing the bug bounties, for instance, at a certain point, I also started to feel that, like, hey, there is probably a better way than kind of doing these one-off tests, kind of hands-on with companies. How can I start to, for instance, through policy, scale and reach thousands, tens of thousands of companies? So I'd say really that's what I'm hoping to accomplish, is to look back and say, okay, I actually helped secure the critical software that we all rely on. I'm kind of seeing measurable reduction in the attacks we're facing, knowing that this is leading to a safer future, especially as we continue to become more and more dependent on technology systems, on AI. So that's ultimately what I'm after.

Jon McLachlan

No, it's incredible. I can really see that. And I feel that too, almost in, like, a, I don't want to call it a civic duty, but an undertaking to help make everyone's life a little bit better. Yeah. So thank you. I appreciate that. It's because of the hard work and the dedication and the focus and the drive and the vision of incredibly talented, smart folks focused on these difficult problems that the world does actually get better. So all the gratitude in the world. If we went the other direction, instead of going into the future, if we could go into the past just for a moment, and I'll let you decide how far into the past, but if you had an opportunity to meet your younger self, would you take that opportunity? And if you would, what, [would you] have any advice for yourself?

Jack Cable

So, yeah, I think certainly I would take the opportunity. What I would tell myself is, I think, really to kind of always just follow the direction of your heart. And just to give one example, where when I was 18 or 17, I was deciding, okay, what to do the summer after high school, and had the standard tech internship at a company out in SF, and was weighing that against working at the Pentagon. And of course, I ultimately chose the Pentagon, but there was kind of a lot of time spent deciding, trying to figure out, okay, which of these routes. There is a lot of prestige and value working in Silicon Valley. That's sort of the more conventional route. But I think a lot of it comes down to thinking about orthogonal directions. What is going to be the most unique experience? What sets you apart from everyone else? And what's going to lead to, like, [not] the most money necessarily, or the most prestige, but really the highest potential for impact. And that was what started my interest in policy and working in government, and my life would, I imagine, be very, very different if I had gone to work for that tech company. So I think it ultimately is around taking the more interesting path, and you never know what's going to come out of that.

Jon McLachlan

I love that. Just reinforcing this notion to optimize for the journey, something that you'll get out of the journey. It's always going to be a journey. The question is, like, which part is going to be today? And if I'm listening to the show and I'm curious and I would love to learn more, is there, should I just look up Jack Cable on LinkedIn? Should I look up Corridor?

Jack Cable

Yes, corridor.dev. So, yeah, feel free to check that out. Reach out to me on LinkedIn or any other place you can find me. And yes, always happy to chat. We're in San Francisco, if folks wanted to meet up in person as well.

Jon McLachlan

And I'm sure you'd be very happy to have, like, a security coffee with maybe a couple of security folks that might be interested to learn more...

Jack Cable

Exactly.

Jon McLachlan

...more about your story. You know, we have a lot of entrepreneurs that listen to the show. So this is a little bit of a leading question. Just a pinch. But is there anything out there that just, like, bothers you deeply? And if someone could just, like, own this problem and solve this problem with a new service, you would be very happy to pay some money to have that problem solved, that you just don't have time yourself to, like, sit down and tackle properly, but you wish that someone would do this?

Jack Cable

So I think there's a bunch of areas, and it's interesting kind of seeing, there's some problems that you can only really understand going through them and kind of encountering them yourself. I think that's one of the areas that I've followed most, is kind of just, okay, seeing, kind of having hands-on experience, and, like, that there's, you know, folks who tried to get into spaces where they haven't kind of directly operated. And while that can work, I think often the biggest thing to build is just your own intuition, your own sense of direction, and having been in the seat of your customer yourself. So that's really, I think, what I would encourage people to do, is go explore spaces, really just kind of sit down and immerse yourself, and there's always going to be kind of more problems to solve. And I think especially exciting, kind of in this age of AI, where the barriers to build a product are a lot lower, the kind of range of what you can do with a product, the possibilities are more unbounded, I think that there's kind of no better time to be starting something. Fall in love with a problem. Go experience the pain firsthand.

Jon McLachlan

Okay, no, that's great advice. You know, when you sit down as an entrepreneur and you build a thing and it's the first version of the thing, it's always been my experience that, like, that first version, it's close, but it's not quite there. You gotta revisit the problem, revisit the pain, and listen to the market. Okay, Jack, well, this has been incredible. Thank you so much for sharing your stories, your journey with us. I'm deeply grateful that there are smart people in this world actively thinking about how to make it better, how to make it more secure. In some sense, the security community, we have to stick together. And this has been a great conversation.

Jack Cable

Thanks so much, Jon, for having me. Really enjoyed the chat. Definitely, anyone out there, please feel free to reach out in any of the angles we talked about. Always happy to chat further.

Jon McLachlan

[Boy], this was a super enlightening conversation. Jack Cable, everyone, the co-founder and CEO of Corridor, one of the best up-and-coming AI-based security companies that you could go and check out. Go learn a little bit more. Let's be part of the change. Let's make this world a better place. I'm your host, Jon McLachlan, and I would like to thank all of our listeners for tuning in to another episode of The Security Podcast of Silicon Valley. This is a YSecurity production. Thank you, thank you, thank you again, Jack.

Jack Cable

Thank you.

[Sponsor read: YSecurity. SOC 2 and ISO done right the first time, a referral program for founders who need it, and the first eight hours free at ysecurity.io/startups.]

FAQ

Questions this episode answers

Who is Jack Cable?
Jack Cable is the co-founder and chief executive of Corridor, an AI security company he started in January 2025, and since Cognition acquired Corridor in October 2026, Cognition's head of security products. He was a senior technical advisor at CISA from 2023 to 2025, leading on Secure by Design and open source software security, and before that a TechCongress fellow in the Senate, a security architect at Krebs Stamos Group, an election security technical advisor at CISA and a hacker at the Defense Digital Service. He placed first in Hack the Air Force in 2017 and studied computer science at Stanford.
What is Corridor?
Corridor is an AI security company for AI-native software development, founded in January 2025 by Jack Cable and Ashwin Ramaswami. It gives coding agents codebase-specific security guidance while they work, reviews pull requests in context, and enforces what's safe to ship, a product it calls Agentic Coding Security Management. It raised a $5.4 million seed round led by Conviction and a $25 million Series A led by Felicis, and in October 2026 it joined Cognition to work on Devin Security.
What is CISA's Secure by Design pledge?
It's a voluntary pledge that software makers sign to work, within a year, toward seven goals: more multi-factor authentication, fewer default passwords, reducing entire classes of vulnerability, more installed security patches, a published vulnerability disclosure policy, accurate CVE records, and evidence of intrusions for customers. It launched at RSA Conference in May 2024 with 68 companies. Jack led its development at CISA, and more than 250 companies had signed when he left in January 2025.
What was Jack Cable's first vulnerability?
At 15, while building an integration with a cryptocurrency site's API, he entered zero into the transaction amount, then negative one dollar, and the payment went through and took a dollar from the account. He reported it to the company, which had a bug bounty and paid him about $1,000. In 2017 he named the site as ChangeTip, a Bitcoin tipping service that has since shut down.
Why is SQL injection still a problem in 2025?
Because the fix exists but isn't the default everywhere. Parameterized queries with prepared statements separate SQL code from user input, MySQL has had them since 2004, and CISA and the FBI asked software makers to eliminate SQL injection in March 2024 after the MOVEit breaches. Jack's point is that the class is fully preventable, and companies like Google have nearly eliminated it by making the safe way the default in their frameworks.
Why do security scanners produce so many false positives?
Most static scanners match code against pre-canned templates without understanding what the code base does, so they flag patterns that aren't exploitable in context and miss flaws like broken authorization that depend on what the application is for. Jack estimates that 90-plus percent of findings are often false positives, which makes validating them, before anyone fixes anything, the hardest part of the job.
Should defenders use AI to find vulnerabilities if attackers can too?
Jack's answer is yes. Attackers already have no trouble finding vulnerabilities, so the asymmetry favors giving defenders more tools: for every vulnerability an attacker exploits, defenders need a hundred others prevented. He compares it to earlier debates about vulnerability disclosure and dual-use tools like Metasploit.
Will AI-generated code be less secure?
Jack expects the vast majority of software to be generated by AI, with people supervising, and the risk he sees is scale: ten or a hundred times more code with the same old vulnerabilities. He doesn't think it will be solved at the model level, because security depends on how code interacts with the rest of a code base, so the fix is bringing that context in early and analyzing every change.
Who is Ashwin Ramaswami?
Ashwin Ramaswami is Corridor's co-founder and was its chief technology officer. He met Jack Cable at Stanford, worked with him at the Stanford Internet Observatory and then at CISA, where they built Crossfeed and scanned election infrastructure in all 50 states in 2020. He left CISA in 2023, ran for the Georgia State Senate in 2024, and joined Cognition when it acquired Corridor.
What did Corridor do after this episode?
It launched Agentic Coding Security Management in December 2025, raised a $25 million Series A led by Felicis at a $200 million valuation in March 2026, shipped integrations with Cursor, Codex and Factory, and Jack testified to the House Homeland Security subcommittee on AI security in June 2026. In October 2026 it released Argos, a model that picks codebase-specific security guidance for coding agents, and joined Cognition to work on Devin Security.
Keep reading on the YSecurity blog
Related episodes
New episodes every other Tuesday

Got a story like this one?

We're always looking for practitioners who've been in the room when it mattered.