
Episode 104 of The Security Podcast of Silicon Valley came out on September 22, 2026, with Jon McLachlan hosting. The guest was Yash Kosaraju, Chief Information Security Officer of a16z, the venture capital firm Andreessen Horowitz (Podbean, Apple Podcasts, Spotify, LinkedIn, a16z). The episode is called “Why a16z’s CISO doesn’t trust the approve button.” The video on our YouTube channel is called “104. Why the a16z CISO doesn’t trust the approve button.” Our companion post, The Human in the Loop Is Going Away, covers why approval prompts fail as a control for AI agents and what to limit instead. This page stays with the conversation.
Yash’s case is that the approval prompt in an AI tool is a weak defense, because people stop reading it. The a16z security team works on what each AI tool can reach: which data, how it gets there, and whether it can write back. And the team doesn’t answer a request with a no. It works out the use case and scopes the data to fit.
The line that sums up the conversation came when Jon asked how a CISO handles agents that take instructions from the internet.
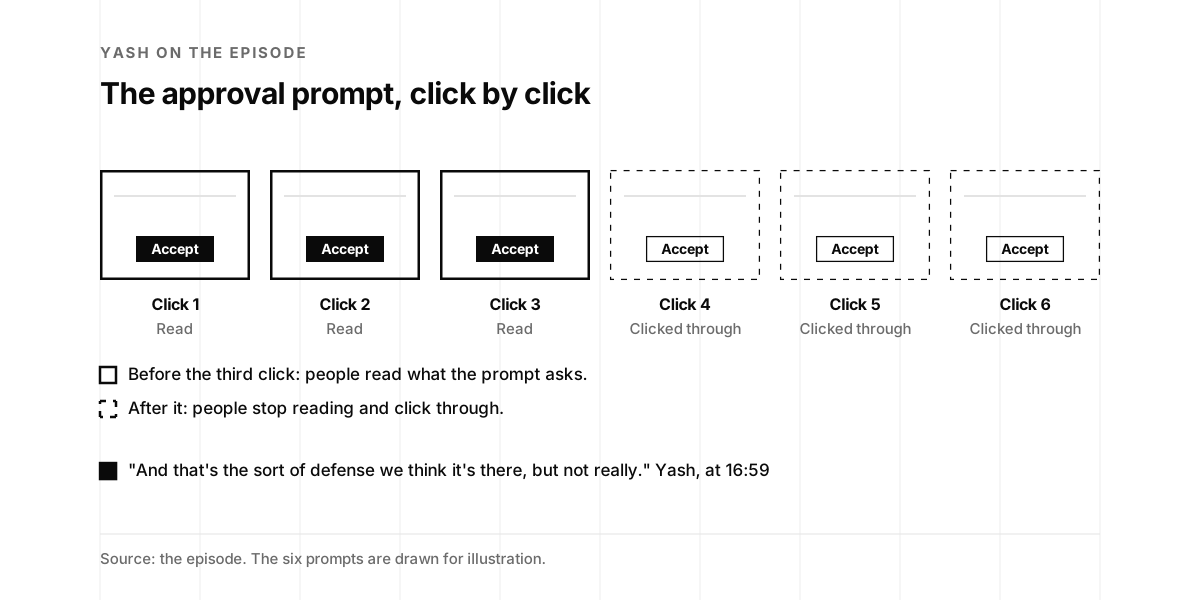
“after the third click, you don’t really read what’s in there and you just start clicking through.”
Yash Kosaraju, at 16:54
This page follows the conversation in order: a section for each part of it, twelve figures, ten clips from the tape, four LinkedIn posts, a post on X, a talk on another podcast, the full transcript, and five tools: a quiz, a scorecard for what your AI tools can reach before anyone clicks approve, a calculator for what the fast mode costs, a timeline, and a to-do list. Where the decodes of the tape disagree on a word, the transcript puts its best guess in brackets, and the page doesn’t quote or retell those words.
Four months at a16z
Jon introduced Yash as the CISO of a16z and listed what the job covers: the corporate environments, the sensitive information, “all of those juicy pitch decks,” and the corporate and cloud security controls. Then Jon asked how long Yash had been there. Technically, four months, Yash said.
“but it feels like about a year.”
Yash Kosaraju, at 2:15
Jon called it startup years. The energy at the firm, in Yash’s words, was high and electric, with everyone excited.
“I get to build on security with all the new technology that’s coming up.”
Yash Kosaraju, at 2:30
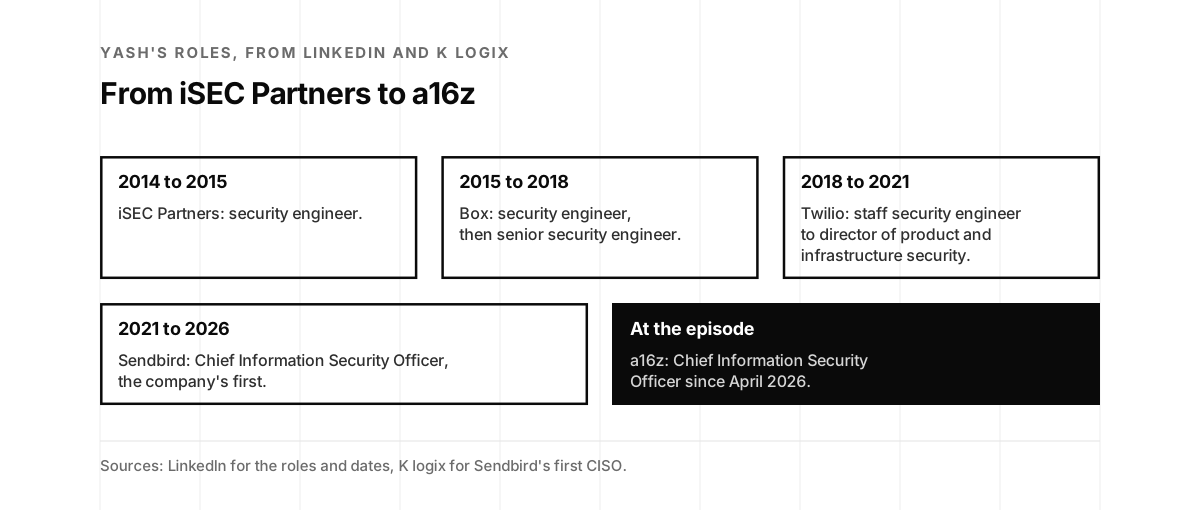
LinkedIn lists Yash as Chief Information Security Officer at Andreessen Horowitz since April 2026. Before that came Sendbird, as CISO from December 2021 to April 2026, Twilio from April 2018 to December 2021, from staff security engineer to director of product and infrastructure security, Box from March 2015 to March 2018, and iSEC Partners from January 2014 (LinkedIn). A 2025 profile by K logix calls Yash Sendbird’s first CISO, hired to build out its security program (K logix).
Wikipedia describes Andreessen Horowitz, also known as a16z, as a venture capital firm founded in 2009 by Marc Andreessen and Ben Horowitz. The 16 counts the letters between the first letter of Andreessen and the last letter of Horowitz (Wikipedia).
In October 2018, while at Twilio, Yash shared Twilio’s post on adding a safe harbor for good-faith researchers to its bug bounty program (X, Twilio). In April 2020, Yash wrote Twilio’s update on the program, which it runs with Bugcrowd (Twilio).
Evolving Our Trusted Bounty Program: Twilio Adds Safe Harbor to Bug Bounty via @twilio
Yashvier Kosaraju (@yashvi3r) · October 30, 2018
Close partners to the portfolio
Jon asked whether the security companies in the a16z portfolio come asking for a test bed. Yash described a partnership.
“we are close partners for our portfolio company.”
Yash Kosaraju, at 2:51
The security team works closely with those companies and could be a customer, an advisor, or help with the right hires and with thinking about the problem the right way.
Founders’ questions range widely, Yash said. Founders who build security products want their product seen the way an enterprise security team would see it. Other portfolio companies ask about hiring a first CISO or a first security hire, or about getting ready for a big customer’s security audit or a compliance audit.
“It’s a long list.”
Yash Kosaraju, at 3:48
The first security hire
Jon asked for the signal that it’s time to hire a CISO, or to make the first security hire. Yash split the question in two.
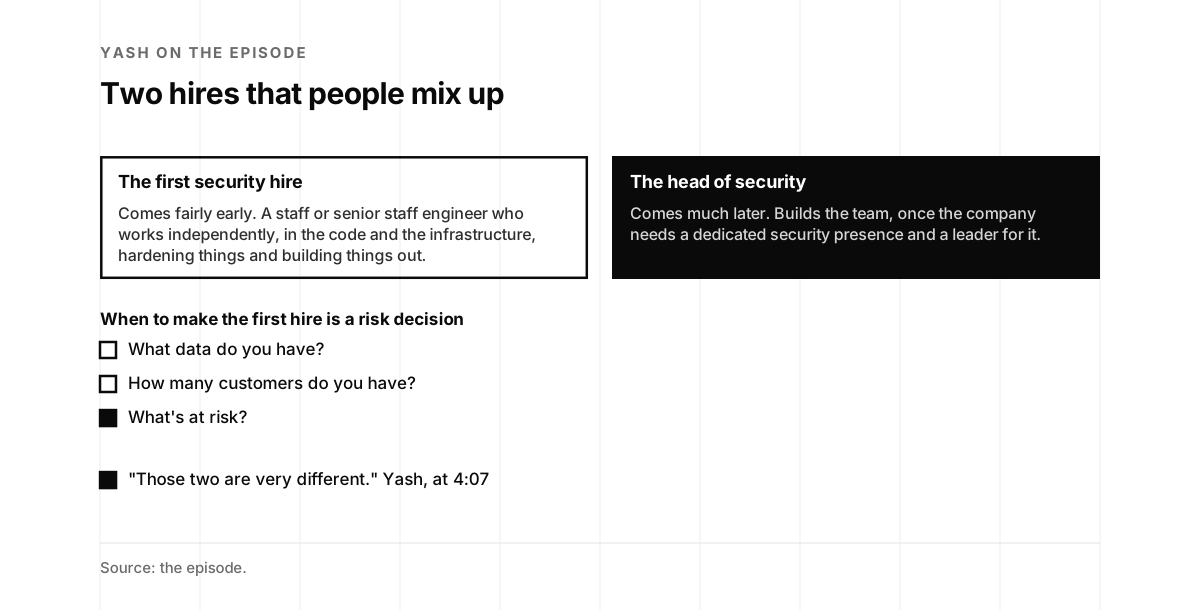
“Those two are very different.”
Yash Kosaraju, at 4:07
The first security hire comes fairly early, and it’s an engineer.
“So when you look at the first security hire, it’s mostly a staff level, senior staff level engineer that can be independent, but isn’t your true head of security person who’s building the team.”
Yash Kosaraju, at 4:11
“This person’s more in the weeds, in the code, in your infrastructure, hardening things, building things out.”
Yash Kosaraju, at 4:24
The timing is a risk decision: what data you have, how many customers you have, and what’s at risk. Where the engineer sits is a decision too. It could be the infrastructure team or another engineering team, wherever the engineer gets enough context and access to execute. The head of security comes much later, once the company needs a dedicated security presence and a leader for it.
Our post In-House, On-Demand, or YOLO? compares the ways a startup can staff security.
When a big buyer asks
Jon asked about tripwires: signals from the sales team or the market that say it’s time for a CISO. Sales gives you those signals, Yash said.
“Some of the bigger clients would definitely ask for one either a call with your security leader or a dedicated point of contact that they can reach out to for emergencies.”
Yash Kosaraju, at 5:39
“And just sort of showing that you have a mature security posture does require somebody with that title.”
Yash Kosaraju, at 5:52
That still isn’t the moment to hire a head of security, because that person builds the team. Yash ties the decision back to what’s at risk and what’s at stake: the data, how much of it you hold, and the access you have into your customers’ environments.
“Ideally, you have a team and maybe a head of security by the time you get to these multi-million, really large-scale deals”
Yash Kosaraju, at 6:20
Those are the deals where buyers start asking for a CISO. From there, the head of security can grow into the CISO role, or a field CISO can answer some of the buyer’s questions.
Where fractional CISOs fit
Jon asked whether a fractional CISO, someone brought in part time, is a common place to start.
“That’s a great resource. You could get either an advisor that you trust or a fractional CISO who can come in and jumpstart your program as well.”
Yash Kosaraju, at 6:52
Wikipedia describes a CISO as the senior executive who sets and maintains the vision, strategy and program that keep an organization’s information assets and technologies protected (Wikipedia). Our post What Is a vCISO? covers the fractional version.
Saturated with vendors
Jon asked about the most exciting security company in the portfolio. Yash didn’t pick one. The companies sit at different levels of maturity, and some take on new problems while others bring a new angle to old ones.
“And it’s always refreshing to see newer, better user-friendly solutions to age-old existing problems.”
Yash Kosaraju, at 7:36
Jon brought up AI, at the top of everyone’s mind, and Black Hat, and all the competition where security meets AI. Yash saw the other side of it.
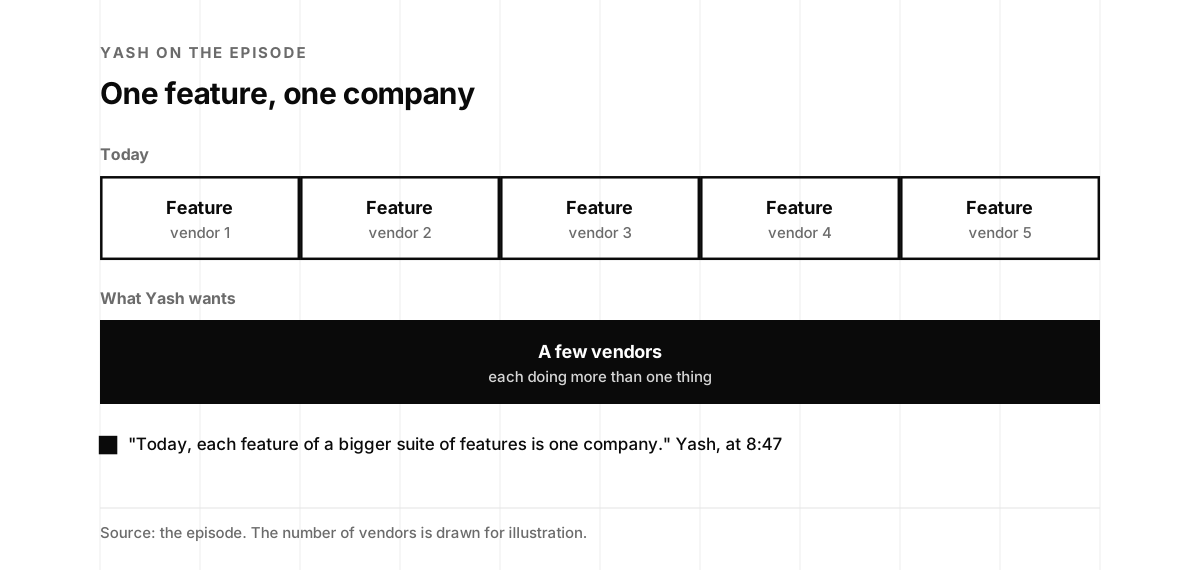
“There are definitely great companies, but on the flip side, what I’m seeing is the security space is saturated with vendors.”
Yash Kosaraju, at 8:29
“Today, each feature of a bigger suite of features is one company.”
Yash Kosaraju, at 8:47
Yash wants consolidation down to a few vendors that each do more than one thing. Jon asked how long that would take. Before AI, Yash said, there was a number to give.
“But now with AI, everything’s accelerated. So it’s all up in the air.”
Yash Kosaraju, at 9:11
On July 28, 2026, Yash asked security vendors on LinkedIn whether “coffee at Black Hat?” outreach had paid off for all its volume, or whether everyone sends it because everyone else does (LinkedIn).
Yash asks security vendors whether "coffee at Black Hat?" outreach pays off.
Yash Kosaraju · July 28, 2026
Code security that goes away
Jon asked which problems the security community will solve first with AI.
“We are taking a stab at multiple problems.”
Yash Kosaraju, at 9:35
The one Yash most wants to see go away completely is code security. Today that means a secure development pipeline with a row of scanning tools in it. With AI writing most of the code, Yash wants the coding agents to make some of those tools unnecessary.
“I’m looking forward to the day where all these coding agents write secure code by default.”
Yash Kosaraju, at 9:58
Assume breach
Jon had been at a small CISO dinner in San Francisco a few weeks earlier, and the mood in the room was bleak. Foundation models can read a code base and the third-party libraries everyone depends on, and start dropping in exploits and zero days. The table’s conclusion was to assume breach.
“Anything exposed to the internet basically is going to break.”
Jon McLachlan, at 11:11
Jon was glad Yash looked at the other side: how defenders use the same tools to fix things.
Catching up, faster
Yash agreed with the people at the dinner.
“They’re not wrong, by the way, right?”
Yash Kosaraju, at 11:39
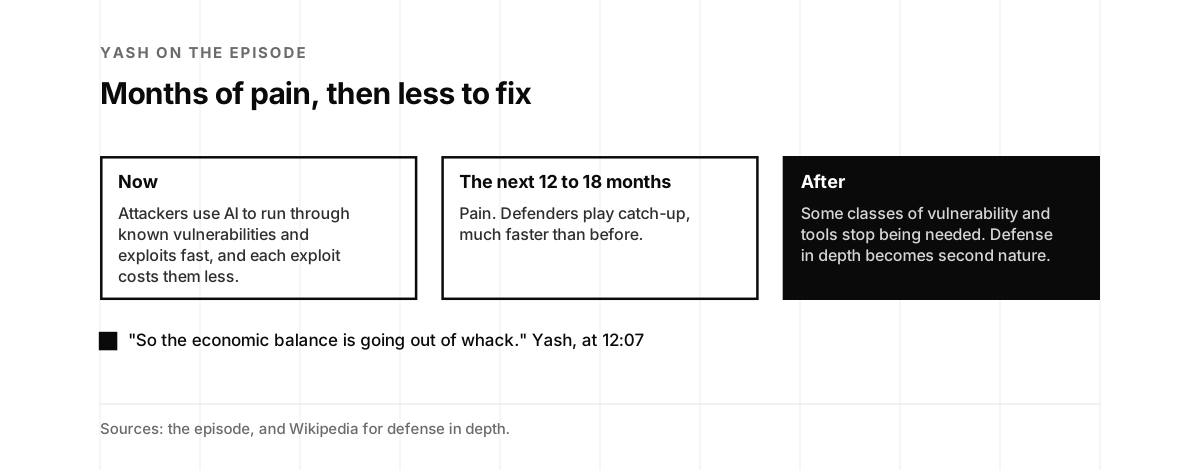
Two things are true at once. AI is good at running through known vulnerabilities and exploits fast enough to overwhelm a defense. And it lowers what each exploit or breach costs an attacker.
“So the economic balance is going out of whack.”
Yash Kosaraju, at 12:07
“However, my hope is that we have this next 12, 18 months of pain where, again, we are playing catch up, but much more rapidly.”
Yash Kosaraju, at 12:10
After that stretch, some classes of vulnerability, and some classes of tools, stop being needed, and building defense in depth becomes second nature.
“And everybody gets there together, screaming and kicking.”
Yash Kosaraju, at 12:38
Wikipedia describes defense in depth as layers of security controls placed throughout a system, to give redundancy when a control fails or a vulnerability is exploited (Wikipedia). The CVEs in Yash’s answer are entries in the Common Vulnerabilities and Exposures system, a reference list of publicly known vulnerabilities (Wikipedia).
Silicon Valley is a bubble
Jon wasn’t sure how much running software foundation models have written so far. Yash agreed there’s a long road ahead for everyone, and named a worry.
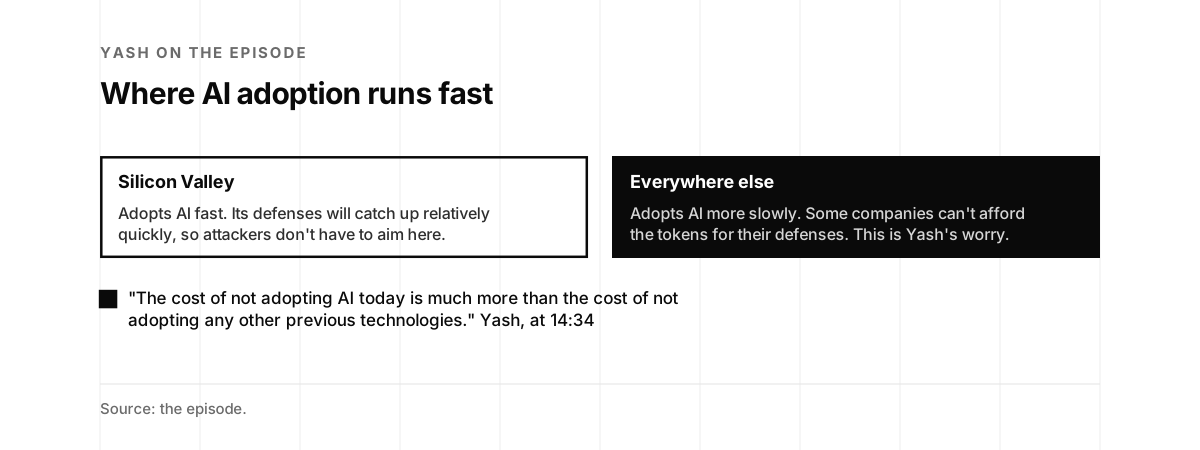
“The thing that worries me, though, is we talk about all of these, but we are here in the Silicon Valley and that is a bubble.”
Yash Kosaraju, at 13:34
“The rate of adoption of AI is very different here than the rest of the US, than the rest of the world.”
Yash Kosaraju, at 13:42
Attackers who ramp up with AI don’t have to aim at the Valley, which will catch up on defense fast. Yash worries about everyone else: companies that haven’t taken up AI, or can’t afford the tokens to build their defenses.
Jon wondered whether new companies would help those late adopters. Yash answered with cost.
“The cost of not adopting AI today is much more than the cost of not adopting any other previous technologies.”
Yash Kosaraju, at 14:34
A layer on top of the cake
Jon described a new layer on the security cake, with AI on top of everything else. A coding agent searches the web, reads about some API, and runs commands on the developer’s machine or in the cloud. It takes instructions from the internet into a prompt that has the developer’s access. Browsers settled this long ago.
“Anything that comes in from the internet, let’s just treat it as untrusted.”
Jon McLachlan, at 15:57
Agents, in Jon’s description, give what comes in mixed levels of trust, and the industry is debating where a human fits in the loop. Jon asked how a CISO at a firm that adopts AI fast handles it.
Wikipedia calls it indirect prompt injection when the attacking prompt sits in outside data, such as a website, an email or a document (Wikipedia).
The third click
Yash started with the state of the field.
“Prompt injection is an unsolved problem.”
Yash Kosaraju, at 16:34
The one defense people count on is the prompt an AI tool shows before it acts, asking you to accept a request or an action. It’s the prompt in the line at the top of this page.
“And that’s the sort of defense we think it’s there, but not really.”
Yash Kosaraju, at 16:59
OWASP’s entry on prompt injection lists both halves of the problem. One mitigation is to “Restrict the model’s access privileges to the minimum necessary for its intended operations.” Another is human approval for high-risk actions (OWASP). Yash’s point is that the approval half wears out.
What the tool can reach
So the a16z team works on access.
“we are adopting AI at a massive pace, but also very deliberately”
Yash Kosaraju, at 17:11
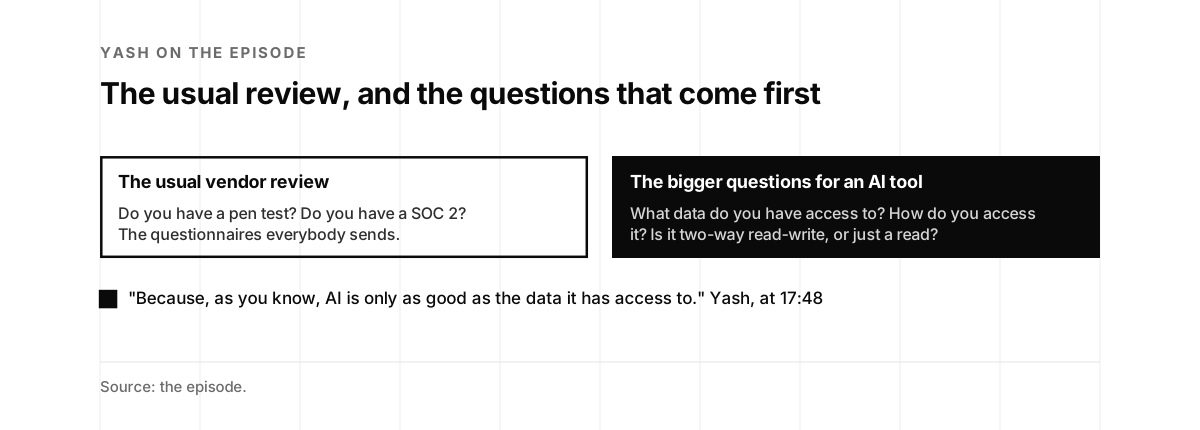
The team looks at the systems each tool can read from and write to, and what it can do. Every company runs vendor due diligence, with its pen test reports and SOC 2 questionnaires. With an AI tool, Yash said, that isn’t the hard part.
“The bigger issue here is: what data do you have access to? How do you access it? And is it a two-way read-write or just a read?”
Yash Kosaraju, at 17:35
“Because, as you know, AI is only as good as the data it has access to.”
Yash Kosaraju, at 17:48
Jon agreed, and summed up the approach: scope what each agent is allowed to touch inside the organization. The principle of least privilege says each part of a system should reach only the information and resources its legitimate purpose needs (Wikipedia). Our post Are You Actually Going to Give the Agent Write Access? takes the write half of Yash’s question further.
A scoped yes
Yash described a rule the cyber team keeps.
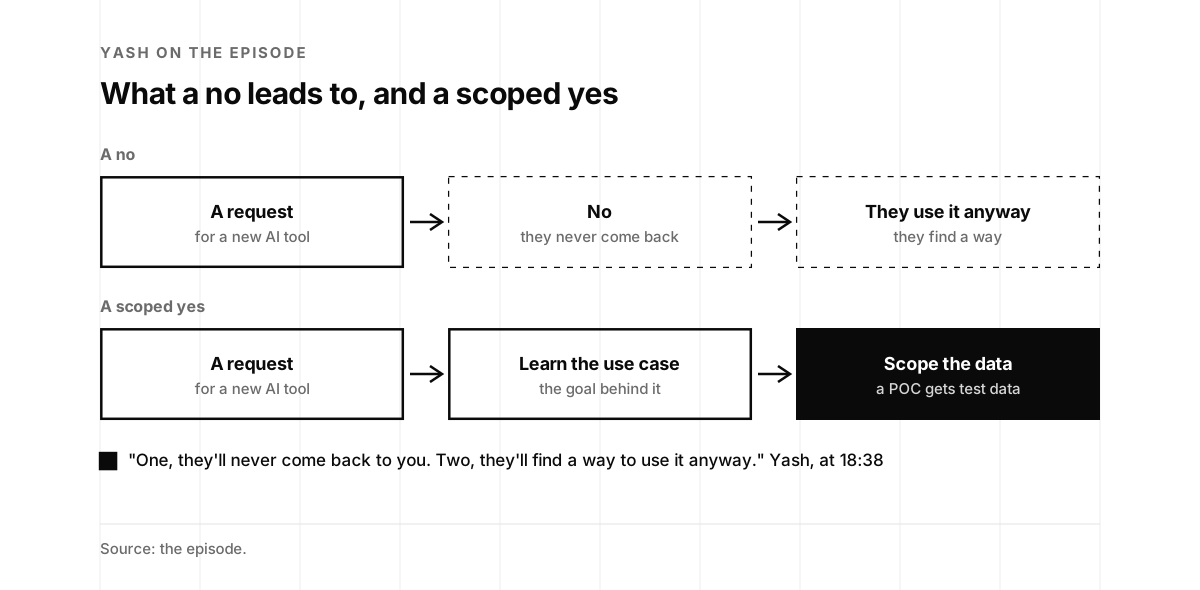
“One thing we are very deliberate about at a16z, especially within the cyber team, is not to say no when people request for something.”
Yash Kosaraju, at 18:28
“One, they’ll never come back to you. Two, they’ll find a way to use it anyway.”
Yash Kosaraju, at 18:38
So the team works with the person, learns what they’re trying to do, and defines access to the right data for that use.
“If it’s a POC, that can have a subset of test data.”
Yash Kosaraju, at 18:51
For anything else, the team works out what data the use needs, and keeps the firm safe. A 2025 profile by K logix had a shorter version: “Security should never be the hammer.” (K logix). Wikipedia calls systems that teams set up outside central IT, to get around its limits, shadow IT, and notes the security and compliance risks they bring (Wikipedia).
In December 2025, as CISO of Sendbird, Yash talked about the same choice on the Cloud Security Podcast, in a chapter called “Security for Platform Engineers: Enabling vs. Blocking” (YouTube).
Two kinds of security people
Jon described two kinds of security people. One walks into a meeting and the room sinks, expecting a no to everything, pushed timelines, and strange requirements for certifications. The other walks into the same room, with the same people, maybe with the same effect on security, and the room is glad.
“Oh, I’m so happy that Yash is here.”
Jon McLachlan, at 19:45
“Culture means so much in the security space, especially if you want to be taken seriously.”
Jon McLachlan, at 20:06
Building people
Jon asked about Yash’s proudest moment.
“that is a deep question, and probably not something I was prepared to answer.”
Yash Kosaraju, at 21:46
The answer has changed over time, Yash said, with one theme running through it.
“I’m more proud of instances where somebody in my team achieves something versus I achieve something.”
Yash Kosaraju, at 21:57
That’s why Yash still likes building teams, building people and growing their careers.
“So when I see somebody who either used to work for me, who’s now a CISO”
Yash Kosaraju, at 22:08
Or someone in a director-level position, Yash went on.
“and they’re doing great things, that makes me proud.”
Yash Kosaraju, at 22:13
In the 2025 K logix profile, Yash’s hiring rule was “I like to hire smart people who want to do the right thing” (K logix).
Not to give back
Jon called that one of the most rewarding parts of giving back to the security community. Yash corrected the framing.
“I’ll be honest. I’m not doing it to give back.”
Yash Kosaraju, at 22:33
“I do it for a very purely personal reason. I am selfish in that sense.”
Yash Kosaraju, at 22:39
Yash had thought it through, asking whether the work was for somebody else, a way of giving back.
“And at some point, I realized, no, this is what helps me get meaning from my life, right? And that is helping others.”
Yash Kosaraju, at 23:14
So the work looks like giving back, and in Yash’s account it starts from a selfish reason. Jon’s answer was that it’s important to know who we are and what we want.
A stint under two months
Jon asked about one of the more challenging moments in Yash’s career. Yash picked a short stint after Box. Some things about the role hadn’t come up in depth during the interviews.
“So when I joined, I quickly realized that is not what I expected.”
Yash Kosaraju, at 24:37
It took a tough and honest conversation with the team there, and Yash left after less than two months. The hard part was the whole process: leaving a team Yash trusted at Box, joining, getting out, and working out what came next. Jon gave credit for not letting it drag on.
Closer to the code
Jon asked about the hardest problem the security community will face in the next five to ten years. Yash shortened the window.
“Five to ten years in the age of AI is probably a question that’s around 20 to 30 years on a normal day.”
Yash Kosaraju, at 25:39
So the question became the next year or so. AI’s skill at exploiting known vulnerabilities is getting security more attention, and that will change how engineering, security and the rest of a company work together.
“So the security teams will have to evolve from what they have been to much more proactive, much more in the weeds.”
Yash Kosaraju, at 26:09
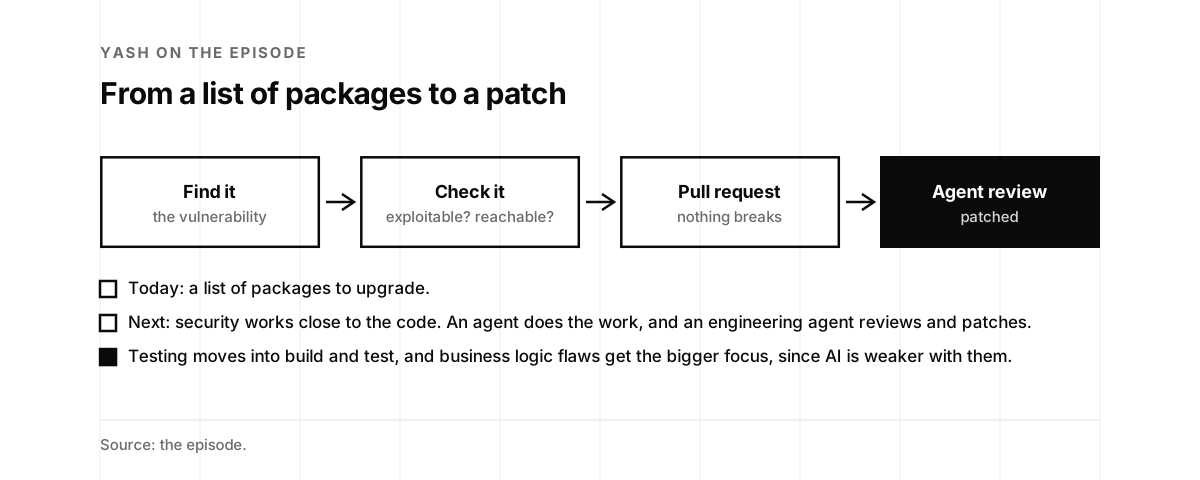
A list of packages to upgrade won’t be enough anymore.
“We’d have to evolve to a much more close to code state where you find them, you figure out if it’s vulnerable, exploitable, reachable, all of those things.”
Yash Kosaraju, at 26:34
Then comes a pull request, a check that it breaks nothing, an agent doing the work, and an engineering agent that reviews and patches. Yash called it a step past DevSecOps. Testing moves too, from the code into the build and test stage, because agents will handle most of the patches.
“a lot of those business logic flaws, which AI isn’t as good as it is with your code”
Yash Kosaraju, at 27:29
That’s where the bigger focus will go, in Yash’s view.
Wikipedia describes DevOps as the integration and automation of software development and IT operations (Wikipedia).
What an AI task costs
Jon turned to cost. A company weighing AI has to make the business case: the return, the expectations, and the token bills. Context decides how well AI works, Jon said, and it drives the cost too.
“My hope, like others, is that the token cost would come down.”
Yash Kosaraju, at 28:36
What Yash sees is that nobody estimates the work well.
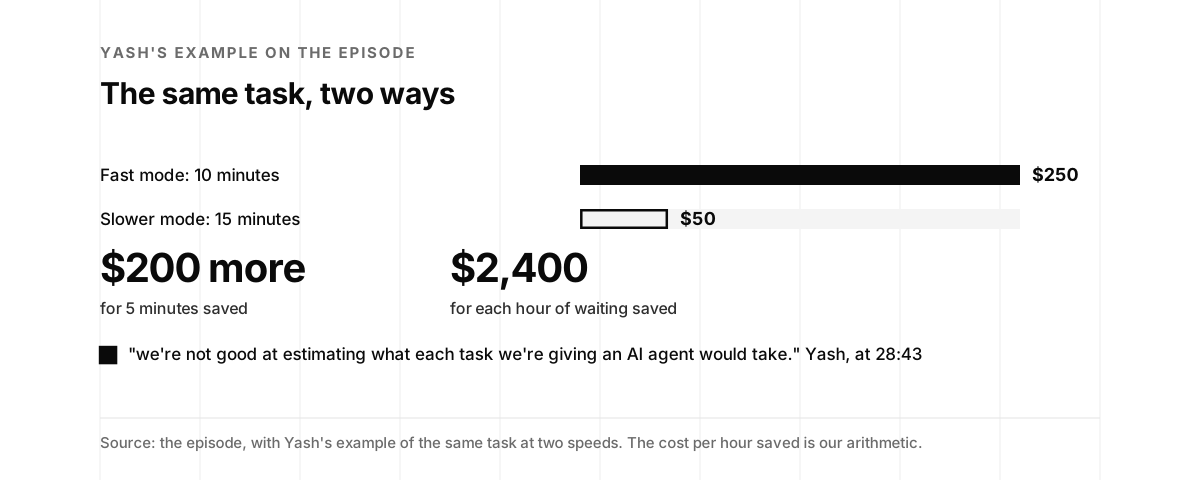
“But on the flip side, what I’m seeing is we’re not good at estimating what each task we’re giving an AI agent would take.”
Yash Kosaraju, at 28:40
“one, they want the latest and greatest model. Two, they want the fast mode and not the slow mode.”
Yash Kosaraju, at 28:53
Yash’s example: the same task can finish in 10 minutes for $250, or take 15 minutes and cost $50. The fix, in Yash’s view, is to get better at estimating what a task takes and what it costs, so a person can decide whether it’s worth the money.
Jon wanted a little dollar sign that shows what a prompt will cost before you click, given your model, your context and everything in the chat.
“You’re buying something. You’re buying some compute.”
Jon McLachlan, at 29:56
Yash didn’t expect the makers of the frontier models to build it, since they have no incentive to. Our post Too Fancy: When Your Agent Costs You $50,000 an Hour to Operate runs the same math at a bigger scale.
A toggle for a cheaper model
Tools with AI built in get expensive too, Yash said, and the fix may come from the tools themselves.
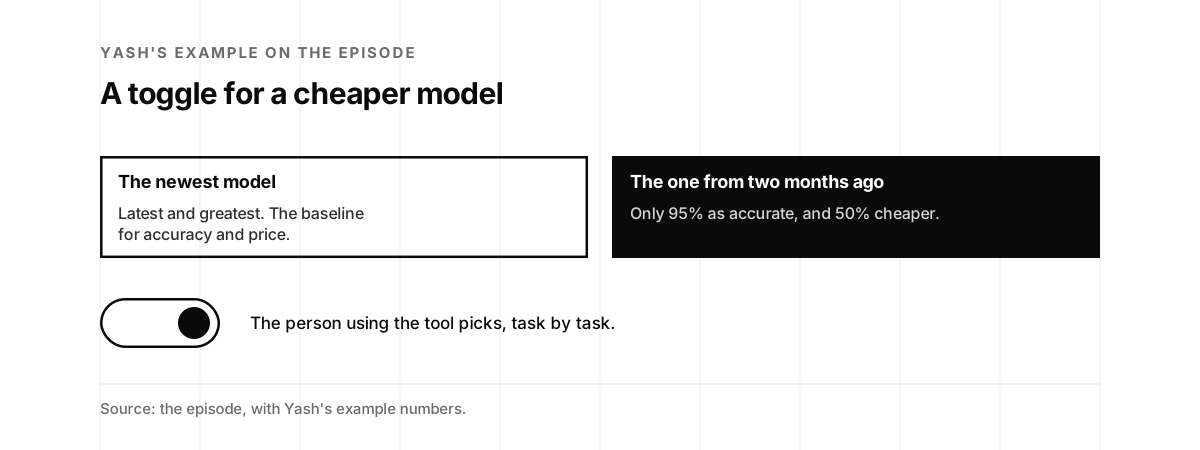
“Maybe the one that came out two months ago is only 95% as accurate, but 50% cheaper.”
Yash Kosaraju, at 31:06
Yash expects tools to give that toggle to the person using them, across frontier models or open weight models the vendor hosts, and costs to come down that way.
Measuring the return
Jon’s view is that problems get solved first by the people who feel the pain. If that’s finance, there’s friction with engineering. Jon asked how Yash keeps the organization under control.
“the whole company is very AI-forward in that sense.”
Yash Kosaraju, at 32:26
“And we have started talking about how do we start measuring ROI? How do we start educating people on what the right model, the right speed is for certain tasks?”
Yash Kosaraju, at 32:30
The goal is a middle ground, where an engineer knows what a task costs and decides whether it’s worth it.
Not token maxing
Jon said the companies that adopt AI most aggressively tend to ask the opposite: why aren’t you using AI more, and could you please spend more.
“But a16z was never that way. We gave people all the tools to experiment, but the mandate was not token maxing or go spend money.”
Yash Kosaraju, at 33:34
“The mandate was: Here’s a bunch of next-generation tools. Try them out, use them, see where they can add value.”
Yash Kosaraju, at 33:43
Yash called it pretty much the same thing, said in different ways.
“And just that change of words gives you a different perspective.”
Yash Kosaraju, at 33:56
On June 11, 2026, Yash posted a role for a staff security automation engineer, to build automation that makes the security team 10x with AI, and added that the job comes with “no token leaderboards” (LinkedIn).
Yash is hiring a staff security automation engineer. No token leaderboards.
Yash Kosaraju · June 11, 2026
No advice for a younger self
Jon asked whether Yash would meet a younger self, and what the advice would be.
“I guess today what I would say is maybe I wouldn’t meet my younger self.”
Yash Kosaraju, at 34:43
“And even if I did, I wouldn’t give any advice because every mistake I’ve made, every decision I’ve taken is what has led me here today.”
Yash Kosaraju, at 34:47
“And changing any of those, even for the better, you don’t know what implications that has.”
Yash Kosaraju, at 34:58
A good time to build
Jon asked for final words for the listeners, many of them founders.
“I am not an entrepreneur, so take this with a grain of salt, but it is a great time to be building.”
Yash Kosaraju, at 35:50
Yash’s advice was to keep at it and work hard, which carries you through the tough times. Then, after the thank-yous, one more thing.
“Oh, I’m also hiring by the way, so please do look at the jobs and apply.”
Yash Kosaraju, at 36:28
Jon pointed listeners to Yash’s team at a16z.
What happened after the tape
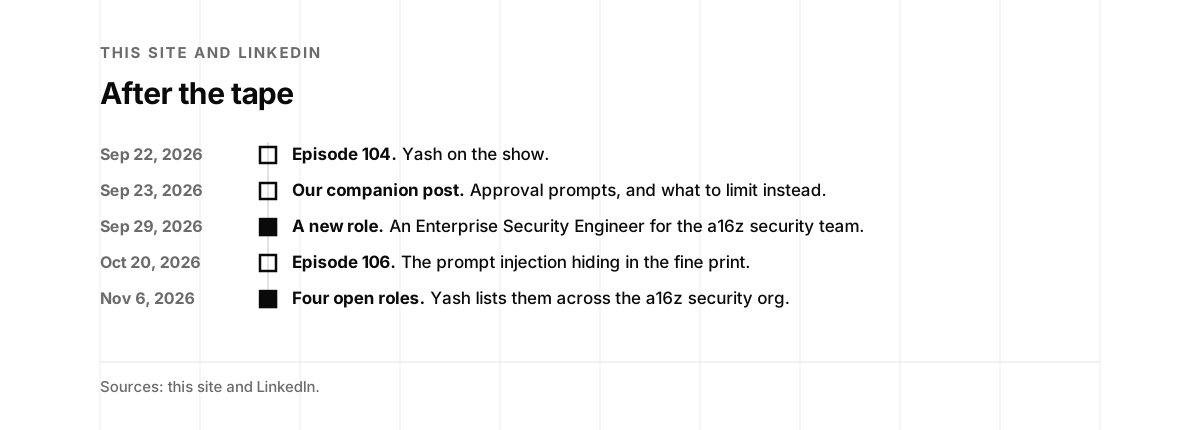
Our companion post came out the next day. The Human in the Loop Is Going Away covers the record on approval prompts, the ways attackers get around them, and what to limit instead, with a scorecard for what your agents can reach.
A new role on the security team. On September 29, 2026, Yash posted an Enterprise Security Engineer role on the a16z security team, owning data protection, SaaS security and data loss prevention, and “making the firm’s fast AI adoption safe” (LinkedIn).
Yash is hiring an Enterprise Security Engineer for the a16z security team.
Yash Kosaraju · September 29, 2026
Four open roles in November. On November 6, 2026, Yash wrote that most companies slow down hiring in November and December, and a16z doesn’t. The post listed four open roles across the security org: a lead engineer for incident response, a staff security engineer for AI and the security platform, a staff engineer for enterprise security, and a staff security technical program manager (LinkedIn).
Yash lists four open roles across the a16z security org.
Yash Kosaraju · November 6, 2026
The same themes on this show. On episode 106, Jesse Anglen of Ruh.ai described the one line of fine print that turns a coding agent against its own keys. On episode 105, Yair Grindlinger of Surf AI made the case for shrinking what a breach can reach. On episode 102, Chris Kirschke of Kyberis AI talked about trusting what feeds your agents, and the one time write access took production down. On episode 101, Johnny Hung and Munam Wasi of Mighty talked about prompt injection becoming a TikTok skill. On episode 100, Xia Hua of Traceforce showed a prompt injection in Playwright’s MCP server.
Did you catch it? A seven-question quiz
Seven questions from the episode. Each answer links the moment in the transcript.
Quiz · seven questions
Did you catch it?
Pick an answer to see whether you caught it.
-
Who should a startup's first security hire be, in Yash's view?
b. "it's mostly a staff level, senior staff level engineer that can be independent" Transcript, 4:14.
-
What did Yash say about the security vendor market?
a. "the security space is saturated with vendors." Transcript, 8:34.
-
Which part of security does Yash most want to see go away?
c. Code security, once coding agents write secure code by default. See Code security that goes away.
-
What happens after the third click on an approval prompt, as Yash put it?
b. "after the third click, you don't really read what's in there and you just start clicking through." Transcript, 16:54.
-
What does Yash call the bigger issue in a review of an AI tool?
a. What data it has access to, how it gets it, and whether it's read-write or read only. See What the tool can reach.
-
What data does a proof of concept get at a16z?
c. "If it's a POC, that can have a subset of test data." Transcript, 18:51.
-
In Yash's example, what can the same AI task cost?
b. $250 in 10 minutes, or $50 in 15. See What an AI task costs.
Before the third click
Eight questions on what your AI tools can reach before anyone clicks approve. The scorecard follows the episode: access, the scoped yes, and cost.
Scorecard · eight questions
Before the third click
Pick the answer that fits today.
-
Do you know which data each AI tool in your company can read?
- No, there's no list
- For some tools
- Yes, written down for every tool
"The bigger issue here is: what data do you have access to?" See What the tool can reach.
-
Which AI tools can write back to your systems?
- We don't know
- We know, and write access is the default
- Write access is granted per use case and reviewed
Yash asks whether a tool's access is read-write or read only. See What the tool can reach.
-
What does your vendor review ask of an AI tool?
- The usual questionnaire and pen test report
- A few questions on data access
- What data it reaches, how, and whether it writes
The pen test and the questionnaire still run. They aren't the hard part with an AI tool. See What the tool can reach.
-
When someone asks for a new AI tool, what happens?
- The answer is usually no
- It waits in a queue
- We work out the use case and scope the data to it
"One, they'll never come back to you. Two, they'll find a way to use it anyway." See A scoped yes.
-
What data does a proof of concept get?
- Production data
- Whatever the team asks for
- A subset of test data
"If it's a POC, that can have a subset of test data." See A scoped yes.
-
How do you treat the approval prompts AI tools show?
- As our main control
- As one control among others
- As a backstop behind access limits we set first
After the third click, people stop reading the prompt. See The third click.
-
Do people know what an AI task will cost before they run it?
- No
- Roughly
- Yes, and they pick the model and speed to fit
The same task can cost $250 in 10 minutes or $50 in 15. See What an AI task costs.
-
Who owns the list of AI tools and their access?
- Nobody
- IT, informally
- A named owner, with a review on a schedule
The a16z team adopts AI fast and decides what each tool can reach. See What the tool can reach.
Start a list of every AI tool, the data it reads, and whether it can write back.
Make write access the exception, and give each proof of concept test data.
Review the list on a schedule, and add what each task costs to the review.
What does the fast mode cost?
The calculator runs Yash’s example from What an AI task costs: the same task can finish faster for more money, or a little slower for less.
Calculator
What does the fast mode cost?
Five numbers: tasks a week, and the cost and minutes of one task in the fast mode and in a slower mode.
At 20 tasks a week, the fast mode costs $4,000 more a week, or $208,000 a year, and saves about 87 hours of waiting a year. That's $2,400 for each hour it saves.
The defaults are Yash's example from the episode, with 20 tasks a week as a placeholder, so put in your own numbers. The calculator counts 52 weeks a year and compares the two modes on price and time only.
From iSEC Partners to a16z
Yash’s path, a16z, the field around it, and this show. Filter by topic.
Timeline
From iSEC Partners to a16z
- The first Black Hat
The conference opens in Las Vegas, right before DEF CON 5 (Wikipedia, on this page).
- Andreessen Horowitz
Marc Andreessen and Ben Horowitz found the venture capital firm (Wikipedia).
- iSEC Partners
Security engineer, until March 2015 (LinkedIn).
- Box
Security engineer, then senior security engineer, until March 2018 (LinkedIn).
- Twilio
Staff security engineer, then manager of product security from March 2019 (LinkedIn).
- A safe harbor for researchers
Twilio adds a safe harbor clause to its bug bounty terms, and Yash shares it on X (Twilio, X).
- The bug bounty, to date
Yash writes Twilio's update on its bug bounty program (Twilio).
- Director at Twilio
Director of product and infrastructure security, until December 2021 (LinkedIn).
- Security Metrics that Count
Harini Rangarajan and Yash on automated security metrics at Twilio (Twilio).
- Sendbird
Chief Information Security Officer, the company's first (LinkedIn, K logix).
- A K logix profile
Yash on working with the business, and why security should never be the hammer (K logix, on this page).
- Cloud Security Podcast
Yash on securing AI agents at Sendbird (YouTube, on this page).
- CISO of a16z
Yash joins Andreessen Horowitz as Chief Information Security Officer (LinkedIn, on this page).
- No token leaderboards
Yash posts a role for a staff security automation engineer (LinkedIn, on this page).
- Coffee at Black Hat?
Yash asks security vendors whether the outreach pays off (LinkedIn, on this page).
- Episode 100
Xia Hua of Traceforce shows a prompt injection in Playwright's MCP server (episode 100).
- Episode 102
Chris Kirschke of Kyberis AI on the one time write access took production down (episode 102).
- This episode
Yash on the show, and our companion post the next day (Podbean, companion post).
- Enterprise Security Engineer
A new role to make the firm's fast AI adoption safe (LinkedIn, on this page).
- Episode 106
Jesse Anglen of Ruh.ai on the prompt injection hiding in the fine print (episode 106).
- Four open roles
Yash lists four open roles across the a16z security org (LinkedIn, on this page).
What to do this week
Five things, in the order of the episode.
- List what each AI tool can reach. For every AI tool in use, write down the data it reads, how it gets there, and whether it can write back, as in What the tool can reach. Our companion post has more on limiting what agents can reach.
- Turn the next no into a scoped yes. Start the next AI tool request as a proof of concept on a subset of test data, as in A scoped yes.
- Put a price on one task. Run one task in the fast mode and in a slower mode, and compare the time and the bill, as in What an AI task costs.
- Score your setup. Run the scorecard and the calculator.
- Get help with it. Our AI access control audits apply least privilege to the AI tools in your company, AI product red teaming attacks your AI product the way real adversaries will, and sales support helps when a big buyer asks for your security leader. If you want to talk it through, book 15 minutes with us.