
Podcast Episode 26

Episode 026 39 min

Andrew Spangler, Head of Security and Compliance at Harness, on Building Trust in Security

with Andrew Spangler · Harness

0:00 / 39:00

Also on Spotify, Apple Podcasts, YouTube, Podbean, Player FM

Episode 26 of The Security Podcast of Silicon Valley, published December 1, 2022. Host Jon McLachlan talks with Andrew Spangler, head of security and compliance at Harness, a software delivery platform. Andrew traces a path from a school help desk and systems administration, where the job after the RSA SecurID breach was rebuilding multi-factor authentication with about 200 new tokens, to security consulting at Rapid7, where a one- or two-week engagement leaves a few hours to build trust, then Puget Sound Energy, NCC Group, Datadog and Harness. They cover common ground as a way into a client's trust, different backgrounds as a source of creativity, handing drudgery to scripts, a ransomware report that pulled a new team together, hiring as priority zero, Log4Shell as the best worst day, the professional pessimist, operational technology built to last 50 to 70 years, people who move on, an interview question about a win, self-healing remediation tied to software bills of materials, and advice to give security a try. About 39 minutes.

Episode notes

In this enriching episode of a YSecurity.io production, Andrew Spangler, the esteemed Head of Security and Compliance at Harness, invites us into the world of security through his experiences, offering a blend of light-hearted banter and profound insights. Andrew's journey in the security field, marked by both humility and vast expertise, serves as the backdrop for a discussion that delves into the core of building trust, leading effectively, and nurturing career growth within the security community.

Andrew shares candidly about the art of building trust—not just within teams but also in the broader context of the organization and its stakeholders. He offers personal anecdotes and strategies for leading teams with integrity, fostering an environment where transparency and accountability are paramount. His approach to interviewing strangers, a task often fraught with challenges, reveals the nuances of establishing rapport and assessing compatibility beyond technical skills.

The conversation also covers the critical aspects of overcoming security challenges and celebrating victories. Andrew emphasizes the importance of acknowledging the hard work and successes of security teams, recognizing that these moments of celebration are crucial for morale and team cohesion. This balanced perspective on addressing challenges and valuing achievements provides listeners with a holistic view of what it means to lead in the ever-evolving landscape of security.

Career development is another key theme of this episode. Andrew offers guidance and encouragement for professionals navigating their paths in the security field, highlighting the importance of continuous learning, mentorship, and community engagement. His reflections on career development are not just advice but a call to action for individuals at all stages of their security careers to pursue growth with purpose and passion.

Tune in to this YSecurity.io production for a conversation with Andrew Spangler that is as engaging as it is enlightening. Whether you're a seasoned security professional, someone just starting out, or simply interested in the human aspects of the security field, this episode offers valuable insights into the dynamics of trust, leadership, and career progression. Join us for a journey into the heart of security, led by one of the most thoughtful voices in the community.

Hosted by Jon McLachlan — co-founder of YSecurity.

The deep dive

Common ground first

Andrew Spangler, head of security and compliance at Harness: from a school help desk to Harness, 200 new tokens after the RSA breach, a couple of hours to win a client's trust, different paths into security, handing the drudgery to scripts, a ransomware report that pulled a new team together, Log4Shell, a utility's 50-year systems, the interview question about a win, and pipelines that fix themselves.

Episode 26 of The Security Podcast of Silicon Valley came out on December 1, 2022, with Jon McLachlan hosting. The guest was Andrew Spangler, head of security and compliance at Harness, a software delivery platform (Podbean, Apple Podcasts, Spotify, LinkedIn, Harness). The episode is called “Andrew Spangler, Head of Security and Compliance at Harness, on Building Trust in Security.”

Trust runs through the whole talk. Andrew builds it with clients in a few hours, with a new team during an incident, and with candidates in an interview. The other thread is automation: hand the repeat work to scripts and pipelines, and spend people on the next problem.

This page follows the conversation in order: a section for each part of it, twelve figures, eight clips from the tape, a post from Andrew’s LinkedIn, the full transcript, and five tools: a quiz, a scorecard for a Log4Shell-sized week, a calculator for repeat work, a timeline, and a to-do list. Where the decodes of the tape disagree on a word, the transcript puts its best guess in brackets, and the page doesn’t quote or retell those words.

From a help desk to Harness

Jon opened by reading Andrew’s path from LinkedIn: education technology at a school district, systems administration, security consulting at Rapid7, security analysis at Puget Sound Energy, NCC Group, Datadog, and Harness. LinkedIn dates the first of those roles to August 2009 and the move to Harness to April 2021 (LinkedIn).

Andrew credited the people: good mentors at every stop, and colleagues generous with what they knew.

“Lots of good people along the way”

Andrew Spangler, at 1:25
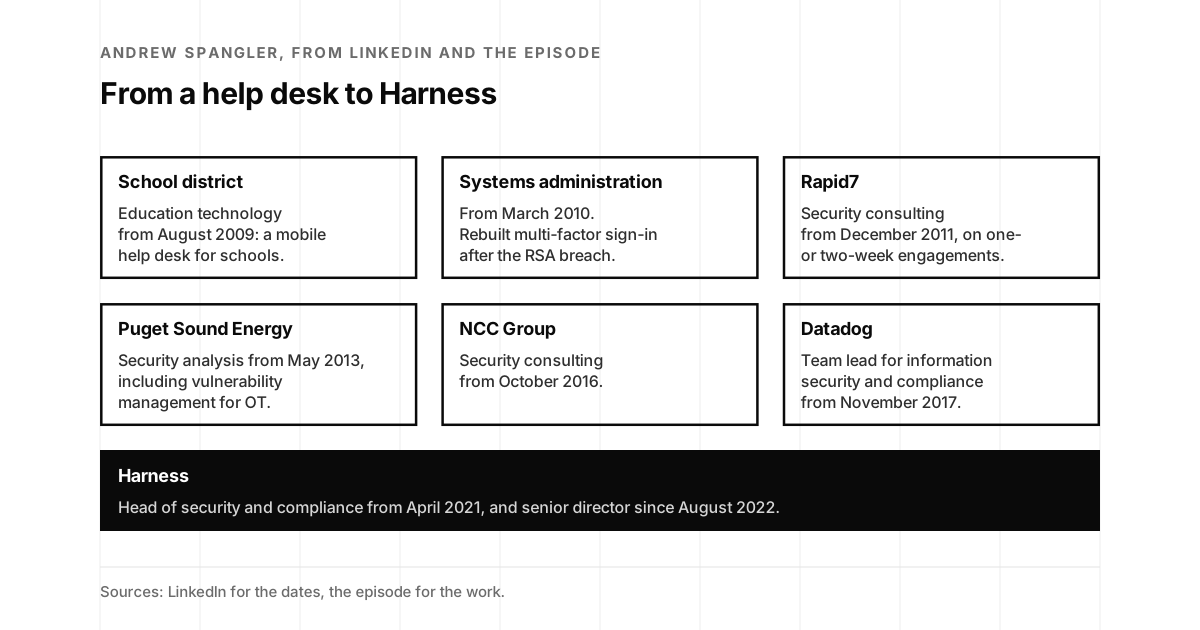
Seven cards. School district: education technology from August 2009, a mobile help desk for schools. Systems administration: from March 2010, rebuilt multi-factor sign-in after the RSA breach. Rapid7: security consulting from December 2011, on one- or two-week engagements. Puget Sound Energy: security analysis from May 2013, including vulnerability management for OT. NCC Group: security consulting from October 2016. Datadog: team lead for information security and compliance from November 2017. Filled, Harness: head of security and compliance from April 2021, and senior director since August 2022.
Andrew's path, from LinkedIn and the episode. Sources: LinkedIn and the episode.

Can I break it? Can I fix it?

Andrew’s first formal job in IT was a mobile help desk for a few elementary schools, and security caught Andrew’s attention there. Part of the pull is the view behind the scenes of infrastructure and applications. Andrew named the urge that many people in the field share: understand how something works, then take it apart.

“Why does it work this way? And can I break it? Can I fix it?”

Andrew Spangler, at 4:13

Two hundred new tokens

The next job was systems administration. One of the big tasks there was rebuilding the company’s multi-factor authentication after the RSA compromise.

Wikipedia tells that story. On March 17, 2011, RSA announced that it had been the victim of “an extremely sophisticated cyber attack.” The attackers sent phishing emails to two small groups of RSA employees, with an Excel file that exploited a flaw in Adobe Flash, then used the Poison Ivy remote access tool to take over machines and reach servers on RSA’s network. On June 6, 2011, RSA offered token replacements or free security monitoring to its more than 30,000 SecurID customers (Wikipedia).

Jon asked whether the company swapped RSA out. It didn’t: the old RSA tokens came out, and new RSA tokens went in. The vendor’s message, in Andrew’s paraphrase: the root credentials were compromised, they would be rotated, and new fobs and hardware were on the way. Andrew’s job was to decommission the old setup, then spin up, configure and deploy the new keys.

“probably right around 200 tokens that I was able to walk through the process of reprovisioning.”

Andrew Spangler, at 5:21

The work earned more trust.

“my boss started to trust me with a little more firewall administration”

Andrew Spangler, at 5:28
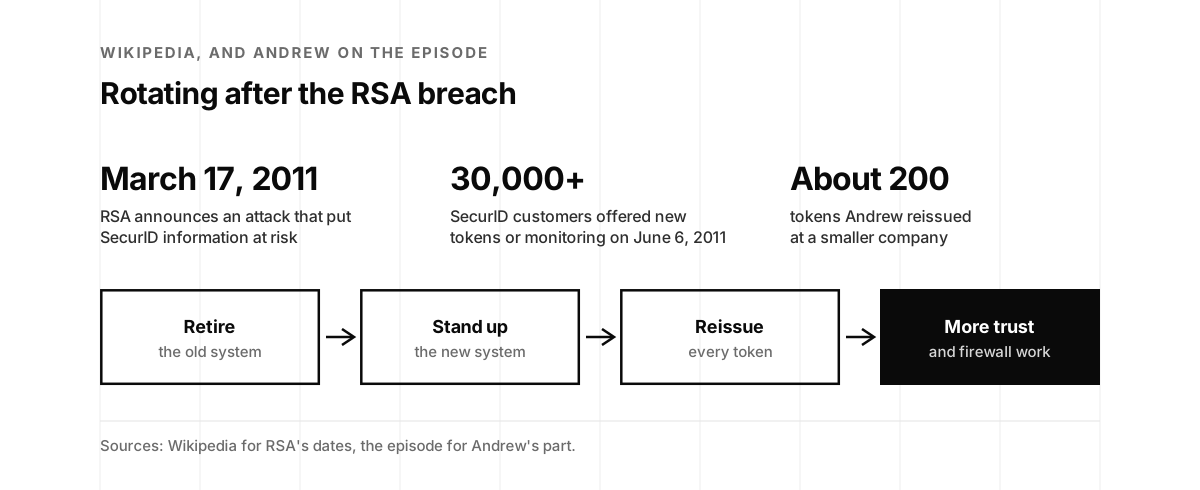
Three numbers. March 17, 2011: RSA announces an attack that put SecurID information at risk. 30,000 plus: SecurID customers offered new tokens or monitoring on June 6, 2011. About 200: tokens Andrew reissued at a smaller company. Below, four boxes joined by arrows: retire the old system, stand up the new system, reissue every token, and, filled, more trust and firewall work.
The 2011 RSA breach and the rotation Andrew ran. Sources: Wikipedia and the episode.

The magic word

Jon caught the word in that story.

“it all comes back to trust”

Jon McLachlan, at 5:55

Jon called trust the cornerstone of security: something between people, and between people and what they expect from systems.
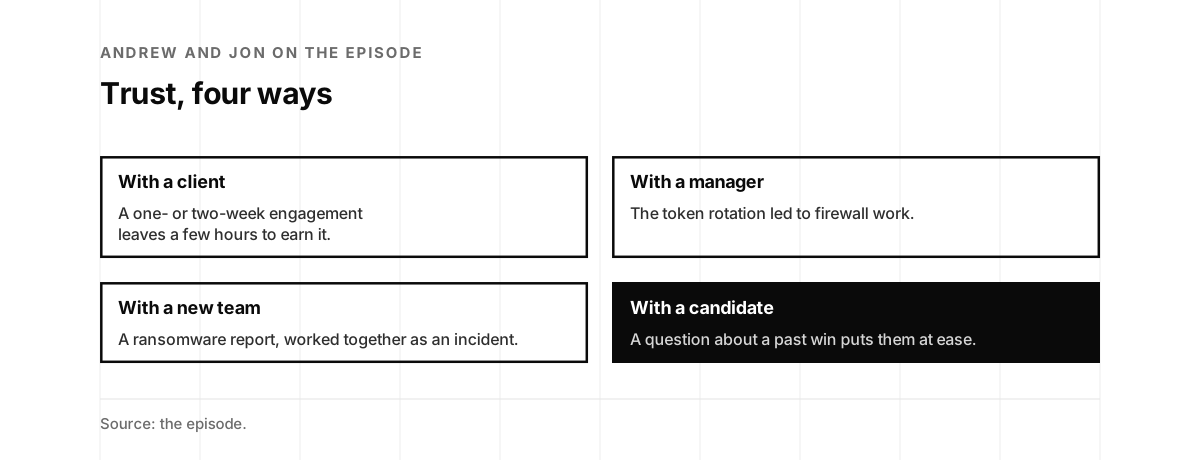
Four cards. With a client: a one- or two-week engagement leaves a few hours to earn it. With a manager: the token rotation led to firewall work. With a new team: a ransomware report, worked together as an incident. Filled, with a candidate: a question about a past win puts them at ease.
Where trust came up in the episode. Source: the episode.

A couple of hours to build trust

A friend put Andrew in touch with someone who had recently started at Rapid7, then a pre-IPO company Andrew didn’t know. The job was security consulting in professional services: helping customers build vulnerability management programs, plus advisory work. Wikipedia notes that Rapid7, a Boston-based security company, acquired the Metasploit Project on October 21, 2009 (Wikipedia).

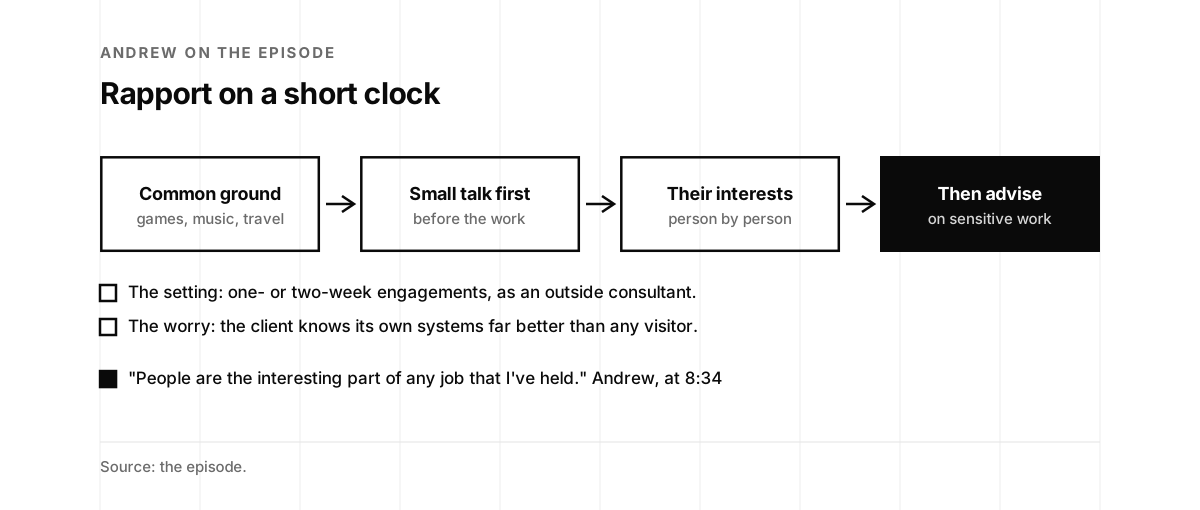
The engagements lasted one or two weeks, and the consultant came in from outside to advise on sensitive processes. By Andrew’s estimate, that left a couple of hours to build rapport and trust.

Jon asked for a favorite technique. Andrew called it what helps a person feel comfortable: finding common ground, such as video games, music, travel, camping or hiking in the desert. Andrew also worried, as a consultant, that the client knew far more about their own systems, and that the consultant would only be in the way. So Andrew spent a little time up front on casual conversation, to learn what interested each person, in the server room or the meeting room.

“People are the interesting part of any job that I’ve held.”

Andrew Spangler, at 8:34
Listen · Andrew Spangler on episode 26, from 6:47
About 20 seconds: Andrew on a couple of hours to build trust as an outside consultant. The clip stops on its own. Read the full transcript.
Four boxes joined by arrows. Common ground, such as games, music and travel. Small talk first, before the work. Their interests, person by person. Filled, then advise on sensitive work. Below: the setting is one- or two-week engagements as an outside consultant, and the worry is that the client knows its own systems far better than any visitor. Quote: "People are the interesting part of any job that I've held."
Andrew's way into a short engagement. Source: the episode.

Different paths, stronger teams

Jon answered the story of Andrew’s route into tech with a point about paths.

“I think that everyone takes a different path”

Jon McLachlan, at 11:08

Those differences, Jon said, make life interesting and make teams stronger than the sum of their individual parts. Andrew agreed, and called it one of the best things about security: the field has been a good avenue for people with all kinds of backgrounds. Some of the best professionals Andrew has worked with came from the liberal arts or had no formal training, alongside plenty of excellence from STEM.

“I love the diversity in backgrounds and the different perspectives”

Andrew Spangler, at 12:09

For Jon, that’s where creativity comes from: differences, more than similarities. Similarities help build trust early. Seeing the world a little differently is where new ideas start. Jon recommended Seeing What Others Don’t, Gary Klein’s 2013 book of case studies on how people gain insights (Wikipedia). Andrew added it to a Goodreads list. The page for episode 16 covers the same book.

Tools for people who build tools

Jon asked what Harness does. Andrew described a software delivery platform: CI and CD, plus modules that work with the platform or on their own, such as feature flags, and security testing orchestration for the software pipelines.

Two things drew Andrew in. One was the leadership team. Harness’s founder, Jyoti Bansal, had founded AppDynamics, which Cisco bought for $3.7 billion in 2017 (Wikipedia, Wikipedia). The other was the space. For years, Andrew had suspected that much of the work Andrew did would someday be automated, and now platforms like Harness do it. Andrew likes industries that

“build tools for people that build tools”

Andrew Spangler, at 14:46

Hand the drudgery to scripts

Jon saw automation as the next step, with layoffs in the news and teams asked to do more with less. Some people fear automation for their jobs. Jon’s view is the opposite: script everything Jon does in a day, and move on to the next layer of problems.

Andrew had felt that fear too: would the work Andrew was good at matter in five or ten years? Time in the seat, and at cloud-native companies like Datadog and Harness, showed Andrew that automation frees people up for more interesting problems.

“It’s less drudgery, it’s less spreadsheets, it’s less manual deployments”

Andrew Spangler, at 16:16

“Let’s let the robots do the drudgery, and we can focus on what comes next.”

Andrew Spangler, at 16:29

Jon pictured a future as a grumpy old man telling a young person about the old days.

“when I was your age, we had this thing called spreadsheets.”

Jon McLachlan, at 16:48

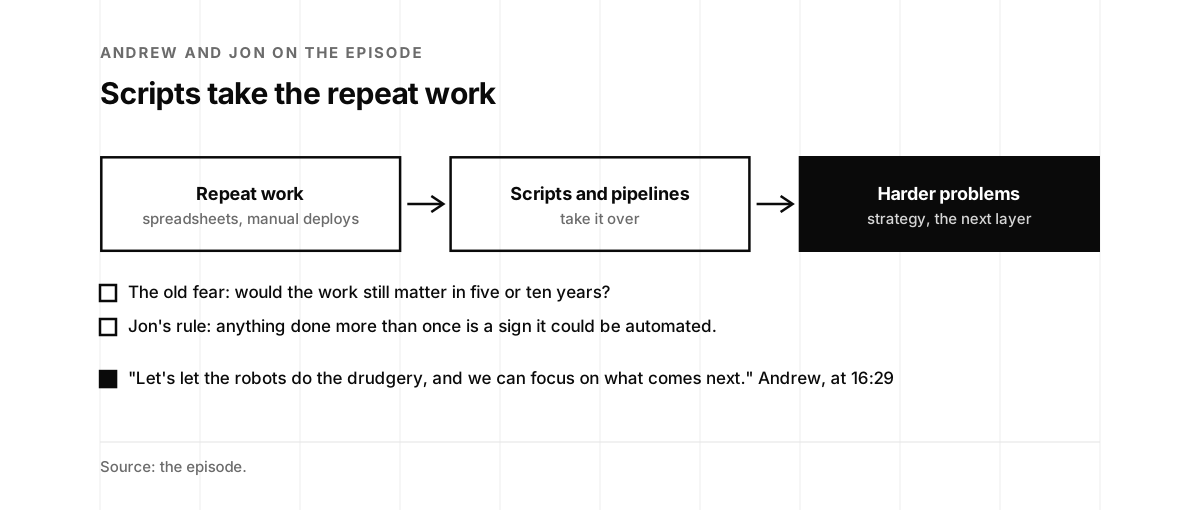
Jon’s own rule: anything done more than once is a sign that it could be automated.
Listen · Andrew Spangler on episode 26, from 16:00
About 35 seconds: Andrew on what automation frees people to do. The clip stops on its own. Read the full transcript.
Three boxes joined by arrows. Repeat work, such as spreadsheets and manual deploys. Scripts and pipelines take it over. Filled, harder problems, such as strategy and the next layer. Below: the old fear was whether the work would still matter in five or ten years, and Jon's rule is that anything done more than once is a sign it could be automated. Quote: "Let's let the robots do the drudgery, and we can focus on what comes next."
Repeat work in, time for harder problems out. Source: the episode.

A minor crisis that pulled a team together

Jon asked about Andrew’s best day at Harness. The first came within about 60 days. Andrew had inherited a team of two engineers at a globally distributed, remote-first company. A report came in that a software engineer’s laptop had been compromised by ransomware. Nothing reached the cloud environments or production, but the team wanted to stop any further spread, so they treated it as an incident.

Wikipedia defines ransomware as malware that holds a victim’s data hostage until a ransom is paid, through encryption, theft with a threat to publish, or both (Wikipedia).

Working the incident built confidence on the team, and Andrew tied it back to trust.

“going through sort of a minor crisis together really has a way of gelling a team.”

Andrew Spangler, at 19:05

Listen · Andrew Spangler on episode 26, from 18:38
About 30 seconds: Andrew on a ransomware report in the first 60 days at Harness. The clip stops on its own. Read the full transcript.

Priority zero

The second best day was about hiring. The people Andrew works with, and works for, have always been what Andrew calls “priority zero.” Hard workers who give everything can still fall short without a good team around them. Building the security team out from two people has been rewarding, Andrew said, with hires who are competent, work hard and catch the vision.
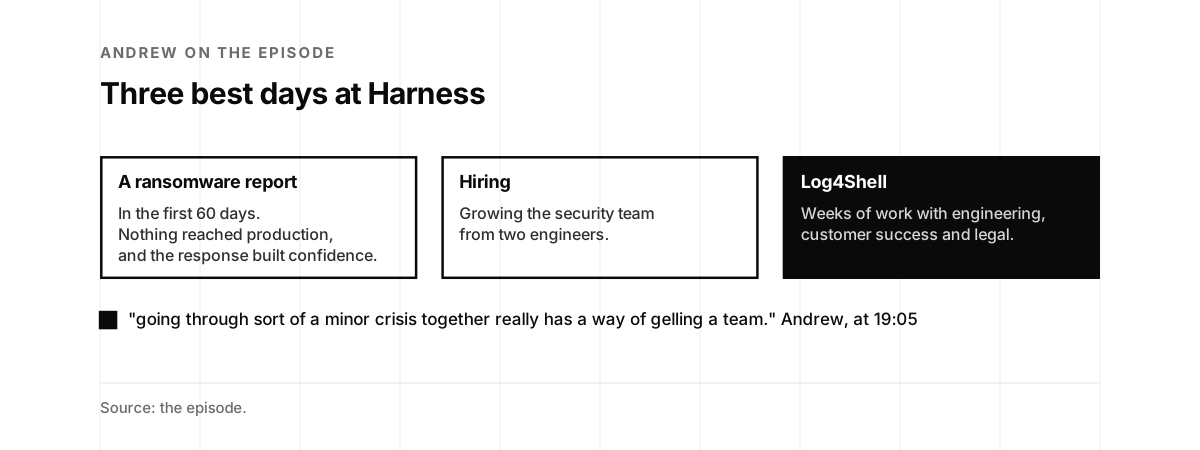
Three cards. A ransomware report: in the first 60 days, nothing reached production, and the response built confidence. Hiring: growing the security team from two engineers. Filled, Log4Shell: weeks of work with engineering, customer success and legal. Quote: "going through sort of a minor crisis together really has a way of gelling a team."
Andrew's three best days at Harness. Source: the episode.

The best worst day

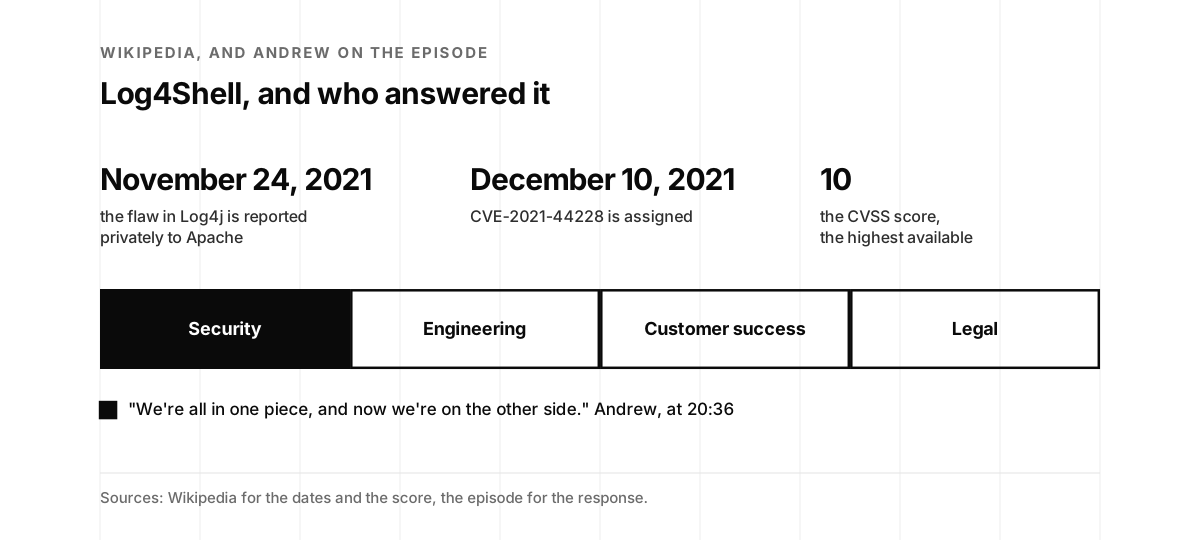
The third was what Andrew called the best worst day: Log4Shell. Wikipedia describes it as CVE-2021-44228, a flaw in the popular Java logging library Log4j that allowed arbitrary code execution. It was privately reported to the Apache Software Foundation on November 24, 2021, got its CVE identifier on December 10, 2021, and received a CVSS score of 10, the highest available (Wikipedia).

At Harness, the response reached well past security. Engineering, customer success and legal all joined in, calm and collected but urgent, over an incident that kept changing for several weeks.

“We’re all in one piece, and now we’re on the other side.”

Andrew Spangler, at 20:36
Listen · Andrew Spangler on episode 26, from 20:08
About 30 seconds: Andrew on Log4Shell, the best worst day. The clip stops on its own. Read the full transcript.
Three numbers. November 24, 2021: the flaw in Log4j is reported privately to Apache. December 10, 2021: CVE-2021-44228 is assigned. 10: the CVSS score, the highest available. Below, four joined boxes for the teams in Harness's response: security, filled, then engineering, customer success and legal. Quote: "We're all in one piece, and now we're on the other side."
Log4Shell's dates, and who joined the response at Harness. Sources: Wikipedia and the episode.

A professional pessimist

Jon noticed that two of Andrew’s three best days were incidents. Both of them, Jon said, look for the good that will come out of whatever is going on.

“as a security professional, you’re kind of a professional pessimist”

Andrew Spangler, at 21:19

Security people ask the tough questions, so it gets easier to see what’s wrong. Andrew’s counterweight is perspective: look at the moment, back at the past and ahead to the future, and see that even when things feel chaotic, it’s going to be okay.

“This is not the worst thing that’s happened.”

Andrew Spangler, at 21:59

Listen · Andrew Spangler on episode 26, from 21:13
About 25 seconds: Andrew on being a professional pessimist by design. The clip stops on its own. Read the full transcript.

Jon agreed about perspective. Software that flies airplanes or doses chemotherapy puts lives on the line, and most CI/CD systems don’t.

Keeping the lights on

That brought Andrew back to Puget Sound Energy. Wikipedia describes it as a Washington utility that provides electric power and natural gas to the Puget Sound region, with more than 1.24 million electric customers (Wikipedia). Andrew’s role included vulnerability management for operational technology. It took Andrew into the field, to generation facilities and substations.

Wikipedia defines operational technology as hardware and software that detects or causes a change through direct monitoring and control of industrial equipment, sometimes called IT in the non-carpeted areas (Wikipedia). Andrew worked with professional engineers on the security of components of the bulk electric system. NERC, the regulator for North American grid reliability, describes its mission as reducing risks to the reliability and security of the grid (Wikipedia).

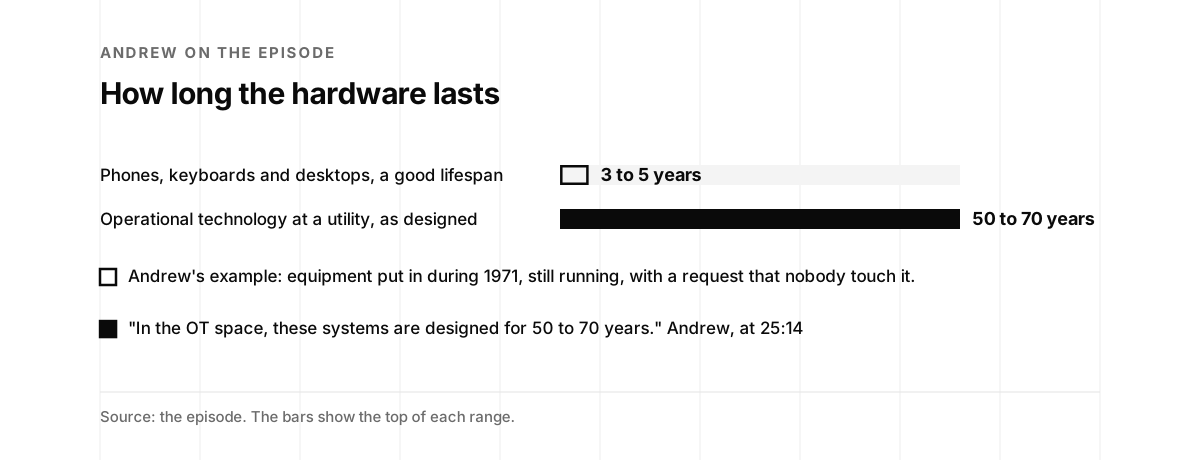
What stood out was time. Phones, keyboards and desktop computers have a good lifespan of three to five years.

“In the OT space, these systems are designed for 50 to 70 years.”

Andrew Spangler, at 25:14

Andrew described walking into a substation and hearing that the equipment went in in 1971, still runs, and shouldn’t be touched. Andrew came away with deep respect for the people who keep the lights on and keep the drips in hospitals moving.
Listen · Andrew Spangler on episode 26, from 24:50
About 40 seconds: Andrew on equipment built to last 50 to 70 years. The clip stops on its own. Read the full transcript.
Two bars. Phones, keyboards and desktops, a good lifespan: 3 to 5 years, a short outlined bar. Operational technology at a utility, as designed: 50 to 70 years, a long filled bar. Below: Andrew's example was equipment put in during 1971, still running, with a request that nobody touch it. Quote: "In the OT space, these systems are designed for 50 to 70 years."
How long the hardware lasts, phones and desktops next to OT. Source: the episode.

Jon tries to keep a phone for six years. Andrew teased Jon about the single camera on the back of the old one, and Jon reported an upgrade.

Twenty whys

Jon named a growth mindset. Andrew traced it to curiosity, the kind that asks why about an answer, then keeps asking.

“there’s 20 whys afterwards”

Andrew Spangler, at 26:53

Andrew finds that same shared curiosity in the people Andrew connects with most in the industry. Jon often says that in a world without computers, Jon would probably have been a philosopher. Jon’s advice: ask why over and over, down to the core values in play, then compare them with your own. From a different view of the world, some problems stop looking like problems.

“Sometimes they look like features.”

Jon McLachlan, at 28:19

When people move on

Jon asked about the worst day. Andrew’s answer was people leaving the team for their next adventure. Even when the move is good for them, it’s bittersweet. And on a small team at a fast startup, 40 or 50 hours of work a week suddenly need a new home.

The saving grace, Andrew said, is the team: good people with different backgrounds, curiosity and an eagerness to learn.

Jon started as an engineer and moved into leadership. One of the most rewarding parts of that shift is helping people take their careers to the next level, at the same company or a different one.

“my loyalty is connected to people.”

Jon McLachlan, at 31:24

When growth can’t happen inside the company, Jon still helps, with options from Jon’s network. Watching people grow into leaders is the reward. Andrew agreed. Seeing people succeed, and helping with mentorship and insight along the way, has been the best part of Andrew’s last five or six years.
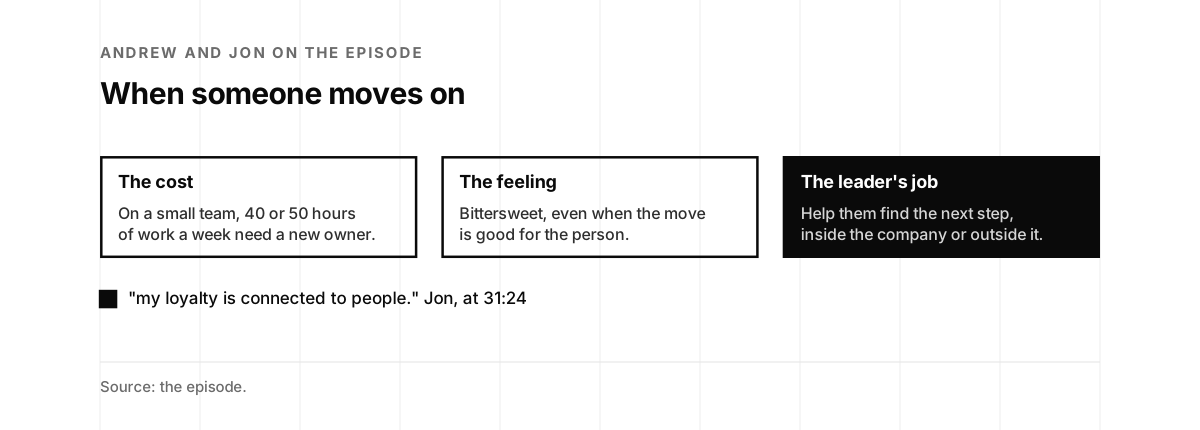
Three cards. The cost: on a small team, 40 or 50 hours of work a week need a new owner. The feeling: bittersweet, even when the move is good for the person. Filled, the leader's job: help them find the next step, inside the company or outside it. Quote from Jon: "my loyalty is connected to people."
What a departure costs a small team, and what a leader can still do. Source: the episode.

Tell me about a win

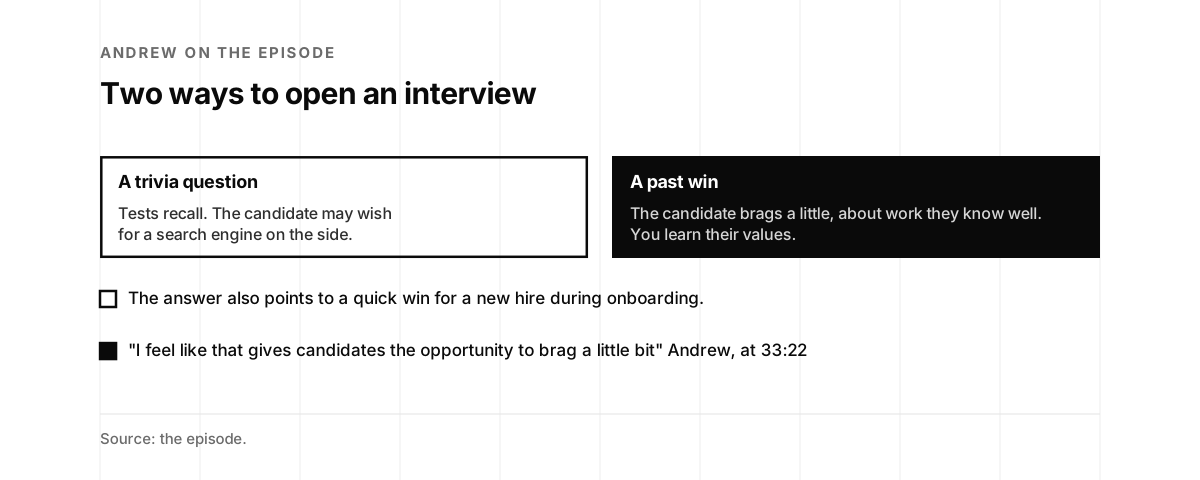
Jon asked for Andrew’s favorite interview question. Andrew asks candidates to describe a win from their career. An interview starts like any first meeting with a stranger, with some ambiguity and trepidation. A candidate might expect a quiz, or a trivia session with a search engine open on the side. Andrew wants to know what the candidate thinks a win is.

“I feel like that gives candidates the opportunity to brag a little bit”

Andrew Spangler, at 33:22

They get to talk about something they’re proud of and comfortable discussing. It tells Andrew more about a person than most trivia questions do. It also shows their values, and where a new hire could land a quick win during onboarding.
Listen · Andrew Spangler on episode 26, from 32:45
About 40 seconds: Andrew on asking candidates about a win from their career. The clip stops on its own. Read the full transcript.
Two cards. A trivia question: tests recall, and the candidate may wish for a search engine on the side. Filled, a past win: the candidate brags a little, about work they know well, and you learn their values. Below: the answer also points to a quick win for a new hire during onboarding. Quote: "I feel like that gives candidates the opportunity to brag a little bit"
A trivia question next to Andrew's question. Source: the episode.

Pipelines that fix themselves

Jon asked what tool Andrew wishes someone would build. The first answer was personal: an easy button for nitro cold brew at home, next to the ice and water on the fridge. Wikipedia describes nitro cold brew as cold brew coffee with nitrogen gas added, introduced in the early 2010s (Wikipedia). If Samsung is listening, Andrew would buy one, and Jon called that a first sale.

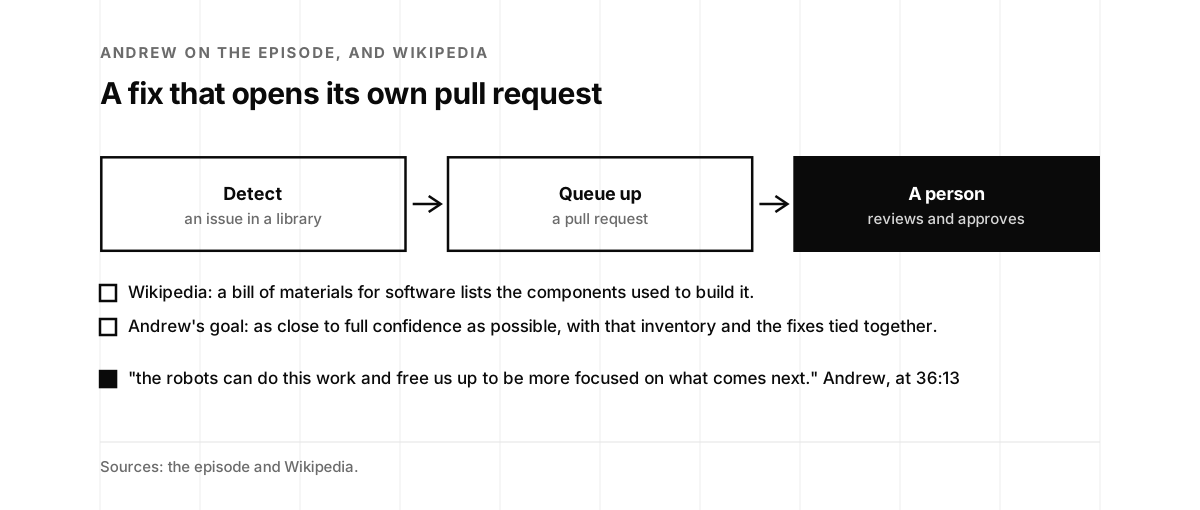
The professional answer was self-healing tools, or AI remediation, like Dependabot on GitHub: the tool queues up a pull request, and a person reviews and approves it. Andrew wants that tied to the work on software bills of materials and vulnerability exchange. Wikipedia describes a software bill of materials as an inventory of the components used to build a piece of software, open source and proprietary (Wikipedia).

“the robots can do this work and free us up to be more focused on what comes next.”

Andrew Spangler, at 36:13

Jon asked whether the secure software development lifecycle could be fully automated someday. Andrew would love to see it, and said Harness was running in that direction.

“I think there’s a future where we’re at least close to that.”

Andrew Spangler, at 36:41
Listen · Andrew Spangler on episode 26, from 35:48
About 30 seconds: Andrew on remediation that opens the pull request for you. The clip stops on its own. Read the full transcript.
Three boxes joined by arrows: detect an issue in a library, queue up a pull request, and, filled, a person reviews and approves. Below: Wikipedia says a bill of materials for software lists the components used to build it. Andrew's goal is as close to full confidence as possible, with that inventory and the fixes tied together. Quote: "the robots can do this work and free us up to be more focused on what comes next."
The loop Andrew described, with a person approving each fix. Sources: the episode and Wikipedia.

Give security a shot

For advice to a younger self, Andrew spoke to people outside the field. There are many jobs in security, and the name alone can sound intimidating. The industry carries historical baggage, and Andrew sees healing at many companies.

One of the best parts of the job, for Andrew, is talking with people who are considering a career in security, or a move into it from another role. That, Andrew said, is where the industry gets stronger, and where much of its creativity comes from. Andrew’s last words of advice: give security a shot, and you might be surprised how much you enjoy it.

“give security a try.”

Andrew Spangler, at 38:06
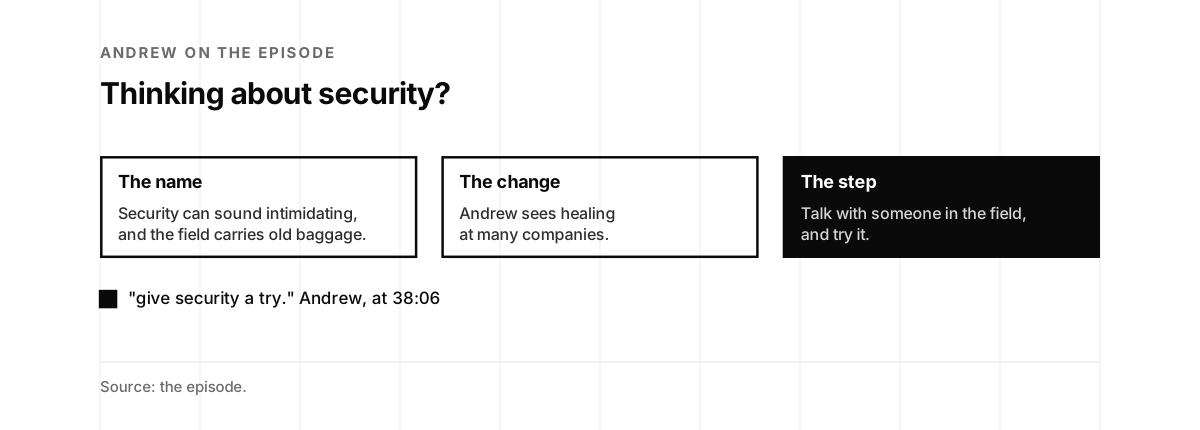
Three cards. The name: security can sound intimidating, and the field carries old baggage. The change: Andrew sees healing at many companies. Filled, the step: talk with someone in the field, and try it. Quote: "give security a try."
Andrew's advice for anyone thinking about security. Source: the episode.

What happened after the tape

Andrew’s role since. LinkedIn lists Andrew as senior director and head of security and compliance at Harness since August 2022, after a director role in the same job from April 2021 (LinkedIn).

Talking with people new to security. Andrew’s advice was to give security a shot, and to reach out. LinkedIn lists Andrew as a mentor in the Cyversity Mentorship Program’s Winter 2023 cohort, “Sharing experiences, tips, recommendations, and advice for the next generation of security professionals” (LinkedIn).

Compliance as a baseline. In May 2025, Andrew shared a conversation on Security & GRC Decoded, a podcast hosted by Raj Krishnamurthy of ComplianceCow. In the host’s summary, Andrew argued that compliance becomes a forcing function for a good security baseline (LinkedIn). In November 2025, Andrew praised the Harness GRC team for bringing software delivery tools, CI/CD and AI into governance work, in a whitepaper the team published (LinkedIn).

Standards for AI agents. On March 31, 2026, Andrew announced joining the consortium behind AIUC-1. The standard’s site calls it “The technical certification for agent security,” maintained by the Artificial Intelligence Underwriting Company, with six risk domains, from data and privacy to society (AIUC-1).

Andrew on joining the AIUC-1 consortium to shape AI best practices.

Andrew Spangler · March 31, 2026
Andrew's post on joining the AIUC-1 consortium. View on LinkedIn.

The same themes on this show. Episode 17 had Sean Cassidy, then the first head of security at Asana, on the day Log4Shell turned engineering into allies. Episode 36 had Feross Aboukhadijeh of Socket on dependency updates and the open source supply chain. Episode 37 opened The Founder’s Guide to Compliance.

Did you catch it? A seven-question quiz

Seven questions from the episode. Each answer links the moment in the transcript or its section.

Quiz · seven questions

Did you catch it?

Pick an answer to see whether you caught it.

  1. What did Andrew rebuild as a systems administrator?

    b. "probably right around 200 tokens that I was able to walk through the process of reprovisioning." Transcript, 5:21.

  2. On a one- or two-week consulting engagement, how long did Andrew say you have to build rapport?

    a. A couple of hours, by Andrew's estimate, to build rapport and trust with a client. See A couple of hours to build trust.

  3. How does Andrew get a short engagement off to a good start?

    c. Common interests, such as video games, music or travel, and a little time up front to learn what interests each person. See A couple of hours to build trust.

  4. What incident in Andrew's first 60 days at Harness pulled the new team together?

    b. Nothing reached the cloud or production, and the team treated it as an incident. See A minor crisis that pulled a team together.

  5. Which incident did Andrew call the best worst day?

    a. Engineering, customer success and legal joined the response, over several weeks. See The best worst day.

  6. How long are OT systems designed to last, by Andrew's account?

    c. "In the OT space, these systems are designed for 50 to 70 years." Transcript, 25:14.

  7. What is Andrew's favorite interview question?

    b. "I feel like that gives candidates the opportunity to brag a little bit" Transcript, 33:22.

Ready for a Log4Shell week?

Eight questions on whether your team could have its own best worst day, built from the episode. Each tip links the section behind it.

Scorecard · eight questions

Ready for a Log4Shell week?

Answer for the services your customers depend on most. If two answers fit, pick the lower one.

  1. If a library like Log4j had a critical flaw today, could you list every place it runs?

    • No
    • For some services, after a search
    • Yes, from a bill of materials for our software, kept current

    A bill of materials for software lists the components behind it. See Pipelines that fix themselves.

  2. Who brings engineering, customer success and legal together in an incident?

    • Nobody named
    • Whoever is around
    • A named incident lead, with a runbook

    "We're all in one piece, and now we're on the other side." See The best worst day.

  3. Can a fixed dependency reach production through your pipeline the same day?

    • No
    • With manual steps
    • Yes, through the normal pipeline

    "It's less drudgery, it's less spreadsheets, it's less manual deployments" See Hand the drudgery to scripts.

  4. Do bots open pull requests for vulnerable dependencies, with a person approving each one?

    • No
    • In some repositories
    • In every repository

    "the robots can do this work and free us up to be more focused on what comes next." See Pipelines that fix themselves.

  5. If an engineer's laptop reports ransomware, is there a plan?

    • No
    • An informal one
    • Yes, written and practiced

    "going through sort of a minor crisis together really has a way of gelling a team." See A minor crisis that pulled a team together.

  6. Could you tell customers quickly whether they're affected?

    • No
    • After a few days
    • Yes, the same day

    Customer success was part of the response at Harness. See The best worst day.

  7. Does the team look back at each incident together?

    • No
    • Sometimes
    • After every incident

    "This is not the worst thing that's happened." See A professional pessimist.

  8. If one person leaves, does their part of the response have a new owner?

    • No
    • Partly
    • Yes, written down

    On a small team, one departure can leave 40 or 50 hours of work a week. See When people move on.

A rough week ahead

A Log4Shell-sized week would start with a search. Begin with an inventory of your dependencies and a named incident lead.

You'd get through it

The basics are there. Add dependency pull requests, a written ransomware plan and a same-day path to production.

Ready for the storm

Keep practicing, and keep the inventory and the owners current as the team changes.

How much drudgery can you hand off?

The calculator counts the hours your team gets back when scripts take over repeat work, as in Hand the drudgery to scripts.

Calculator

How much drudgery can you hand off?

Four numbers: the people on the team, the hours each spends a week on repeat work such as spreadsheets and manual deployments, the share a script or pipeline could take, and the working weeks in your year.

12.0hours a week back
576hours back over the working weeks
14.440-hour weeks of work back

A team of 3 spending 8.0 hours each a week on repeat work gets back about 12.0 hours a week when scripts take 50% of it. That is about 576 hours over the working weeks, or 14.4 40-hour weeks of work.

The defaults are placeholders, so swap in your own counts. The math assumes the scripts need no upkeep, so treat the result as a ceiling. Andrew's measure is what the time goes to next: harder problems and strategy.

From a help desk to the AIUC-1 consortium

Andrew’s path, the field around it, and this show. Filter by topic.

Timeline

From a help desk to the AIUC-1 consortium

  1. AppDynamics

    Jyoti Bansal, later a co-founder of Harness, founds AppDynamics (Wikipedia, on this page).

  2. A school help desk

    Andrew starts in IT as an education technology specialist (LinkedIn, on this page).

  3. Rapid7 buys Metasploit

    The Boston-based security company acquires the Metasploit Project (Wikipedia).

  4. Systems administration

    Andrew's next role, where the RSA rotation would land (LinkedIn, on this page).

  5. The RSA breach

    RSA announces an attack that put SecurID information at risk (Wikipedia, on this page).

  6. New tokens on offer

    RSA offers token replacements or free monitoring to its more than 30,000 SecurID customers (Wikipedia).

  7. Rapid7

    Andrew joins Rapid7 as a security consultant (LinkedIn, on this page).

  8. Puget Sound Energy

    Andrew becomes a senior security analyst at the utility (LinkedIn, on this page).

  9. NIST's energy sector work

    Andrew contributes to NIST practice guides through the National Cybersecurity Center of Excellence, into November 2017 (LinkedIn).

  10. NCC Group

    Andrew joins the security consulting firm (LinkedIn, Wikipedia).

  11. Datadog

    Andrew becomes team lead for information security and compliance (LinkedIn).

  12. Harness

    Andrew joins as director and head of security and compliance (LinkedIn, on this page).

  13. Log4Shell reported

    The Log4j flaw is privately reported to the Apache Software Foundation (Wikipedia).

  14. CVE-2021-44228

    Log4Shell gets its CVE identifier, with a CVSS score of 10 (Wikipedia, on this page).

  15. Episode 17

    Sean Cassidy on Log4Shell and a high-trust security culture at Asana (episode 17).

  16. Senior director

    Andrew becomes senior director and head of security and compliance (LinkedIn).

  17. This episode

    Andrew on the show (Podbean).

  18. A mentor

    Andrew mentors in the Cyversity Mentorship Program's Winter 2023 cohort (LinkedIn, on this page).

  19. Episode 36

    Feross Aboukhadijeh of Socket on dependency updates and the open source supply chain (episode 36).

  20. Security & GRC Decoded

    Andrew shares a conversation on compliance as a security baseline (LinkedIn).

  21. A GRC whitepaper

    Andrew praises the Harness GRC team's whitepaper on automation in governance work (LinkedIn).

  22. AIUC-1

    Andrew joins the consortium behind the AIUC-1 standard for AI agents (LinkedIn, AIUC-1).

What to do this week

Five things, in the order of the episode.

  1. Start with common ground. On your next review with a team you don’t know, open with a casual conversation about what interests them, as in A couple of hours to build trust.
  2. Script one repeat task. Pick the spreadsheet or manual deployment that comes back every week and hand it to a script or the pipeline. The calculator shows what the whole list is worth.
  3. Know where every library runs. Keep a bill of materials for your software current, so the next Log4Shell starts with a lookup (Wikipedia). The scorecard shows the other gaps.
  4. Let bots open dependency fixes. Turn on dependency pull requests, and have a person approve each one, as in Pipelines that fix themselves.
  5. Get help with it. Our 24/7 Monitoring & Response team watches your infrastructure and responds hands-on, Product Security builds security into the pipeline, and a vCISO can lead the team. If you want to talk it through, book 15 minutes with us.

Key takeaways

  1. Trust is the cornerstone

    Jon called trust the cornerstone of security: between people, and between people and their systems.

  2. Start with common ground

    On a one- or two-week engagement there are a few hours to build rapport. Andrew starts with shared interests and casual conversation.

  3. A rotation can earn trust

    After the RSA breach, Andrew replaced about 200 tokens at a smaller company, and took on more firewall work.

  4. Different paths make stronger teams

    Jon and Andrew agree that people with different backgrounds bring the perspectives that hard problems need.

  5. Hand the drudgery to scripts

    Automation frees people from spreadsheets and manual deployments for harder problems and strategy.

  6. A minor crisis can gel a team

    Within about 60 days at Harness, a ransomware report on an engineer's laptop, worked as an incident, built confidence on Andrew's new team.

  7. Log4Shell was the best worst day

    Engineering, customer success and legal joined security for weeks, calm and collected but urgent.

  8. OT runs for decades

    Phones, keyboards and desktops last three to five years. The operational technology Andrew saw at a utility is designed for 50 to 70 years.

  9. Ask candidates about a win

    A question about a past win lets candidates talk about work they're proud of. It tells more about a person than most trivia questions, values included.

  10. Let bots open the fix

    Andrew wants self-healing remediation that queues up the pull request for a person to review and approve, tied to work on software bills of materials.

Chapters

Tap a chapter to play from there.

Pull quotes

“Lots of good people along the way”

Andrew Spangler ·

“Why does it work this way? And can I break it? Can I fix it?”

Andrew Spangler ·

“probably right around 200 tokens that I was able to walk through the process of reprovisioning.”

Andrew Spangler ·

“my boss started to trust me with a little more firewall administration”

Andrew Spangler ·

“it all comes back to trust”

Jon McLachlan ·

“People are the interesting part of any job that I've held.”

Andrew Spangler ·

“I think that everyone takes a different path”

Jon McLachlan ·

“I love the diversity in backgrounds and the different perspectives”

Andrew Spangler ·

“build tools for people that build tools”

Andrew Spangler ·

“It's less drudgery, it's less spreadsheets, it's less manual deployments”

Andrew Spangler ·

“Let's let the robots do the drudgery, and we can focus on what comes next.”

Andrew Spangler ·

“when I was your age, we had this thing called spreadsheets.”

Jon McLachlan ·

“going through sort of a minor crisis together really has a way of gelling a team.”

Andrew Spangler ·

“We're all in one piece, and now we're on the other side.”

Andrew Spangler ·

“as a security professional, you're kind of a professional pessimist”

Andrew Spangler ·

“In the OT space, these systems are designed for 50 to 70 years.”

Andrew Spangler ·

“my loyalty is connected to people.”

Jon McLachlan ·

“I feel like that gives candidates the opportunity to brag a little bit”

Andrew Spangler ·

“the robots can do this work and free us up to be more focused on what comes next.”

Andrew Spangler ·

“I think there's a future where we're at least close to that.”

Andrew Spangler ·

“give security a try.”

Andrew Spangler ·

About the guest

Andrew Spangler, Head of Security and Compliance, Harness

Andrew Spangler is head of security and compliance at Harness, a software delivery platform, a role LinkedIn dates to April 2021, with the senior director title since August 2022. Andrew's path ran from education technology at a school district and systems administration to security consulting at Rapid7, security analysis at Puget Sound Energy, consulting at NCC Group, and team lead for information security and compliance at Datadog. LinkedIn also lists Andrew as a mentor in the Cyversity Mentorship Program's Winter 2023 cohort and, since March 2026, a member of the AIUC-1 consortium.

About the host

Jon McLachlan is co-founder of YSecurity, the on-demand cybersecurity team for startups, and of Cyberbase.ai. The Security Podcast of Silicon Valley is hosted by Jon McLachlan and Sasha Sinkevich. Jon McLachlan on LinkedIn ↗

Context and sources

  • Episode 26 on Podbean: Andrew Spangler, Head of Security and Compliance at Harness, on Building Trust in Security. Source ↗
  • Andrew Spangler's experience on LinkedIn: Harness since April 2021, Datadog from November 2017, NCC Group from October 2016, Puget Sound Energy from May 2013, Rapid7 from December 2011. Source ↗
  • Andrew Spangler's volunteering on LinkedIn: the Cyversity Mentorship Program, Winter 2023, and NIST's National Cybersecurity Center of Excellence, from 2016 to 2017. Source ↗
  • LinkedIn, March 31, 2026: Andrew on joining the AIUC-1 consortium. Source ↗
  • LinkedIn, May 23, 2025: Andrew shares a Security & GRC Decoded conversation on compliance as a security baseline. Source ↗
  • LinkedIn, November 20, 2025: Andrew on the Harness GRC team's whitepaper. Source ↗
  • AIUC-1: a certification for agent security, maintained by the Artificial Intelligence Underwriting Company, with six risk domains. Source ↗
  • Wikipedia, RSA SecurID: the attack RSA announced on March 17, 2011, and the token replacements offered on June 6, 2011. Source ↗
  • Wikipedia, Metasploit: owned by Rapid7, a Boston-based security company, since October 21, 2009. Source ↗
  • Wikipedia, Puget Sound Energy: a Washington utility with more than 1.24 million electric customers. Source ↗
  • Wikipedia, NCC Group: an information assurance firm for security consulting and managed services. Source ↗
  • Wikipedia, Datadog: an observability service for cloud-scale applications. Source ↗
  • Wikipedia, Jyoti Bansal: founder of AppDynamics in April 2008, and co-founder and CEO of Harness. Source ↗
  • Wikipedia, AppDynamics: acquired by Cisco in 2017 for $3.7 billion. Source ↗
  • Wikipedia, Gary A. Klein: author of Seeing What Others Don't, from 2013. Source ↗
  • Wikipedia, Log4Shell: CVE-2021-44228 in Log4j, reported privately on November 24, 2021, with a CVSS score of 10. Source ↗
  • Wikipedia, Ransomware: malware that holds a victim's data hostage until a ransom is paid. Source ↗
  • Wikipedia, Operational technology: hardware and software that monitors and controls industrial equipment. Source ↗
  • Wikipedia, North American Electric Reliability Corporation: the regulator for the reliability and security of the grid. Source ↗
  • Wikipedia, Software supply chain: a software bill of materials inventories the components used to build software. Source ↗
  • Wikipedia, Cold brew coffee: nitro cold brew adds nitrogen gas, and was introduced in the early 2010s. Source ↗

Transcript

Automatic transcription. Jon McLachlan hosts this episode with Andrew Spangler, head of security and compliance at Harness. There is no diarization on the tape, so speaker labels were assigned from the content and checked against reference recordings of each voice from this episode, and a few short lines may sit with the wrong speaker. Names and terms were normalized where the recognizer misheard them (Jon McLachlan, Andrew Spangler, Harness, Jyoti Bansal, AppDynamics, Rapid7, Puget Sound Energy, Log4Shell). Words in [brackets] are best guesses where the audio is unclear, and [...] marks words no decode made out. Speech is transcribed as spoken, though many repeated words and false starts are left out, and so are short backchannels such as "yeah" where they overlap the other speaker.

Read the full transcript 6,647 words

Jon McLachlan

Welcome, everyone, to the Security Podcast of Silicon Valley. I am your host, Jon McLachlan, and I'm here today with a very special guest, Andrew Spangler, the head of security at Harness. Welcome to the show, Andrew.

Andrew Spangler

Thanks, Jon. Really glad to be here and looking forward to talking with you today.

Jon McLachlan

I'm super looking forward to it too. You bring to the table so much great experience. You launched your career at Mount Vernon School District as an educational technology specialist, back in the day. From there you became a system administrator, but then it looks like you got sucked into the security world here. You were a security consultant for Rapid7, and then after that, you were a senior security analyst at Puget Sound Energy. And then you worked at a very nice place that I'm sure most of our listeners are familiar with, the NCC Group. You were a senior security consultant there for a good chunk, a year or so and two months. Then Datadog pulled you in. You were a team lead of the information security and compliance group there at Datadog. And that's probably where you met Pierre, at the acquisition of his little startup, the [Sqreen] startup. Cool. And now you're at Harness. You're the head of security and compliance. Welcome to the show.

Andrew Spangler

Thanks, Jon. It's been quite a journey. Lots of good people along the way, including our mutual friend Pierre. Lots of good mentors and generous knowledge transferred from folks at each of those places that have brought me to this current role, where I still benefit from the expertise of my teams and the exposure that I get as a part of Harness.

Jon McLachlan

I really feel and vibe with the sense of humility. But I'm sure that you also put in some blood, sweat and tears along the way there.

Andrew Spangler

Plenty of that, for sure. Yeah, plenty of that. I think, like many things, or like many of our friends and colleagues, technology was always really interesting to me, even as a kid. My dad was a tech enthusiast from as far back as I can remember. And one of my first introductions to technology was an old warehouse computer with an 8086 processor and an amber screen and DOS manager. We even had a dot matrix printer. So the whole setup, and really got hooked on technology through video games, believe it or not. I think that's probably not [too] crazy.

Jon McLachlan

But I think it is a very common story of those dot matrix [printers] and that funny sound that they used to make.

Andrew Spangler

You go into, I think it was called Print Shop, and you could print out a little banner for your room or happy birthday sign for your sister, in my case, and have a lot of fun. And the interest only grew from there.

Jon McLachlan

That's really sweet. You printed something out for your sister.

Andrew Spangler

Oh, yeah. Sometimes I think the best use of technology is when you can use it to interact with other people, and maybe have an opportunity to, even in a small way, build something that you couldn't do yourself. I'm the farthest thing from an artist, but there's a lot of sharp edges that can be rounded by using technology, even back then. So, lots of fun memories back in the day.

Jon McLachlan

That's amazing. So was there anything specific about security that initially attracted you to that space?

Andrew Spangler

Yeah, so as you mentioned, I really got my first formal job in IT working as really a mobile help desk for a couple of different elementary schools in Washington State, up there in Mount Vernon. At the time, my future brother-in-law also was working at that school district, and he's both a security enthusiast and security engineer. And his interest and passion about that really grabbed my attention. And I think many of us in the field would echo the sentiment that it's just a cool space to be in. You get the behind-the-scenes visibility into what's going on with infrastructure and applications, and it really plays off that, I think, common interest that many folks in the field have, of wanting to understand how things work. Why does it work this way? And can I break it? Can I fix it? And let me take it apart and put it back together. And I think that was a big piece for me. And at the next job you mentioned, where I had the chance to do some systems administration, one of the big tasks that I had during my time there was to rebuild our multi-factor authentication system after the RSA Poison Ivy compromise, back in the late [2000s], or maybe early 2010, which kind of got me some practical hands-on experience with at least security technology.

Jon McLachlan

So you guys ripped out the RSA stuff and you put something else into play?

Andrew Spangler

In our case, we ripped out all the old RSA stuff and replaced it with the new RSA stuff. So there was a, hey, our root credentials have been compromised. We're going to go ahead and rotate those. We'll send you all new fobs, and we'll send you all new hardware. And part of my job was to seamlessly decommission the old setup and spin up, configure, and deploy all of the new keys. It was a smaller company, probably right around 200 tokens that I was able to walk through the process of reprovisioning. And in addition to that, my boss started to trust me with a little more firewall administration and kind of getting to see the broader edges of the security field. And that really was exciting work to me.

Jon McLachlan

Yeah, you said the magic word, trust. It's, I guess, the cornerstone of all things security, isn't it? It's not just something that exists between people, but between, like, our expectations of systems. I think it all comes back to trust at some very fundamental level here in the security world.

Andrew Spangler

Absolutely. Yeah. So, talking about that kind of first foray into security, not too long after, I had a friend of mine put me in touch with his cousin, who had just started at Rapid7 at the time, an unknown company to me. This was back pre-IPO, 2010, 2011. And the company was hiring for a security consultant, really, to work in the professional services team. So I was able to take the experience and knowledge that I had gathered at that point in systems engineering and systems administration, and apply some real practical security practices as a part of that work, going out and helping folks build vulnerability management programs and doing some sort of advisory work with our different customers. And to your point, being able to cultivate trust in such a small time-boxed window, with those one or two-week engagements, you really have a couple of hours to build rapport and trust with people, especially when you're coming in as an external person to advise them on some of the more sensitive processes that they have in our organization.

Jon McLachlan

Yep. As an outsider, sometimes that can be especially challenging. Do you have a favorite technique to help accelerate that journey towards reinforced trust?

Andrew Spangler

I think I've never really thought of it as a technique as much as what helps me feel comfortable, just to build relationship and build rapport, I think. Finding some common ground, common interest, whether it's something like video games or music or travel.

Jon McLachlan

Yeah. Camping.

Andrew Spangler

Exactly right. Camping, hiking out in the desert, all those kinds of things will give you a good opportunity to at least establish some common ground in a non-hostile way, I think. One of the things I was always concerned about as a consultant is that the client would have so much more knowledge about their systems and their environment and the intricacies of those things than I would, that I wouldn't be useful, or I wouldn't be helpful to them and would be in the way. And so part of my strategy was, I want to get to know these folks. And so I'd spend a little bit of time up front just having some casual conversations and getting to know what was interesting to them, which I felt like opened up, or maybe a better word is, the posture of the rooms that we were in, whether it was a server room or a big meeting room.

Jon McLachlan

Nice. No, I love this notion of being a little bit just less standoffish and more together, more connected.

Andrew Spangler

People are the interesting part of any job that I've held. And I think that there's always the tactical execution we have to be mindful of, but the richness of relationships and being able to make contributions to other people, and to receive from them as well, has been [far and away the highlight] of my career.

Jon McLachlan

Absolutely, I couldn't agree more. Did I screw up? Did I miss your education? I did miss your education. I was just wondering if you had gone to school for computer science or anything. And I'm looking at your LinkedIn here.

Andrew Spangler

I was just going to say, man, no, you didn't miss it, because there wasn't any. There was no formal education.

Jon McLachlan

Good for you. Oh, all respect to the world, man.

Andrew Spangler

Oh, man. And that's where I think a lot of those mentors, and you mentioned earlier the blood, sweat, and tears. I think I heard a quote one time that luck is the intersection of preparation and opportunity. And I think that's really been true, at least in my case. Right after high school, I moved to Los Angeles for about 18 months, and I attended an intensive program covering global history of philosophy, which I enjoyed immensely. It's amazing. Man, often I think back to those days, where my only responsibility was to read books and then talk about what I thought. Those were very good days. But after I finished that, I wasn't really sure what I wanted to do. I knew that I didn't want to make a commitment to an educational path, or a financial commitment to student loans, without at least some sort of confidence that I can build a life off of this education. And so I really started doing a bunch of different things. I worked at a few different small businesses. I was involved in some community events. And then, actually, along with the IT piece, I found that friends and family and small business owners in the town that I lived in needed help with their technology. And that was an easy way for me to make a few bucks, to meet some more people, and let me scratch that IT itch.

Jon McLachlan

What town was it?

Andrew Spangler

This was a little town up in northwestern Washington called [Sedro], when I was living up there. I think there were about 6,000 people. The tagline of the town is the gateway to the North Cascades. So it's really the last stop before you get into the beautiful wilderness of Mount Baker.

Jon McLachlan

Oh, that sounds amazing. No, that sounds really beautiful. And thank you for sharing, too. It's good. I think that everyone takes a different path, and no one arrives in this present moment and close to the same. And I think it's those differences that make life interesting, and make teams stronger than the sum of their individual parts, and really drive at the core of what it means to be a participant in the economy and the world and in a team.

Andrew Spangler

And so, it's good. Good for you. I think you're right on the money, man. It's one of my favorite things about our security field, is that it's new enough, I think, in this space. Really, technology in this iteration feels new every year, but I think the kind of historical discipline of security, as it's evolved over the last, at least for me, 15 plus years, has been a great avenue for folks with all kinds of backgrounds. Some of the best professionals I've worked with have had liberal arts backgrounds, or kind of no formal training. And certainly there's a lot of excellence from STEM and from the hard sciences, but I love the diversity in backgrounds and the different perspectives that we can bring to these unique problems that we're trying to solve.

Jon McLachlan

Certainly. You hit it right on the money. This is where creativity comes from, our differences. It's not our similarities. Our similarities [may] feel good, and it's important to find those similarities early on in the relationship to help build that trust, like we were talking about. But I believe 100% this is where creativity comes from, seeing the world just a little bit differently. In fact, there's a book out there called Seeing What Others Don't. It's a series of case studies around, like, where creativity has come from in the past, in past instances. And it's an interesting read. I'll put the details in the description, perhaps. But have you read that book, by chance?

Andrew Spangler

No, but I'm definitely adding that to my Goodreads list.

Jon McLachlan

Because you share a lot of these perspectives. It sounds like maybe you had it. Also, it sounds like 100% you've taken full advantage of all of your opportunities along the way and put in all those blood, sweat and tears through a long and interesting career through security. And now you're at Harness. And even though Harness is a quite successful startup, I'm sure many of our listeners maybe have never heard of it. So, would you like to share a few words about what Harness does, just at a high level, and the role security plays at Harness?

Andrew Spangler

Yeah, I'd be happy to. So, Harness is a software delivery platform. We do CI, CD, and a bunch of complementary and [standalone] modules that can be used, as I mentioned, either in conjunction with the platform itself or in a standalone fashion. Things like feature flag management, one of my favorite, security testing orchestration, helping you to get your [vuln scans] running as a part of your software pipelines, a whole suite of things. And one of the things that really grabbed my attention about Harness is not only a really high-caliber leadership team. Our founder, Jyoti Bansal, had also previously founded AppDynamics and a number of other ventures out there in the Bay. But then also the space itself. I think over the last, I don't know, seven or eight years of my career, I've had kind of a sneaking suspicion that a lot of the work I'd be doing, or I was doing at the time, would be automated in the future. And sure enough, now it is. And it's through, at least primarily, through platforms like Harness. And so that was definitely something I wanted to be a part of. I really like industries that build tools for people that build tools, infrastructure-level type of work. And I feel like software delivery is a modern iteration on that theme.

Jon McLachlan

It's a natural next step for all things automation, isn't it?

Andrew Spangler

Yeah. Yeah.

Jon McLachlan

Especially in this day and age, where there's all these layoffs happening, and the economy is not all sunshine and flowers like it used to be, and you have to do less with more. And I think I bumped into a sentiment every once in a while, which is, sometimes people are afraid of automation, not just from a risk perspective, but maybe from, like, almost like a job security point of view. But the way I've always seen it is, yeah, let's get everything automated. Let's please replace everything I do in a day with a script, so I can go off and think about and work on that next layer of problem and contribute at a much higher level than I was.

Andrew Spangler

Completely agree with you, Jon. That was, along with that sneaking suspicion, was also a looming sort of specter of uncertainty. Is the work that I feel like I'm good at going to be irrelevant in five years, in 10 years? And so that kind of job insecurity was definitely a factor for me as well. And I think what I've come to realize, both through just time in seat as well as exposure to cloud-native companies like Datadog and now at Harness, is it really does. It frees you up to work on more interesting problems. It's less drudgery, it's less spreadsheets, it's less manual deployments, and a lot more time back to focus on higher-order problems, or sort of strategy and the interesting work. Let's let the robots do the drudgery, and we can focus on what comes next.

Jon McLachlan

I love it. This mental picture just popped into my head when you were describing that future. And I would love to be an old man, a grumpy old man, that could turn to a young person at some point in the future and say, when I was your age, we had this thing called spreadsheets.

Andrew Spangler

May it be true. May it be true.

Jon McLachlan

Hey, don't give up. You've got to finish all the hard work that we started. You're at Harness and everything. You're in a perfect position to be able to help, but we can all contribute in some way or another. Anytime I find myself doing something more than twice, that came out wrong, every time I found myself doing something more than once, it's the indicator that this could be automated.

Andrew Spangler

That's really, yeah, definitely.

Jon McLachlan

My brain stops everything and it imagines how it could be automated. That's somewhat intrusive, but that's okay. Meditation helps.

Andrew Spangler

A little mindfulness in the mix.

Jon McLachlan

A little bit of mindfulness goes a long way, doesn't it?

Andrew Spangler

Yeah, it really does.

Jon McLachlan

Okay, so what's been your best day at Harness so far?

Andrew Spangler

That's a great question. There have been a lot of really good days. It's tough to pinpoint a best day. I think there may be a couple of standouts for me that really felt things started to click, and that we were on the right track, and we were doing the stuff of security. The first one's within the first, I don't know, maybe 60 days. I had inherited a small team of two engineers. We're a globally distributed, remote-first company, and although there are physical office locations, majority of the company, including my team now and at the time, is fully remote. And I had a couple of engineers that I was working with, and we had a report that one of our software engineers' laptops had been compromised by ransomware. Fortunately, no effect to our cloud environments or to anything in production, but still something that we wanted to prevent any further spread. And we treated it as an incident. And through that process of incident management and rapid response, I felt we built confidence in each other. Back to your great point about trust as a foundation of the work that we're doing. So the process and professionalism and expertise that I was able to witness and participate in and contribute as a part of that response effort was a great kind of first win, a great first best day at Harness. And going through sort of a minor crisis together really has a way of gelling a team. And that was the output from that. I think another highlight day for me, again, has been hiring. So, team and the people that I'm working with, people that I'm working for, has always been priority zero for me. And as we talked about earlier, an integral component to any success that I've had. I know a lot of people, and I'm sure you do too, who are very hard workers and give 110%, but you can do that in a vacuum if you're not surrounded by a good team. It's not wasted effort, but the result can be less than what you hope. And so big wins for me, being tasked to build out a security team from two, has been really rewarding, to bring on people that are competent and hardworking and catch the vision. And then maybe the last one that I was thinking of is the best worst day, when Log4Shell was announced and kind of hit the airways earlier this year. Again, for many of the same reasons, seeing the coordination and professionalism and the expertise across the company, not just security. Obviously engineering is involved, our customer success teams are involved, our legal teams are involved. And the calm and collected, yet urgency with which we responded to that evolving incident over several weeks, really was another great win. It felt we got through, we got through the storm. We're all in one piece, and now we're on the other side. That was a really good day.

Jon McLachlan

No, that's amazing. Okay, so what's incredible about your answers is two out of your three best days have been related, and have been where stuff has been hitting the fan. Perhaps we're both afflicted with the same, I'm not sure what to call it, mental disability, where no matter what's going on, we're going to see the good that's going to come out of it, and we're going to focus on that. And I just don't know any other way to view the world, or to view things that happen. It sounds like you maybe have a very similar perspective.

Andrew Spangler

Man, that's been a lifeline for me, Jon. I'm certainly not immune to pessimism. I think in many ways, as a security professional, you're kind of a professional pessimist by design.

Jon McLachlan

We are.

Andrew Spangler

We ask all of those tough questions. It's easy to see, at least, it becomes easier to see, what's wrong with the situation or with the technology or with some given task at hand. And I've found that, for me, looking not only at the moment, but also reflecting on the past, and then again into the future, has helped bring that perspective of, even though this feels a chaotic maelstrom, it's going to be okay. This is not the worst thing that's happened. And then that's up to me to see, or better see, the [wins], right? The points of light in those dark moments. And that's been an important part of getting through those tough times.

Jon McLachlan

Oh, I couldn't agree more. Like, seeing, keeping things in perspective. I couldn't imagine what it would be like to be writing, like, software that flies airplanes, or that controls, like, how much drug is administered during a chemotherapy session, or an x-ray that blasts you with x-ray radiation. Those critical systems have someone's life on the line. But for the most part, a CI/CD system or, I don't know, coin stuff. It's not, no one's going to die.

Andrew Spangler

I was just going to say, you make a really important, and I think a good point about perspective in our work as well, as a part of our tools that we have available to us to execute our work, to interact with people around us, that perspective of what we're doing. And certainly in the moment, things are very important, and not to minimize any of those things, but I think back to my time at Puget Sound Energy, which is the largest utility in western Washington State, serves all the big, relatively big cities in Washington. And part of my role there was [IT] and OT, operational technology, vulnerability management. And so I had a real privilege to go out into the field, going to generation facilities, whether it was hydroelectric or natural gas or geothermal, and then out to substations, and really getting a small perspective on the underpinnings of something that's easy to take for granted. And then when it's not available, we all notice it right away, and there's, to your point, the potential for catastrophic consequence. And so my respect for people who have dedicated their careers and their expertise to keeping the lights on, to keeping the drips in the hospitals moving, is just immense.

Jon McLachlan

Yeah, definitely. I'm of the same perspective too. It's almost like just serving in the military or something. It's just more on a cyber scale.

Andrew Spangler

Yeah. Yeah.

Jon McLachlan

So you had the privilege to see, get the inside scoop, maybe just a couple years old, of how secure the infrastructure is. I didn't realize that was a security position that you had.

Andrew Spangler

Yeah, that was a fascinating world to learn. It's not a natural path to go into operations technology as someone without that kind of formal engineering background. And I worked very closely with professional engineers on this security posture for components of the bulk electric system, and again benefited daily from the expertise of really great colleagues. So, yeah, fascinating work. One of the interesting things that really stood out to me was, as we'd go out to these facilities or have conversations with folks, I think of technology, even hardware, as almost ephemeral, right? Even these days, the phones that we use, the keyboards, the desktop computers, three to five years is a good lifespan, generally speaking. In the OT space, these systems are designed for 50 to 70 years. And so you're walking into a substation and they're saying, hey, we put this in in 1971, and it's still rolling strong, and no need to touch it. In fact, don't touch it. It's working fine as it is.

Jon McLachlan

Hey, if it's not broken.

Andrew Spangler

Exactly right.

Jon McLachlan

You know, it's funny you mentioned three to five years. I try to make my phones last about six, and then I just go off and I buy the best phone after six years. But by the end of that six years, I start to get those funny looks from my friends, and what's wrong with you? Maybe an upgrade from the thing that belongs to Smithsonian. And I'm like, maybe, yeah, eventually. One more year.

Andrew Spangler

There's only one camera on the back of that thing, Jon. Come on, man.

Jon McLachlan

I just upgraded. So here we go. It has the three now. Finally.

Andrew Spangler

Yeah.

Jon McLachlan

It's going to last for a long time. And I love this theme. I feel that it's come up multiple times here, and I'll just call it out. It sounds like you have a very strong growth mindset, where you're always learning, you're always curious, you want to understand how things work, and you're willing to pay that cost to better yourself.

Andrew Spangler

Yeah, absolutely. That was, I think, something, again, to go back to those early years, something instilled by my parents, by the people that I had the good fortune to be around as I was young. And then I think also just as a part of the personality that kind of evolved into who I am now, is very interested in how things work and why they work. I would guess that I was one of those kids that just kept asking why. I asked the question, and then there's seven, not seven whys, but there's 20 whys afterwards, and you're never satisfied until you get down to the bits and bytes. That's also been a really valuable part of my personal development and professional development over the years, the kind of internal drive to uncover what's next, what's the next page say. And I think that's a common theme I've found, at least in people that I've really resonated with in our community and in our industry, is that sort of shared sense of curiosity.

Jon McLachlan

It even connects back to your intense education where you were, and philosophy, connected to the bits and pieces. It's funny that you mentioned philosophy too, and that you did actually go down that path. I always, I often say that if we had lived in a world without computers or computer science, I probably would have been a philosopher.

Andrew Spangler

Seems like a great gig. What could be better than just thinking it up all the time?

Jon McLachlan

It's important. I think it's important to understand where meaning comes from. Ask those tough why questions. Ask them over and over again. Ask them until you get to the very core value system that you're dealing with. And then once you get to the core value system, maybe you could even have a playful sense of empathy with your own values, and compare and contrast, see how they're different, see how that leads to a different world perspective. And when you have a different world perspective, sometimes problems don't look like problems anymore. Sometimes they look like features. Funny how that works, isn't it?

Andrew Spangler

Yeah. Isn't it? Yeah, at the time, really focused and dedicated to learning and absorbing. Our curriculum was really, read 300 to 500 pages before 1 p.m., and then from 2 to 6, we're going to all sit in a room. There's about 15 of us. We're going to all sit in a room with a moderator who's going to lead a discussion in the Socratic method, kind of prompting you to examine your assumptions, and like you mentioned, boiling down the periphery to that core value system, and then continuing to ask those why questions. And I feel like that experience, plus some exposure to the world through travel, have really some of the things that I draw on on a regular basis when I'm kind of thinking through my life and career.

Jon McLachlan

Or are you in a computer system?

Andrew Spangler

Or even a computer system, or a video game, or a video game.

Jon McLachlan

Yeah, there we go. There's nothing wrong with having a little bit of fun [over]. Life is far too [an] important thing to be taken so seriously all the time, as well, isn't it?

Andrew Spangler

Exactly. Exactly.

Jon McLachlan

Okay. Okay. So what's been the worst day that you've had so far in your journey at Harness?

Andrew Spangler

Yeah, that's another tough one. I'm sure you've had the unique experience of having components of a best day and a worst day somehow [bring it] to the same 10 hours. Yeah.

Jon McLachlan

Story of my life.

Andrew Spangler

Yes. Those best days can be so fleeting. I think some of the challenges for me so far, you've had a couple of folks move on from the team into their kind of next adventure, and that's been tough on a number of levels, I think. There's a part of me that really values that relational connection. And so even if it's a good thing, especially when it's not, but even if it is a good thing, there's still some bittersweet flavor to that experience. And then, just practically, when you're building a small security team at a high-velocity startup, where, as you mentioned earlier, you got to do more with less, you really feel the impact of, all of a sudden, 40, 50 hours a week are just, now you got to figure out where's this going to go. And that was a real challenge. But sure, again, back to the importance of putting ourselves with good people, with diverse backgrounds, with unique perspectives and eagerness to, you know, curiosity and the eagerness to learn, is really the saving grace in those.

Jon McLachlan

So I started off as an engineer, and it shifted more into leadership roles. And I have to say, like, one of the most rewarding pieces of having gone through that shift is to help people achieve what they want to achieve and bring their careers to that next level. And whether or not that's within the same company or at a different company, I don't think really matters too much, because my loyalty is connected to people. And that's where I get my drive. And very oftentimes, it is. You can facilitate that type of growth within the same company, but when you can't, that doesn't mean that our job as leaders is to drop the ball. It's just, okay, this is going to be an interesting journey for you, and here's the options that I can think of in my network. And to watch these people, individuals who have that drive, that hunger, that curiosity, learn and grow themselves and become leaders themselves is quite rewarding, in ways that I had no idea until having gone through the experience myself.

Andrew Spangler

I would absolutely echo that sentiment. That's by far been my favorite part of transitioning, making that career transition into a leadership role. There's always the pressure of execution, and your own internal motivation to perform well and make life better for the team. But seeing people succeed, being able to encourage and, in some ways, provide mentorship and insights, [unblocked], and then see them grow and take on new responsibilities, take initiative, top highlight for me, absolutely, over the last five or six years.

Jon McLachlan

Okay, so in the spirit of people and building teams, what's your favorite interview question? And why?

Andrew Spangler

One of my favorite interview questions is to ask folks to tell me about a career highlight. I feel like, again, to close the loop, picking [up] the beginning of our conversation, where you meet somebody new for the first time and there's ambiguity, there's a little bit of trepidation, especially walking into an interview, where you don't know, are they going to be reasonable? Is this interviewer going to quiz me on things? Is this going to be a trivia session where I have to hopefully try to Google on the side? I don't want to do that. I really want to know, what do you think is a win? What has been a good win for you? And I feel like that gives candidates the opportunity to brag a little bit. It also puts them in a position where they can talk about something they're comfortable with, that they're proud of. And I feel like that tells me more about someone than most trivia questions, or asking for, sort of, linked lists or [...]. Yeah, exactly. Yeah, exactly right. So I really love to hear about what was the win for you, and then you can unpack it from there. But I think giving people the opportunity to highlight something that they're really proud of achieving is a good way to get to know someone's values, and, were they to join the team, maybe a good place to plug them in for a quick win during the first onboarding period.

Jon McLachlan

Yeah, and set them up for success. 100%. So, how about if we fast forward into the future just a little bit? I'll let you decide how much into the future you'd like to take this question. But if we look into the future, or fast forward into the future, what's one tool or service that you just wish someone would build already, that you think would make that future so much better, so much brighter, that maybe you haven't had the opportunity to build yourself, or it hasn't been a business priority yet for you and any of your places that you've been at? This is a leading question for the entrepreneurs that are listening to the podcast.

Andrew Spangler

Might be. I was going to say, I wish I had a good app to pitch right now.

Jon McLachlan

Oh, okay. All right. No, you could come back and say, Jon, ask me that question again. Here, I got an app now, like in the future. Anytime.

Andrew Spangler

Thanks, Jon. Thank you. I think, personally, personally, I would love for inexpensive easy button for nitro cold brew at home. I have been searching for a convenient way to make a nitro cold brew at home, and I have just not been able to find it. It's doable, but it's a real labor of love. And I would love to just, like, you have a dispenser in your fridge where you can get ice or water, I just want, like, another button that's nitro cold brew.

Jon McLachlan

A fridge that serves your nitro cold brew, and all you have to do is put the beans in at the very top, and it does the rest.

Andrew Spangler

That's right. If you're listening, Samsung, I would buy that.

Jon McLachlan

There you go. We got your first sale right there.

Andrew Spangler

From a professional standpoint, I would really love to see the continued integration of this kind of self-healing tools, or AI remediation, like Dependabot in GitHub, where, you know, hey, we detected there's [vulns] in these libraries, and actually even queued up a PR for you. You need to just review and approve. I'd love to see that get tied in with a lot of the good work that's being pioneered now around software bill [of] materials and this vulnerability exchange, and be able to move towards a future where we have as close to 100% confidence as possible that, again, the robots can do this work and free us up to be more focused on what comes next.

Jon McLachlan

Do you think we'll get to a world where the secure software development lifecycle could be 100% automated by something like Harness?

Andrew Spangler

I would love to see that future. I think we're, I know at Harness, we're running in that direction as fast as we can. I think there's lots of interesting challenges to overcome, but peering into the crystal ball, I think there's a future where we're at least close to that.

Jon McLachlan

Yeah. I think so too. I'm very optimistic about this, and I'm very grateful and humbled that there are people in this world, very smart people in this world, dedicated to this problem, especially there at Harness, thinking about it and moving not just that company forward. It's an open source project. There's lots of contributions that are going back. There's nothing obscure about it. Yeah, very transparent, and can really help a lot of people move more quickly.

Andrew Spangler

Great story. And I'm excited. I'm excited about the future. I think there's lots of opportunities in front of the industry, and it's cool to be one of the many people pushing on the cart to move things.

Jon McLachlan

Yeah, definitely. Absolutely. Would you like to leave our listeners with any words of wisdom? Perhaps advice for your younger self that you wish you had heard back in the day?

Andrew Spangler

Well, what a great question. I don't even want to give a number, because there's so many variants, but there are many jobs in the country and around the world. I think just the name security can come across intimidating to some folks. There's some historical baggage that the industry carries. I think in many companies, we're beginning to see some healing and some relief. And so, maybe the words of wisdom is, give security a try. Reach out to someone. Along with mentoring the team, one of the highlights for me has been when I get the opportunity to speak with people who are considering a career in security, or considering transitioning from a different role into a security-focused role. I think that's where we as an industry get stronger. I think that's where, to your point, a lot of our creativity and excitement comes from. And so my word of advice would be, give security a shot, and you might be surprised with how much you enjoy it.

Jon McLachlan

Amazing. Thank you so much, Andrew. It's been a real pleasure to have you on the show. Thoroughly enjoyed our discussions. Thank you. Thank you again. Thank you so much for your time today. And thank you to all of our listeners for tuning in to another episode of the Security Podcast in Silicon Valley.

Andrew Spangler

Thanks for having me on, Jon. This is great.

FAQ

Questions this episode answers

Who is Andrew Spangler?
On this December 2022 episode, Jon introduced Andrew Spangler as head of security and compliance at Harness, a software delivery platform. Andrew's path ran from a school help desk and systems administration through Rapid7, Puget Sound Energy, NCC Group and Datadog to Harness, where LinkedIn dates the role to April 2021.
How do you build trust quickly as a consultant?
Andrew starts with common ground, such as video games, music or travel, and spends a little time up front on casual conversation, to learn what interests each person before giving advice on sensitive processes.
What did Andrew do after the RSA SecurID breach?
As a systems administrator, Andrew rebuilt the company's multi-factor authentication with new RSA tokens, about 200 of them. Wikipedia dates RSA's announcement of the attack to March 17, 2011.
Why did Andrew call Log4Shell the best worst day?
The response pulled in engineering, customer success and legal alongside security for several weeks, and the company came through it. Wikipedia describes Log4Shell as CVE-2021-44228, a flaw in the Java logging library Log4j with a CVSS score of 10.
How long does operational technology last?
In Andrew's account, phones and computers last three to five years, while OT systems at a utility are designed for 50 to 70 years, such as equipment from 1971 that's still running.
What is Andrew's favorite interview question?
Andrew asks candidates to describe a win from their career. It lets them brag a little about work they're proud of, shows their values, and hints where a new hire could land a quick win.
What tool does Andrew wish someone would build?
Personally, an easy button for nitro cold brew at home. Professionally, self-healing remediation like Dependabot on GitHub, which queues up a pull request for a person to review and approve, tied to work on software bills of materials.
What happened after the episode?
LinkedIn lists Andrew as senior director and head of security and compliance at Harness since August 2022, a mentor in the Cyversity Mentorship Program's Winter 2023 cohort, and, since March 2026, a member of the AIUC-1 consortium.
Keep reading on the YSecurity blog
New episodes every other Tuesday

Got a story like this one?

We're always looking for practitioners who've been in the room when it mattered.