
"We Need SOC 2 Soon, But We're Not Ready to Hire": What We Heard at Twin Cities Startup Week
One founder put her hand up and asked it out loud. "Where can I get a security team that I don't have to hire in house?" Most of the room was sitting on the same question. Here's what she asked, what it costs to answer it either way, and how to tell which side of it you're on.
This past Wednesday, the YSecurity Minnesota team attended Twin Cities Startup Week. Three of us sat in on a session called “Building with Cybersecurity in Mind,” led by Nathaniel Engelsen, SVP of Technology at Augeo, and Clea Ostendorf, CEO of Wolfpack Security. The talk focused on building security in from the start, rather than adding it later once a customer requires it. It was a great session.
Then they opened it up for questions at the end, and the Co-Founder of a healthtech company put her hand up.
She said it was all great information, being that she’s a growing startup, but then she asked the question that was on a lot of people’s minds in that room. What if we’re not ready to hire someone full time? Her company wasn’t there yet. The need wasn’t going anywhere either. So was there such a thing as an on-demand security team, or a consultant, who’d just take this on for a company her size?
Nathaniel and Clea gave her the best answer they could have. There might actually be people in this room who could help you with that.
We were glad to be exactly that resource for her, and made a point of introducing ourselves before she left.
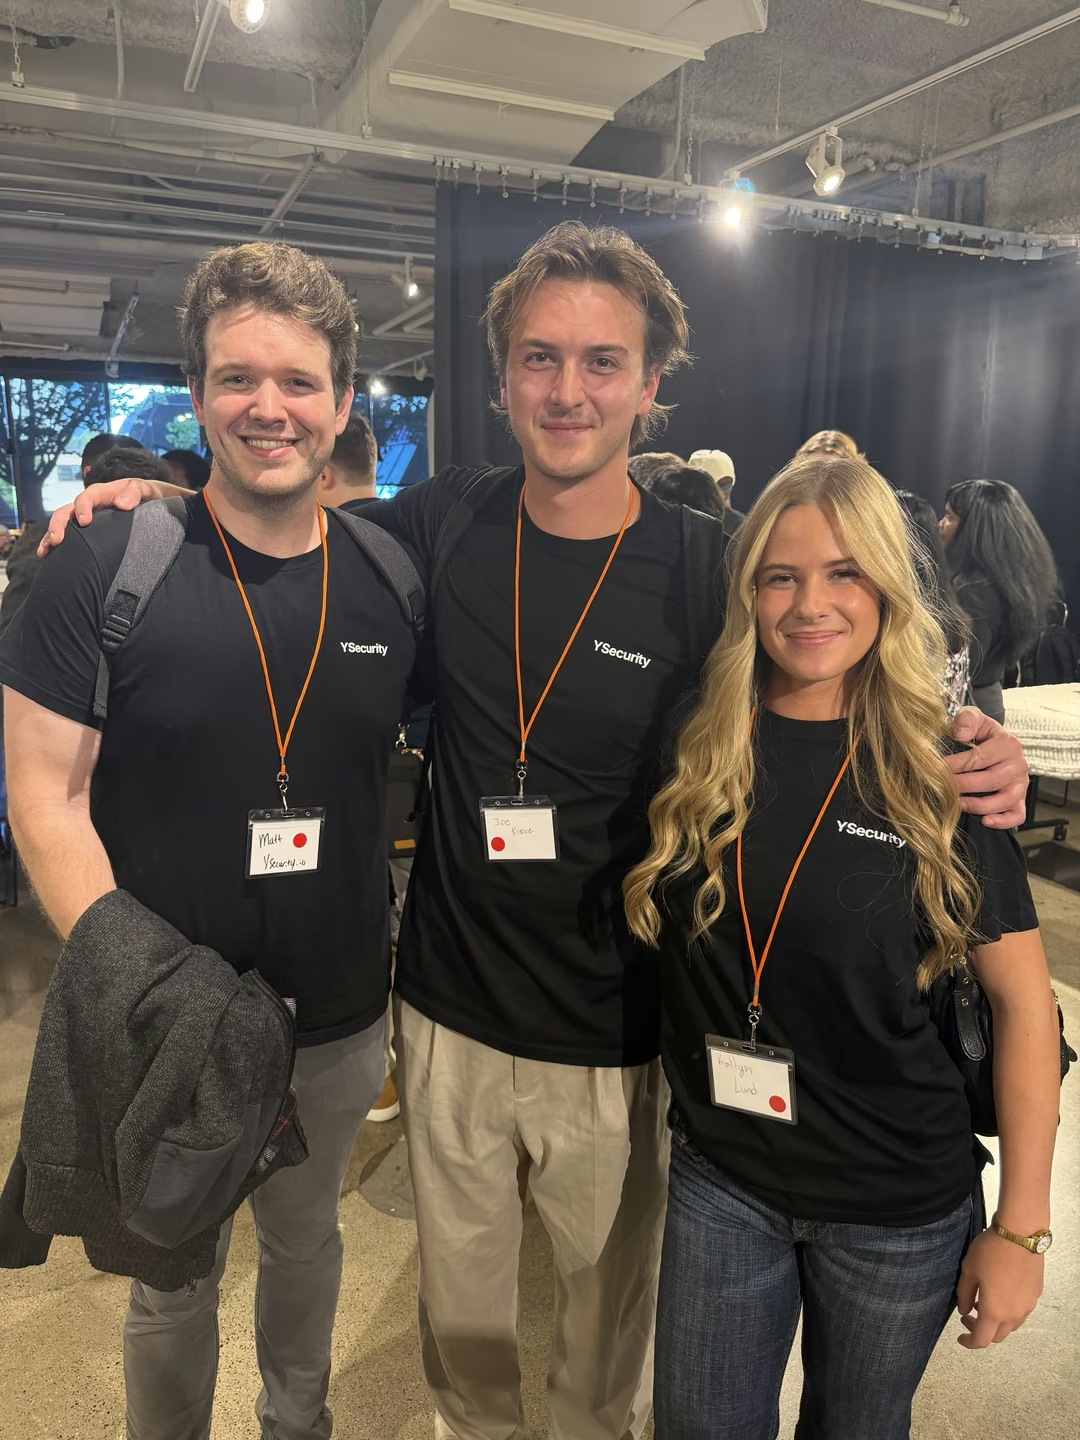
We had a great conversation. We took the time to understand her, her company, and what they actually needed day to day. It was a good chance to share that this is a problem so many founders face, and to explain that’s exactly what YSecurity is for.
She was the only one who asked the question out loud, but it’s a question a lot of growing companies are facing.
Why nobody else asked
We spent the rest of the day meeting founders, and the same thing kept coming out in slightly different words. We need a SOC 2 soon. We’re not ready for an in-house team. We’ve been looking around and we haven’t found the right team yet.
That last part stood out to us. A founder who’s already looking has typically accepted that this is something they’ll need to spend money on. What’s missing is a clear, plain-language breakdown of the options, so the decision gets pushed to next quarter, where it sits next to the security questionnaire nobody’s answered yet.
There’s also the part nobody says. Asking that question in a room full of other founders feels like announcing you’re behind. You’re not. Having a real security obligation and nobody obvious to hand it to is about as normal as startups get.
The deadline is usually SOC 2, and it shows up on someone else’s schedule
Hardly anyone starts a security program because they woke up worried about attackers. They start one because a customer asked for something. Usually a SOC 2 report, usually mid-deal, usually with a close date attached to it.
Then the math hits. A first-time SOC 2 Type 2 takes six to twelve months end to end. Type 2 requires an observation window where the auditor watches your controls run over time, and you can’t compress that part no matter who you hire. Run it yourself and it eats 500-plus hours of somebody’s year, spread across a timeline that often stretches toward the longer end. Hand it to a team who’s walked the path before, and that timeline tends to compress. At YSecurity, we typically get first-time clients through the full process in about five months.
So when a buyer asks in March, the honest answer is you should’ve started in September. That’s what the waiting costs, and it never shows up as a line item. It shows up as a deal that slips two quarters.
What a full-time hire runs
Hiring could be the right move for some companies. It’s worth knowing the full picture before you commit to it — if you’re still weighing that decision, we put together a webinar on how to know if you need an in-house or on-demand security team.
Security engineers in the US are landing between $120,000 and $230,000 in total comp this year, with senior and lead roles reaching $250,000 to $400,000+ depending on scope. Fully loaded at a venture-backed startup, once you add benefits, equity, the recruiter’s cut and the tooling budget they’ll ask for in week two, we put a senior security lead at $350,000 to $650,000 a year.
Then there’s the wait. ISACA’s 2025 survey found 65 percent of organizations sitting on unfilled security roles, 55 percent calling their teams understaffed, and 39 percent saying a non-entry-level hire takes three to six months to land. Three to six months to find the person. Then onboarding. Then however long it takes them to get through your codebase.
And the work doesn’t arrive in one shape. A SOC 2 project, a pen test, a product security review, and the questionnaire sales needs back by Friday are four different jobs. Handing all four to one new hire in their first quarter is how you lose them in their third.
What “on-demand” means, and what a vCISO is
This gets called a lot of things. Fractional. Embedded. vCISO, short for virtual chief information security officer. Under the vocabulary it’s one idea: an outside team owns your security work without going on your payroll. Senior judgment when there’s a call to make, hands when there’s work to do, and nothing when there isn’t.
Set that model next to one fully loaded senior hire, and it stops being a close comparison.
The category’s also blown up, which cuts both ways. Cynomi surveyed North American providers last year and found 67 percent offering vCISO services, up from 21 percent the year before, with 96 percent either offering them already or planning to inside two years.
Tripling in a year explains a lot about why the founders we met kept saying they’d been looking and hadn’t found the right fit. When a category grows like that, a good number of the new arrivals are selling a policy pack and a quarterly check-in call. So push on a few things before you sign anything. Who does the work, the person on the sales call or someone you’ll never meet? Do they go into the codebase, or only the documentation? Will they fill out your customer’s security questionnaire, or hand it back to you with comments in the margin? And will they get on the call when your buyer’s security team wants to talk to a security person?
That last one is our whole model. We sit in your Slack, your stand-ups and your customer calls, because the questions that kill deals almost never show up in writing first.
If you’re healthtech, the ground’s moving under you
The founder who asked has better timing than she probably knows.
HHS put out a proposed overhaul of the HIPAA Security Rule back in January 2025. It’s still only a proposal, and the current read is a final rule around mid-2027 with roughly 240 days after that before anyone has to comply. Nothing’s due next week. What matters is where it’s pointed. Encryption of electronic protected health information would become mandatory at rest and in transit. So would multi-factor authentication. Risk assessments on a fixed annual schedule. Annual penetration testing, required instead of suggested.
Most of that currently sits under “addressable,” which is the regulatory word founders have been quietly reading as optional. That’s the flexibility going away.
The rule is the slow half of this anyway. Hospital and payer procurement teams are asking for these controls right now, as though it were already final, because their risk teams read the same proposal you did. If you sell into health systems, your buyer is your compliance deadline, and your buyer moves faster than HHS ever will.
So which one are you
Short version.
Hire in-house when security is part of what you sell, when it lives inside the product, and when there’s a steady 20 to 40 hours a week of it every week. At that point you’ve stopped buying help and started building a function, and a function needs somebody sitting in every planning meeting.
Go on-demand when the work’s real but lumpy. A certification with a date on it. A pen test before a renewal. A questionnaire holding up a contract. One quarter where you need somebody senior in the room with a buyer, and three where you don’t. Paying a salary for that shape of work means paying a lot for the quiet months.
And on-demand doesn’t have to mean short-term. Plenty of companies run their entire security function this way for years, not just for one certification or one deal — a dedicated team, embedded long-term, without ever building the function in-house.
If you’re not sure which one you are, we built a 2-minute quiz that runs your situation through some of the same questions we’d ask you on a call. One of the answers it can give you is go hire someone in-house, and we mean it.
Last thing
She named her constraint, said what she needed, and asked whether it existed. Three people who could answer her were sitting four seats away.
This is a real situation so many founders are dealing with right now, and you’re not the only one figuring it out. If you want to talk it through, our founders Jon McLachlan and Sasha Sinkevich are hosting a webinar on October 6 at 9:30am PT called The $300K mistake most founders make: are you about to make it?, where you can come ask us directly.
On-demand security frequently asked questions
- What is an on-demand security team?
- On-demand security, also called fractional, embedded or vCISO services, means an outside team owns your security work without going on your payroll. The good ones do the work instead of advising on it: running the SOC 2, shipping security features into your codebase, filling out customer security questionnaires, and showing up on the calls where your buyer's security team asks the hard questions.
- How much does a vCISO or on-demand security team cost?
- Published rates generally run $3,000 to $6,000 a month for startup and small-business engagements, and $6,000 to $12,000 a month at growth stage. Compare that to roughly $350,000 to $650,000 a year fully loaded for one senior in-house hire, plus the three to six months you'll spend looking before they start.
- Can we get a SOC 2 without a security person on staff?
- Yes, and most startups do. A first-time SOC 2 Type 2 usually takes six to twelve months end to end, because Type 2 requires an observation window the auditor has to watch run over time. Run it yourself and it'll eat 500-plus hours of internal time, usually spread across the longer end of that range. Hand it to a team that's walked the path before and the timeline compresses. We typically get first-time clients through the full process in about five months.
- How long does it take to hire a security engineer?
- Longer than most founders plan for. ISACA's 2025 State of Cybersecurity survey found 65 percent of organizations with unfilled security positions, and 39 percent saying a non-entry-level role takes three to six months to fill. That's before onboarding, and your deal's deadline isn't waiting.
- Is HIPAA changing for healthtech startups?
- A proposed overhaul of the HIPAA Security Rule was published in January 2025 and still isn't final. It would make encryption of ePHI, multi-factor authentication, annual risk assessments and annual penetration testing mandatory rather than addressable. The rule isn't the near-term pressure, though. Hospital and payer procurement teams are already asking for those controls today.
- How do we tell a good on-demand provider from a bad one?
- Ask who does the work day to day, whether they go into the codebase or only the documentation, whether they'll complete a customer security questionnaire instead of handing it back with comments, and whether they'll join the call when your buyer's security team wants to talk to a security person. The category tripled in a year, so plenty of providers are selling a policy pack and a quarterly check-in.